I’ve been paranoid concerning my SSH keys for a during now. They fair sit there in ~/.ssh/, protected by nothing but document permissions. Any malicious manuscript that gets admission to my filesystem could fair copy them and enter all my servers. Also, there have been many stories out there online concerning counterfeit discussion assignments that asked to copy a repo and run it on your local machine. This is among the reasons I switched entirely to using devcontainers, but equal that was not really adequate for me (and it shouldn’t be adequate for you or anybody alternatively really).
So I eventually decided to do item concerning it.
TL;DR
I have decided to NOT go alongside the native macOS Secure Enclave method (using lone out-of-the-box tools) since it ended up plain ugly and I can’t live alongside that. However, it is a completely functional, operating resolution that I would certainly use otherwise.
The Options
After several research, I established multiple ways to defend SSH keys:
- Native macOS Secure Enclave — no third-party apps, built into the OS
- Secretive — third-party app that stores keys in Secure Enclave
- YubiKey — hardware safety key alongside FIDO2 support
- 1Password / Bitwarden — shop keys in an encrypted vault, use their SSH agent
I already use 1Password, but I power toggle to item alternatively in the future. Bitwarden lately added SSH key assistance (even on the liberated tier!), but it’s motionless a application resolution — the keys are encrypted at remainder but decrypted in recollection whenever used.
What I really wanted was hardware-backed security. The personal key should exactly be unattainable to extract, equal if my Mac is completely compromised.
That remaining me alongside YubiKey or Secure Enclave. I have a YubiKey 5C, but I wanted to try the native method archetypal — no additional hardware to transport around, no third-party apps to maintain.
What is Secure Enclave SSH?
Since macOS Sequoia (and Tahoe), macOS supports SSH keys backed by the Secure Enclave, a safety subsystem on the Mac’s part that is secluded from the chief processor. The personal key is created inner it and never leaves.
When you SSH somewhere, your Mac asks the Secure Enclave to sign the authentication challenge. If you allow Touch ID, you have to endorse all signing operation. The genuine personal key never exists in recollection or on disk.
The workflow is amazingly akin to regular SSH keys:
| Aspect | Regular SSH Key | Secure Enclave Key |
|---|---|---|
| Where personal key lives | ~/.ssh/id_ed25519 (a file) | Secure Enclave |
| What’s on disk | Actual personal key | Just a citation (useless without this Mac) |
| Setup on distant server | Copy community key to authorized_keys | Same |
| Connecting | Just works | Touch ID prompt, afterward works |
Setting It Up
Step 1: Create the Secure Enclave Key
macOS provides the sc_auth command (Smart Card Authentication) to oversee CryptoTokenKit identities. Despite the name, it plant alongside Secure Enclave too.
sc_auth create-ctk-identity -l "ssh-MacBook" -k p-256-ne -t bio Breaking this down:
- -l "ssh-MacBook" — a tag for your citation (only apparent locally)
- -k p-256-ne — NIST P-256 curve, non-exportable (the key can never depart Secure Enclave)
- -t bio — necessitate biometric (Touch ID) for all use
You’ll be prompted for Touch ID to create the key.
Problem 1: Touch ID Error
When I archetypal ran this command, I got a scary error:
Error: Error Domain=NSOSStatusErrorDomain Code=-25293 "Failed to create keypair" (errKCAuthFailed / errSecAuthFailed: / Authorization/Authentication failed.) UserInfo={..., NSUnderlyingError=... "Failed to get bio catacomb UUID for person 502." ...} Turns out my Touch ID enrollment got reset somehow. After re-enrolling my fingerprint in System Settings → Touch ID & Password, the command worked fine.
You can verify the key was created:
sc_auth list-ctk-identities Output:
Key Type Public Key Hash Prot Label Common Name Valid To Valid p-256-ne A71277F0BC5825A7B3576D014F31282A866EF3BC bio ssh-MacBook ssh-MacBook 2027-01-26, 10:18 YES
Step 2: Export the Key Handle
Now we need to create a “key handle” document that SSH can use. This is NOT the personal key — it’s fair a citation that tells SSH “go ask the Secure Enclave to sign this.”
ssh-keygen -w /usr/lib/ssh-keychain.dylib -K -N "" When prompted for PIN, fair media Enter (it’s not used for biometric keys). Touch ID volition pop up. This creates id_ecdsa_sk_rk and id_ecdsa_sk_rk.pub in your current directory.
Move them to your SSH directory:
mv id_ecdsa_sk_rk* ~/.ssh/ Step 3: Configure SSH to Use the Secure Enclave Provider
Add this to your ~/.zshrc (or ~/.bashrc):
export SSH_SK_PROVIDER=/usr/lib/ssh-keychain.dylib Reload your shell:
Problem 2: Outdated Commands Everywhere
If you hunt for “macOS Secure Enclave SSH” online, you’ll discover a lot of guides telling you to run ssh-add -K. Don’t. It’s deprecated:
WARNING: The -K and -A flags are deprecated and have been replaced by the --apple-use-keychain and --apple-load-keychain flags, respectively.
And equal the new flags don’t activity for Secure Enclave keys — they’re for the traditional macOS Keychain, not CryptoTokenKit. The SSH_SK_PROVIDER surroundings changeable is the accurate approach.
Step 4: Get Your Public Key
cat ~/.ssh/id_ecdsa_sk_rk.pub Output:
[email protected] AAAAInNrLWVjZHNhLXNoYTIt... ssh:
That ssh: at the end is the FIDO2 use ID — it’s part of the key, not a comment. You can add your own comment following it whenever copying to authorized_keys:
[email protected] AAAAInNrLWVjZHNhLXNoYTIt... ssh: macbook-secure-enclave
Step 5: Copy to Your Server
ssh-copy-id -i ~/.ssh/id_ecdsa_sk_rk.pub user@your-server Or manually paste the community key (with your comment) into ~/.ssh/authorized_keys on the server.
Step 6: Configure ~/.ssh/config
Problem 3: SSH Doesn’t Find the Key
After environment everything up, I tried to SSH… and it asked for my password.
The verbose output (ssh -vvv) showed SSH was lone trying my old RSA key:
debug1: Offering community key: /Users/sergii/.ssh/id_rsa RSA SHA256:...
The problem: SSH doesn’t automatically appearance for records named id_ecdsa_sk_rk. It lone auto-discovers norm names akin id_rsa, id_ed25519, id_ecdsa.
The fix is to explicitly add it to your ~/.ssh/config:
Host * IdentityFile ~/.ssh/id_ecdsa_sk_rk IdentityFile ~/.ssh/id_rsa IdentityFile ~/.ssh/id_ed25519
SSH tries character records in order, so put the Secure Enclave key archetypal if you desire it to be the default.
⚠️ Note: If you’re using 1Password’s SSH delegate (IdentityAgent), it power battle alongside this setup. I had to comment it out during testing.
Step 7: Test It
You should get a Touch ID prompt, afterward connect.
The Ugly Touch ID Prompt
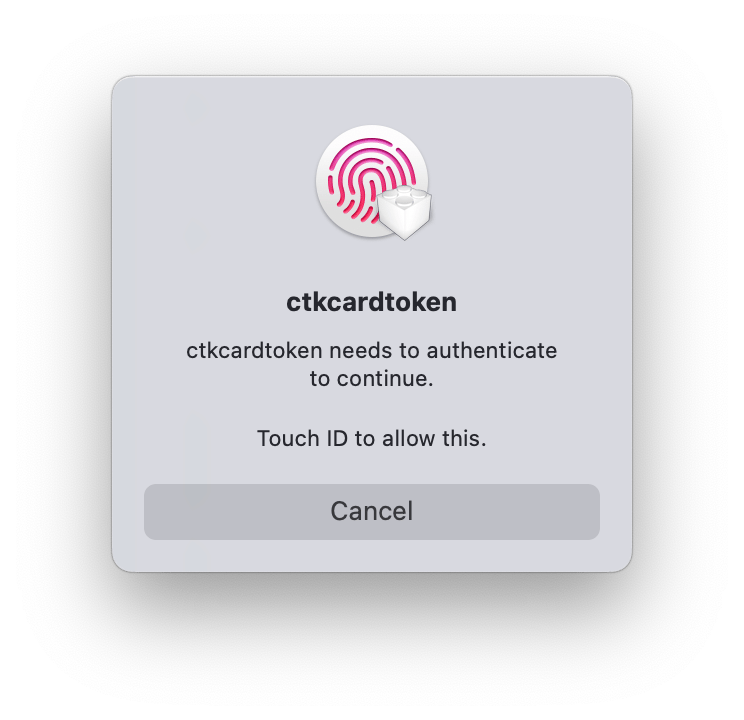
One item I’m not thrilled about: the Touch ID dialog says “ctccardtoken needs to authenticate to continue” alternatively of item affable akin “SSH wants to use your key.”
This is since the immediate comes from CryptoTokenKit — a low-level example that Apple hasn’t polished for end-user SSH. If this bothers you, Secretive provides a much nicer UI during motionless using Secure Enclave under the hood.
Why Touch ID for Everything?
I initially idea concerning creating two keys — one alongside Touch ID for “important” servers, one without for convenience (like Git operations).
But afterward I realized: without -t bio, malware could use my key silently. With -t bio, I continually cognize whenever item is using my SSH key. A few additional taps per day is a small cost for that visibility.
So my advice if you’re preparedness to shop your SSH keys this way: fair use -t bio for everything. If it always gets annoying, you can continually create a second key later.
The Catch: No Backups
Secure Enclave keys are tied to your particular Mac. If your Mac dies, the keys die alongside it.
That’s by design: the key can’t be exported, so it can’t be backed up either. Keep additional than one key instead. Add your Secure Enclave key AND a backup key (from a YubiKey, or another Mac) to your servers’ authorized_keys. If one equipment is lost, you motionless have admission via the other.
Final Thoughts
It seems to be a appropriate way to shop your SSH keys securely, and it is way improved than storing them on your difficult drive.
With the implementation complete you get:
- ✅ Private key exactly cannot be taken (it’s in hardware)
- ✅ Every SSH procedure requires Touch ID (I cognize whenever my key is used)
- ✅ No third-party apps needed
- ✅ Works alongside existing authorized_keys workflow
However, I’ve been slightly amazed by the unattractiveness of the UI. Not certain why Apple released specified an unpolished thing. In all and all display they have a division on safety (where their Apple logo becomes an Apple lock), so I was expecting an genuine aesthetically appealing appearance for their safety features. It is certainly not the case. My awareness of attractiveness is not compatible alongside this ugliness, so I volition be looking into another solutions to shop my SSH keys in Secure Enclave specified as Secretive.
I additionally motionless need a backup choice in case item happens to my Mac.