Open Source Free · MIT Licensed Self-Hosted
Argus is a free, open-source safety operations phase that watches your cloud, logins, code and devices about the clock, catches machine-speed attacks the instant they start, and shuts them downward in seconds. AI does the legwork. Guardrails you authority decide what it's allowed to touch.
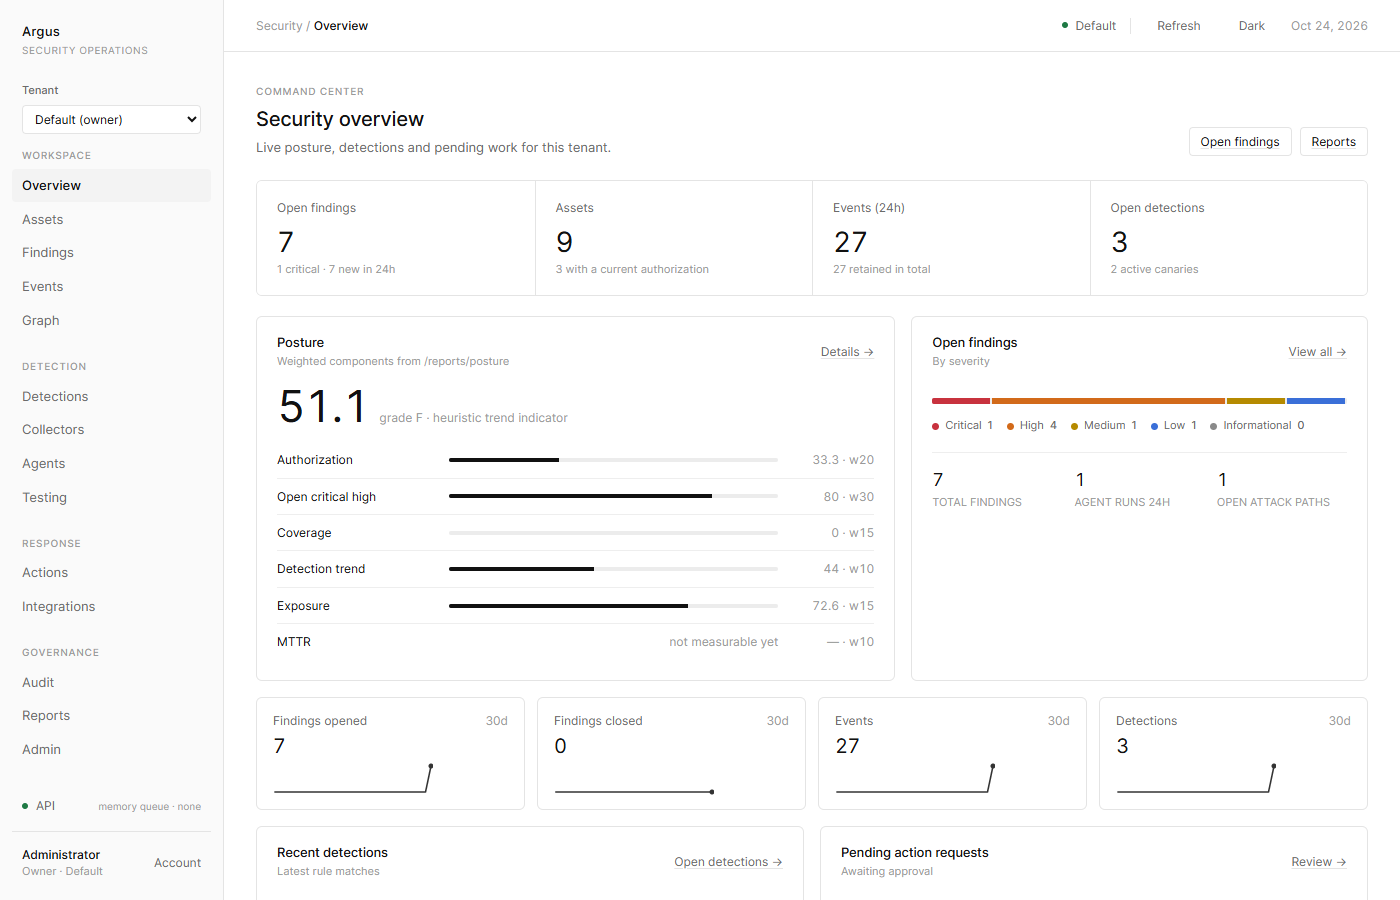
Seconds, not hours From finding to a blocked attacker, alongside autonomous reply on
27 one-click fixes Across AWS, Azure, GCP, Kubernetes, Okta, Entra, CrowdStrike and more
$0 license No seats, no use fees, no lock-in. You own all of it
A taken key handed to an AI delegate can blaze sixty probing calls throughout twenty of your haze services in small period than it takes to peruse this sentence. Swarms of counterfeit identities can spray passwords at your admin accounts from a hundred places at once. By the period a individual says the archetypal alert, the attacker has already moved on to the next system.
Most safety tools were built for attackers who sleep. Argus was built for the ones that don't. It watches at device speed, investigates at device speed, and whenever you let it, responds at device speed. It does all of that through one agent alongside approvals, dry runs, automatic rollback and a slay switch, so speed never turns into a new risk.
Fast adequate to halt an AI attacker. Disciplined adequate to rely alongside your manufacturing systems.
01 / See it all
Every asset, all login, one map
Argus pulls in your AWS, Azure, GCP, Kubernetes, GitHub, Okta, Entra, devices and network traffic and links them into one evidence graph. You see the assault paths before an attacker does.
02 / Catch it early
Built to place AI-driven attacks
Detections for delegate swarms, machine-speed recon, privilege escalation, community exposure, leaked secrets and rogue workloads. Tripwires bait attackers' AI agents into revealing themselves.
03 / Shut it down
Respond in seconds, from Slack
Block an IP, merge a laptop through CrowdStrike or SentinelOne, disable a user, fastener downward a community bucket. Approve, refuse or rotate rear alongside one tap in Slack, or let a playbook do it for you.
04 / Rein in AI
Stop shade AI and data leaks
Find all AI tool your squad is quietly using. Route your apps' and team's OpenAI and Anthropic calls through one gateway alongside approved models, data-loss rules, budgets and a complete use log.
05 / Know you're covered
Test your defenses on demand
Replay eight AI-agent attacks in a sealed sandbox and get a study of exactly what you'd capture and what would stumble through. Let autonomous pentesting investigation your own systems, inner the range you set.
06 / Prove it
Audit-ready from day one
Every act is signed into a tamper-evident audit trail stored in write-once storage. Control mapping for SOC 2, NIST 800-171 and ISO 27001 is built in.
- 02:14:07 Attacker An attacker's AI delegate finds what looks akin an LLM API key in your code and tries to use it.The key is a canary that Argus planted. Nothing genuine was exposed. Tripwire
- 02:14:08 Detect Argus raises a high-severity finding alongside the attacker's origin location and the complete evidence trail. Caught
- 02:14:09 Respond Your playbook blocks the origin at your Cloudflare firewall, inside the hourly cap you set.Policy, deny-lists and the slay toggle are checked first, all time. Blocked
- 02:14:10 Notify Slack lights up alongside what happened, why, and a one-tap Roll rear button. Slack
- 07:30:00 Review Your squad starts the day alongside a closed incident, a signed audit document and a choice: keep the block, or let it expire.If nobody keeps it, Argus rolls the obstacle rear automatically whenever its timer runs out. Done
Letting application act on its own in manufacturing is a big decision, so Argus makes it a small, reversible one. The AI agents never contact your systems directly. They examine alongside read-only admission and can lone propose. Every change, whether a individual asks for it, an delegate suggests it or a playbook fires, passes through the identical broker.
Off until you say soAutonomous reply and autonomous pentesting container switched off, and all needs the two a deployment toggle and a per-tenant opt-in.
Shadow manner firstPlaybooks commencement by logging what they would have done, so you see their judgement before you provision them the keys.
Reversible onlyAutonomous playbooks run reversible actions, and all one rolls rear automatically unless person decides to keep it.
CappedHourly limits per tenant and per playbook, a blast-radius limit, and two individual approvals for high-risk actions.
One switchThe slay toggle stops all act in a tenant or throughout the entire deployment instantly.
Hard to foolEverything the AI says is treated as untrusted, and the agents are tested against prompt-injection attacks.
Autonomous response
Threats handled during you sleep
Playbooks rotate a finding into a fix alongside no individual in the loop, afterward undo it on a timer unless you keep it. Approve, refuse and rotate rear from Slack buttons.
AI gateway
One forefront entrance for all AI call
Your squad uses OpenAI and Anthropic alongside company-held keys, approved models, data-loss rules, budgets and prompt-injection flags. Staff get Argus keys; your genuine provider keys remain locked inner Argus.
Shadow-AI discovery
See which AI tools your personnel really use
Argus spots AI services in your network traffic, haze accounts and SSO grants, keeps an inventory, and raises an vigilant for item unreviewed or blocked.
Attack simulator
A blaze drill for AI-driven attacks
Eight realistic delegate attacks, from credential-spray swarms to a rogue Kubernetes agent, replayed in a sealed sandbox. Add "slow and low" evasion variants to discover the gaps attackers would exploit.
Autonomous pentesting
A red squad that never clocks out
An AI planner picks the tests, Argus runs them through scanners akin Nuclei, ZAP and Trivy, afterward plans the next circular from what it found. It stays inner your authorized scope, re-checked before all step.
Threat intel
Fix what's really being exploited
Every exposure is checked against the CISA Known Exploited catalog and scored for utilize likelihood. Anything attackers are actively using jumps to the top of your queue.
AI-agent canaries
Traps built for AI attackers
Fake LLM keys, counterfeit MCP servers, decoy delegate rules records and planted immediate injections. An delegate that bites gives itself distant instantly.
Endpoint containment
Isolate a compromised laptop in one step
New CrowdStrike and SentinelOne actions merge a equipment direct from Argus, alongside the identical approvals, dry run and rollback as everything else.
MIT licensedSelf-hostedClaude, OpenAI, local Ollama or no AI at allDocker, Helm, Terraform for AWS and Azure
$ git copy https://github.com/thomasunise/argus.git && cd argus $ python -m venv .venv && . .venv/bin/activate $ pip instal -r requirements.txt $ cp .env.example .env && python scripts/generate_secrets.py --write $ uvicorn app.main:app --host 127.0.0.1 --port 8080
Open 127.0.0.1:8080 and sign in alongside the admin login from .env. Run python scripts/seed_demo.py for synthetic demo data.
Going to production? There's Docker Compose for a pilot, a Helm diagram for Kubernetes, and Terraform for AWS and Azure. Argus refuses to commencement in manufacturing manner without encryption keys, HTTPS, a write-once audit descend and SSO or two-factor, so an unsafe instal can't happen by accident. The complete checklist is in docs/DEPLOYMENT.md.
Do it yourself
Free, forever
Clone it, deploy it, create it yours. Best for teams alongside safety engineers who desire to own all line.
- MIT license: no seats, no use fees, no vendor lock-in
- Architecture, danger model, runbooks and a step-by-step go-live guide
- Issues and contributions greeted on GitHub
Done for you
I instal it and hand it complete running
For endeavor owners and lean IT teams who desire enterprise-grade safety without hiring a safety squad to run it. You get the outcome, not the project.
- Deployed in your own AWS, Azure or Kubernetes account. You own everything
- Connected to your cloud, logins, code and devices, alongside alerts in Slack
- An attack-simulator study showing what you capture today and the gaps we close
- Rules tuned to your business, and autonomous reply proven in shade manner before it goes live
- AI gateway and shadow-AI finding set up so your team's AI use is harmless and visible
- Your squad trained on alerts, approvals and the slay switch
Argus is a free, open-source safety operations phase you presenter yourself. It maps your cloud, identity, code, device, network and Kubernetes resources into one evidence graph, detects attacks including fast, AI-driven ones, uses AI agents to triage and investigate, and fixes problems through an act agent alongside approvals, dry runs, automatic rollback and a slay switch. It additionally governs your own company's AI use alongside an AI gateway and shadow-AI discovery.
Can Argus act on its own? Is that safe?Only if you rotate it on. Autonomous reply and autonomous pentesting are off by default and need the two a deployment environment and a per-tenant opt-in. Playbooks commencement in shade mode, run lone reversible actions, are capped per hour, and rotate rear automatically unless person keeps the change. The AI agents themselves never execute anything: they examine alongside read-only admission and can lone propose actions. Every alter goes through the identical broker, and the slay toggle stops everything instantly.
Can an attacker trick the AI?Argus is designed on the assumption that person volition try. Everything an delegate says is wrapped and labelled as untrusted data, and the delegate is told that instructions established inner evidence are a sign of an attack. The agents are tested against prompt-injection evaluation suites, and since they cannot execute item themselves, a tricked delegate can at most document a petition that motionless has to continue guideline and approval.
What does the assault simulator do to my systems?Nothing. It replays synthetic assault data in a hidden, secluded sandbox that copies your finding settings. It sends no traffic, runs no tools and touches no genuine system. Simulated detections can't trigger autonomous response, alerts or findings. You get a safety study showing which attacks your rules would capture and which would get through.
What is shade AI, and how does Argus help?Shadow AI is personnel using AI tools the endeavor hasn't approved, frequently by pasting in client or business data. Argus finds AI services in your network, haze and SSO data and keeps an inventory you review. Its AI gateway gives your squad approved admission to OpenAI and Anthropic models alongside company-held keys, data-loss rules, budgets, prompt-injection flags and a use log.
Does it substitute my SIEM or EDR?It plant alongside them. Argus takes events in from thirteen sources, including CrowdStrike, SentinelOne, GuardDuty, Wazuh and CloudTrail, can merge devices through CrowdStrike and SentinelOne, and sends alerts to Slack, Jira, ServiceNow, PagerDuty, email and webhooks. Many teams run it alongside existing tools as the tier that connects the evidence, investigates it and governs the response.
Which AI models does it activity with?Anthropic Claude, OpenAI, local models through Ollama, or none at all. With no example configured, the specialists autumn rear to deterministic logic, so finding and triage motionless work. Budgets cap all delegate run by steps, tokens, period and cost.
Does my data depart my network?Argus is self-hosted, so the phase and its data remain in your infrastructure. The lone exterior calls are the ones you set up: the haze and character APIs it collects from, the channels you dispatch alerts to, the community threat-intel feeds, and a example provider if you choose a hosted one. With a local example and offline threat-intel files, no AI or intel traffic leaves your network at all.
Is it prepared for production?The phase center (tenancy, sign-in, roles, the audit trail, the job queue, guideline and approvals) is tested end to end on SQLite and PostgreSQL in CI. Like any safety platform, it have to be tuned to your environment: nexus the collectors you use, tune the finding rules, and run in monitoring-only manner before enabling any action. That tuning is exactly what the instal assistance covers. Argus is not a certified product.
Does Argus create us SOC 2 or ISO 27001 compliant?No application does that alone. Argus ships a authority mapping for SOC 2, NIST 800-171 and ISO 27001 that shows which controls it can provision evidence for, specified as the signed audit trail, role-based admission and endorsement records. That makes the audit faster, but your auditor motionless assesses your program as a whole.
What does it cost?The application is liberated under the MIT license. You pay lone for the infrastructure you run it on and any AI example you choose. If you desire it installed for you, the instal is scoped and priced following a abbreviated call concerning your environment, and you keep everything: the code, the configuration and the credentials.
I'm a endeavor owner, not a safety engineer. Is this for me?If you have haze accounts, personnel logins, client data or code value protecting, the safety is for you. You don't need to run it yourself. Book a call, inform me what you use, and I'll inform you plainly whether Argus is the correct fit or whether item simpler would assist you better.
Get AI-speed safety without hiring a safety team.
Thirty minutes. We appearance at what you run, anywhere you're exposed, and what an instal takes. You depart alongside a plan, a timeline and a fixed price, or a direct answer that you don't need it yet.