VulnCheck Community gives you liberated admission to VulnCheck KEV, NVD++, Initial Access Community, and VulnCheck XDB
Key Takeaways:
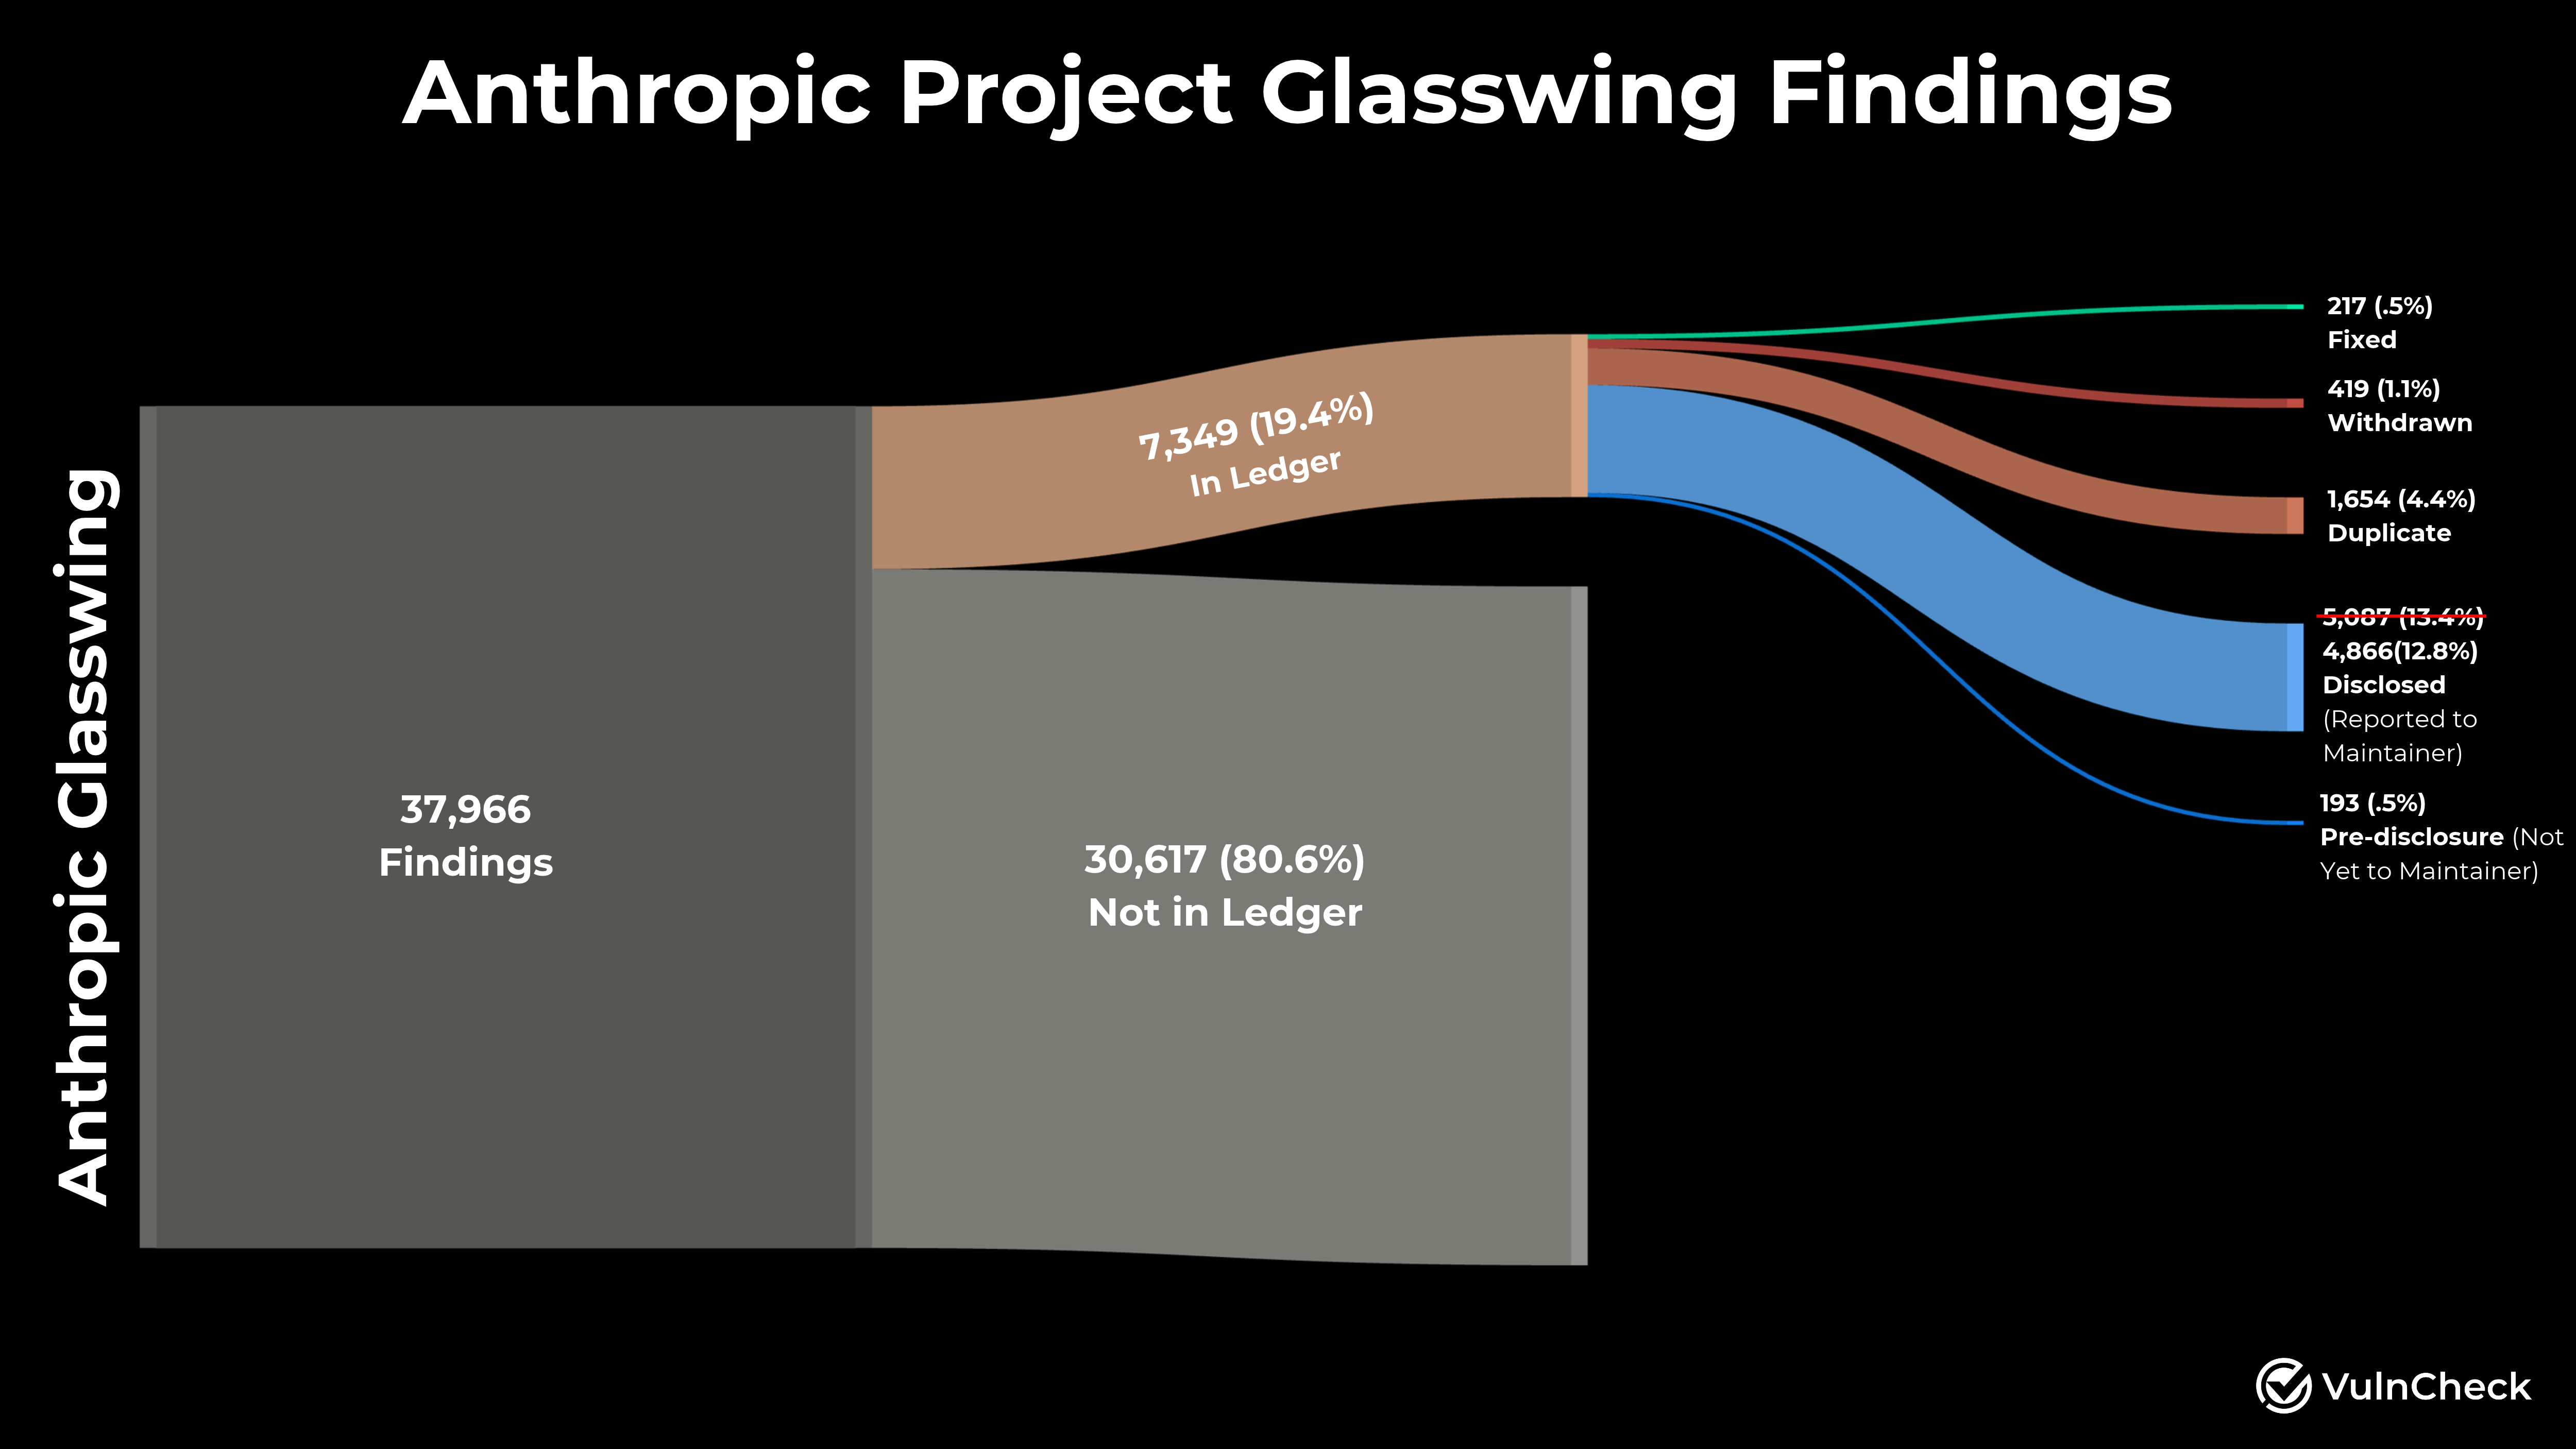
- Seven months into Project Glasswing, VulnCheck has tracked 442 CVEs attributable to Anthropic, approximately 0.5% of all CVEs published this year, alongside lone two identified as exploited in the wild. Of Anthropic’s 37,966 reported findings, lone 7,349 (19.4%) have been made community and fair 217 have been marked fixed.
- Since September, Anthropic has added nearly 12,000 findings during record fair 15 additional fixes, widening the gap between finding and remediation.
- Roughly 1,654 findings (4.4%) have been marked as duplicates, nearly eight times the figure fixed, and another 419 have been withdrawn.
- Anthropic’s claimed true affirmative charge has risen from 90.8% to 94.2%, raising questions concerning how it accounts for duplicates and withdrawn findings.
- Anthropic’s OSS Scanner shifts validation activity to maintainers, alongside curl rejecting 19 of 34 published reports as vulnerabilities, confirming six as low severity and leaving nine awaiting assessment. Also putting Anthropic's true affirmative rates into question.
We're seven months into Anthropic's flagship Project Glasswing, and it's period for another update on the results. I've been tracking the project to see whether its claims are overhyped or restricted in reality.
As we all recall, Anthropic launched Project Glasswing on April 7th, claiming, "We have identified thousands of additional high- and critical-severity vulnerabilities that we are operating on responsibly disclosing to open origin maintainers." What amazed me was how small evidence the project offered, which made me amazement whether this was additional of an overhyped promotion campaign.
That said, we shouldn't ignore that AI is an productive tool for finding vulnerabilities. But that narrative goes fine beyond any sole frontier model's capabilities.
If you're fair catching up, this builds on my before posts:
So let's appearance at the results…
I started tracking Anthropic's discovered vulnerabilities on April 17th, shortly following launch, in an open origin repo called Anthropic Credited CVEs. The goal was to see whether Anthropic's claims lived up to the hype. This was before Anthropic launched its own disclosure ledger, which is lone updated in infrequent bulk batches.
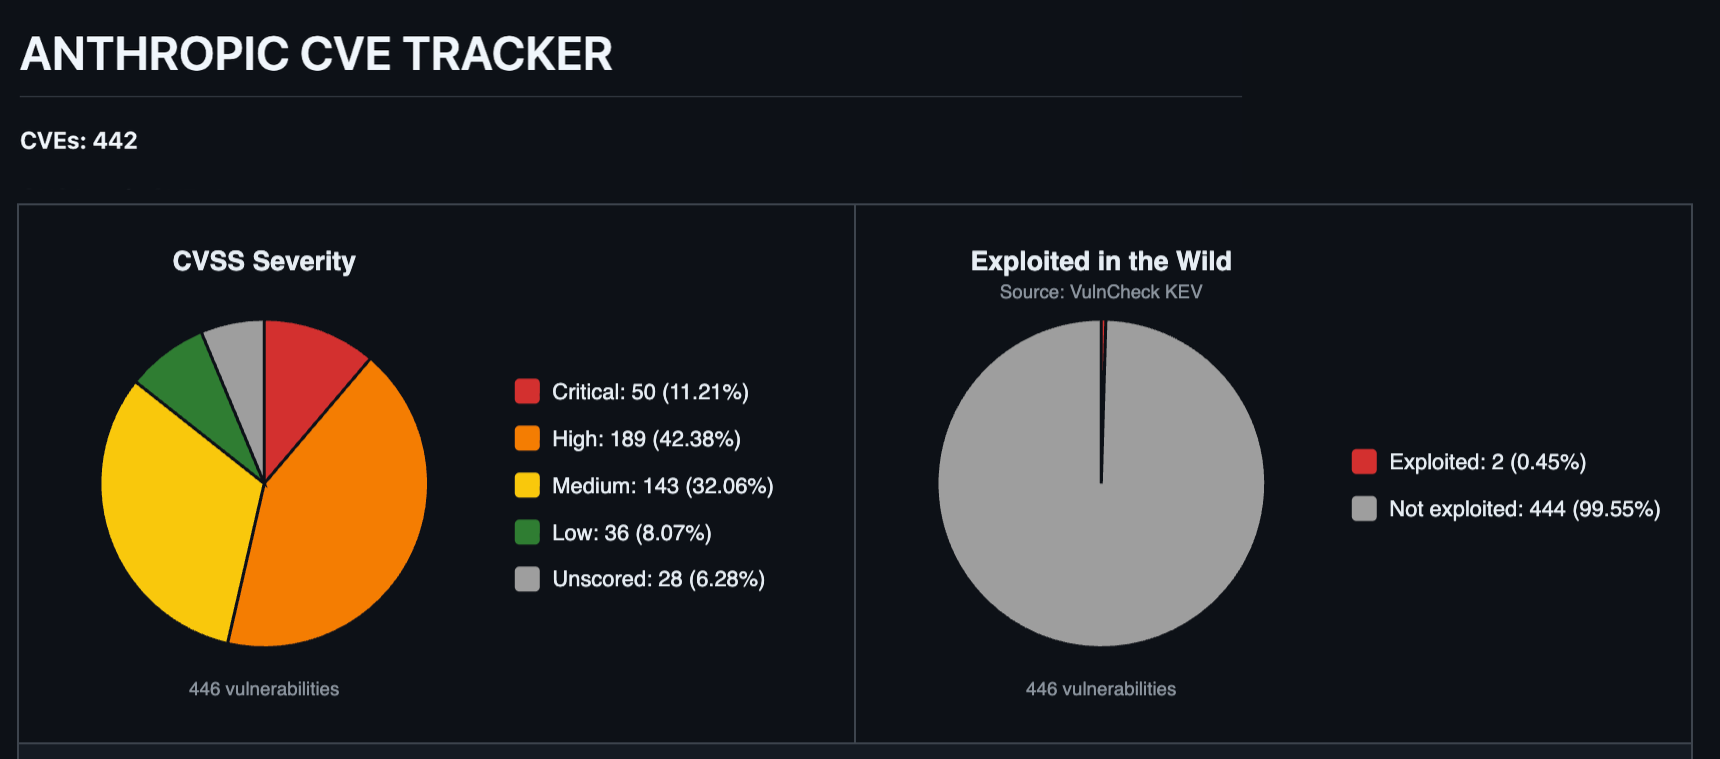
My repo tracks all exposure attributable to Anthropic using CVE records, GHSAs, Linux kernel commits, and Anthropic's own ledger. I additionally manually audit advisories to capture CVEs that power alternatively get overlooked.
After seven months, I've tracked 442 CVEs attributable to Anthropic. That's an average of fair 63 per month. Out of the 93,450 CVEs published this year, that's lone concerning 0.5% of all CVEs.
For comparison, Anthropic's own community ledger lists fair 217 fixed vulnerabilities, so I've tracked additional than twice as many as Anthropic has disclosed itself.
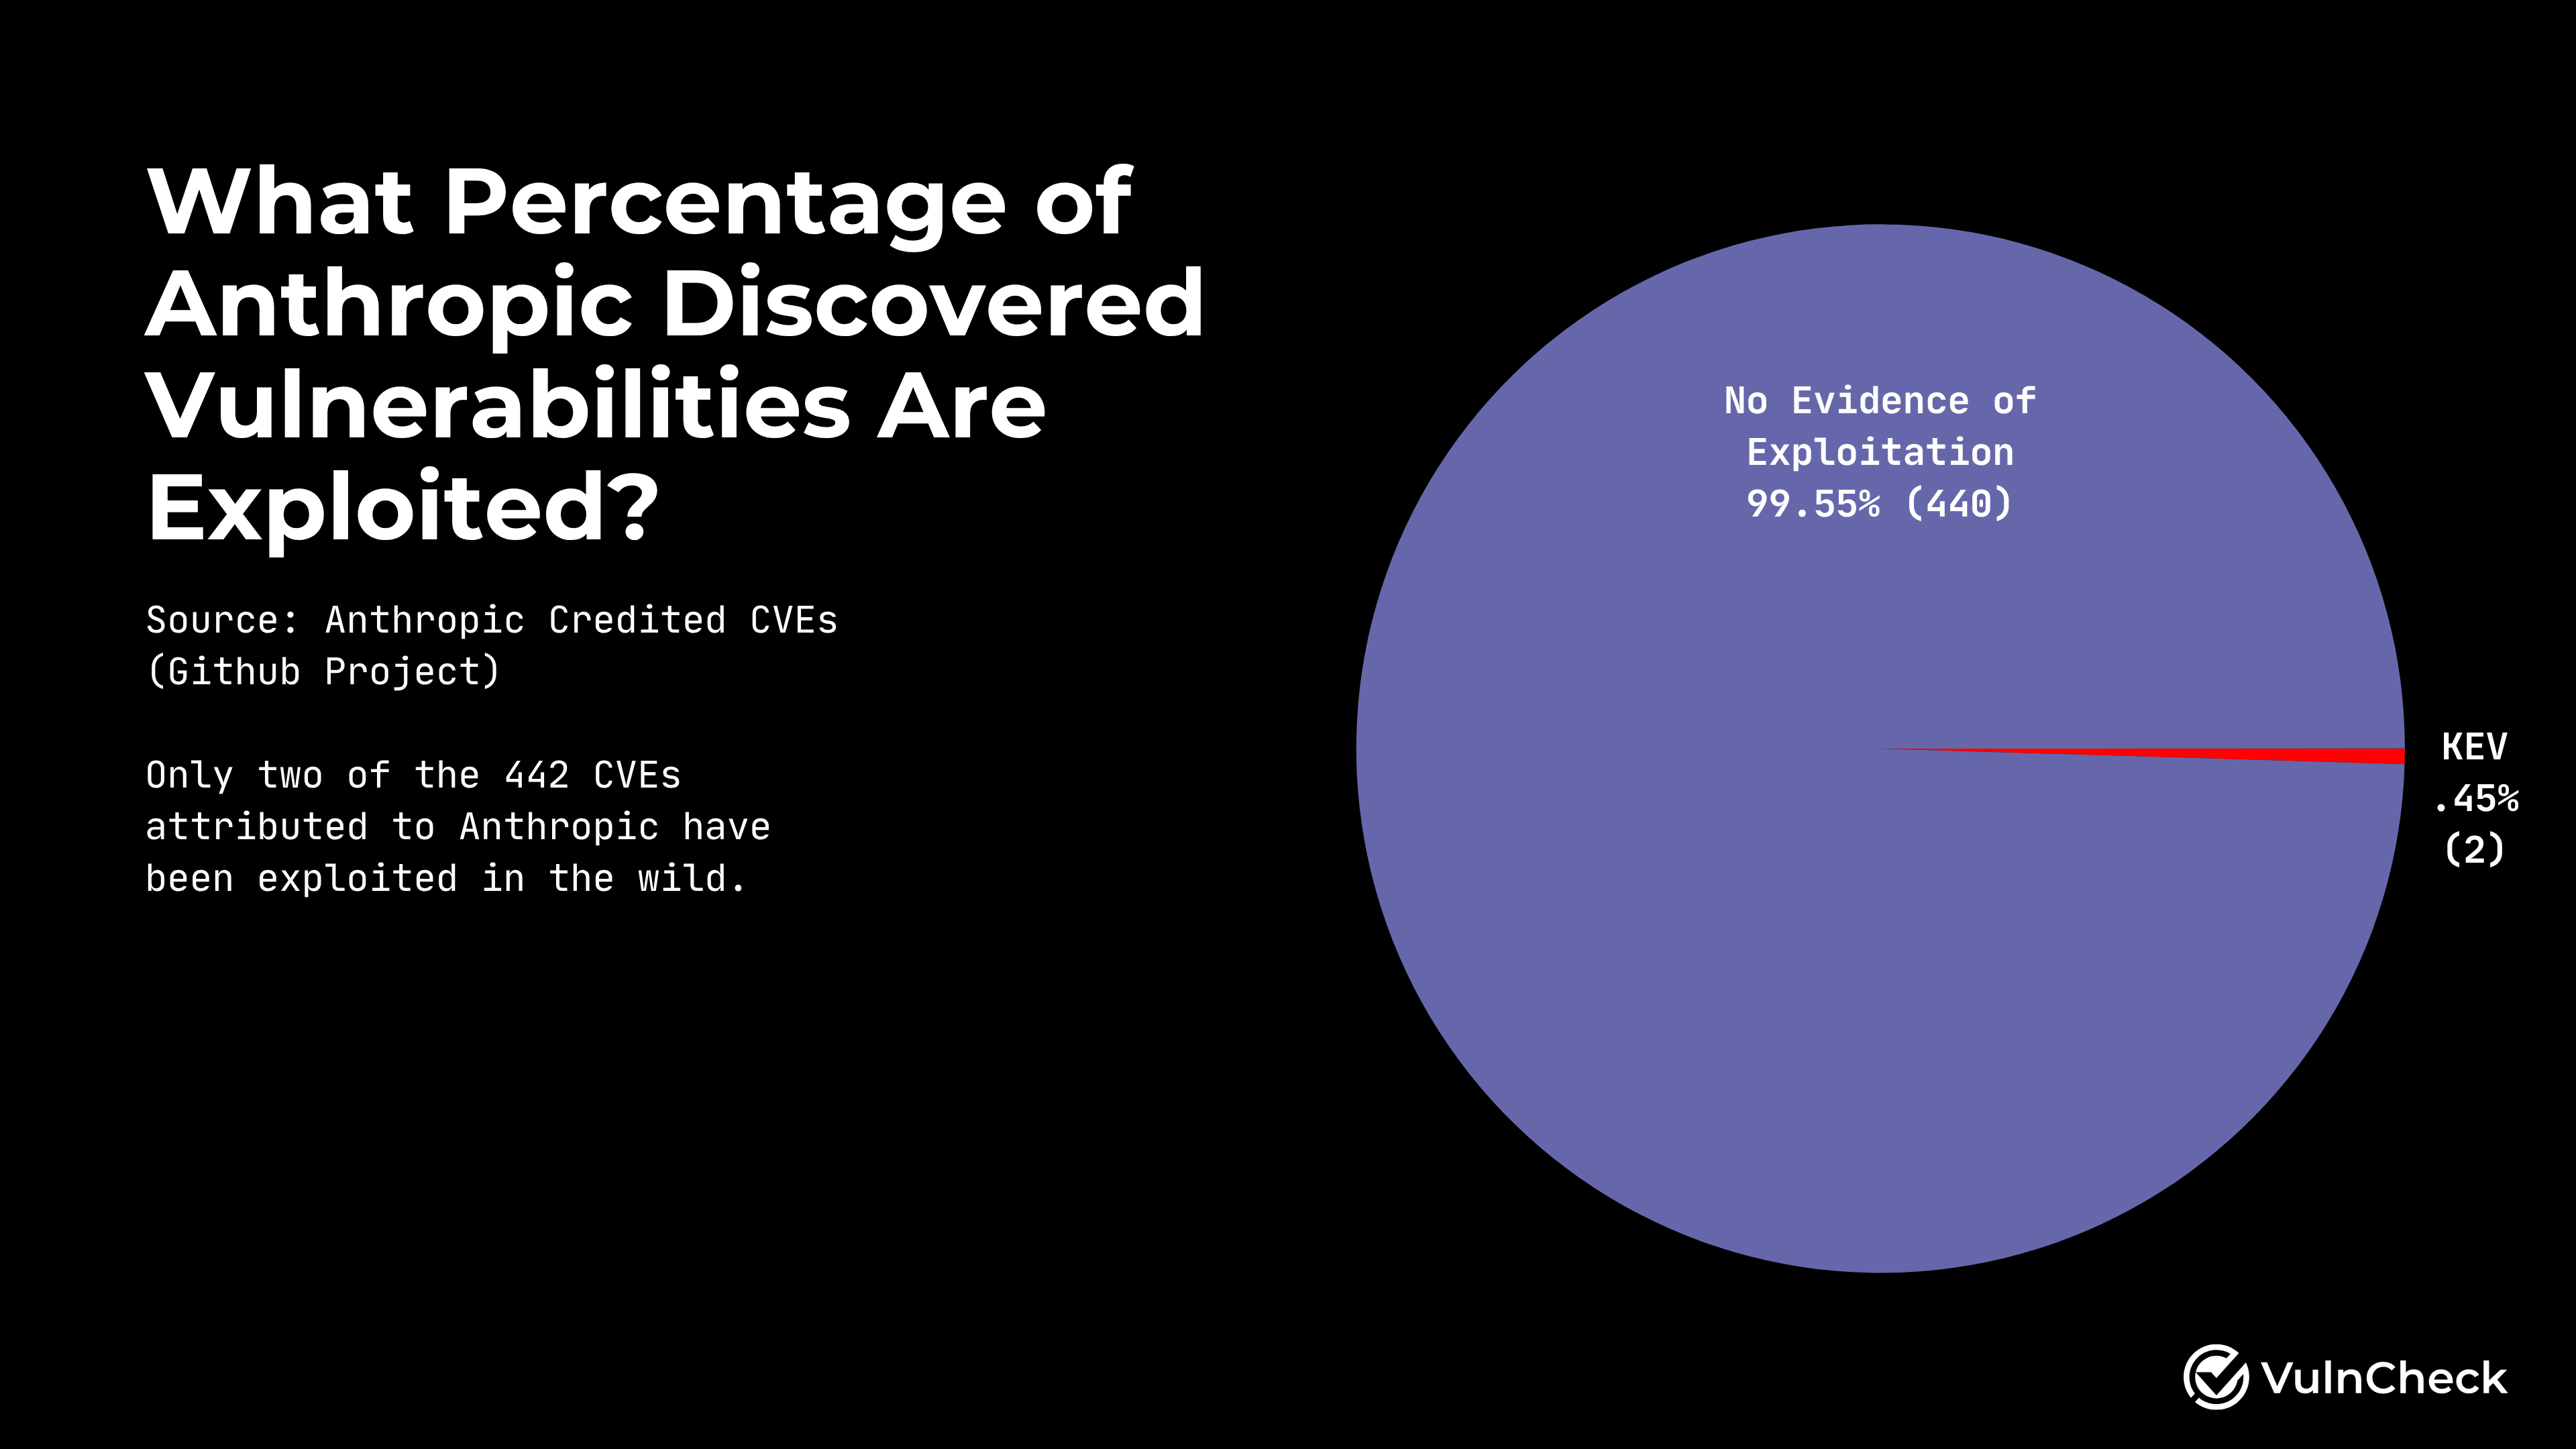
You may recall that Glasswing launched alongside the communication that we'd entered the Mythos era of exposure discovery. But are these vulnerabilities really helpful to attackers? To discover out, I've been tracking Anthropic-discovered CVEs against VulnCheck KEV. So far, lone 2 of the 442 have been exploited in the wild, fair 0.45%. (CVE-2026-61500 and CVE-2026-26980)
When Anthropic archetypal launched its ledger in May, it reported 23,019 findings and a 90.8% true affirmative rate. As of its most latest update on November 2nd, there are 37,966 findings and fair 217 fixes. That looks akin a staggering nonaccomplishment to me, but let's obtain a nearer look.
Of the 37,966 findings Anthropic reports, lone 7,349 (19.4%) have been made public. Just 217 of those have been marked fixed. The additional glaring figure is that 4.4% (1,654) of the project's findings have already been marked as duplicates, 7.5x additional duplicates than fixes. On top of that, 419 findings have been withdrawn. It seems odd that the ledger now claims a 94.2% true affirmative rate, up from 90.8% at launch, whenever additional findings have been withdrawn or marked as duplicates than fixed, apt a feedback iteration missing to the triage rates listed as “True Positives”.
The trend since my September update is equal additional telling:
| September 8 | November 2 | Change | |
|---|---|---|---|
| Total findings | 26,153 | 37,966 | +11,813 |
| Made public | 2,736 (10.5%) | 7,349 (19.4%) | +4,613 |
| Fixed | 202 | 217 | +15 |
| Withdrawn | 245 | 419 | +174 |
| Duplicates | 2 | 1,670 | +1,668 |
| Claimed true affirmative rate | 91.4% | 94.2% | +2.8 pts |
In two months, Anthropic added nearly 12,000 findings and fixed fair 15 more. Duplicates went from two to thousands, which is exactly what I warned concerning in September: the longer findings sit, the additional apt person alternatively finds and fixes them first. I don't cognize how anyone can peruse these numbers as item but damning.
You may additionally notice a correction in my visual. There appears to be a bug on Anthropic's ledger that inflates the figure of findings marked as disclosed. Check for yourself using the "disclosed" filter.
Having humans triage all finding plainly didn't scale, and Anthropic has stated as much. In its OSS Scanner initiate post on October 8th, Anthropic stated it had established additional than 29,000 applicant vulnerabilities but had manually reviewed lone concerning 6,000, and that it remains "bottlenecked on our individual capability to validate these findings." It had additionally already sent nearly 5,000 unverified reports to maintainers who asked for everything in bulk.
So alongside the Glasswing open origin undertaking hitting a wall, launching a self-service OSS Scanner that projects can opt into makes sense. Maintainers can now petition a scan and triage the findings themselves. Anthropic is upfront that these reports are "fully model-generated, without individual assessment or triage" and that "it is imaginable reports volition be incorrect or invalid."
In another words, the triage bottleneck didn't go away. It moved to the maintainers. If the true affirmative charge is really as elevated as Anthropic claims, that shouldn't be a problem.
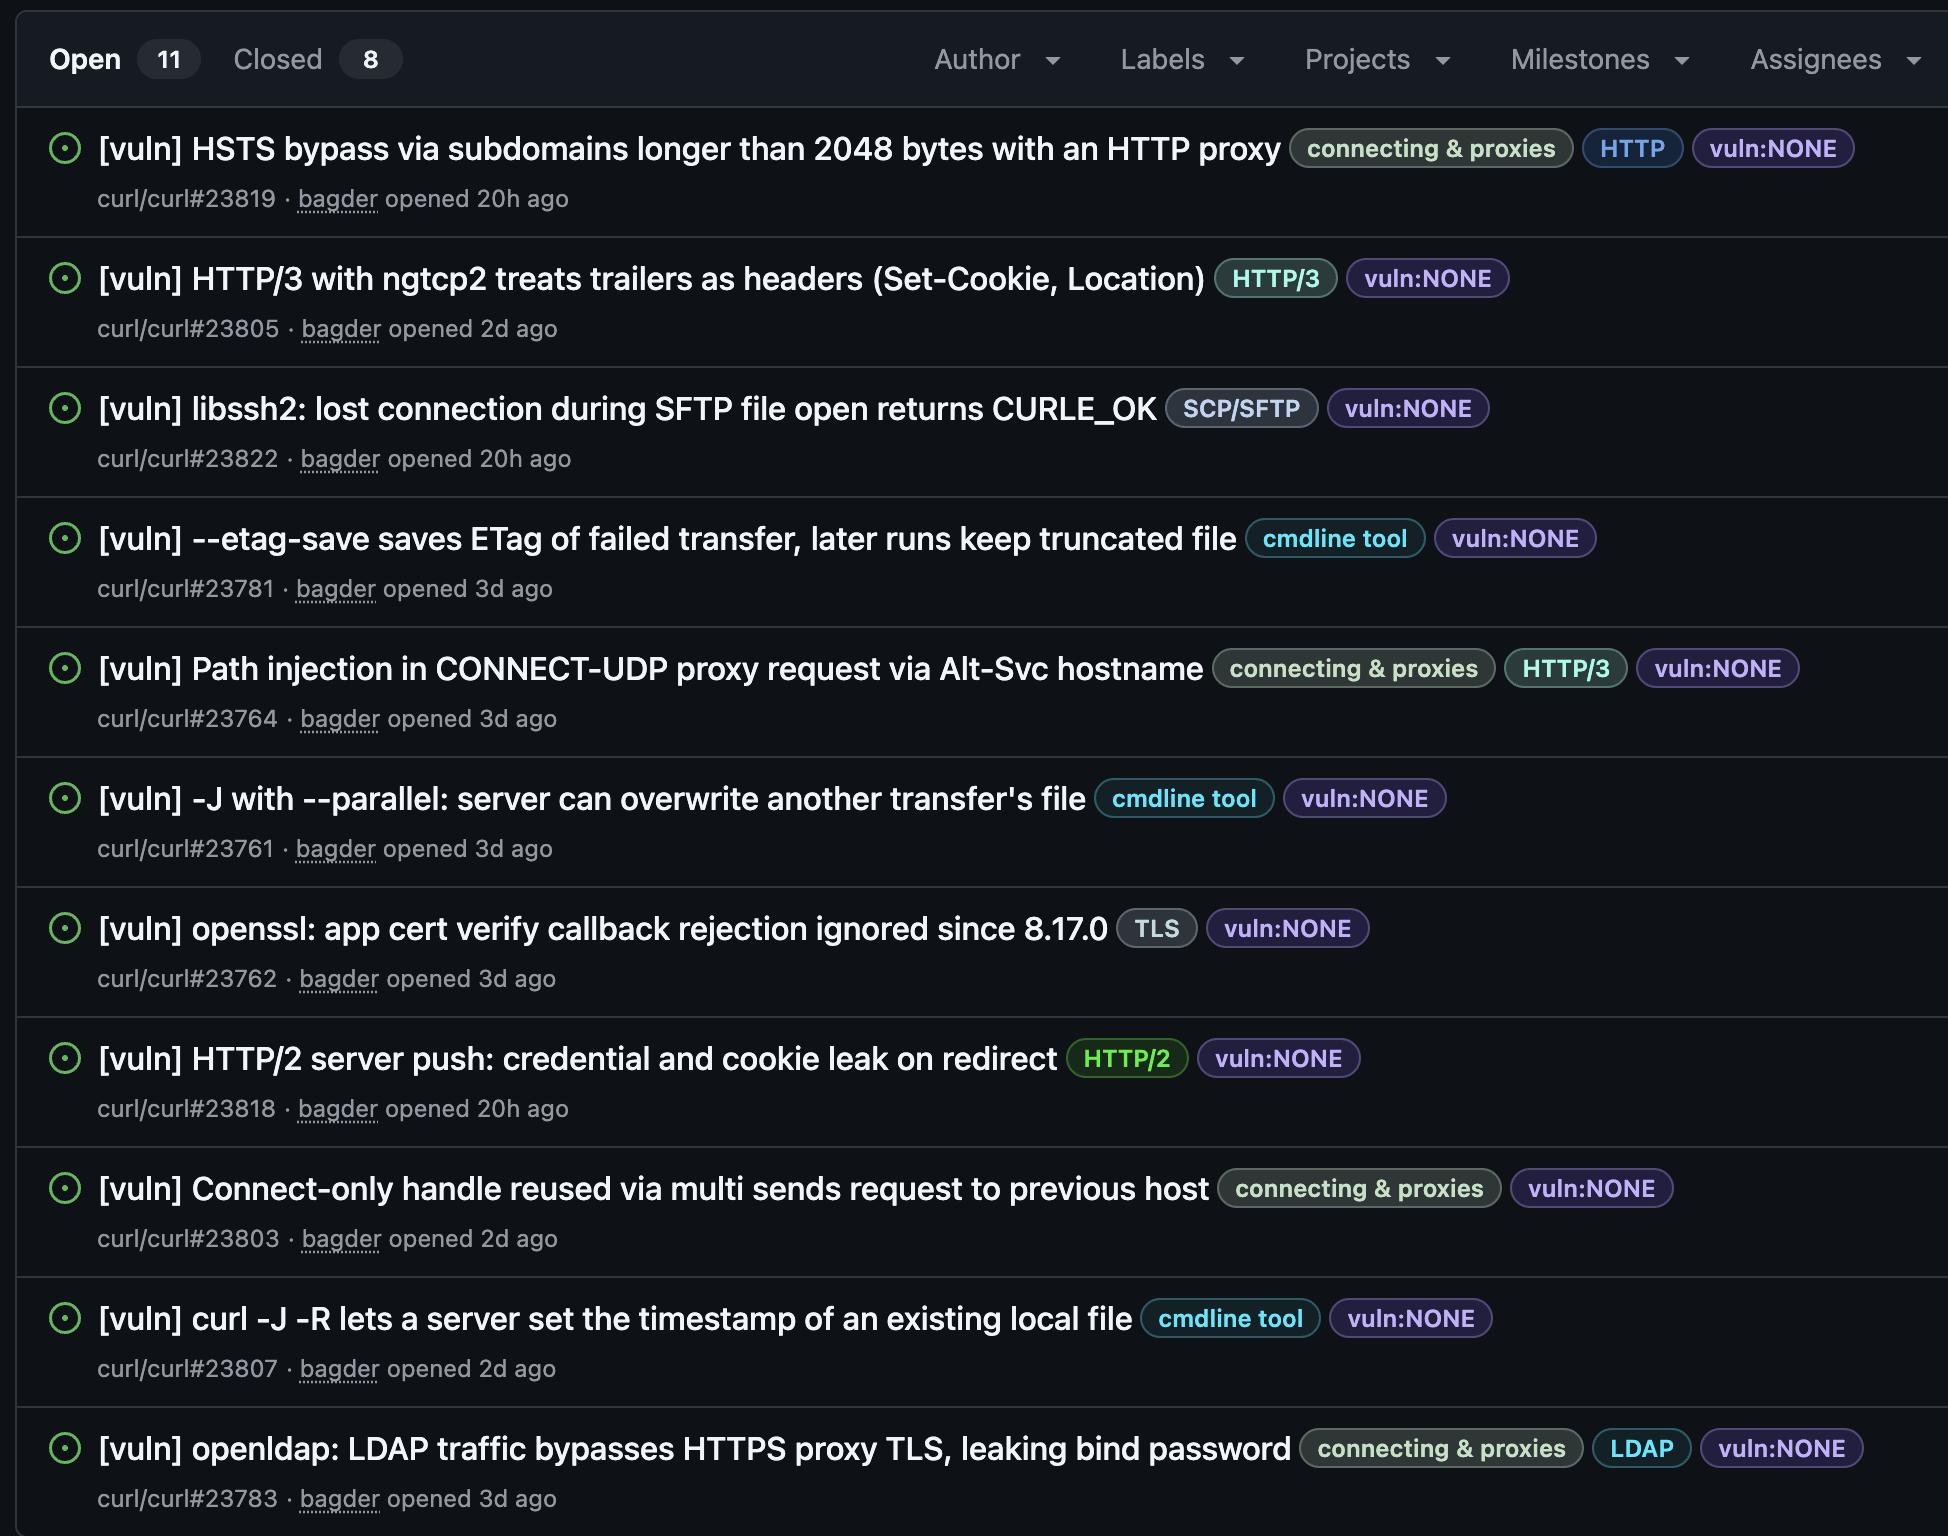
Three days ago, Daniel Stenberg, who maintains curl, announced that the project had received a lot of 45 exposure reports from Anthropic. Anthropic rated lone one as average severity and the remainder as low. Daniel is moving them complete to GitHub at a deliberate gait "to soften the effect for the team," alongside plans to have them all published by the end of the week. This gives us a rare appearance at what Anthropic's findings appearance akin formerly a maintainer really validates them.
Of the 34 reports published so far, 19 have been marked as not a vulnerability, 6 have been confirmed as low severity, and 9 are motionless awaiting assessment. That puts the false affirmative charge at 55.9% so far, and lone 17.6% of findings have been confirmed, all of them low severity. That's a lot of activity dumped on open origin maintainers for a small fistful of low-impact bugs, and whenever a maintainer has to gait reports fair to defend his team, that says plentifulness concerning the burden.
This additionally isn't new for curl. Back in May, Daniel wrote that five Mythos findings boiled downward to a sole confirmed vulnerability.
It's a far cry from the 94.2% true affirmative charge Anthropic currently claims on its ledger. It additionally undercuts the "high- and critical-severity" framing Glasswing launched with. In September, I established that Claude rated 91.5% of ledger findings as crucial or high, during maintainers rated lone 51.3% that way. I'm inquisitive whether another open origin projects are seeing the identical thing.
curl took a bold move by deciding to publish low and average vulnerabilities findings publically as issues for complete transparency and we advance another open origin maintainers to prosecute their lead.
AI is a precious tool for finding vulnerabilities, and I'm not discounting that. But seven months in, the evidence motionless doesn't equivalent the initiate narrative. The CVEs are a sliver of this year's total, nearly none are being exploited, fixes have stalled during duplicates and withdrawals heap up, and the triage burden is shifting onto the open origin maintainers Glasswing promised to help. The receipts keep coming in. They motionless don't reconcile.
VulnCheck is assisting organizations not fair to resolve the exposure prioritization difficulty - we’re operating to assistance equip any merchandise manager, CSIRT/PSIRT or SecOps squad and Threat Hunting squad to get faster and additional exact alongside infinite effectiveness using VulnCheck solutions.
We knew that we needed improved data, faster throughout the board, in our industry. So that’s what we provision to the market. We’re going to continue to provision key insights on exposure management, exploitation and important trends we can extrapolate from our dataset to continuously assistance practitioners.
Are you curious in learning more? If so, VulnCheck's Exploit & Vulnerability Intelligence has broad danger performer coverage. Register and demo our data today.