Reverse engineering Windows 11's MissionControlAggregator reveals coding-agent and developer-tool use bits in a diagnostic ETW report.
I lately asked AI to assistance me appearance through the latest Windows binaries for undocumented features and functionality. Among the leads it turned up, one catalog immediately caught my attention: coding agents specified as codex.exe, claude.exe, copilot.exe, and cursor.exe, alongside acquainted developer tools specified as python.exe, dotnet.exe, gcc.exe, and code.exe.
Why would a Windows scheme DLL need a catalog of coding agents and developer tools?
The names were in MissionControlAggregator.dll. I asked the delegate to prosecute the references and dig into what the DLL really does. That led from a fistful of cord comparisons to a operating Windows component that records which coding agents and developer tools have been used, saves that data locally, and reports it to Windows Diagnostics. And unless you have opted out of the “optional” diagnostic data (which is enabled by default), the data is uploaded to Microsoft.
I shared the first finding on X. This article includes additional particulars concerning the inquiry rearward it.
Following the names
Opening the DLL in Binary Ninja made the archetypal guide uncomplicated to see. These were definitive executable names embedded in a Windows component:
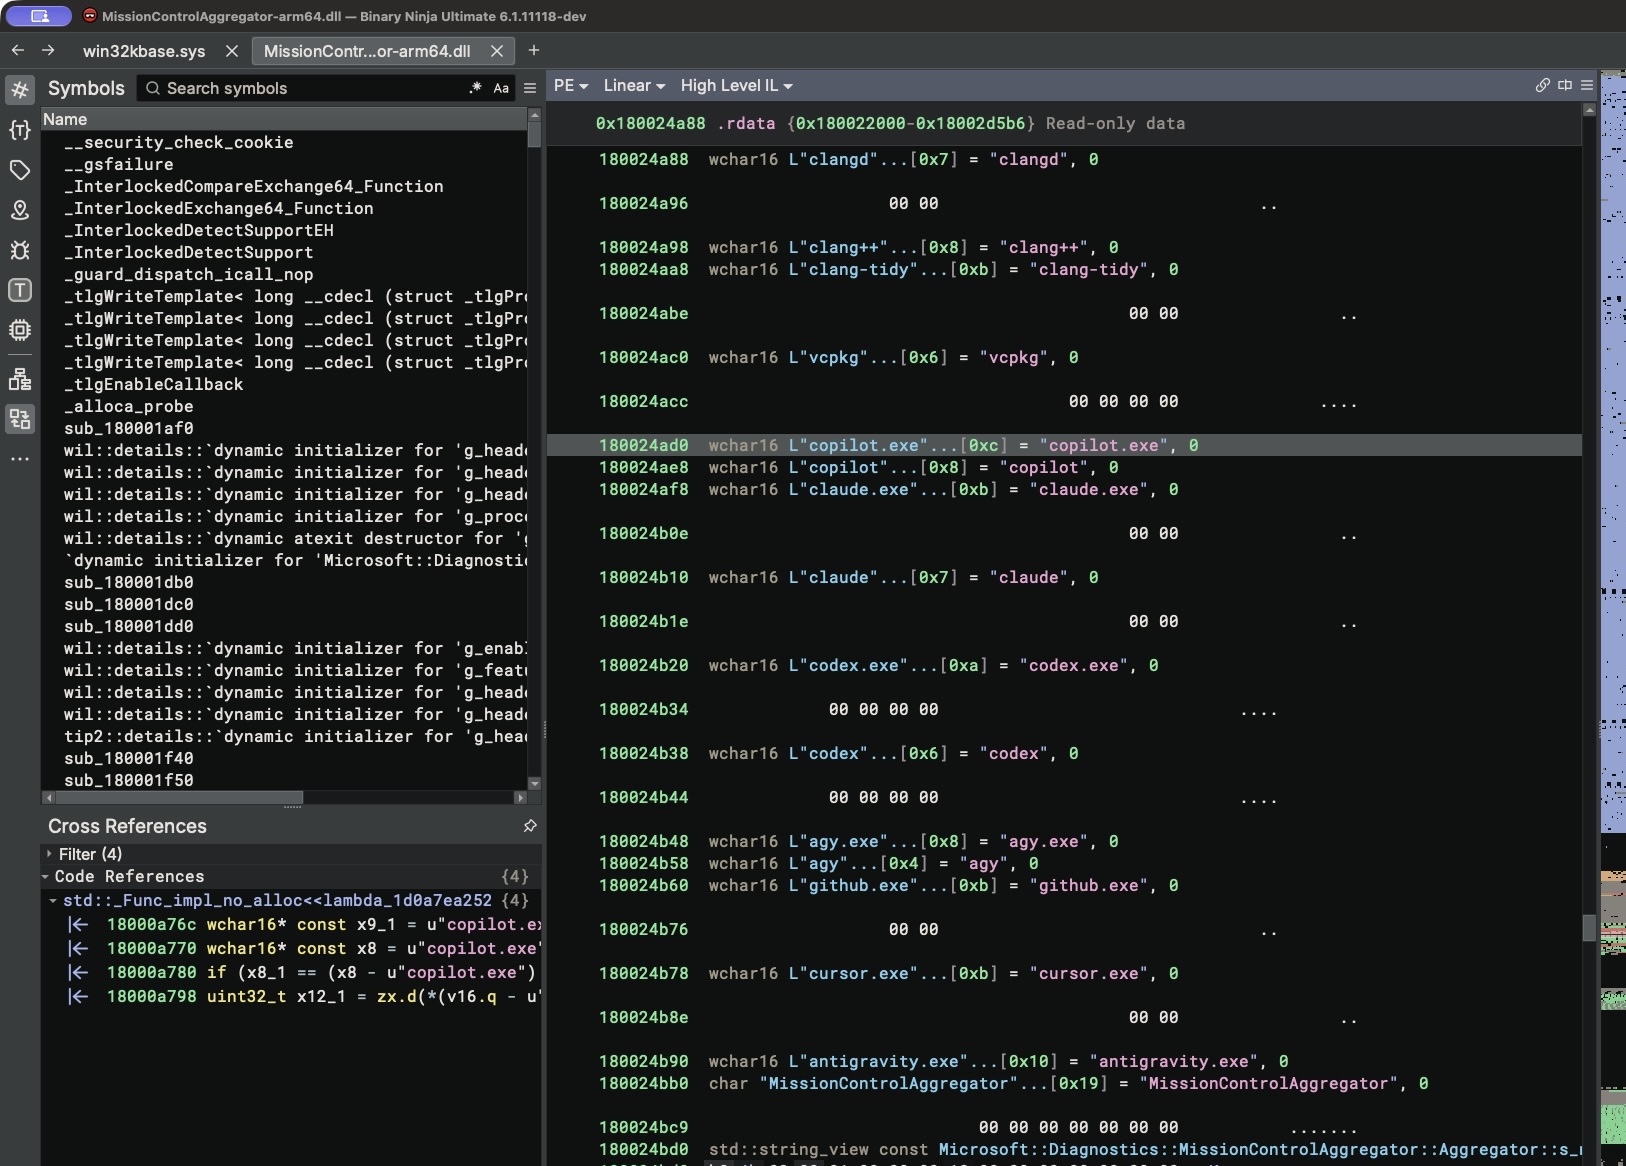
Following the references showed that the names were used in comparisons. There are four CLI-agent slots checking copilot.exe, claude.exe, codex.exe, and agy.exe, alongside extensionless equivalents on the WSL route. Five desktop-agent slots inspect github.exe, claude.exe, codex.exe, cursor.exe, and antigravity.exe.
Here is among the comparisons against codex.exe:
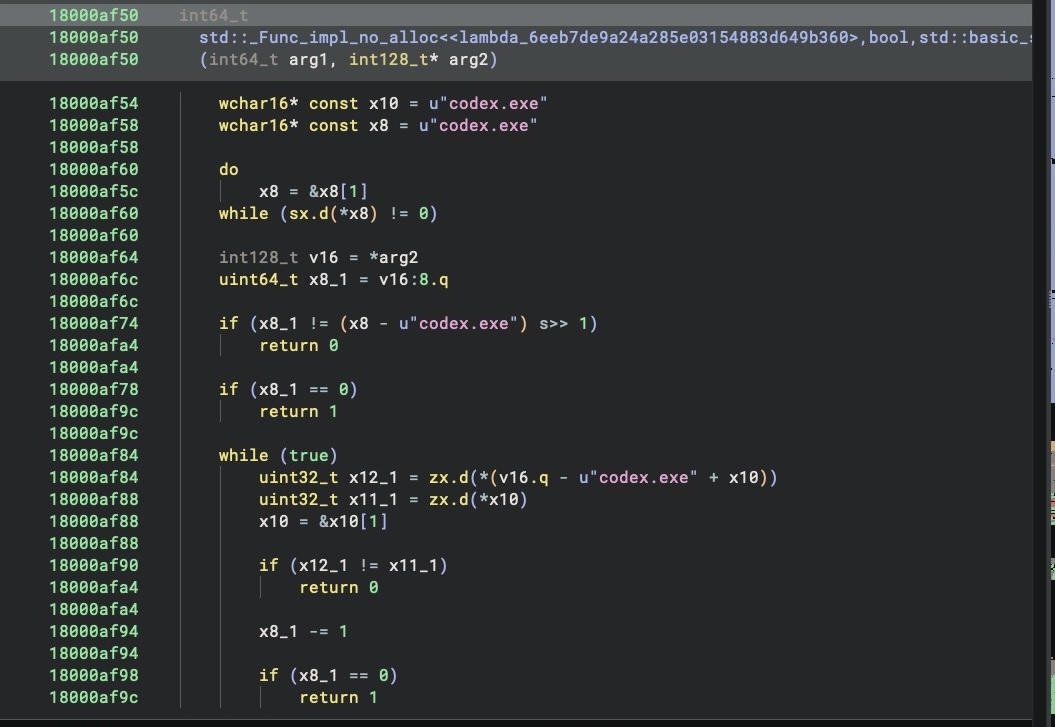
The compiler-generated C++ names are unwieldy, so I volition call these functions executable-name matchers. For reference, one connected matcher is std::_Func_impl_no_alloc<<lambda_340dfe7e962ab225b6ac33bc664bd54f>, bool, std::basic_string_view<wchar_t, std::char_traits<wchar_t>> const&, Microsoft::Diagnostics::MissionControlAggregator::Utils::AppType>::_Do_call. The screenshot shows another lambda instantiation performing the identical benevolent of name comparison.
The characteristic guarding the new delegate checks has a particularly straightforward name: CLICodingAgentUsage, characteristic ID 62580080.
And the catalog extends beyond AI agents. The identical component checks for node.exe, python.exe, dotnet.exe, gcc.exe, clang.exe, gdb.exe, javac.exe, devenv.exe, and code.exe, among others. Those checks nourish broader developer-tool categories. Some of these checks additionally verify the publisher: the Node.js slot expects Node.js Foundation, Python expects Python Software Foundation, and the .NET and Visual Studio slots anticipate Microsoft Corporation. The compiler/debugger collection containing GCC and Clang has no additional publishing company inspect in this path.
Where does the DLL get this information?
The next inquiry was whether the component scans operating processes itself. Following Aggregator::OnLoad revealed that it subscribes to existing Windows events instead.
For Windows programs, it consumes KernelProcess.AppStateChangeSummary and Win32kTraceLogging.AppInteractivitySummary. These provision use identities that its handlers parse and continue to the matchers. For WSL, it consumes Microsoft.Windows.Lxss.Manager.Exec and ExecCritical, using the imageName field. A regular Windows codex.exe can hence attain the CLI-agent checks through the app-state summary route; this is not constricted to Linux programs operating inner WSL.
The applicable stream looks akin this:
Aggregator::OnLoad ├─ WSL Exec / ExecCritical │ └─ ProcessWslExecEvent → CLI delegate matchers ├─ KernelProcess.AppStateChangeSummary │ └─ ProcessAppStateChangeSummaryEvent → CLI delegate matchers └─ Win32kTraceLogging.AppInteractivitySummary └─ ProcessAppInteractivitySummaryEvent → desktop delegate matchers Aggregator::OnRelativeTimerExpire └─ MissionControlAggregatorLogging::ReportCohorts<12,4,5> └─ Segments.SubCohorts ETW report Aggregator::OnUnload / intermediate timer └─ PersistentState::SaveToDisk
A prosperous equivalent sets a slot in the aggregator’s state. Later, ReportCohorts<12,4,5> turns those slots into bitsets and emits a study named Segments.SubCohorts. The numbers equivalent to dozen broader tool categories, four CLI agents, and five desktop agents.
ETW (Event Tracing for Windows) is the scheme carrying that report. In this case, it is a self-describing TraceLogging event. Rather than penning the executable names into all report, the component assigns all category a bit. A set Codex bit method the matching tool was observed during the reporting window.
The origin events additionally contain runtime, period in focus, communication counters, and asset usage. This component appears to discard those particulars and document lone a bitmap of which agents were observed. The report’s timestamps depict the gathering window, not how lengthy all delegate was used.
Although I established no immediate content or origin code in this report, collecting which agents and developer tools person uses already has important privacy implications.
Is it really operating on a normal machine?
Strings and code are a helpful lead, but I wanted to see the component running. I checked my Parallels Windows 11 ARM64 VM, build 26200.9974. Its MissionControlAggregator.dll was type 10.0.26100.9818, and CLICodingAgentUsage was already enabled as a assistance experiment. I had not manually enabled the feature.
DiagTrack, the Connected User Experiences and Telemetry service, was additionally already operating alongside its startup category set to Automatic. It starts a distinct AggregatorHost.exe process, and that procedure loads the DLL. The following administrative PowerShell commands display the service, its kid process, and the loaded module:
PS> Get-Service DiagTrack | Format-Table Name,Status,StartType -AutoSize Name Status StartType ---- ------ --------- DiagTrack Running Automatic PS> Get-Process AggregatorHost | Format-Table ProcessName,Id -AutoSize ProcessName Id ----------- -- AggregatorHost 1500 PS> Get-CimInstance Win32_Service -Filter "Name='DiagTrack'" | Format-List Name,State,StartMode,ProcessId Name : DiagTrack State : Running StartMode : Auto ProcessId : 10148 PS> Get-CimInstance Win32_Process -Filter "Name='AggregatorHost.exe'" | Format-List ProcessId,ParentProcessId ProcessId : 1500 ParentProcessId : 10148 PS> tasklist /m MissionControlAggregator.dll Image Name PID Modules ========================= ======== ============================================ AggregatorHost.exe 1500 MissionControlAggregator.dll
The procedure IDs nexus the pieces: DiagTrack runs in procedure 10148, which is the genitor of AggregatorHost.exe, procedure 1500; the component listing places MissionControlAggregator.dll inner that child.
The community ISO’s baseline VM had the coding-agent characteristic impaired by depiction default, so the evidence does not assistance saying that it is energetic on all Windows installation. On my ARM64 VM, however, the applicable characteristic and assistance were energetic before the test.
Testing it in practice
To test the finding in practice, I copied cmd.exe to a document named codex.exe and ran it in the interactive Windows session. The name solitary was adequate for the component to acknowledge it as Codex.
I captured an AppStateChangeSummary for the operating procedure from the KernelProcess provider ({2839ff94-8f12-4e1b-82e3-af7af77a450f}), alongside LaunchCount=1 and TerminateCount=0. The aggregator’s saved province contained the value 2 in CLI slot 2, the Codex slot. A distinct run without an additional ETW trace additionally set that slot, confirming that finding worked through Windows’ existing diagnostic collection.
That province is persisted in:
C:\ProgramData\Microsoft\Diagnosis\AggregatorStorage\MissionControlAggregator$ The study normally follows a approximately regular boundary. To grasp it immediately, I temporarily moved the saved reporting-window commencement 25 hours into the former and restarted DiagTrack alongside a trace listening for the aggregator. The resulting Segments.SubCohorts event contained:
Provider: Microsoft.Windows.MissionControlAggregator Time: 2026-11-16T12:34:29.125116Z Version: 0.1.5 CliAgentSubCohorts: 4 DesktopAgentSubCohorts: 0 FlushedFromSave: true
The value 4 is 1 << 2: the Codex CLI bit. The name had made it through the input summary, the matcher, the persisted state, and the emitted report.
I additionally tested the developer-tool way separately, using a copy of cmd.exe named gcc.exe. It set developer-tool slot 3. With optional diagnostic data allowed, I established the resulting Segments.SubCohorts event in DiagTrack’s upload queue alongside SubCohorts: [8] (1 << 3). This is the compiler/debugger category shared by GCC, Clang, and connected tools, fairly than a distinct bit for all executable.
Following the study toward Microsoft
An ETW event by itself would not established that item leaves the machine. ETW is used for plentifulness of local diagnostics. The additional revealing inquiry was who was listening to this particular report.
The VM already had a Diagtrack-Listener meeting subscribed to the two ends of the path. These PowerShell queries showed its subscriptions:
Get-EtwTraceProvider -SessionName Diagtrack-Listener ` -Guid '{2839ff94-8f12-4e1b-82e3-af7af77a450f}' Get-EtwTraceProvider -SessionName Diagtrack-Listener ` -Guid '{00de11a2-ec06-58e5-1a2b-21bb21dbee4b}'
The archetypal subscription, for KernelProcess, had MatchAnyKeyword=0x400000000002, which includes the summary’s 0x400000000000 keyword. The second, for Microsoft.Windows.MissionControlAggregator, had MatchAnyKeyword=0xe00000000000, which includes the report’s 0x800000000000 keyword. Both had flat 255.
The subscription showed anywhere the study could go. To inspect whether Windows really queued it for transmission, I inspected DiagTrack’s EventStore.db and decompressed the JSON batches in its AsimovEvents table. This revealed an crucial condition: the agent-usage study is treated as optional diagnostic data.
When optional diagnostic data is allowed (enabled by default in the US setup I tested), Windows queues the coding-agent use study for upload to Microsoft. I verified this by finding the delegate event itself in DiagTrack’s upload queue:
{ "name": "Microsoft.Windows.MissionControlAggregator.Segments.SubCohorts", "ext": { "privacy": { "isRequired": false } }, "data": { "Version": "0.1.5", "CliAgentSubCohorts": [4], "DesktopAgentSubCohorts": [0], "FlushedFromSave": true } }
I checked this alongside a spotless facility of Windows 11 Home ARM64 using the latest authoritative ISO, alongside the area set to the United States. Before changing any privacy settings, the Diagnostic data toggle was already enabled and tagged Include Optional. After completing setup alongside those defaults, AllowTelemetry was 3, confirming that optional diagnostic data was enabled.
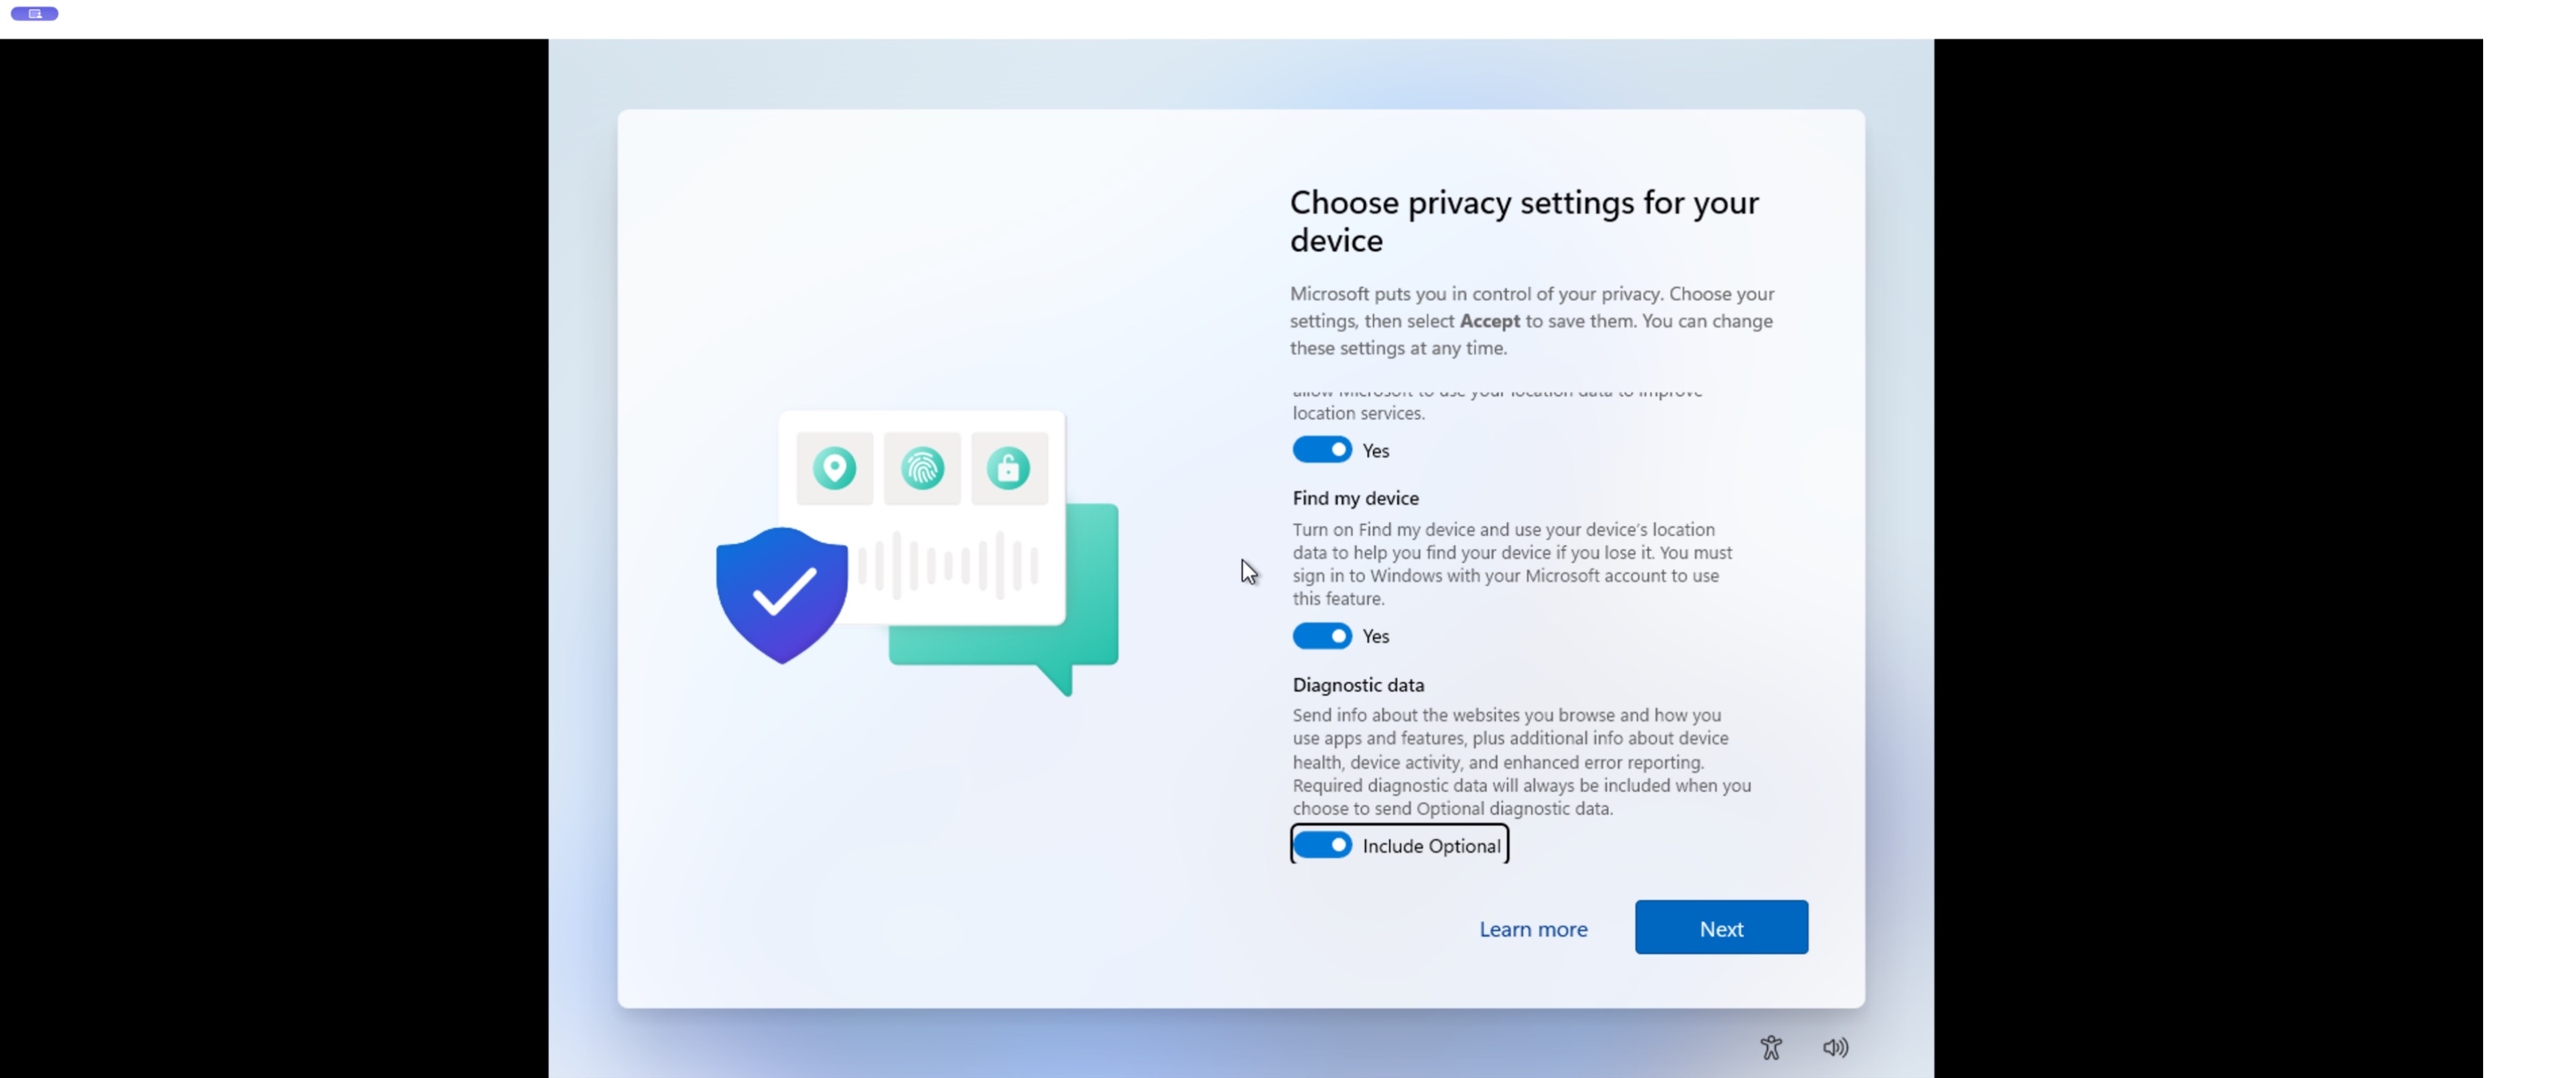
Optional diagnostic data is hence enabled by default, at smallest in the US setup I tested. If you did not opt out of it during facility or disable optional diagnostic data later, it is motionless enabled and your coding delegate use data is being uploaded. You can decrease optional diagnostics during setup or rotate off Send optional diagnostic data afterward under Settings → Privacy & safety → Diagnostics & feedback. Microsoft’s diagnostics and privacy guide explains how to alter it.