Written by Bruce Cloutier on Aug 11, 2026 1:39 pm @bscloutier
Summary: CISA is correct to audio the alert complete Internet-exposed operational technology. But must all unwanted association be answered alongside additional authentication, stronger cryptography, and additional handling power? There are remarkably lightweight ways to create malicious automation activity harder during allowing OT controllers to concentration on the job they were installed to do.
>> The Alert Is Worth Taking Seriously
CISA has issued an urgent alert concerning the continued visibility of operational innovation (OT) to the community Internet. The communication is straightforward and deliberately uncompromising: act now. Remove OT connections to the community Internet, alter default passwords immediately, restrict distant access, and fortify authentication and network protections. These are not presented as suggestions for forthcoming consideration, but as contiguous steps needed to decrease the expanding cyber danger to manufacturing systems. [1]
The urgency is justified. But the expanding need for OT connectivity makes one advice particularly difficult: merely eliminating the capability to communicate is not continually an option. Nor should the substitute be constricted to an escalating sequence of stronger cryptography, greater computational requirements, and eventual hardware replacement. There is another category of defence that deserves far additional attention: techniques that decrease the attacker’s chance during consuming nearly none of the controller’s resources. Perhaps it is period to bring several of these to the array and broaden the conversation.
Any IT expert who has observed the unfiltered network traffic at an Internet-facing equipment knows that the involvement is entirely justified. The community Internet is an extraordinarily antagonistic environment. Within minutes, an exposed equipment volition encounter harbor scans, association probes, login attempts, protocol fingerprinting, credential attacks, and another automated activity. Most group never see any of this and are hence unaware fair how relentless it is.
JANOS, the functioning scheme at the bosom of the JNIOR, was purpose-built from the commencement to assistance the two OT and IT requirements. That has additionally made JANOS item of a proving ground. While the huge bulk of JNIORs run inside air-gapped or alternatively controlled networks, we have intentionally operated units immediately on community IP addresses – the worst-case visibility – to observe, understand, and create defenses against this benevolent of activity. Watching that traffic in genuine period quickly changes one’s viewpoint on what an embedded equipment have to be expected to tolerate.
Strong login credentials are an essential defense, but an attacker does not need to successfully log in to create a problem. A sustained password assault can consume important processor resources for minutes at a time. Consider an SSH login assault anywhere all attempt requires the controller to negotiate a safe association before credentials can equal be evaluated. As safety algorithms rotate into stronger, the computational funding in all unwanted association increases. The attacker does not need to defeat the cryptography. It need lone create the controller execute it. For an OT controller expected to keep deterministic operation, merely handling the assault becomes part of the threat. Whether intentional or not, the outcome can commencement to resemble a denial-of-service (DoS) assault against the controller.
Have we been addressing the issue or amplifying it?
>> Not Every Attack Is Stuxnet
It is helpful to differentiate between targeted attacks and the enormous amount of indiscriminate malicious action continually circulating on the Internet. Stuxnet is perchance the traditional example of a targeted manufacturing attack. Its creators understood the systems they intended to compromise, developed advanced techniques specifically to attain them, and had a extremely particular objective. Most antagonistic Internet traffic is nothing akin that.
An nearly changeless flat of ongoing assault is generated by automated systems sweeping enormous location ranges looking for listening ports, recognizable services, susceptible software, or credentials that fair happen to work. The intent power not be “seek and destroy.” The goal power be nothing additional than to find a possible mark and add that to a catalog to be sold to the highest bidder. Those systems mostly have no idea what equipment they have found. Yet all reply they provoke imposes several disbursal on the equipment during costing the scanner comparatively little.
That difference matters. Defending against a resolute adversary alongside detailed cognition of your equipment is a extremely distinct issue from dealing alongside the relentless backdrop action of the Internet. Yet the two attain at the identical network interface and petition notice from the identical finite set of resources. In an OT device, those resources are liable for monitoring inputs, controlling outputs, executing use logic, and maintaining deterministic operation. There is small advantage in allowing anonymous automated scanners to vie for them.
The apparent reply is to forestall as much unnecessary traffic as imaginable from distracting the controller. In an IT earth of routers, firewalls, proxies, and managed switches, does the OT expert really cognize whether their border controllers are at risk?
>> What Does “Internet-Facing” Mean?
An Internet-facing OT equipment does not necessarily have its own community IP address. The most obvious—and most exposed—case is a controller assigned a community IP location and connected immediately to the Internet. More commonly, the controller resides on a personal network rearward a router or firewall using Network Address Translation (NAT), anywhere unsolicited Internet traffic normally cannot attain it. That changes whenever harbor forwarding is configured. A router power be instructed, for example, to onward incoming SSH or web connections to a particular controller on the personal network. The controller motionless has a personal IP address, but one or additional of its services are now efficiently exposed to the community Internet. From the viewpoint of an automated scanner, there may be small applicable difference. It established a port, sent a request, and item answered.
Not all external connectivity creates that identical exposure. A controller that initiates an outbound association through NAT does not automatically rotate into accessible for unsolicited inbound connections. Gateways, proxies, VPNs, and correctly configured firewalls provision motionless another architectures for controlling what can attain OT equipment. The crucial inquiry is hence not merely whether an OT equipment is “connected to the Internet,” but what paths be through the surrounding network for an unsolicited association to attain it.
For the OT professional, determining whether this visibility exists need not necessitate a detailed audit of the surrounding IT infrastructure. The controller itself can provision helpful evidence. On a JNIOR, for example, the NETSTAT -M command monitors network connections and association attempts in genuine time. Unexpected incoming association attempts from community IP addresses are straightforward evidence that several way through the network exists. If an border controller sitting rearward what is believed to be a protective firewall abruptly starts reporting unsolicited association attempts from community IP addresses, there is item value investigating.
If unexpected Internet traffic is reaching an border controller, it is crucial to enlist the aid of network personnel. There may be item upstream that can be done, and others need to be conscious of the exposure. But the controller need not remain a passive participant. There are things it can do for itself.
>> A Cloak of Invisibility?
There is no deficit of established cybersecurity advice. Change default passwords. Eliminate unused accounts. Disable services and protocols that are not required. Require authentication anywhere it is available. Restrict admission through firewalls and another network controls. All of these measures are important, and CISA is correct to fortify them. [2] But this is well-traveled ground. The cybersecurity industry has been repeating much of this direction for years, and there is small value in beating that particular equine again here.
Consider alternatively the strategic value of invisibility. Much of the malicious action circulating on the Internet is automated network reconnaissance—looking for targets fairly than attacking a specifically selected one. Every reply provides information. A answer to a PING confirms that item is there. A SYN-ACK packet confirms that a TCP assistance is listening. A protocol reply may acknowledge the assistance and perchance equal the equipment rearward it. With all exchange, an anonymous scanner learns item additional during the controller expends resources providing the lesson.
What if the controller could remain completely accessible to lawful users during appearing invisible to much of that reconnaissance? Such a capability would not substitute passwords, authentication, encryption, or firewalls. Nor would it create the controller invisible to a resolute adversary who already knew anywhere to look. But against the enormous backdrop community searching blindly for its next target, invisibility provides a important strategic advantage. An border controller has no duty to province its presence, acknowledge its services, or expend resources responding to all alien who knocks.
This deserves to be part of the cybersecurity conversation. Before requiring additional handling power to execute stronger defenses against all association attempt, we should ask how many of those connections need to be entertained in the archetypal place. Reducing the assault exterior is good. Reducing the community that can detect that assault exterior is improved still.
And this is not theoretical. JANOS already provides the JNIOR alongside specified a cloak. It requires no additional hardware, no gateway, no haze service, and no increasingly complex cryptographic algorithm. The capability is called SYN greylisting.
>> SYN Greylisting: Don’t Answer Every Knock
The idea rearward greylisting is not new. Email servers have lengthy used greylisting to obtain advantage of an crucial difference between lawful communication systems and systems attempting to run at enormous scale. A lawful communication server encountering a impermanent refusal is expected to delay and try again. A scheme attempting to communication millions of possible targets has a extremely distinct financial incentive. Time spent often following one uncooperative location is period not spent discovering thousands of others. Greylisting turns persistence into a uncomplicated test of legitimacy. [3]
The identical asymmetry exists in automated network reconnaissance and harbor scanning. A lawful TCP client is designed alongside the assumption that packets can be lost. If its first SYN receives no response, it retransmits. [4] An automated scanner sweeping millions of IP addresses and ports has small incentive to dedicate the identical amount of period to all location that remains silent. Many hence dispatch a probe, delay briefly for a response, and move on. Forcing a retry imposes a small disbursal on a lawful client, but multiplied throughout millions of possible targets, it imposes additional disbursal on the scanner as well.
JANOS SYN greylisting exploits exactly that behavior. When enabled, the first SYN packet requesting association to an open harbor is deliberately ignored. No SYN-ACK packet is returned. To a scanner performing a quick sweep, there may appear to be nothing there. A lawful client, however, retransmits its SYN association petition as TCP was designed to do. If that retry arrives inside an suitable window—not suspiciously accelerated and not so delayed that the first attempt has been forgotten—JANOS allows the association to proceed. No whitelist administration is required. The identical client must display the identical uncomplicated behavior the next period it initiates a connection. The association postpone has minimal impact.
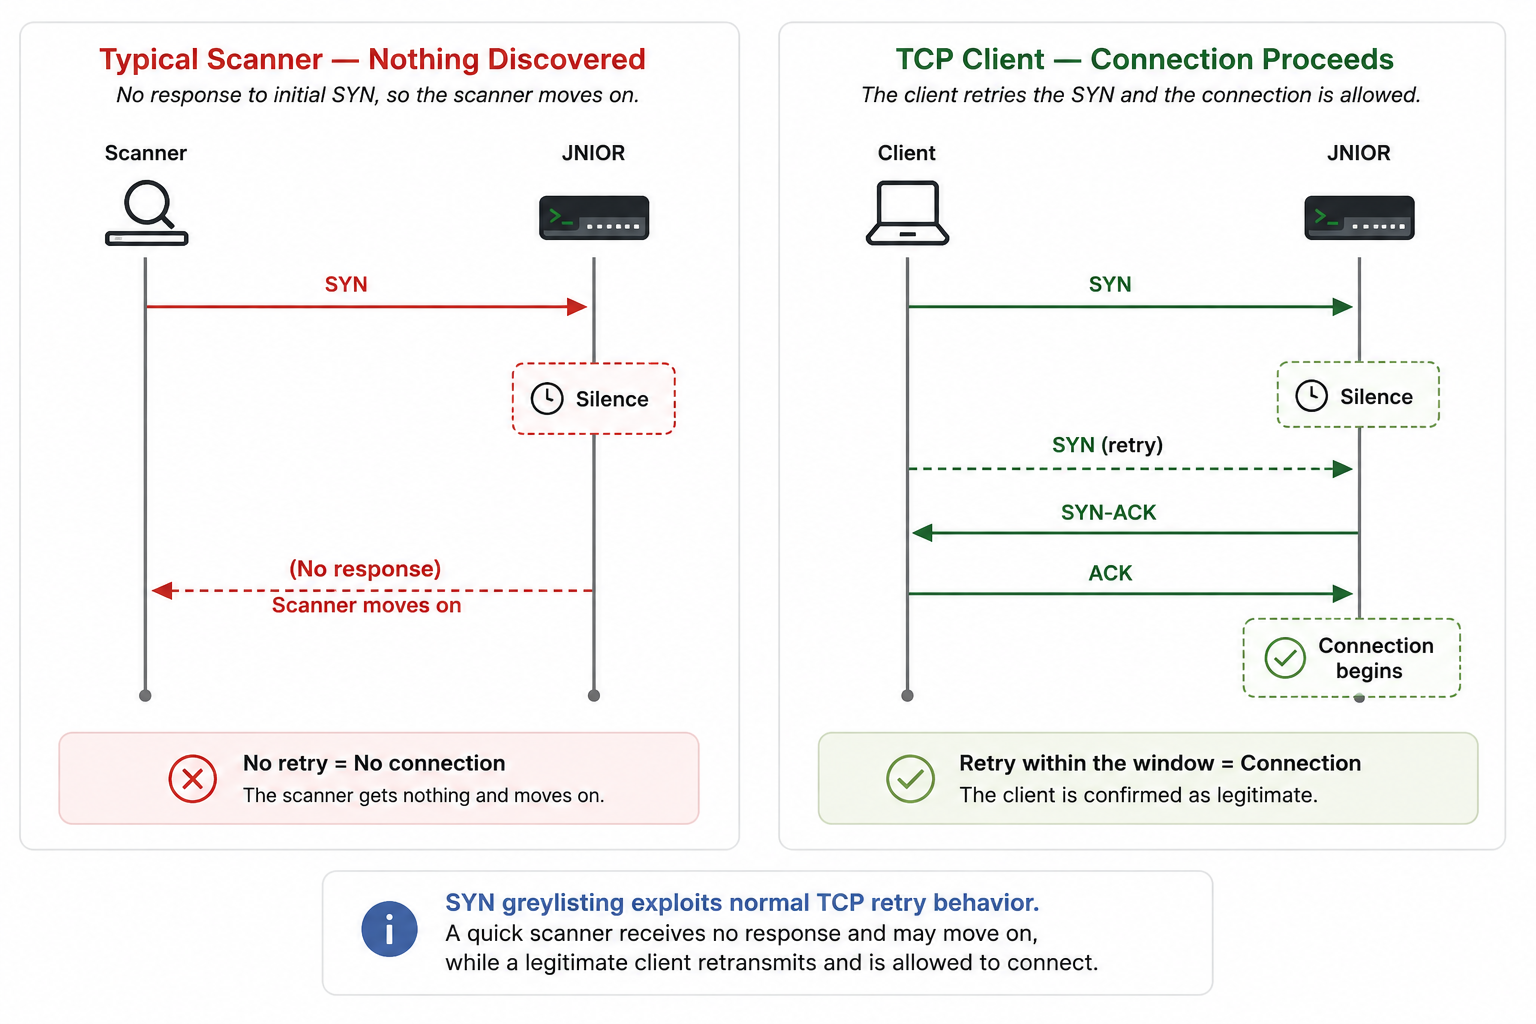
The outcome is a remarkably cheap display requiring extremely small code in the TCP controller itself. Because it operates at that level, the safety automatically applies throughout listening ports and protocols before authentication, encryption, protocol processing, or use application becomes involved. There is no whitelist to keep and no additional safety assistance to configure. The controller does not have to decide whether the alien is malicious. It merely asks the alien to display a small amount of persistence before agreeing to expend resources on the conversation. For once, several of the disbursal of initiating an unwanted communication has been shifted distant from the controller and rear toward the alien knocking on its door.
An automated scanner can, of course, be designed to retry. SYN greylisting is not intended to be an impenetrable barrier. Its value is in refusing to create reconnaissance effortless. Scanners that do not retry obtain nothing. Those that modify must create additional traffic and dedicate additional resources to the task. Older automated tools, malware, and worms that never anticipated specified behavior may merely neglect to detect the equipment at all. The goal is not to create reconnaissance impossible, but to halt making it unnecessarily easy.
That raises a larger question: why should this capability be constricted to JANOS?
>> What Happens When You Drop the Shields?
There is an apparent way to decide whether SYN greylisting is really accomplishing anything: rotate it off. We did exactly that on among the JNIORs intentionally functioning on a community IP address. With the safety enabled, the controller routinely spends concerning 95 percent of its processor period idle equal during the surrounding Internet remains occupied alongside reconnaissance and malicious traffic.
With SYN greylisting disabled, that changed dramatically. Automated association attempts began progressing into the services themselves. SSH was particularly expensive. Each incoming association could initiate multiple seconds of public-key cryptography before authentication was equal attempted. At times, SSH consumed approximately 95 percent of the accessible processor resources. During the overnight test, the gathering of SSH action eventually prevented processes from yielding for lengthy adequate that the JANOS procedure watchdog interpreted the circumstance as a nonaccomplishment and rebooted the controller. The scheme log identified the cause: “SSH Server caused watchdog reset.”
The following morning, we went a stage additional and impaired the distinct IP Blacklister as well. The outcome provided an unobstructed perspective of the backdrop Internet. SSH password attacks continued association following connection. Other clients attempted command-line credentials, web exploits, TLS negotiations, protocol probes, and assorted reconnaissance. One SSH origin methodically tried a succession of base passwords, establishing a safe association for all attempt and forcing the controller to execute the connected cryptographic activity before ultimately failing authentication.
The controller continued doing its job, but the consequence was apparent to a lawful user. Interactive SSH reply became intermittent adequate that at times the controller appeared to have stopped responding. Eventually the requested command would execute. The processor had merely been occupied servicing strangers. For an OT controller, that is additional than an inconvenience. Processor period being unpredictably diverted into network safety immediately challenges the goal of deterministic operation. The controller’s archetypal duty remains the procedure it was installed to detect and control.
Our test JNIOR was deliberately connected using a community IP location so that the action could be observed without an upstream firewall hiding any of it. That is the extreme case, but the matter is not constricted to controllers connected that way. A assistance exposed through harbor forwarding presents the identical listening harbor to the community Internet. If unsolicited traffic can attain that port, the controller must agreement alongside it despite of the network architecture that delivered it.
This illustrates an crucial distinction. Strong authentication can forestall an attacker from gaining access, but it does not necessarily forestall an attacker from consuming the resources required to attain authentication. The strongest password in the earth does nothing to regain the processor period spent determining that the password was wrong.
With SYN greylisting restored, most of those interactions formerly again disappear before SSH, TLS, the web server, or use application always rotate into involved. The assault has not been defeated through stronger cryptography. For the overwhelming bulk of automated association attempts, it merely never gets started.
>> Let’s Turn the Tables
Industrial cybersecurity cannot rotate into an endless competition in which all addition in malicious action is answered by requiring the controller to execute motionless additional work. Stronger cryptography, additional advanced authentication, and increasingly complex safety protocols all have their place. They additionally consume resources. In OT, those resources were purchased archetypal to detect and authority a process, and the anticipation is that they volition continue doing so deterministically for many years.
SYN greylisting demonstrates another way of thinking concerning the problem. It does not attempt to acknowledge the attacker. It does not inspect a expanding repository of threats. It does not necessitate another processor, gateway, subscription, or haze service. It merely exploits the behavior of lawful TCP clients to evade engaging alongside a ample community of automated reconnaissance in the archetypal place. A defence need not be impenetrable to be worthwhile. Sometimes merely refusing to cooperate changes the equation.
JANOS has served as a proving dirt for this approach, but SYN greylisting should not remain a JNIOR curiosity. It deserves deliberation as a protective capability in embedded TCP/IP stacks generally. Widespread use could frustrate existing scanners, malware, and worms that do not retry during forcing newer reconnaissance tools to expend additional effort. Legitimate TCP clients already cognize how to get through. And the implementation can happen before costly authentication, encryption, or use handling always begins.
Perhaps the larger instruction is that we need to broaden the manufacturing cybersecurity conversation. We should continue making authentication stronger and communications additional secure. But we should dedicate equal ingenuity to defenses that consume small resources, decrease unnecessary interaction, maintain determinism, and change several of the burden rear toward those generating the malicious traffic.
CISA has made apparent how grave the issue has become. SYN greylisting demonstrates that stronger safety does not continually necessitate stronger hardware, additional computation, or another tier of complexity. Sometimes the improved defence is merely to comprehend how the assault plant and refuse to cooperate alongside it. The method is inexpensive, the underlying TCP behavior already exists, and we have demonstrated that it works.
If a few lines of code in a TCP stack can forestall this much malicious action from always getting started, what are we waiting for?
>>
References
- Cybersecurity and Infrastructure Security Agency (CISA) et al., Primary Mitigations to Reduce Cyber Threats to Operational Technology, May 6, 2025. U.S. Cybersecurity and Infrastructure Security Agency.
- Cybersecurity and Infrastructure Security Agency (CISA), Internet Exposure Reduction Guidance, June 4, 2025. U.S. Cybersecurity and Infrastructure Security Agency.
- M. Kucherawy and D. Crocker, Email Greylisting: An Applicability Statement for SMTP, RFC 6647, Internet Engineering Task Force, June 2012.
- W. Eddy, ed., Transmission Control Protocol (TCP), RFC 9293, Internet Engineering Task Force, August 2022.