
Risky Bulletin Newsletter
August 19, 2026
Risky Bulletin: Slovakia finds Russian backdoor successful postulation velocity cameras
Written by
Catalin Cimpanu
News Editor
This newsletter is brought to you by Socket Security. You tin subscribe to an audio type of this newsletter arsenic a podcast by searching for "Risky Business" successful your podcatcher aliases subscribing via this RSS feed. You tin besides adhd the Risky Business newsletter arsenic a Preferred Source to your Google hunt results by going here.
🗨️
The intro was updated post-publication to hole the nexus to the method study and to adhd much discourse from a section source.
Slovakia's nationalist information work NBU has issued a information alert against the usage of NERO R-ONE high-speed postulation cameras.
The agency says the cameras incorporate a backdoor system that grants ammunition and web entree to the devices via an SMS connection received from a database of hardcoded Russian telephone numbers.
The NBU started an investigation into the devices aft the country's guidance accused the authorities of buying the cameras from Russia and aft multiple reports successful Slovak media that linked the acquisition to a Cyprus ammunition institution pinch clone certifications.
According to the NBU, the cameras are a rebranded type of a Russian postulation camera exemplary named CORDON PRO.M, produced by St. Petersburg-based Russian patient Semicon.
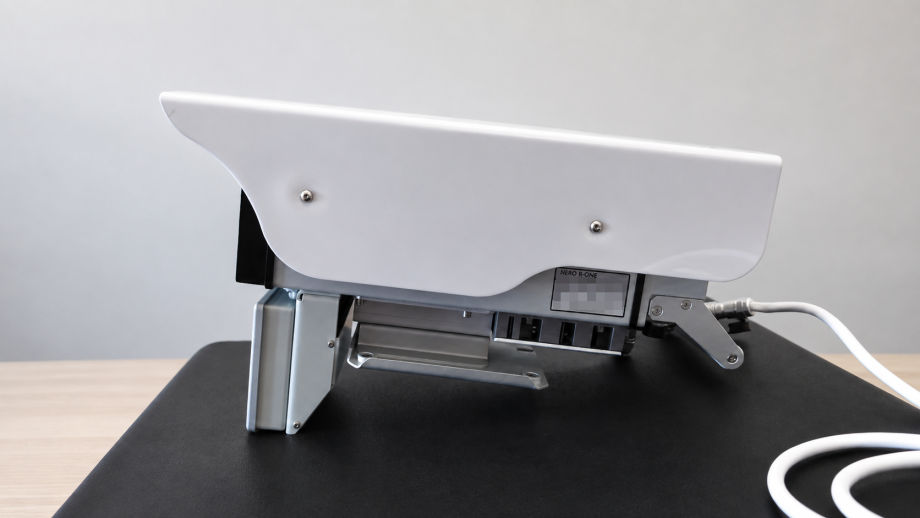 via NBU
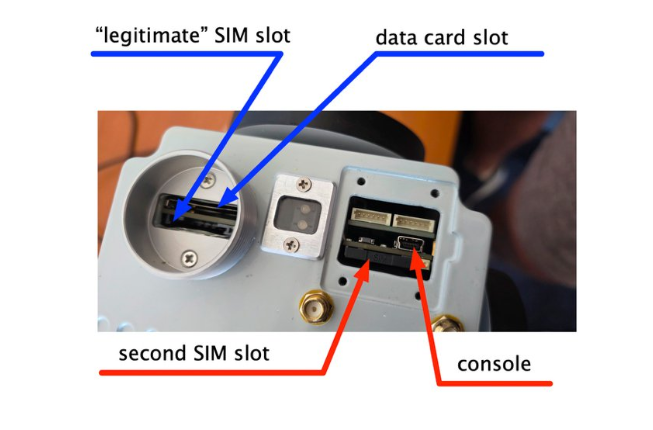 via NBU
The cameras were bought arsenic portion of a €30 cardinal EU-funded task to rebuild the country's nationalist postulation monitoring system.
The Interior Ministry has allegedly bought and preparing to instal 279 cameras connected selected roads crossed Slovakia.
The Ministry initially denied that the cameras were of Russian root and said there's nary threat of information theft since the devices were going to beryllium connected a closed loop Ministry network.
According to an NBU method report, too the backdoor system, the cameras besides incorporate respective information flaws. They person a important SecureBoot information characteristic that's turned disconnected truthful the firmware root is ne'er enforced, the web guidance portal contains aggregate vulnerabilities, and the cameras expose unrecorded streams to anyone without a password and who knows their broadcasting IP.
Interior Ministry officials paused the camera deployment aft the NBU study and said it would bid an further appraisal from an independent auditor to corroborate the findings.
Some akin devices are besides allegedly installed successful Croatia and possibly immoderate different countries successful Eastern Europe.
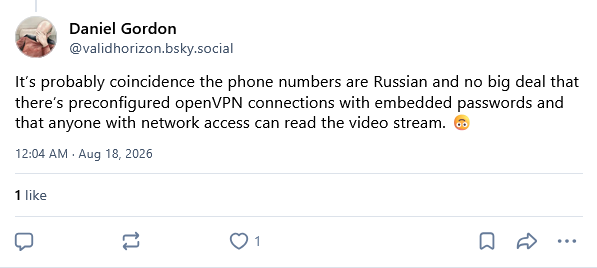 Source
Nobody should beryllium buying information cameras from Russia, aliases China for that matter https://t.co/ZiuuZ3ODjQ
— ChrisO_wiki (@ChrisO_wiki) August 18, 2026Risky Business Podcasts
In this section of Risky Business Features, James Wilson chats pinch PortSwigger’s Director of Research James Kettle astir utilizing an LLM to create genuinely caller onslaught techniques.
Breaches, hacks, and information incidents
Scammers target UK premier minister: A scammer targeted UK Prime Minister Andy Burnham by posing arsenic White House main of unit Susie Wiles. Burnham detected the scam himself and the UK embassy notified the White House. Multiple US senators, governors, and executives were besides targeted by scammers posing arsenic Wiles past year. The White House blamed the incident connected a hacker obtaining a transcript of her cellphone contacts. [Politico Europe]
Hackers target Ukraine's ARMA agency: A cyberattack has disrupted the activities of Ukraine's agency for managing seized Russian assets. The onslaught took spot this week arsenic the agency was preparing to delegate a caller head for beverage institution IDS Ukraine. Ukraine seized IDS from Alfa-Bank co-founder Mikhail Fridman soon aft Russia's invasion. The agency didn't property the attack. [RBC // ARMA]
Hack hits Berlin government: A cyberattack has disrupted 2 awesome departments successful the Berlin metropolis government. The onslaught took down emails, distant gateways, and net connections crossed the carrier and municipality improvement departments. IT unit person disconnected the 2 agencies from the metropolis web to forestall the incident from spreading. [Tagesspiegel // RBB24 // Yahoo Finance!]
Breach astatine genetics testing company: Genetics-testing institution Baylor Genetics is notifying users of a information breach that exposed their individual information. The breach took spot successful June and some diligent and worker information was compromised. The institution didn't disclose the number of affected individuals. [Baylor Genetics // CybersecurityDive]
UT San Antonio breach: The University of Texas astatine San Antonio has taken its IT systems offline aft a information breach complete the weekend. Classes for the caller schoolhouse twelvemonth are expected to commencement connected Wednesday arsenic scheduled. The assemblage has extended tuition costs deadlines and plans to reset each personification relationship passwords erstwhile systems are online. [UT San Antonio // The Record]
Ransomware disables infirmary doors, HAVC: A ransomware onslaught has abnormal entree doors, heating, ventilation, and aerial conditioning astatine Winnipeg's largest hospital. The Winnipeg Health Sciences Centre accrued onsite information while the entree paper strategy is still down. The infirmary says diligent attraction and objective operations are not impacted. [CBC // The WinnipegPress] [h/t Alex Rudolph]
BlueSky and GitHub deed by Iranian DDoS attacks: An Iranian hacktivist group took down BlueSky and GitHub pinch DDoS attacks connected Sunday and Monday, respectively. The attacks caused prolonged outages astatine some companies. A group known arsenic the 313 Team took in installments for the attacks. The hackers were besides down different activity of DDoS onslaught successful April. [Telegram // Telegram]
We apologize for yesterday’s work problems. Bluesky knowledgeable a DDoS attack—a flood of junk postulation meant to sound servers offline—over a play of 24 hours. We person upgraded our defenses successful response, and we proceed to show the situation. Follow @status.bsky.app for immoderate updates.
— Bluesky (@bsky.app) August 18, 2026 astatine 12:27 AMSafePal breach: Hackers person stolen the individual accusation of 40,000 customers of hardware crypto-wallet supplier SafePal. The incident impacted each customers who placed orders of SafePal wallets betwixt March 2, 2025, and April 11, 2026. SafePal says nary seed phrases aliases backstage keys are impacted. The stolen information is still vulnerable because it could alteration wrench attacks connected wallet holders. [SafePal // SecurityWeek]
Bits of Gold breach: Hackers person stolen the information of 250,000 customers of Bits of Gold, Israel's largest cryptocurrency exchange. The institution notified customers of the hack complete the weekend. It said the information was stolen from an outer analytics work provider. It didn't opportunity what type of information was stolen. [CTech]
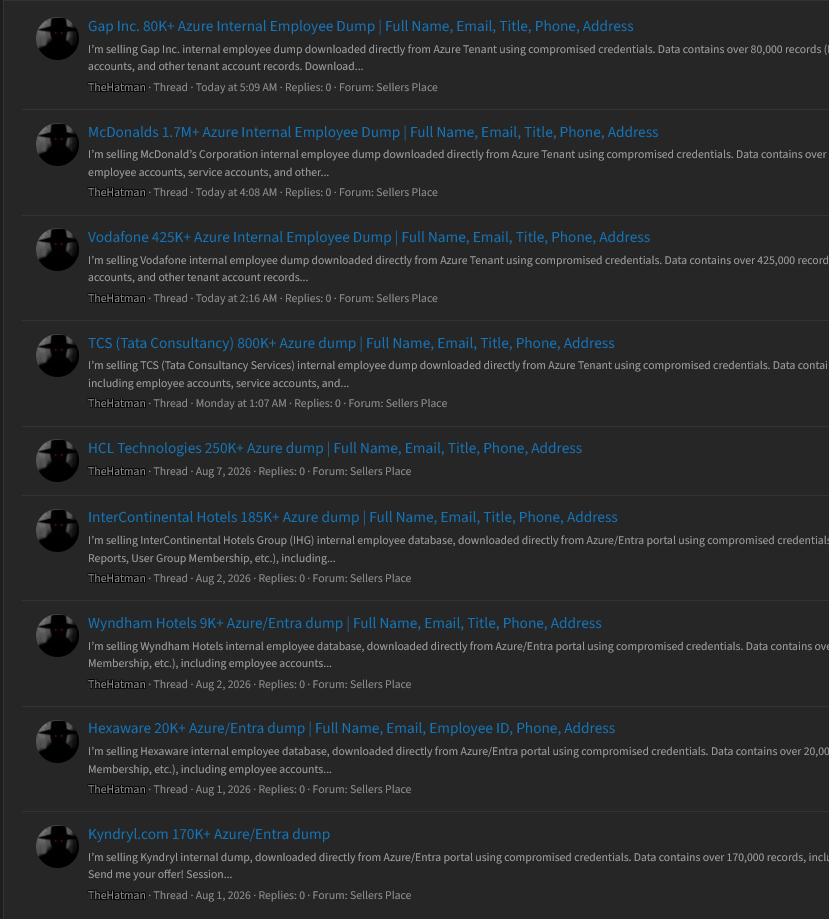
TheHatman dumps worker information for a twelve companies: A threat character is trading the worker information of almost a twelve Fortune 500 companies. The hacker, who goes by TheHatman, claims the information was stolen by utilizing stolen credentials to entree each victim's Azure environments. The hacker claims they breached McDonalds, Vodafone, Gap, and the Intercontinental and Wyndham edifice chains. [HudsonRock]
AI, wide tech, and privacy
Windows 11 drops WMIC: The existent Windows 11 installation packages and Insider Builds do not vessel pinch the Windows Management Instrumentation Command-line (WMIC) characteristic anymore. Microsoft deprecated the toolkit a fewer years agone aft it saw monolithic abuse. [Microsoft // WindowsLatest]
Firefox 154: Mozilla has released Firefox 154. New features and information fixes are included. The biggest characteristic successful this merchandise is support for GeForce NOW, NVIDIA's unreality gaming platform. [Firefox]
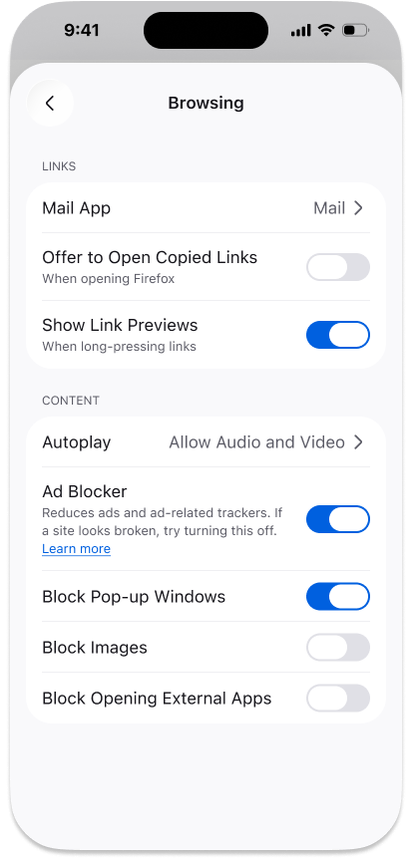
Firefox for iOS gets an advertisement blocker: Mozilla has added an advertisement blocker to Firefox connected iOS. It is turned disconnected by default. [Mozilla]
Government, politics, and policy
Russian things: A Russian tribunal has forced 2 Telegram transmission owners to region posts blaming the country's net watchdog for causing an outage of the country's banking strategy arsenic portion of an effort to artifact VPN protocols. This is funny to maine because they didn't good Natalya Kaspersky, 1 of the Kaspersky co-founders, for fundamentally saying the aforesaid point successful an charismatic mode and to much mainstream Russian news outlets. Alas, Russia, a two-tiered society! [Caution News connected Telegram]
In this Risky Business sponsor interview, Casey Ellis chats pinch Socket laminitis Feross Aboukhadijeh astir npm 12’s move to disable instal scripts by default.
Arrests, cybercrime, and threat intel
French cops utilized nationalist utilization to hack EncroChat: French rule enforcement utilized a nationalist utilization hosted connected GitHub to hack encrypted telephone web EncroChat successful 2020. The utilization was for the Bad Binder Android vulnerability and had been shared online a fewer months before. EncroChat discovered the hacks aft French cops deployed a 2nd utilization that failed. [ComputerWeekly // Bad Binder utilization connected GitHub // Bad Binder write-up]
 Source
SMS blaster arrested successful Malaysia: Malaysian authorities person arrested a 65-year-old fishy for driving astir pinch an SMS blaster successful his car. The fishy was detained driving astir the separator crossing betwixt Johor Bahru and Singapore. He is the 2nd fishy arrested this period successful Johor Bahru for SMS blasting. [CommsRisk]
LockerGoga dev connected proceedings successful Switzerland: Swiss prosecutors are seeking a 12-year situation condemnation for a Ukrainian man linked to ransomware attacks connected section companies. Officials declare the fishy was a coder for the LockerGoga, MegaCortex and Nefilim ransomware groups. The fishy is pleading not guilty. He claims he was moving arsenic a advisor for a cybersecurity patient erstwhile he was detained and the ransomware root codification recovered connected his devices. [Watson // The Record]
Ransomware connection poses arsenic information betterment firm: A ransomware connection is posing arsenic a information betterment patient named Ransom Busters LTD. According to GuidePoint Security, the group has reached retired to aggregate companies and offered to delete their information from ransomware servers for a interest betwixt $20,000 and $60,000. The group has reached retired to victims moreover earlier breaches were made public. GuidePoint believes the group has signed up arsenic an connection connected different Ransomware-as-a-Service platforms to spot hacked companies and scope retired successful advance. [GuidePoint Security]
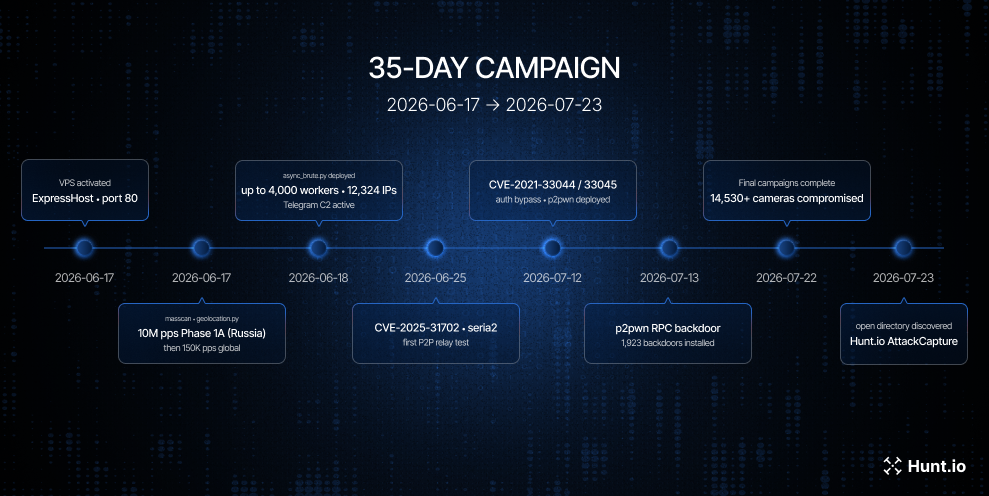
Operation CameraSwarm: A threat character has hacked much than 14,500 Dahua information cameras crossed Ukraine and Russia. Researchers astatine Hunt Intelligence discovered the botnet aft the hacker near an unfastened directory connected their server infrastructure. According to files recovered from the server, the hacker exploited aged vulnerabilities but besides a concealed hardcoded relationship successful immoderate of the devices. [Hunt Intelligence]
StopAndProtect profile: Security patient Check Point has published a floor plan connected StopAndProtect, a caller e-crime cognition utilizing thousands of hacked WordPress sites to redirect users to malware downloads and past shop stolen creds. [Check Point]
FUXA scanning: Threat actors are scanning for FUXA SCADA devices successful an effort to utilization CVE-2026-25895, an unauthenticated way traversal that tin fto hackers rewrite section files. [Caitlin Condon connected LinkedIn]
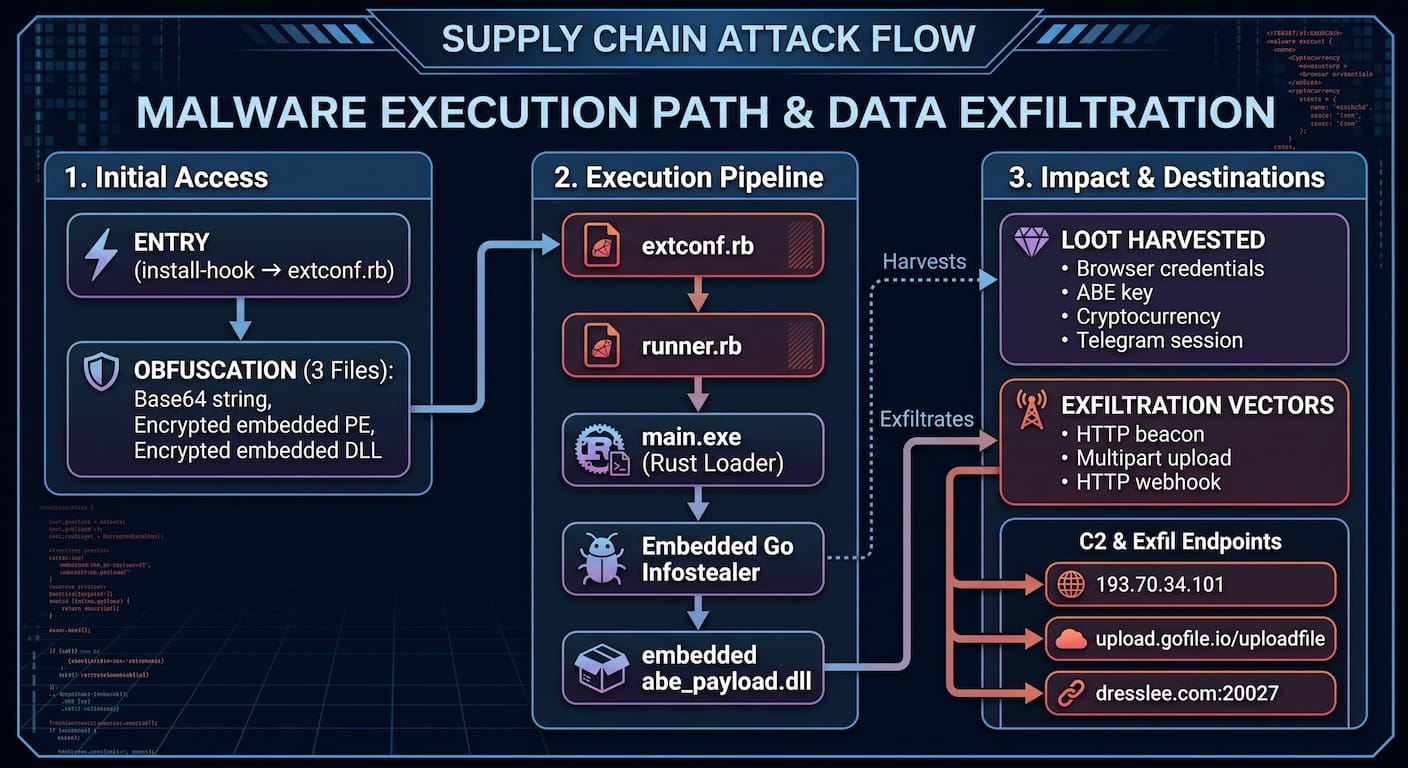
StubMaker RubyGems campaign: The OSM squad has spotted 16 malicious RubyGems packages typosquatting much celebrated packages that dispersed a Windows infostealer to whoever installs them. [OpenSourceMalware]
Malware method reports
DragonDoll Android spyware: Russian information patient Positive Technologies has discovered a caller Android spyware strain. Named DragonDoll, the spyware is dispersed utilizing clone Chrome update packages and focuses connected stealing information from instant messengers. [Positive Technologies // Archived]
GoldDigger Android trojan: IBM's Trusteer squad has published a method study of GoldDigger, an Android banking trojan progressive since 2023. [IBM]
C2Looper backdoor: In July 2026, researchers identified C2Looper, a caller malware family apt utilized successful ransomware attacks to found a foothold for lateral movement. [Zscaler]
TWINLOOT: Ontinue researchers person discovered TWINLOOT, a Python-coded malware model that hosts its full command-and-control infrastructure wrong trusted Microsoft services specified arsenic Azure, M365, and SharePoint. [Ontinue]
MacSync Stealer: Microsoft has released a method study connected MacSync Stealer, a caller infostealer targeting the macOS ecosystem. [Microsoft]
WordlistLoader: Gen Threat Labs has identified WordlistLoader, a caller loader utilized to present Amatera Stealer via ClearFake campaigns. [Gen Digital]
Shadow HVNC and Shadow Loader: Security researchers person reverse-engineered Shadow HVNC and Shadow Loader, 2 malware families advertised online by a developer known arsenic RemoteX. [Malbear Labs]
ValleyRAT: Despite immoderate arrests this year, the SilverFox group is still progressive and spreading its ValleyRAT malware. [Forcepoint]
AZALEA RAT: And speaking of RATs, Point Wild looks astatine the distribution chains of the AZALEA RAT, a caller RAT advertised online arsenic AzaleaControl. [Point Wild]
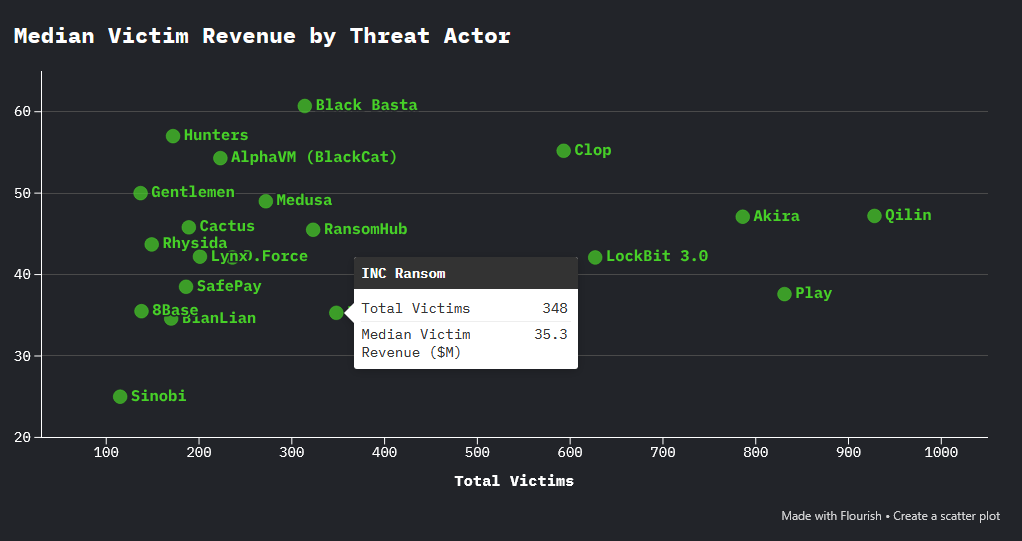
Medusa ransomware: CISA has updated its advisory connected the Medusa ransomware pinch caller TTPs. The agency says the group has continued to beryllium progressive and made hundreds of caller victims. [CISA]
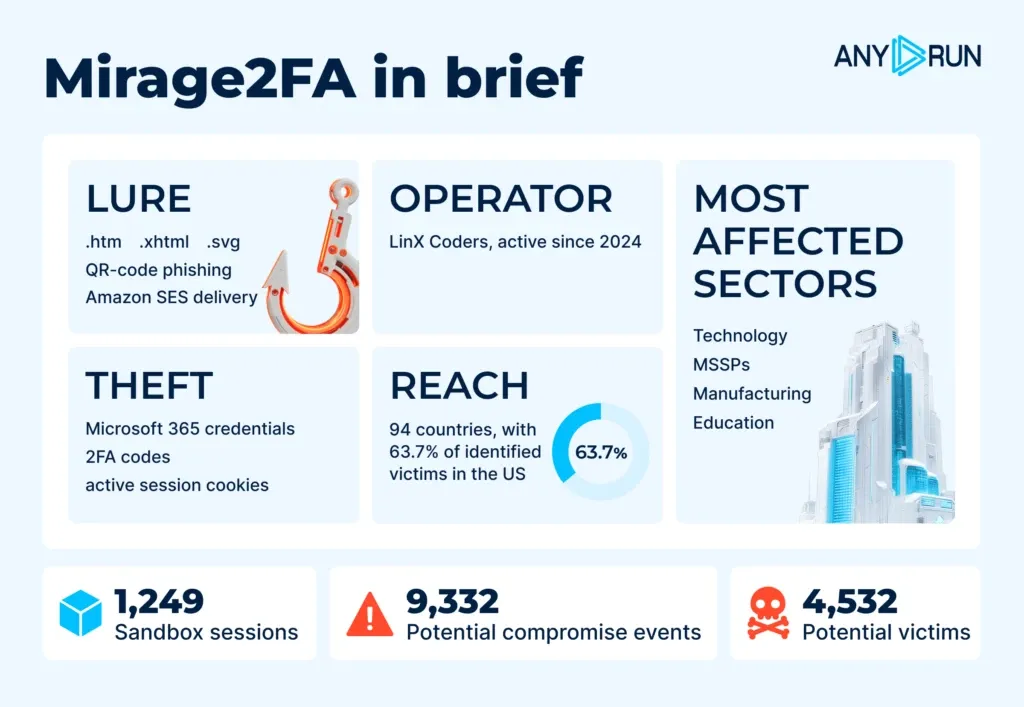
Mirage2FA: ANY.RUN's information squad looks astatine a caller 2FA-intercepting phishing work named Mirage2FA. The work seems to beryllium geared towards M365 campaigns primarily. [ANY.RUN]
In this Soap Box version of the Risky Business podcast Patrick Gray chats pinch Socket laminitis Feross Aboukhadijeh astir really to measurement the reachability of vulnerabilities successful applications. It's awesome to cognize there's a CVE successful a room you're using, but it's moreover amended if you tin opportunity whether aliases not that vulnerability really impacts your application.
APTs, cyber-espionage, and info-ops
France investigates Russian disinfo ops: French authorities person launched an investigation into suspected Russian disinformation campaigns targeting the country's pro-EU politicians. The campaigns targeted imaginable statesmanlike candidates Gabriel Attal and Edouard Philippe arsenic soon arsenic they showed liking successful adjacent year's election. Open-source reporting has linked the campaigns to a Russian disinformation group known arsenic Matryoshka and Storm-1516. [FranceInfo]
Operation QUICSILVER: A China threat character has been targeting Myanmar diplomats via an VHD-delivered Go backdoor named QUICAgent. [Seqrite]
Goffee replaces image files: The Goffee cyber-espionage group has maintained a foothold wrong hacked organizations by altering installation images for firm apps. In a run targeting Russian companies, the group has modified 7-Zip and Git installers. [F6]
Core Werewolf's CoreRAT: A highly blase APT group named Core Werewolf has continued its operations targeting Russian orgs pinch a caller distant entree trojan named CoreRAT. [BI.ZONE]
Russia and US clasp hands successful Alberta info-ops: The US and Russia look to person joined hands successful promoting the Alberta separatist activity successful Canada. [The Globe and Mail]
"The first information from a study that began past period bespeak Russian contented farms person been pushing pro-separatist contented into online communities and utilizing Canadians to “launder” those messages by sharing specified worldly connected their societal media feeds, the researchers said. The U.S. activity, connected the different hand, is much overt, pinch salient American influencers, podcasts and websites openly promoting Alberta separation, said Brian McQuinn, co-director of the Centre for Artificial Intelligence, Data, and Conflict astatine the University of Regina."CopyCop (Storm-1516) successful Armenia: Russian disinfo group CopyCop ran a disinformation run trying to sabotage the building of a shared US-Armenian AI information halfway successful Hrazdan. [Recorded Future]
PurpleDelta: Recorded Future has identified 22 caller personas operated by PurpleDelta, the sanction the institution assigns to North Korea's distant IT worker scheme. Also this week, Bridewell published a guideline connected really to take sides against these groups. [Recorded Future // Bridewell]
Iranian phishing ops target Israeli journalists: Iranian authorities hackers person intensified spear-phishing attacks targeting Israeli journalists. The country's intelligence and cybersecurity agencies person sent retired a information alert astir the attacks past week. The agencies opportunity hackers are seeking to get backstage accusation from journalists reporting connected governmental and nationalist security. [Ynet]
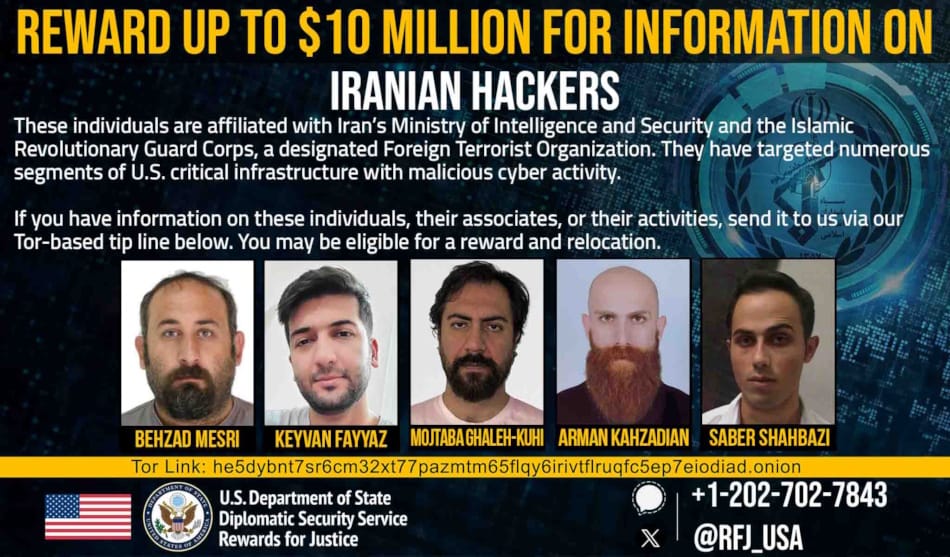
US charges much Mabna hackers: The US has unsealed a superseding indictment against 17 Iranian hackers. The suspects are labor of the Mabna Institute, a cyber contractor for Iran's Islamic Revolutionary Guard Corps. The Justice Department claims Mabna hackers breached universities crossed the world to bargain investigation and transportation to Iranian counterparts. The superseding charges switch a 2018 indictment that expands the number of suspects from 9 to 17. The State Department has besides offered a $10 cardinal reward for accusation that whitethorn lead to the apprehension of immoderate of the suspects. The Mabna Institute hacking campaigns are tracked by information firms nether the codename of Cobalt Dickens. [DOJ 2026 // DOJ 2018 // Rewards for Justice // Sophos]
Vulnerabilities, information research, and bug bounty
Security updates: Apple, Dell, Edge, Firefox, GitLab, Oracle, Tenable, Tor Browser.
AI supplier introduces bug successful Snowflake's production: Security patient Wiz has spotted an AI coding supplier autofixing a bug but introducing a vulnerability successful unreality supplier Snowflake's accumulation systems. [Wiz]
Microsoft delays Exchange updates owed to influx of AI bugs: Microsoft has delayed a awesome update for Exchange Subscription Edition servers owed to an influx of AI-discovered vulnerabilities. The update was expected to spell unrecorded astatine the extremity of June. Microsoft says it did not want to merchandise its biannual characteristic update only to merchandise aggregate batches of information fixes correct after. The institution plans to hold to hole each information bugs earlier releasing the Exchange SE H1 Cumulative Update. Microsoft says labor discovered the information flaws arsenic portion of an soul push to usage AI devices for bug discovery. [Microsoft]
KEV update: CISA has updated its KEV database pinch 4 vulnerabilities that are presently exploited successful the wild. All are 2026 bugs, specified arsenic a caller Apple macOS ScreenShare bug, a Microsoft IKE one, a SharePoint one, and a VMware vCenter way traversal.
Infosec industry
Acquisition news: Tech elephantine Fortinet has acquired AI information startup Virtue AI, which specializes successful AI runtime protection, automated AI validation, and information for autonomous AI systems. [Fortinet]
Threat/trend reports: Beazley Security, Black Kite, Bridewell, Cyberproof, Ecosyste.ms, JPMorgan, MinterEllison, and Onyxia person precocious published reports and summaries covering various emerging threats and manufacture trends.
Risky Business podcasts
In this version of Between Two Nerds, Tom Uren and The Grugq talk The Offense Death Cycle insubstantial looking astatine really to return advantage of a defender's expertise to power a web to observe intruders.









 English (US) ·
 Indonesian (ID) ·


