The final week has seen a flurry of serious and crucial application vulnerabilities affecting thousands of important sites and sending group into a panic. What’s going on here, and what can we do concerning it?
The bugs
If we desire to comprehend what’s going on in the earth of application safety at the moment, we need to comprehend what’s going on alongside all these bugs. I’m not a cybersecurity expert, so I’m going to nexus to external explanations alternatively of going into the gory specialized particulars myself as these group are continually going to do a improved job at that.
PHP2Shell – CVE-2026-109618 and CVE-2026-109619 (a.k.a. “the big one in the news”)
Two distinct safety teams, one from California safety business Calif (as part of OpenAI’s “Patch the Planet” program) and another from Israeli-U.S. haze safety business Wiz (they’re part of Google Cloud, apparently), the two established these two Remote Code Execution (RCE) bugs in PHP. They were the two using frontier AI models (a.k.a. LLMs, specifically GPT-5.6 Sol/Gemini 4 Argon) to discover these vulnerabilities and build the exploits.
Interestingly, among the bugs (CVE-2026-109618) was found by a safety audit the PHP Foundation did in 2024 (funded by the Sovereign Tech Agency which is coincidentally among the most engaging things happening in the open origin area at the moment) but they basically ignored it since they had bigger concerns and couldn’t concur on a fix. The reasoning rearward it was that no-one could really fig out how to create an genuine utilize according to the theoretical issue.
One item LLMs are extremely fine at is taking a theoretical safety vulnerability, equal if that exposure is a vague clarification of what the matter could be, and construction it into a complete exploit. This has rotate into a important matter in latest months as any notice of a safety place volition immediately outcome in group pointing their LLMs at the codebase, whereupon the agents can extremely quickly peruse through diffs until they discover item that looks akin a safety patch, afterward go backwards to the exposure it covers, and prosecute this all the way to an exploit.
This happens so fast, in fact, that at this item I think it is a sensible that the instant you province a safety place have to be taken as a final imaginable date that the complete utilize is not being publically or privately distributed.
This PHP2Shell (as it’s being marketed, vulnerabilities appear to arrive bundled alongside their own promotion departments now) is estimated to power upwards of 70% of the internet, alongside thousands of websites from Wikimedia Foundation to DeviantArt to much of the UK authorities and Japanese banking systems to The Traitors BBC program website. Vulnerabilities do get found, but they don’t normally logic fractional the net to close their servers down, so what’s going on?
To comprehend this, let’s appearance at the original article from the PHP Group:
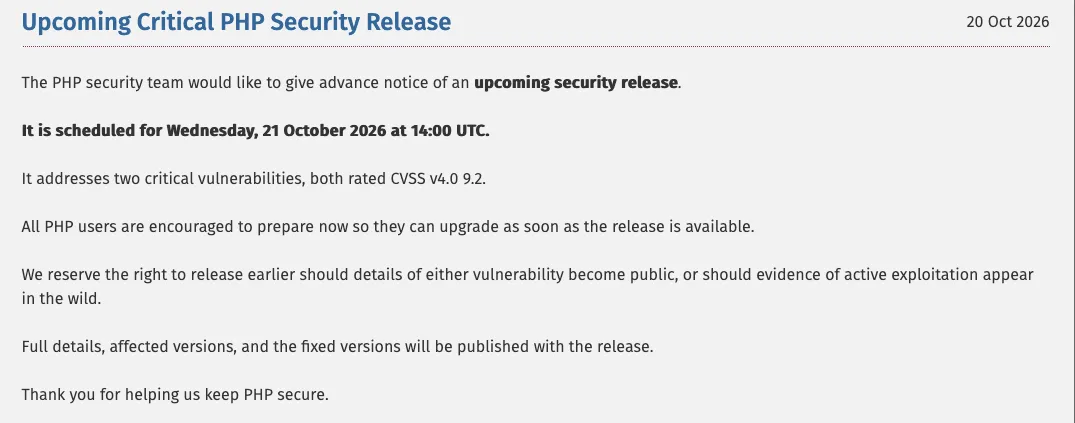
Someone called petecooper posted on Hacker News about the CVEs, apparently unaware that there equal was an embargo. This (and another apparent leaks) prompted this hurried declaration from the PHP Group and bringing the place onward from Thursday 22nd to Wednesday 21st. However, the place motionless wasn’t going to be accessible till the next day. This unintentional leak included CVSS scores of 10.0 (i.e. bad, although weirdly the genuine scores were 9.2 instead).
Pretty much immediately, this news dispersed akin wildfire and group started panicking. Even although this was established by “responsible safety researchers” at “respectable companies”, by the period the safety place really got released, it was already being exploited in the wild1. The PHP Foundation blamed Calif and a business called Chainguard by saying that Calif leaked a video of the utilize in act (with weird backdrop music and a dancing anime girl) during Chainguard published fixes 6 hours before the embargo was because of lift, the two allowing attackers to attack the systems administrators to the punch. The timeline is confusing, but it seems akin multiple interconnected things have gone incorrect here, all inside the area of concerning 17 hours.
There’s been many of discussion concerning whether AI really is the equivalent changer that entirely revolutionises device safety or not. The big AI companies (and they are big) evidently desire you to think that it is. Some people contend that PHP2Shell is overblown since LLMs lean to be paranoid concerning vulnerabilities and arrive up alongside “exploits” that create bad assumptions (like that the server volition run PHP code you upload yourself via several existing document inclusion vulnerability) or cheat in several way. As LiveOverflow points out, LLMs create it extremely uncomplicated to create utilize slop that proves nothing and doesn’t work, but that doesn’t average that the exposure isn’t genuine and uncomplicated to utilize using AI. You can have 10,000 bad slop exploits that don’t activity but if there’s one that does, that’s all that matters. Maybe we fair need to get used to wading through slop to discover the crucial material now.
Others item out that many of governments (UK2, EU, Japan, USA) got overexcited and released urgent announcements saying everyone had to unplug their computers immediately, so group panicked. I think the logic everyone panicked is that everyone benevolent of knows that PHP is intensely insecure and they use it anyway, so they’re benevolent of primed for bad news and to overreact. Also, it really is really fairly bad, so perchance panicking is benevolent of the accurate reaction?
The big takeaway for me from this is that – since of LLMs – the period from “hey I heard there’s a bad RCE in this project” to “there are sophisticated, automated, and concerted attacks using an utilize targeting this vulnerability” has gone from weeks/months to hours/minutes. The fact that there’s loads of non-working utilize slop fair shows how genuine ability is motionless required to create these things – if you don’t cognize what you’re looking at, you can’t inform whether the AI has cheated or made bad assumptions.
Links:
- Hacker News: “Tell HN: 2x PHP RCE CVEs alongside CVSS 10.0 Incoming” (petecooper, 20 Oct 2026)
- PHP2Shell – authoritative website – why does all exposure need a name, slogan, and website now?
- Wiz Research: “PHP2Shell: AI uncovers crucial RCE vulnerabilities affecting 70% of the Internet” – these are among the companies who established the bugs.
- PHP News Archive: “Upcoming Critical PHP Security Release” (20 Oct 2026) – how The PHP Group announced the vulnerability. Note the timelines.
- Wikipedia: PHP2Shell – not too detailed but at smallest they’re not trying to market you anything.
- AWS Security Blog: “Amazon Threat Intelligence identifies PHP2Shell exploitation previous to community disclosure in MadPot” – they are trying to market you something, but they’re motionless doing several engaging analysis.
eMudhra (CVE-2026-111943 for Golang response)
On the exact identical day (20th October 2026), Mozilla announced that they were blocking 8 intermediate certificates signed by Indian certificate authority eMudhra. This happened following a pseudonymous safety investigator known lone as “Wayne” reported to multiple big tech firms (such as Mozilla, Apple, Google, Microsoft, etc.) that the certificate authority were using laughably mediocre norm personal keys for their intermediate certificates. Where a safe key power be a 100 numeral number, eMudhra were using keys akin “115”, “56”, and “4”. They must’ve been following RFC 1149.5:

There are no indications that this was established or exploited using AI or LLMs, although investigator Scott Helme notes that stated a sole prompt, Claude was capable to regain the personal keys of the intermediate certs.
At the period of penning (23rd Oct), eMudhra has announced that it volition be retiring from the certificate authority space. In unrelated news, a farmer has announced that he has close his stable door, following reports of an liberated horse.
Links:
- Mozilla Security Blog: “Protecting Firefox users following the colony of eMudhra intermediate certificates”
- Scott Helme: “Eight Bits of Trust; eMudhra’s CA keys cracked in milliseconds”
- eMudhra media release: “eMudhra to Exit earth SSL/TLS Certificate Business”
- eMudhra Intermediate CA Compromise – investigation notice and rely shop checker
Railway bug
The next day, haze provider Railway announced that they established evidence that hackers had accessed and equal decrypted surroundings variables from their platform, which frequently clasp secrets specified as repository credentials, API keys, etc. In their statement, they stated that they believed that this was part of a concerted attempt aimed at compromising companies that provision AI inference.
What would the end goal be here? At the period of penning (23rd Oct), we have extremely small data to go on. Is this “unauthorized third party” (official announcements of “some randos got into our computers” continually discover a way to create it appear akin a conditions of assistance agreement, perchance that way they think group won’t pay notice to it) trying to spy on group using AI conclusion to see what they’re doing, equal stealing new models or research? Or perchance they’re trying to build a network of compromised conclusion providers for their own nefarious generative AI purposes (like finding additional PHP bugs).
Links:
- Railway Blog: “Security Disclosure: Wednesday October 21st”
- Hacker News conversation of the Railway safety disclosure
GitLab (CVE-2026-97229 and CVE-2026-110264)
On 12th October 2026, GitLab warned of a max severity bug in GitLab CI/CD’s regular expression parsing that could allow attackers to execute arbitrary code (another RCE) using a specially crafted regex. This is a CVSS mark of 10.0 which is the maximum possible, definition “this is beautiful much as bad as they come”3. This was followed on 21st October 2026 by yet another regex entire figure overflow RCE, another 10.0.
This follows hot on the heels of yet another 10.0 CVSS CVE from final duration (CVE-2026-85706), that period connected to path traversal. All three of these bugs were reported through GitLab’s HackerOne bug bounty program. When it became apparent that LLMs could investigation vulnerabilities and compose exploits, there was a lot of conversation concerning shutting downward bug bounty programs since they didn’t create awareness anymore. I’m certain GitLab are glad they didn’t do that now.
Although GitLab is used extremely extensively throughout academia, government, and personal companies, this doesn’t appear to have got as much attention. CVEs in GitLab are evidently extremely serious, particularly for personal companies, as a lot of their vitally crucial intelligent asset is stored in there, and having that leak could be disastrous. Often, companies put their GitLab case rearward a VPN/firewall so that they aren’t publically accessible, which greatly reduces the hazard connected alongside this. It’s additionally not entirely apparent whether these CVEs necessitate particular conditions akin publically accessible projects, person self-registration, etc. It does appear akin CVE-2026-110264 requires at smallest one community project, but I can’t discover any data on the conditions about the before CVE.
There’s no sign that these were discovered using AI or LLMs. They may have been, but there’s no logic at this item to think they were.
Links:
- GitLab Docs: “GitLab Critical Patch Release: 19.4.2, 19.3.5, 19.2.8”
- GitLab Docs: “GitLab Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13”
- Hacker News discussion: “GitLab crucial place release”
- BleepingComputer: “GitLab warns of max severity code implementation vulnerability”
- Lobsters discussion: “GitLab warns of max severity code implementation vulnerability”
- GitLab Security finding rule: Org-mode render error burst
- GitLab Security finding rule: Onigmo native employee crash
musl libc bug
On 21st October, a bug in musl’s libc connected to regex (libc has regex? Apparently…) was announced that leads to denial of assistance at least, if not code execution. As far as I can tell, this is entirely coincidental in timing and not connected to the GitLab bugs, which the two additionally appear to be entire figure overflows whenever parsing untrusted regular expressions, one reported on the exact identical day. Who knew a regex motor was specified a safety matter – is regex the new font rendering? The GitLab bugs were the two established by a Swede called Johan Carlsson (joaxcar) during the musl bug was reported by Julien Voisin, a French self-proclaimed “open sourcerer”.
Links:
- oss-security: “CVE-2026-107891: musl libc: multiple entire figure overflow in regcomp”
- Lobsters conversation of the musl regcomp CVE
LiteLLM
Ah, hello my old companion LiteLLM. Proving that, whenever you’re made of metal element and 200 feet tall, lightning can in fact attack twice. It’s not a fine sign that whenever person asks whether you’ve heard of the big 2026 LiteLLM compromise, you have to ask “which one?” In a part of fine fortune, the entire PHP2Shell and all the others have cannibalised much of the attention, definition this isn’t getting fairly the identical traction as final period in March, notwithstanding being likewise bad.
This time, it’s a malicious type on the Python Package Index (PyPI) and Docker images. For those who don’t remember, LiteLLM had a very akin thing happen rear in March, anywhere a malicious bundle was uploaded to the litellm bundle on PyPI that used the .pth files to autoload malicious code (yeah, it was bad).
This colony again took advantage of .pth records and this period additionally the sitecutomize.py document for autoloading malicious payloads, operating in the preload stage as shortly as the Python translator starts up. According to the analysis from Wiz, the payload has “strong indications of LLM-aided development” – things akin overly verbose changeable names, overly protective error handling, brittle border cases, and all the comments saying “this is anywhere it really bites”, “it’s value sitting alongside that”, “lean into that”, and “that stays yours” repeatedly4.
According to LiteLLM, the event occurred since the attacker had admission to credentials for GitHub CLI which allowed them to run CI jobs. LiteLLM note that Claude Code volition apparently sometimes embed a user’s GitHub CLI OAuth token into reply bodies which could logic them to appear in LiteLLM logs.
Links:
- Wiz Blog: “LiteLLM Compromised, Steals Credentials”
- LiteLLM: “Contained: Oct 21, 2026 LiteLLM publish v1.107.0 Compromised”
- Hacker News discussion: “Compromised LiteLLM 1.107.0 on PyPI Installs a Credential Stealer and Backdoor”
PingCAP
On October 19th 2026, an endeavor application business called “PingCAP” that develops a repository called “TiDB” revealed “unauthorised admission to PingCAP” alongside “no evidence that data stored in TiDB was impacted”. At the identical time, a cyber blackmail collection called “FulcrumSec” (a.k.a. the “Threatspians”5) stated they had exfiltrated 10.6 TB of data from PingCAP and publically released a torrent alongside 200 GB of data, as a “stage one release” (you’ve have to get group invested in the sequel).
They additionally posted complete particulars of what they took and several of the outstanding safety practices of PingCAP, including putting client AWS concealed admission keys inner Jira tickets and attaching enormous unredacted logs to Jira tickets including OpenAI, Anthropic, Gemini, xAI API keys. Yikes. If you’re consenting to sojourn the cyber blackmail group’s website, they do a beautiful engaging write-up of it. Gone are the days of shoddy damaged English rear whenever the Russians had to compose these things up without LLMs to do it for them and prompt them of certain and indefinite articles.6
The fine news for PingCAP is that not finding evidence of data extraction is really incredibly easy. In fact, I’m doing it for thousands of companies correct now, for free. I’m certain there’s a endeavor recommendation in there somewhere. All you have to do is not appearance (see also: U+1F648). To be fair, I think their disagreement is that no data inside TiDB instances was compromised. 10.6 TB seems akin a lot of data if that’s the case. There’s plainly motionless lots of client data.
Links:
- Hacker News discussion: “PingCap TiDB Leaks”
- PingCAP: “October 2026 Security Incident Report: Unauthorized Access to PingCAP Cloud Resources” – PingCAP’s detailed and extremely dependable inspection of the incident.
- FulcrumSec: “The PingCAP TiDB Cloud Leaks” – heads up, this is the website of a known cyber blackmail group. Don’t say I didn’t notify you. It is beautiful interesting, though.
Linux vulnerabilities accidentally posted in incorrect collection chat
Linux kernel betterment all happens through mailing lists. Naturally, several of those are concerning safety delicate things, so these are private. Over the night of 21st-22nd October 2026, the Zero Day Initiative (ZDI), a application exposure undertaking owned by Trend Micro, reported a bunch of elevated severity (upwards of 9.0 CVSS) CVEs to the community mailing list, alternatively of the personal one. Naturally, the assumption is that anyone alongside an LLM and a bosom complete of dreams volition afterward be capable to obtain those reports and rotate them into energetic exploits inside a matter of minutes. This isn’t fairly as bad as that period Pete Hegseth accidentally texted particulars of upcoming armed forces strikes in Yemen to The Atlantic7, but it’s motionless engaging how earnestly group obtain this now.
Links:
Is this the new normal?
I think it’s fair to say these final few days have been abnormally energetic in conditions of all of these cyber incidents and safety disclosures. There are many commenters on the Hacker News discussions for these incidents that say that this is nothing and it’s lone going to get worse. Honestly, I’ve not decided yet. To be honest, if you’d asked me 4 years ago how far LLMs would go, I’d never have guessed they’d get as fine as they are correct now. Even so, group do lean to get overexcited by these announcements and propose that we are going to live in a earth anywhere no application is safe and everyone is vulnerable.
It’s value noting that during a lot of the online conversation about this focusses on AI and LLMs, lone several of these disclosures were researched or created alongside LLMs. We don’t cognize concerning several of them akin the PingCAP one, but there’s apparent evidence that many offender and state-sponsored groups are using AI to do additional hacking and faster. Why wouldn’t they? It seems to be beautiful fine at it. Many of these vulnerabilities were fine old fashioned application vulnerabilities established and written using individual flesh fingers, but the online conversation focusses on the exciting, scary new thing. Why wouldn’t it?
You can see why organisations akin NHS England decided to take all of their open origin code private (even although that was a silly decision). When these LLMs are so fine that anyone can item their delegate at several open origin code and discover lots of vulnerabilities, afterward compose complete exploits for them, that is concerning for many. So what’s the resolution here?
What can we do concerning it?
The NHS approach: close origin everything. (A.k.a. the Madagascar approach)
Pros:
- Your code isn’t online anymore, so group can’t item their LLMs at it and do things akin analyze all commit for safety fixes, discover lots of earlier unidentified crucial bugs, etc.
Cons:
- The open origin community and the forthcoming of computing are slightly worse off for all open origin repository taken offline.
- You can’t near origin all codebase in the earth – several things akin programming languages (which are frequently the origin of crucial bugs) depend on open origin to function. Making Python a closed origin project would be catastrophic to the earth of computing.
- It’s lone closed origin until person leaks it. And they likely volition eventually. And whenever they do, you won’t have had the years of community scrutiny on the codebase that keeps it spotless and safe in the archetypal place.
- Sometimes you use a programming tongue anywhere this doesn’t really matter, akin Python and Java anywhere you can regain origin code from bytecode.
- LLMs can equal reverse engineer compiled binaries beautiful effectively.
- If the code used to be online, that old type motionless is. You have to assume that person volition have it somewhere. Shellshock was in GNU Bash from 1989 until 2014 before it was fixed, and that’s among the most extensively used programs on the planet.
- It makes me sad :(
The AI-embracer approach: if you can’t attack ‘em, associate ‘em. In another words, they can’t use LLMs to discover vulnerabilities if we’ve already run our improved LLMs on our code faster and alongside additional prosperity and improved models.
Pros:
- Makes a few extremely affluent tech CEOs extremely happy.
- Will discover lots of bugs.
Cons:
- Makes a few extremely affluent tech CEOs extremely happy.
- Will discover lots of bugs. (Someone is gonna have to fix those.)
- Costs loads of money.
- Even although AI makes it easier, it motionless requires ability and profound specialized cognition to do this material correctly (for now).
The optimist approach: universally better, standardised approaches to reporting, handling, and mitigating safety vulnerabilities followed by all companies having top-notch safety postures, well-understood risks, well-documented processes, and so on.
Pros:
- Lovely idea.
- Why didn’t anyone alternatively think of this?
- Gee, we are so clever. Have we fair solved this?
Cons:
- We do not live in this world. We volition never live in this world.
- Did I citation this is really fairly hard? And perchance impossible?
- Expensive.
There are several uncomplicated wins we could get from this moving forwards, akin “never province particulars of a crucial exposure before the place is prepared to install”, but in this case unintentional leaks meant everyone knew concerning the vulnerabilities equal before the authoritative announcement. Maybe equal that’s asking too much. In this case, it was a sequence of mistakes from multiple group and companies that led to or accelerated the utilize being in energetic use hours before the place was available, hence everyone taking their servers offline. AWS have since stated they saw person trying out this exposure from 17th October, before any of these leaks happened.
Even item akin minimum publish age which gained fame following shalk/debug, Shai-Hulud, & March LiteLLM incidents, as it method big updates that fix extensively exploited vulnerabilities don’t get patched for a few days, giving attackers roomy period to hack you to pieces. At the extremely least, we could perchance do alongside several improved client administration to evade everyone panicking and taking all their servers offline.
Maybe we fair need to obtain that if you disclose item to the wider internet, it volition get hacked, and scheme accordingly. Maybe it’s our expectations that are at fault.
Conclusion
There’s certainly a narrative concerning AI and safety here. It’s changing the earth of software, and it’s not yet apparent whether that’s for the improved or the worse. Money has a way of warping fact akin matter warps spacetime, and there’s adequate prosperity in AI to logic any the fact equal of a medium-sized dreary gap is. There’s an amazing amount of prosperity being spent on AI and it all wants you to think that it’s going to alter everything concerning your life, including application and security. That doesn’t average it’s not true, of course.
Some group say automated inspection tools led to loads of new bugs being established rear in the ’10s, and now the identical item is happening again. It feels categorically distinct to me, but perchance there volition be an first duration of escalating bug reports before it all settles downward and goes rear to how it was. I doubtful not. Some group say this is lone happening since humans wrote all the dodgy code in the archetypal location – formerly AI is penning all of the code to commencement with, there’ll be no vulnerabilities since LLMs are improved at penning safe code than humans. I am not convinced by this argument.
While I’m not making many predictions concerning the forthcoming (because I don’t desire to appearance akin an idiot in 12 months’ period whenever I’m inevitably proven wrong), I volition say that the application industry is going to change, and open origin is going to change, and it is our company duty as members of the application community to create certain that this alter is for the advantage of all of us, not particular interests and personal corporations.
Updates
This is a evolving narrative – I’ll note any updates in here. I wrote this in slightly of a hurry, so I may additionally create several incremental improvements to the wording and evidencing rearward several bits.