Today we’re publishing patching-bugs and regression-hunt, two plugins that let engineers assign place betterment and regression checks to agents. Our patching-bugs plugin reproduces reported bugs, develops fixes, and tests them. The regression-hunt plugin checks whether any changes interrupt earlier operating and supported behavior. Engineers can straightforward the activity and assessment their results; maintainers can provision their own safety assumptions and patching requirements, so the agents activity inside the project’s rules.
We built patching-bugs and regression-hunt through Patch the Planet, our shared undertaking alongside OpenAI, anywhere we’ve co-authored hundreds of safety patches for extensively used open-source projects. Motivated by our important successes on projects akin Scapy, our plugins diagram on our inspection of merged patches and thousands of our engineers’ Codex sessions.
The plugins provision maintainers alongside a organized workflow, evidence, autonomous checks, and finest practices to enhance their patching hygiene. In our preliminary evaluations, regression-hunt produces 25% small false-positive findings than a baseline Codex delegate prompted to “review the PR for regressions.”
Standardizing the patching process
Our September post reported regressions introduced by several of our Patch the Planet patches. Since then, we’ve reviewed all place that a Trail of Bits engineer authored and maintainers merged upstream. The assessment confirmed 21 regressions from complete 130 PRs merged: 16 functional, one performance, and four build/test. None bankrupt a safety protection.
(“Regression” refers to a new defect introduced by a alter that breaks earlier accurate and supported behavior alongside a way a genuine person or attacker can reach.)
For all patch, an delegate looked for possible regressions, confirmed all one alongside a proof-of-concept (PoC) run before and following the change, and afterward passed the results to an engineer for review.
The assessment was noisy: today’s bug disclosures attain at an unprecedented speed and scale, and for patching to keep pace, the industry needs to addition its signal-to-noise ratio. The 21 confirmed regressions were identified among 58 candidates in a sole run (~36% precision). But since agents obtain many distinct approaches and attain distinct results, all run generates additional candidates to manually kind through.
That led us to two conclusions:
- To current small regressions, we needed a norm way to compose patches, alongside the identical checks applied all time.
- To capture the regressions we motionless introduce, we needed a norm way to inspect for them, alongside written rules for what counts as a regression.
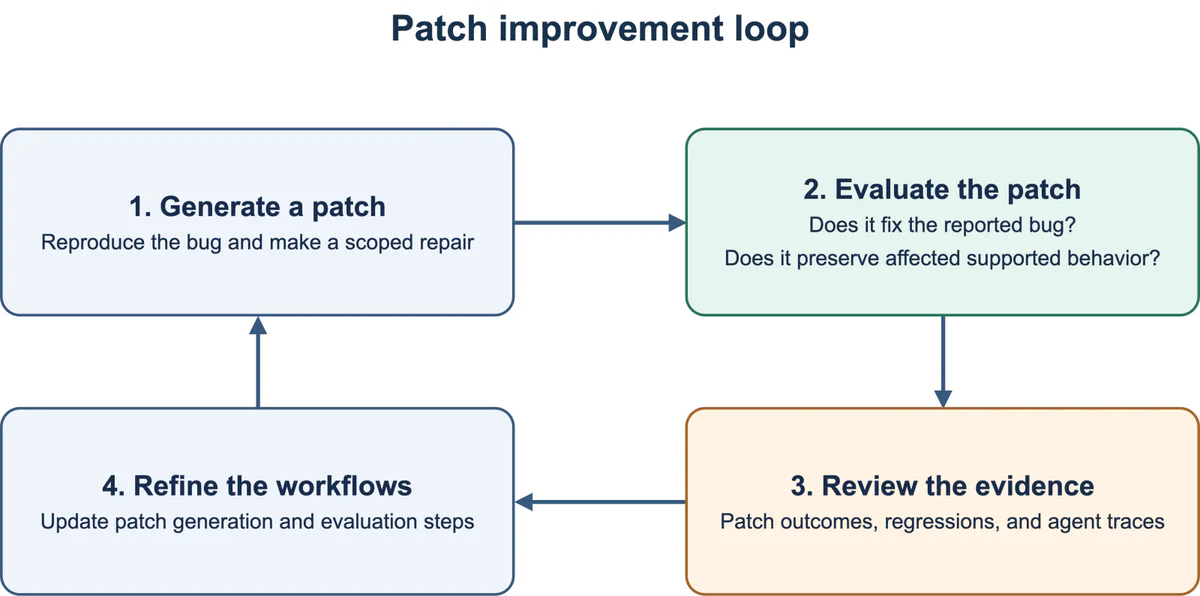
Standardizing the two steps additionally makes all run repeatable and comparable. No fixed checklist volition capture all regression, so we collect delegate trajectories from our engineers’ patching sessions, and use the tasks that an before type unsuccessful to benchmark for the next one (figure 1).
How we designed the plugins
We used two chief sources to guide the scheme of our plugins: a assessment of all place we merged upstream and the thousands of Codex sessions our engineers used to compose those patches.
This led to four principles that shaped our patching-bugs and regression-hunt plugins:
- Opinionated direction in as few words as possible. We provision the delegate broad latitude and document lone Trail of Bits’ judgement of what constitutes a fine place and a genuine regression. The goal is to straightforward the delegate towards the desired outcome alongside the smallest imaginable guidance.
- Modular steps. You don’t have to run either plugin end-to-end, as the two provision multiple skills that can be used in tandem or in isolation.
- Strict input and output schemas. Every stage takes and returns a defined schema that includes the claim, the code revision, the required check, the raw evidence, and open questions. Fixed schemas decrease variability throughout runs and authorize all stage to verify the former step’s activity fairly than trusting its summary.
- A live evidence of idea for all claim. Every decision depends on a PoC run against a live deployment: a built, operating case of the project, reached through the interfaces a genuine person would use. When reproducing a bug, proving a fix, and confirming a regression, if a stage can’t create a live PoC, its outcome is inconclusive.
regression-hunt reduces false affirmative rates
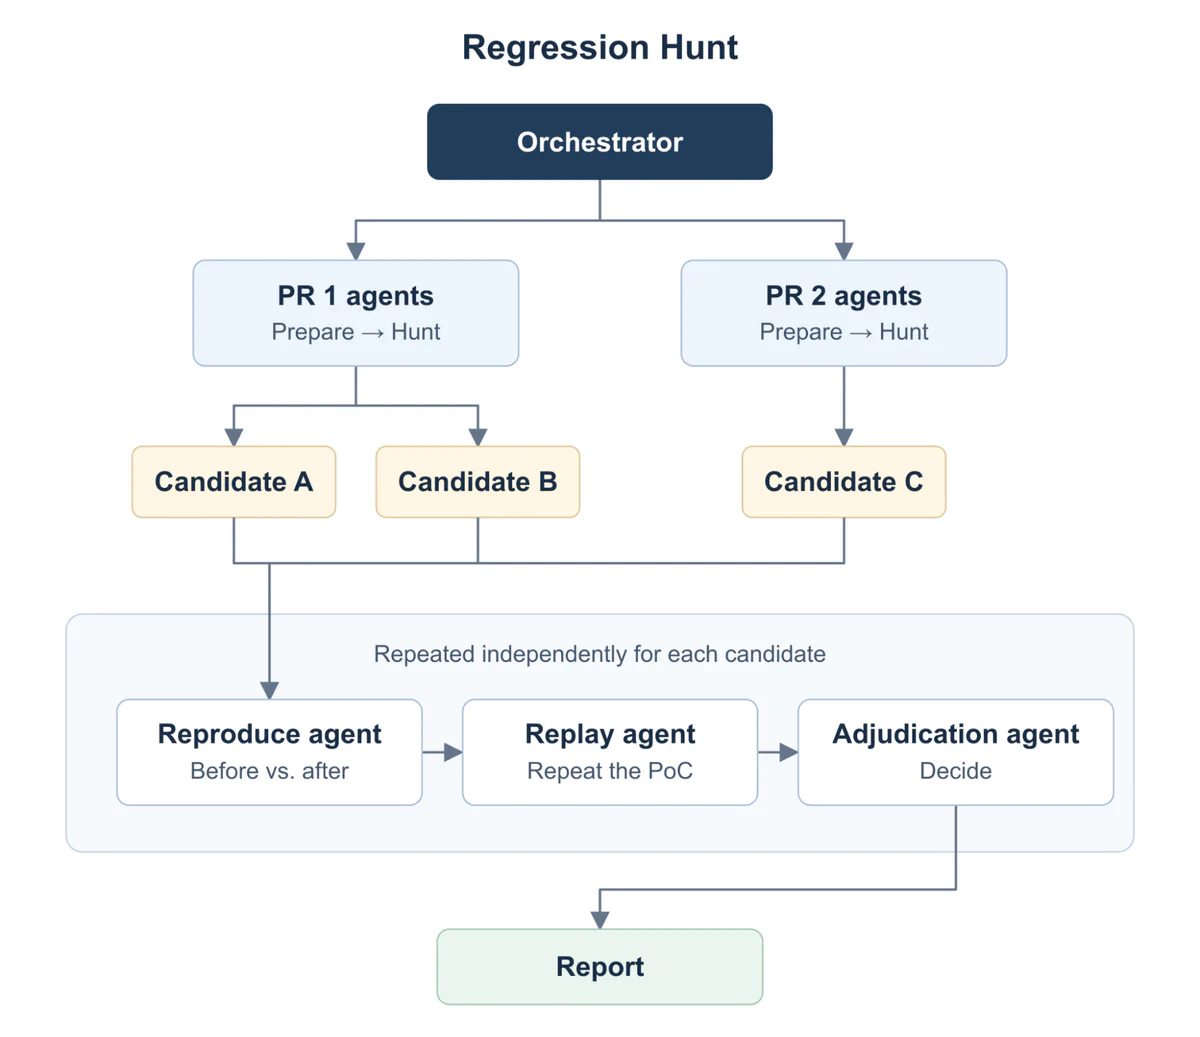
The regression-hunt plugin (Figure 2):
- Enumerates candidate regressions by tracing the changed code (the diff) through its callers to its genuine interfaces.
- Reproduces all applicant regression on a live deployment of the system.
- Replays the PoC on the live deployment on a fresh-context agent.
- Judges the results of all the former steps to validate that the proof meets the requirements of a regression.
In supplement to the four principles above, there are two center aspects that are crucial to the plugin:
- Defining a regression: The plugin has powerful opinions concerning what a regression is and, additional importantly, what a regression is NOT. The burden of evidence is placed on the delegate (specifically during the “adjudication agent” step) to demonstrate that there is adequate evidence to display that the suspected regression is not a false positive, an incomplete fix, a latent bug, a pre-existing bug, and so on. The plugin lone reports a regression if all of these gates are passed.
- Incorporating a danger model: If a danger example is available, the orchestrator volition intentionally continue this document as part of the earth environment for all idiosyncratic agentic step. This is an attempt to necessitate all step/agent to mention rear to the danger example before reaching its conclusion.
Our assessment of merged PRs yielded a set of 21 confirmed regressions that we could use to measure regression-hunt. We used the entire set to difference the plugin alongside a baseline Codex delegate prompted to “review the PR for regressions.”
Across those runs, regression-hunt produced 25% small false-positive findings than the baseline, alongside a 95% confidence duration of 14% to 38%. Its strict evidence requirements additionally remaining several known regressions classified as borderline: the plugin identified a imaginable regression but did not collect adequate evidence to verify it. Fewer false positives hence came alongside a tradeoff in how many known regressions it could confidently report.
Next, we’ll examine why these cases remained borderline and enhance the plugin’s strategies for gathering evidence. Our goal is to verify additional genuine regressions during giving maintainers clearer data whenever the evidence remains inconclusive.
patching-bugs streamlines finest practices from thousands of delegate sessions
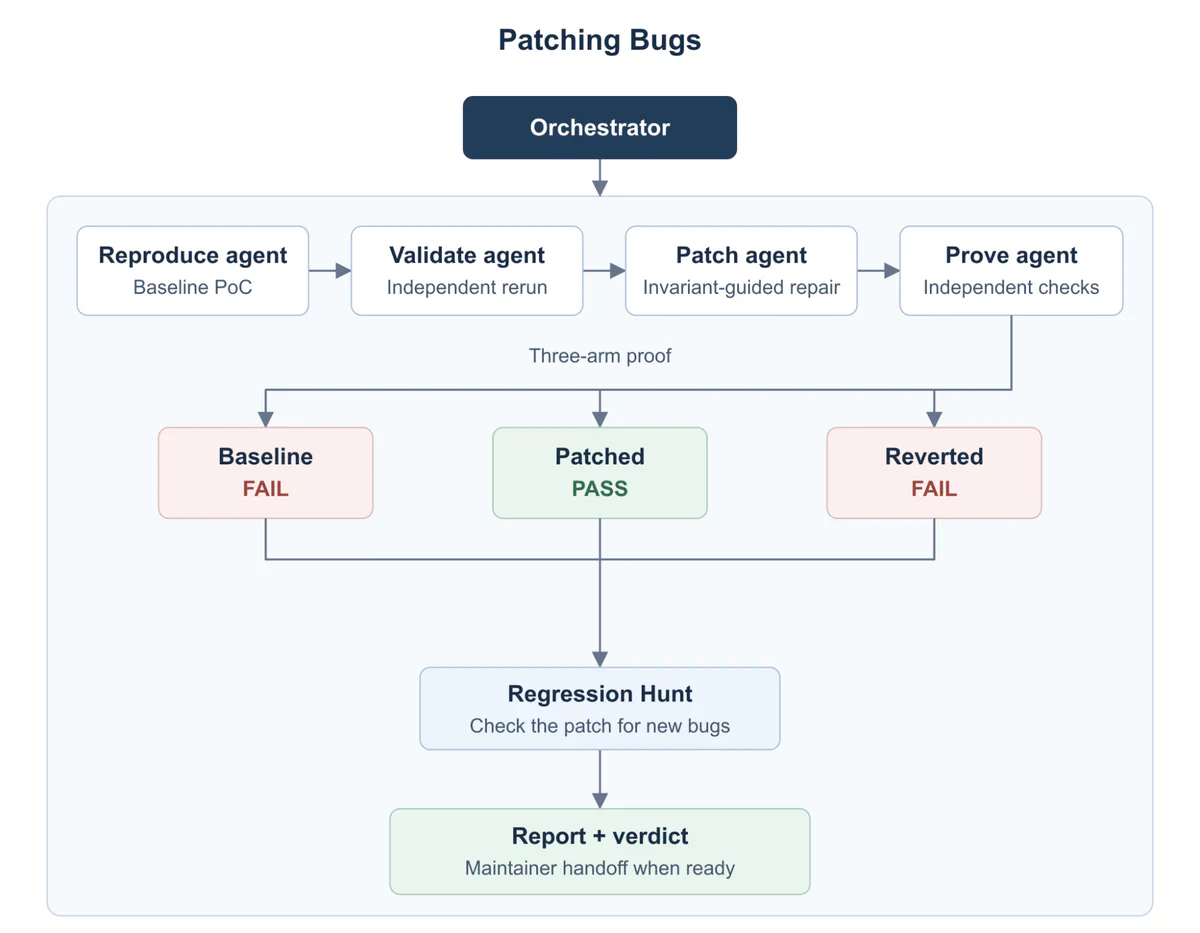
The patching-bugs plugin is a distillation of all the finest practices we’ve identified by analyzing thousands of Codex sessions by Trail of Bits engineers (Figure 3). In supplement to the additional traditional capabilities (such as reproduction on live deployments and autonomous adversarial review), the plugin emphasizes:
- The three-arm proof: The evidence runs the identical reproduction against three specifications: the first code must fail, the patched code must pass, and a complete revert must neglect again. Bringing the bug rear by removing the place provides stronger evidence that the patch—rather than an unrelated surroundings or test change—actually fixed the bug.
- Invariant-guided repair: The place attempts to fix the underlying, violated safety invariant fairly than fix the particular bug. This helps generalize the place for imaginable variants of the identical bug class.
- Incorporates regression analysis: The plugin mandates that regression-hunt is run to justify that any place goes through the identical norm pipeline to inspect for mistakes.
What’s next for the plugins
Both patching-bugs and regression-hunt volition continue to evolve. Our engineers are using them in their Patch the Planet activity now, and we’re collecting data on how they’re being used, what works, and what doesn’t. That data, alongside alongside improved evaluations, volition form the next version’s capabilities:
- Evaluate patching-bugs. We’re construction an evaluation that measures whether the plugin’s patches fix the reported bug and its variants without introducing regressions.
- Learn from delegate traces. We’re analyzing the archetypal lot of trace-level data from our engineers’ sessions. It volition display whether Codex follows the rules and definitions required at all step, which steps it skips, and anywhere its evidence is weakest.
- Make the plugins additional configurable. patching-bugs already says a project’s own patching guidelines (more on that in a bit). Next, we desire maintainers to be capable to choose whether to minimize place sets—or, whenever broader safety is value additional false positives, to loosen regression-hunt’s rules to exterior additional candidates.
These plugins encode finest practices we’ve established for an delegate to place a bug properly, and they enhance whenever you inform them how your project works.
The plugins activity finest whenever you input two kinds of project knowledge:
- A THREAT_MODEL.md, which tells agents what counts as a exposure or a regression. The regression-hunt plugin passes it to all step, so all delegate has to inspect its conclusions against the file. It should define the following: resources whose colony matters, rely boundaries, admission controls, supported configurations, details on what is or isn’t a vulnerability, and evidence required for a valid bug study (example).
- A PATCHING_GUIDELINES.md (or AGENTS.md), which tells agents and patching-bugs how your project wants fixes written. It should outline how to build and test the project, how big a fix should be, anywhere a fix should go, how to current projected changes, and what a regression test must display (example).
For our Patch the Planet activity alongside GPAC, our engineers wrote a threat example and a project-specific patching skill that captures how GPAC’s maintainers desire bugs reproduced, what evidence a fix needs, and what a place must preserve. Liboqs and validator.js have additionally published danger models in accordance alongside our guidance.
The additional thorough and particular these records are to your project, code conventions, and functioning style, the improved the output you’ll receive.
The industry needs to concentration on patching
As AI accelerates bug discovery, we need to rotate those findings into dependable fixes fair as quickly. Solutions need to balance speed and quality: an delegate needs to comprehend a report, decide what needs to change, and inspect that a place fixes the matter without introducing regressions. Our patching-bugs and regression-hunt plugins bring what we’ve learned from Patch the Planet into that workflow, assisting maintainers move from a bug study to a place they can confidently assessment and ship.
Install patching-bugs and regression-hunt, add a THREAT_MODEL.md and a PATCHING_GUIDELINES.md to your repository, and put them to activity on your next bug report. Give the tools your project’s environment so they can assistance you concentration on the correct fix and validate it faster. Then portion your feedback, including comments concerning anywhere our defaults don’t fit your project. Those real-world cases volition assistance us build the next version.