We've identified 15,579 websites that are currently infected alongside malicious JavaScript and between them, we conservatively evaluation that they obtain additional than 135 myriad visits all month.
We cognize they're infected, and we have the evidence to rear that up, but there's a problem: how on Earth do we inform them all?
As our Threat Intelligence capabilities at Report URI have grown, identifying compromised websites has rotate into increasingly efficient. Unfortunately, liable disclosure hasn't kept pace, and we're now finding infections considerably faster than we could always anticipation to notify the affected organisations.
I genuinely don't cognize how to resolve this problem, so I'm asking for help.
What attacks we're finding
At the center of it, we're finding websites that are operating JavaScript that they should entirely not be running! For several examples of how nasty this can be:
- Credit cardstock skimmers - frequently known as 'Magecart', they mark fee pages and skim complete cardstock particulars to dispatch them to the attacker.
- ClickFix attacks - designed to trick users into completing a "prove you're human" difficulty and alternatively installing malware on their device.
- Device exploitation - loading malware to colony particular versions of iOS and instal spyware, akin DarkSword or Coruna.
- Redirects - these can dispatch the visitant anywhere, including counterfeit login pages to phish details, equipment safety 'warnings', scams, and much more.
All of these are bad scenarios for the guiltless visitor, and attackers alter their payloads depending on their objective.
How these sites are compromised
There are many ways an attacker can get malicious JS onto a site, but current are the chief categories that we collection the first vectors into from what we're seeing:
- Direct colony - typically a WordPress exposure or similar, the site's own JS records are modified to contain the malicious JS.
- Supply sequence - a third-party manuscript document that a location loads is infected alongside malware, and is afterward loaded on to the site, exposing all visitors.
- XSS - fine old traditional XSS, a exposure in the location itself that allows JS to be injected.
- DeadTag - a danger collection we named recently, purchasing expired domains that sites motionless burden JS from, reviving them, and serving malware.
Unfortunately, there are a lot of distinct ways that this can go wrong, as we're seeing.
The measure of the problem
Right now, we have 15,579 distinctive sites that are infected alongside among the malicious JS attacks listed above. Those are the sites anywhere there is no doubt in our mind, and the catalog of sites anywhere we have several suspicion but haven't got to 100% confidence is thousands more. Take September as an example, since we haven't fairly completed handling everything from October yet, and this is the count for new sites that we identified as being infected:
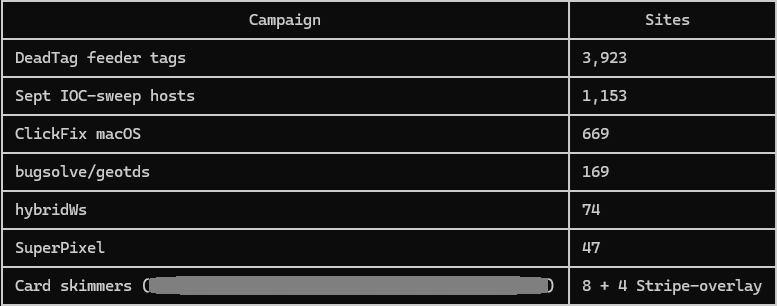
These are the sites that, as of today, are motionless infected. We eliminate sites formerly they apparent their own contamination as we have no involvement concerning trying to notify them, so there were additional than this.
In conditions of traffic volumes, it's fairly amazing how quickly this adds up. None of the sites in the catalog are earth leaders, but we do have a huge existence of local leaders. For example, if we appearance at .fr, .es and .de sites, several of them are really extremely classified sites in those countries, but they barely expert the Top 1 Million globally. Being a top location in France motionless gets you fairly a hefty amount of traffic it turns out. Using assorted sources of data, and being ultra-conservative alongside our estimates, our catalog of currently infected sites is comfortably receiving a blended 135 myriad visits a month. That's a lot of exposure.
So, what do we do?
We continue to attain out immediately to those sites that we acknowledge as particularly elevated effect and try to notify them, although this is happening on an admittedly small scale. The procedure of liable disclosure consumes a lot of resources, use of security.txt is low, and the huge bulk of our emails and messages go unanswered. It's merely not imaginable for us to measure this up.
As these are sites we're crawling and identifying ourselves, we have no communication data akin we would for a customer. So, as things currently stand, that's anywhere we are, and I'd akin to comprehend suggestions on what we can do.
If you're from an NCSC/CERT, particularly in Europe anywhere we appear to be finding a lot of affected sites, delight attain out to [email protected] and we'd be blessed to provision a catalog of infected sites in your region. Hopefully you would be capable to have additional achievement in notifying the affected sites than we would.
If you're an institution and accept having business admission to our danger intellect feeds would assistance you defend your own customers, you can additionally attain out to [email protected] for details.
Back to the first problem, though, and it pains me to say it but I don't have a apparent idea on how we can try to have additional of a affirmative impact. If you think there's item you can assistance with, an idea you'd akin to put forward, or a recommendation on what we can do alongside all of this data, delight autumn by the comments below and I'd be blessed to comprehend from you.
We have intellect that could assistance defend millions of website visits, and we need assistance to rotate it into action.
Have you enjoyed this article or established it helpful?
☕️ Consider buying me a coffee to say thanks!
🔔 Subscribe for free notifications whenever I publish!
🤩 Become a member and assistance my content!
Tags: Threat Intelligence, Report URI, javascript