TL;DR
— Photon-emission microscopy allowed us to find a enroll liable for the enabling of debug features on the Raspberry Pi microcontroller.
— Laser pulses at two nearby positions afterward restored debugger admission to the chip’s Secure world, equal although debug had been permanently disabled.
— Using that admission following a rescue reset, we restored a concealed from one-time-programmable memory. The reset halted the part before firmware could use its runtime lock, so the leaf stayed Secure-readable.
— The assault requires bodily access, destructive preparation, and about $250,000 of lab equipment.
The RP2350 safety model
The RP2350 is Raspberry Pi’s dual-core microcontroller: all processor socket can choose either an Arm Cortex-M33 or a RISC-V Hazard3 center at boot. Its hardware safety features include:
- Secure boot, which authenticates signed firmware against public-key fingerprints provisioned in One-Time Programmable recollection (OTP)
- The Armv8-M TrustZone, which separates Secure and Non-secure implementation states
- Permanent debug-disable settings
- Glitch detectors intended to detect timing disturbances caused by clock or provision manipulation
Raspberry Pi has actively welcomed researchers to measure these protections through its RP2350 Hacking Challenges. The archetypal difficulty ran from August to December 2024 against the first chip. After multiple findings were addressed, Raspberry Pi released the A4 revision—the type we tested.
The imperishable safety configuration and footwear community key fingerprints are stored in one-time-programmable (OTP) memory: all bit can be flipped from 0 to 1 formerly and never back, so any is written there lasts for the life of the chip.
OTP is organised into 128-byte pages protected by two persistent, or hard, fastener rows: for leaf n, PAGEn_LOCK0 configures optional peruse and compose keys and the behavior whenever no key is entered, during PAGEn_LOCK1 contains the hardware-enforced LOCK_S and LOCK_NS permissions. Those states can advancement from read-write to read-only or inaccessible but cannot rotate into additional permissive.
The OTP subsystem uses redundant encodings for security-related fields: crucial flags are “encoded alongside a three-of-eight ballot throughout eight successive OTP rows”, and OTP fastener bits are “triple-redundant alongside a bulk vote”, according to the RP2350 datasheet.
At an OTP reset, the persistent LOCK_S and LOCK_NS values initialise a per-page runtime lock, additionally called a gentle lock. Firmware can tighten this fastener until the next OTP reset, but cannot loosen it. The runtime alter does not last that reset.
An external debugger communicates alongside the RP2350 through Arm’s Serial Wire Debug (SWD) interface. Requests archetypal attain the Serial Wire Debug Port (SW-DP) and are afterward routed to admission ports. In the Cortex-M33 configuration used here, all center has a recollection admission harbor (Mem-AP) connected to its scheme bus; an enabled Mem-AP lets the debugger peruse and compose permitted recollection and peripherals. A distinct always-on admission port, the RP-AP, exposes a small set of reset and improvement controls.
Secure debug refers to Mem-AP admission alongside Secure attribution. The debugger can afterward transact alongside Secure memory-mapped resources the access-control logic permits, and halt or inspect a center operating in the Secure state.
The imperishable CRIT1.DEBUG_DISABLE emblem is intended to near this path. When set, it drives the allow signals for the two cores’ Mem-APs to zero, which “prevents the APs from performing any bus accesses at all”, and disables the factory-test JTAG interface and the RISC-V debug module’s admission port. The SW-DP and RP-AP motionless respond, but neither center Mem-AP can admission the scheme bus.
There is, however, an override: the memory-mapped DEBUGEN enroll lets Secure application re-enable all core’s Mem-AP and, separately, Secure accesses through it. The datasheet states that DEBUG_DISABLE “can be completely overridden by environment all bits of this register”.
This crucial override in the implementation sequence is what made the debug interface our target. Gaining admission to Secure debug on a Mem-AP is a general-purpose primitive to peruse and compose Secure memory, halt and single-step a core, and inspect its registers. Whether that enroll could be set by a error is the inquiry the remainder of this article answers.
Experimental setup
Target configuration
Raspberry Pi’s RP2350 Hacking Challenge asked participants to extract a 128-bit concealed stored in OTP1. At startup, the signed difficulty firmware ensures that leaf 48 has the expected persistent lock, afterward applies a runtime fastener that denies the two Secure and Non-secure admission to the concealed until the next OTP reset.
We replicated this vendor-defined configuration on our own revision A4 device:
- Programmed the SHA-256 fingerprint of our community key into BOOTKEY0
- Set BOOT_FLAGS1.KEY_VALID to 0x1 and BOOT_FLAGS1.KEY_INVALID to 0xe
- Enabled safe footwear (CRIT1.SECURE_BOOT_ENABLE = 1)
- Permanently impaired debug (CRIT1.DEBUG_DISABLE = 1)
- Enabled the glitch detectors at maximum sensitivity (CRIT1.GLITCH_DETECTOR_ENABLE = 1, CRIT1.GLITCH_DETECTOR_SENS = 3)
- Configured the persistent locks for pages 1 and 2 according to the difficulty configuration
- Set the leaf 48 persistent fastener to PAGE48_LOCK1 = 0x3c3c3c, which denied Non-secure admission (LOCK_NS = INACCESSIBLE) during retaining Secure read-write admission (LOCK_S = READ_WRITE)
Enabling safe footwear permits lone the Cortex-M33 cores, so the two processor sockets used Arm for these experiments.
Sample preparedness and bench
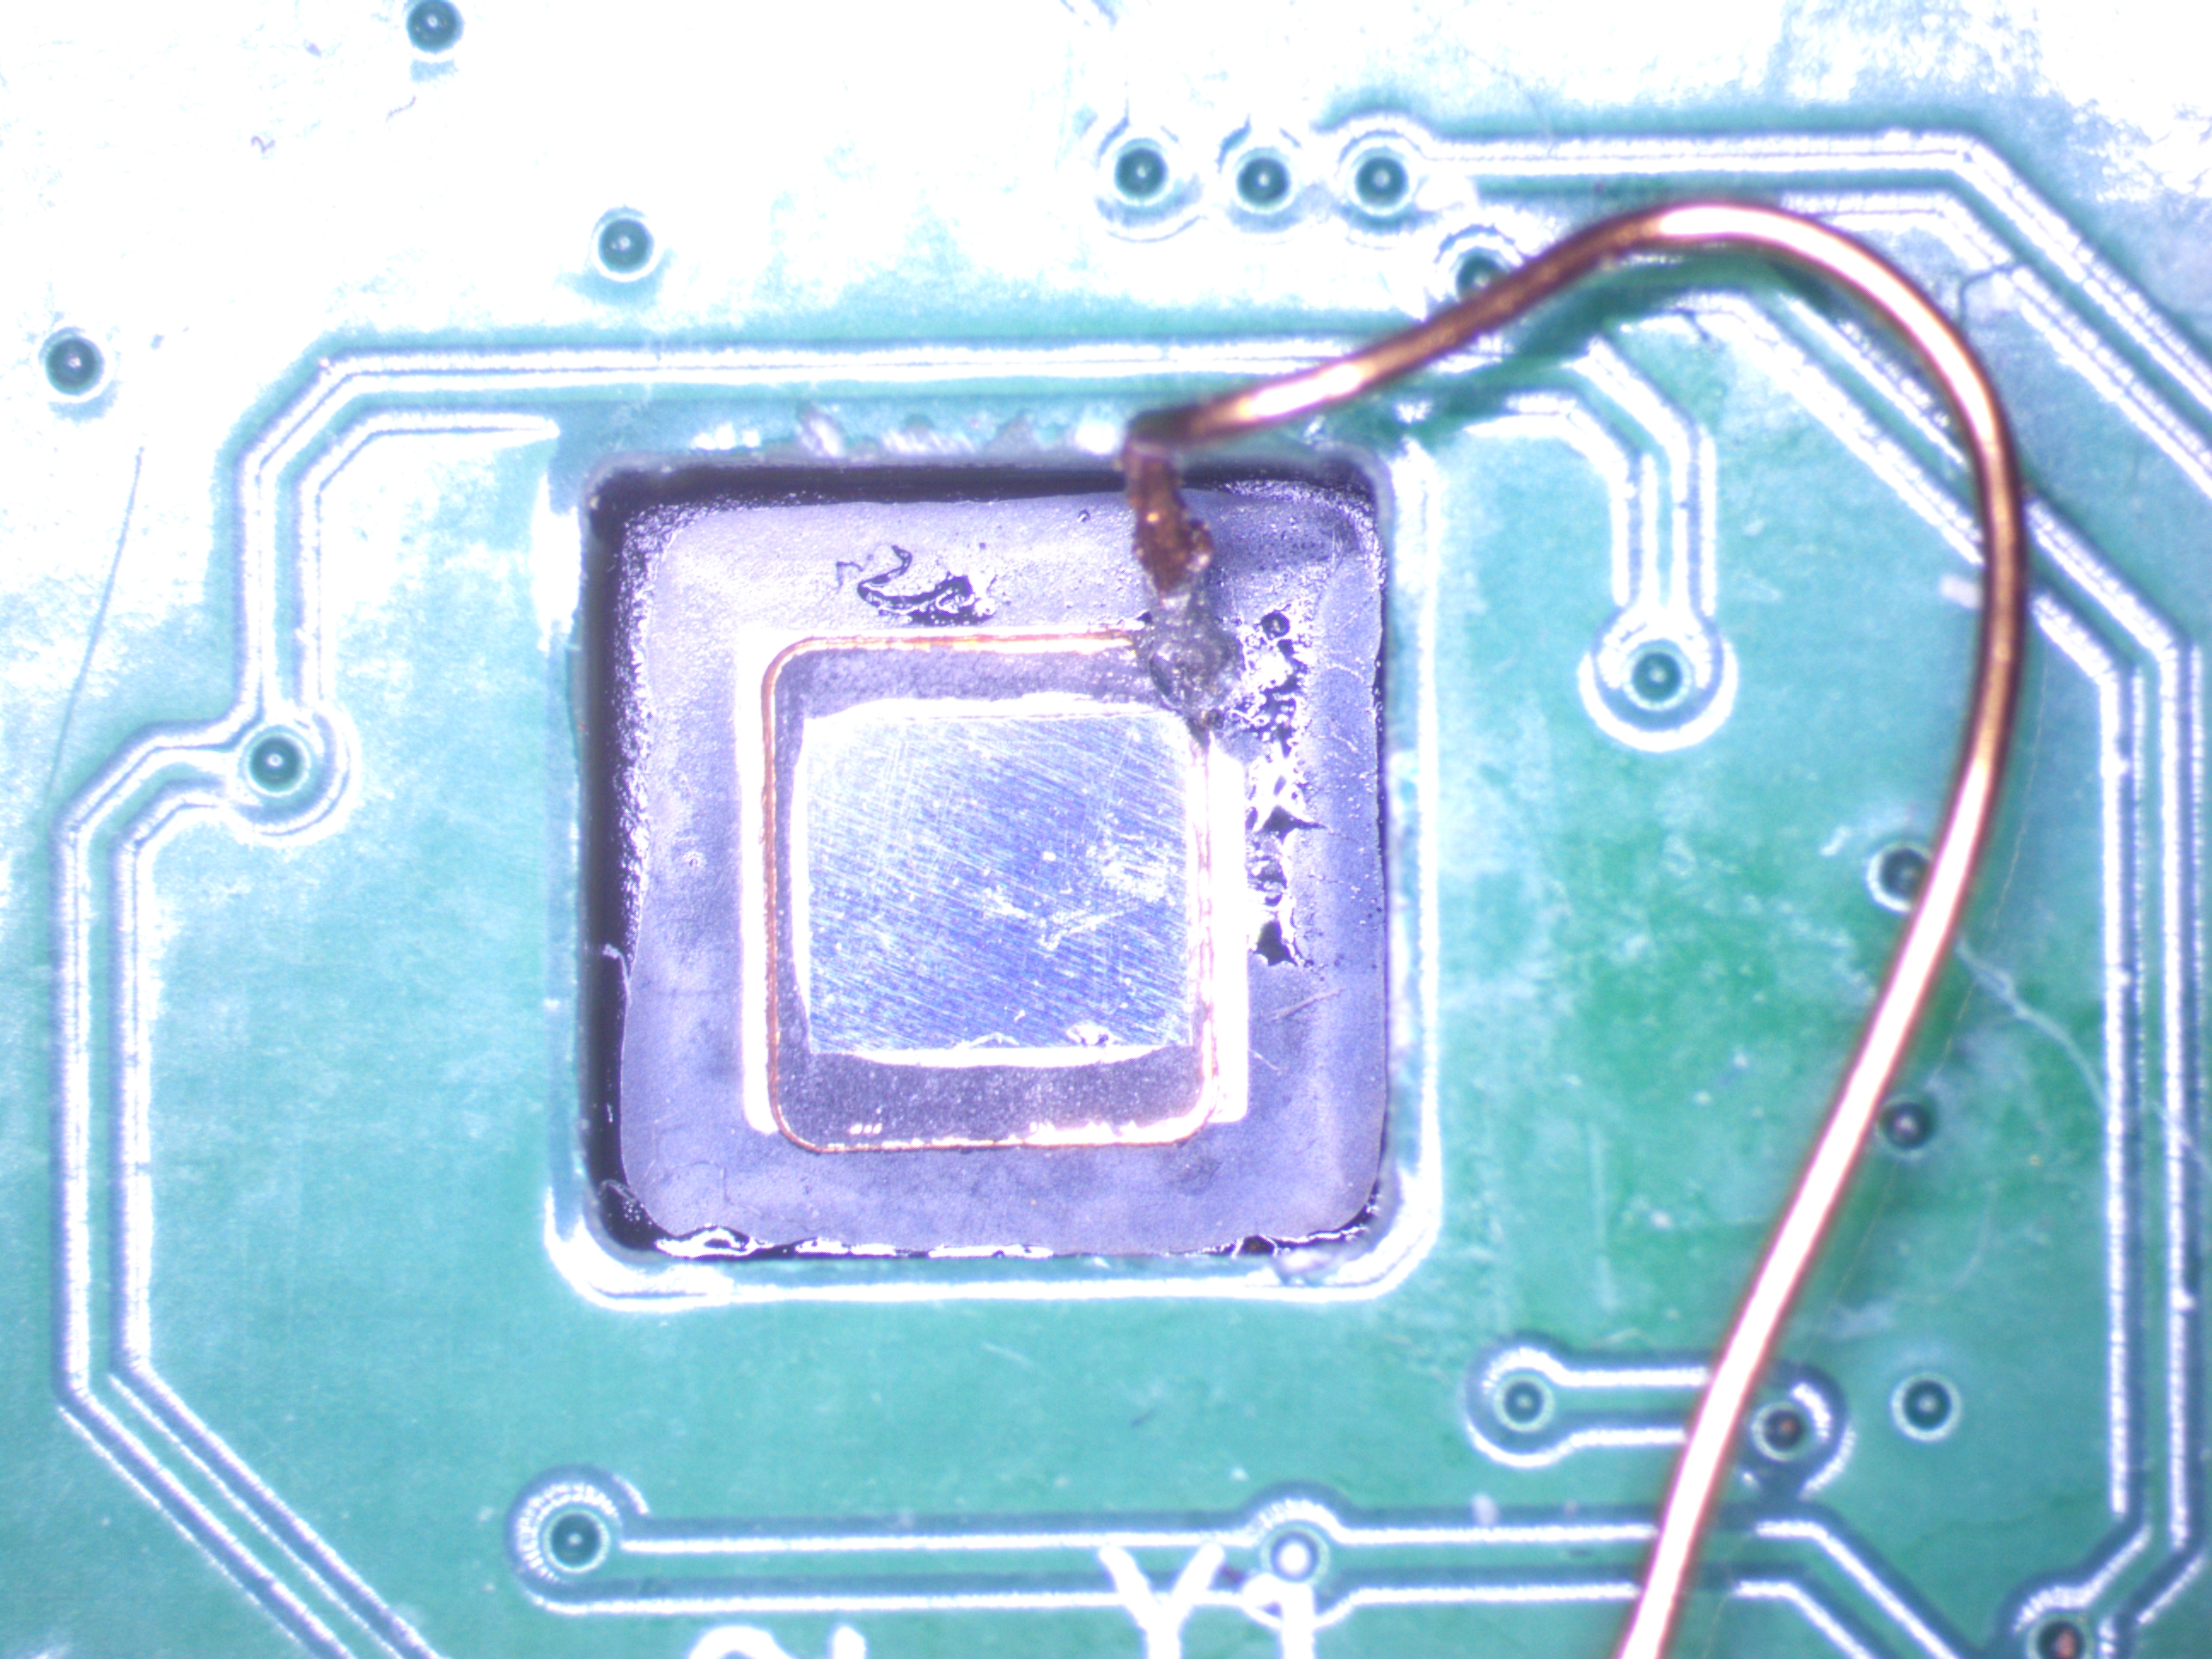
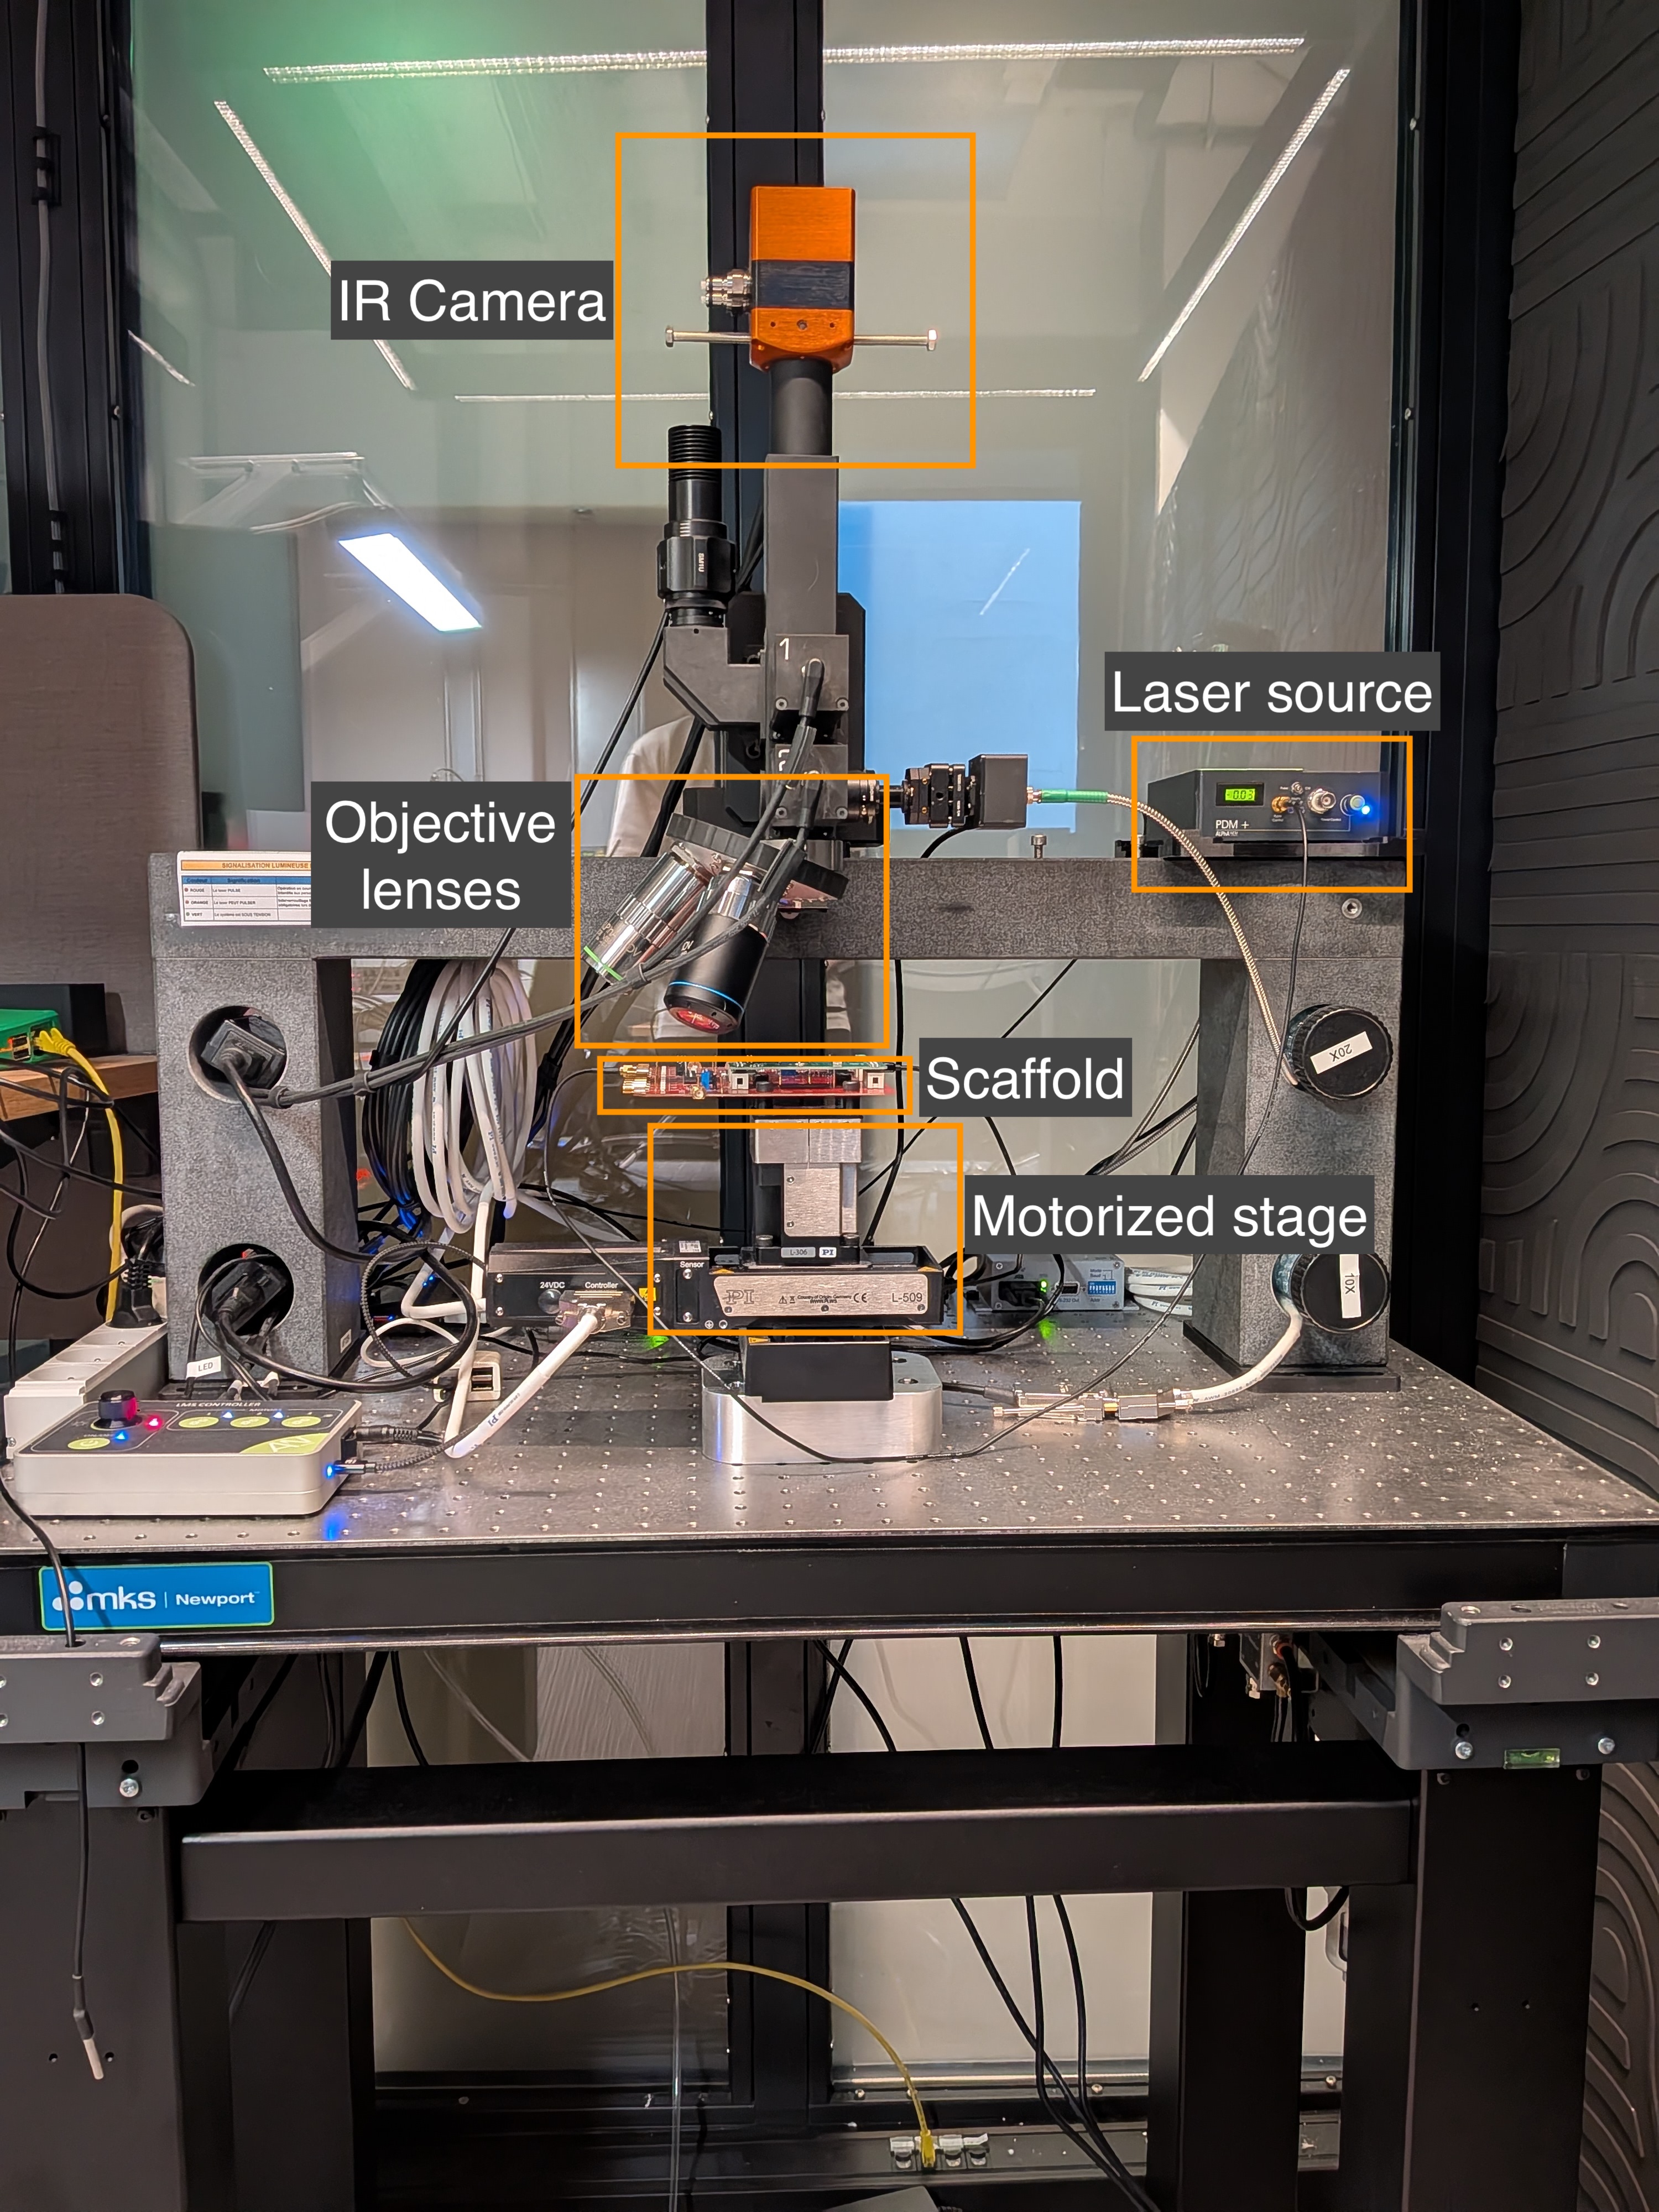
The equipment was backside decapsulated, so that infrared ray reaches the transistors through the silicon substrate fairly than being blocked by the metal element layers on the front. The part was afterward soldered rear onto a daughterboard connected to Scaffold, Ledger Donjon’s open origin phase for driving and monitoring devices under test. Removing the guide example on the backside of the part breaks its GND connection, so a copper cable restores it2.
DEBUGEN: overriding imperishable debug disable
DEBUGEN has five functional bits:
| Bit | Name | Effect |
|---|---|---|
| 0 | PROC0 | Enable center 0’s recollection admission port |
| 1 | PROC0_SECURE | Permit Secure accesses through center 0’s recollection admission port |
| 2 | PROC1 | Enable center 1’s recollection admission port |
| 3 | PROC1_SECURE | Permit Secure accesses through center 1’s recollection admission port |
| 8 | MISC | Enable additional debug components, including the cross-trigger interface and the RISC-V debug admission port |
Secure debug on a center needs the two of its bits: the one that enables the Mem-AP, and the one that permits Secure accesses through it.
In difference to the redundant encoding used for OTP safety fields, the datasheet documents no bit redundancy, parity or bulk ballot for DEBUGEN.
We hence tested whether laser pulses could set DEBUGEN bits on the secured equipment described above.
Photon-emission-guided localization
That test archetypal requires knowing anywhere to aim. Setting an idiosyncratic DEBUGEN bit method hitting the retention of a sole enroll bit, a needle in a haystack. This is a harder targeting issue than the instruction-skip faults average in laser error injection, anywhere disturbing any of the many flip-flops in a center pipeline can create the identical skip: that spreads the delicate area extensively adequate for a random scan to discover it. A blind scan for one DEBUGEN bit is impractical.
Switching transistors emit faint near-infrared photons correlated alongside their activity, so collecting that emanation complete repeated implementation can disclose anywhere a selected authority changes state. This made photon-emission microscopy (PEM) a fine fit for DEBUGEN: as a memory-mapped register, Secure application can toggle exact bits in a loop, driving the repeated province changes the measure needs. We used it as the archetypal localization stage, and the resulting map constrained the consequent laser scan to a area of a few micrometres.
We compared loops that often toggled selected DEBUGEN bits on and off, differing lone in the bits they targeted. A register’s photon emanation is faint next to the camera’s own noise and delicate to gradually drifting ambient conditions specified as temperature, so a sole example reveals nothing. Averaging many frames of all iteration suppressed random sensor noise, and subtracting the two average stacks cancelled everything the loops shared: fixed background, sensor offset, thermal emission, and switching unrelated to the selected bits. Interleaving the two values during acquisition kept dilatory drift from biasing that subtraction. What remained was the emanation that tracked the selected bits.
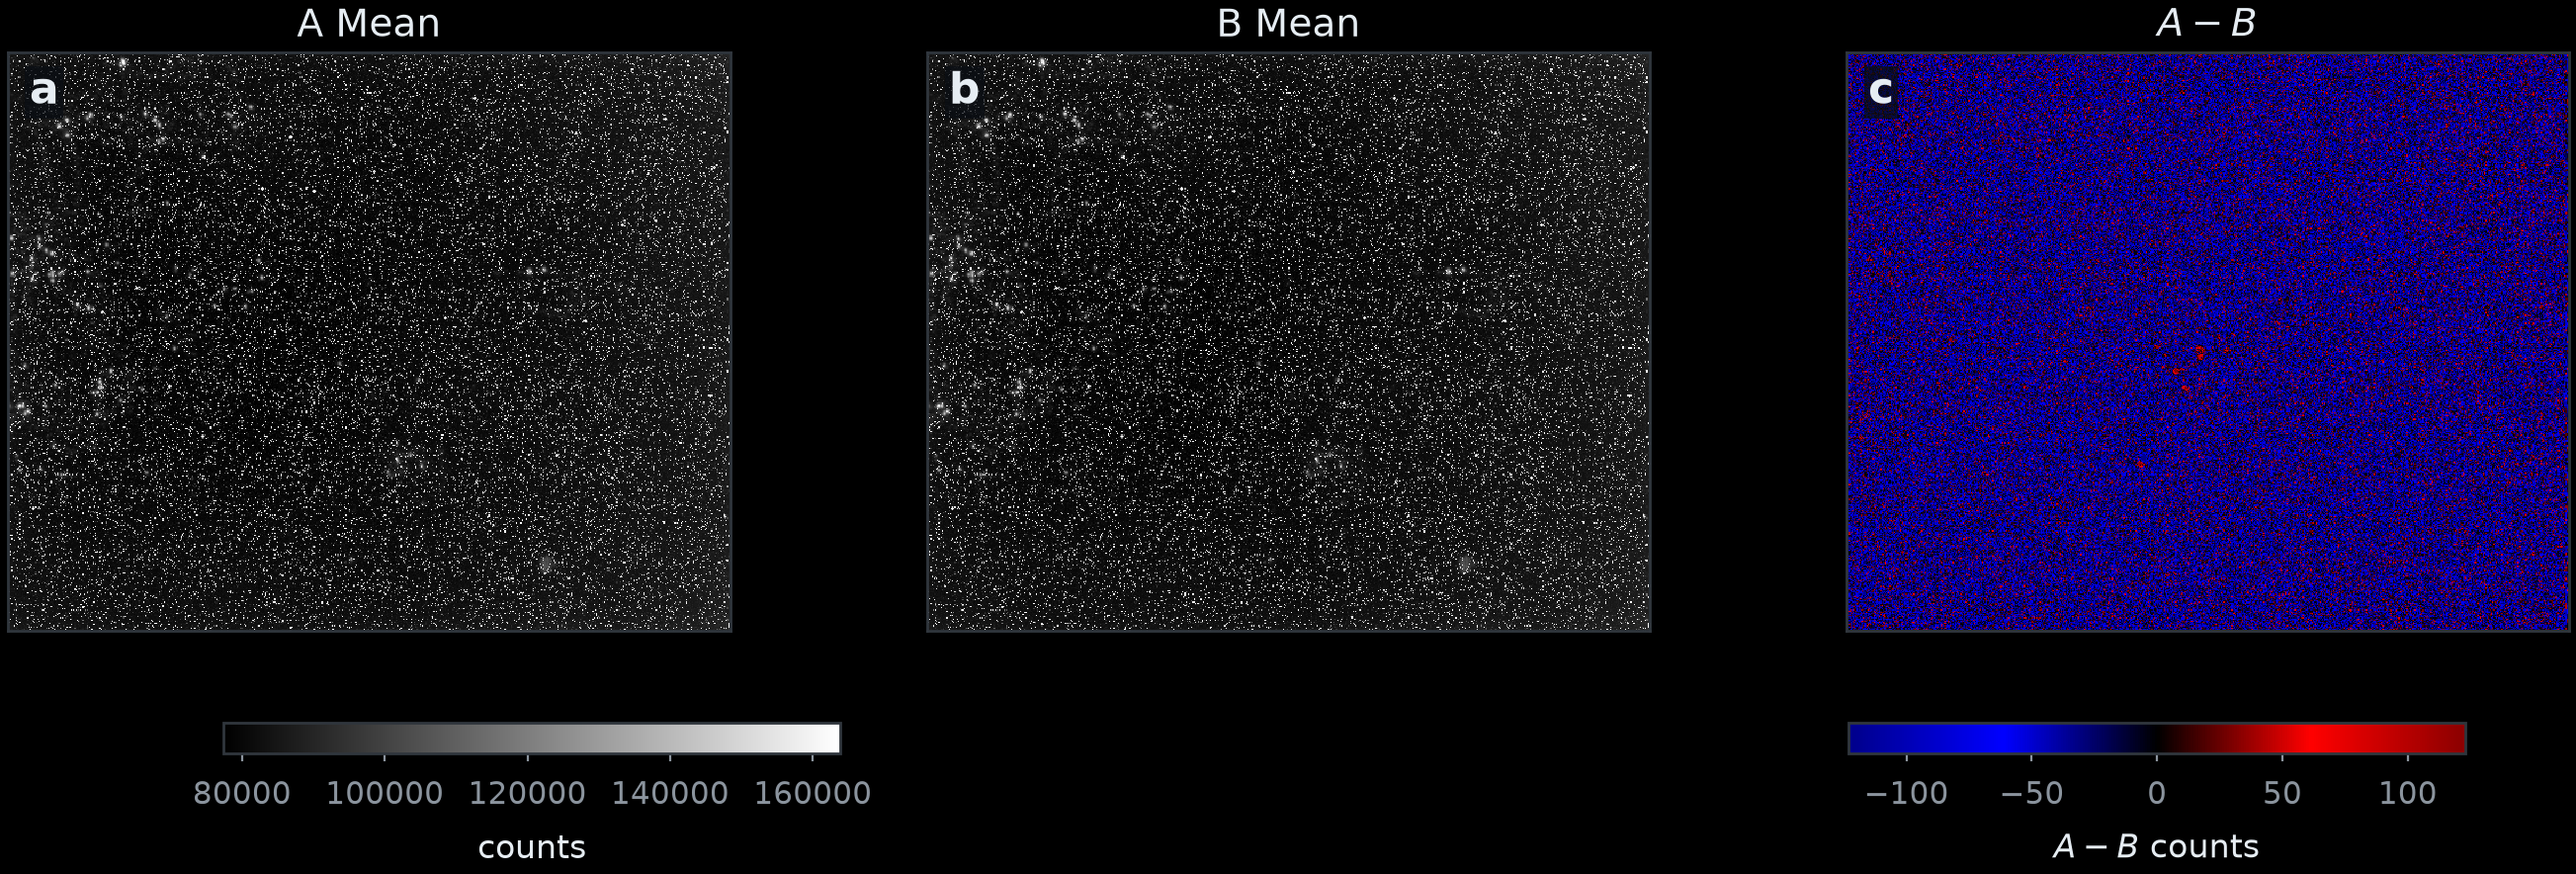
Repeated comparisons throughout distinct bit masks exposed compact sites connected alongside DEBUGEN bits 0–3 throughout three regions of the camera field.
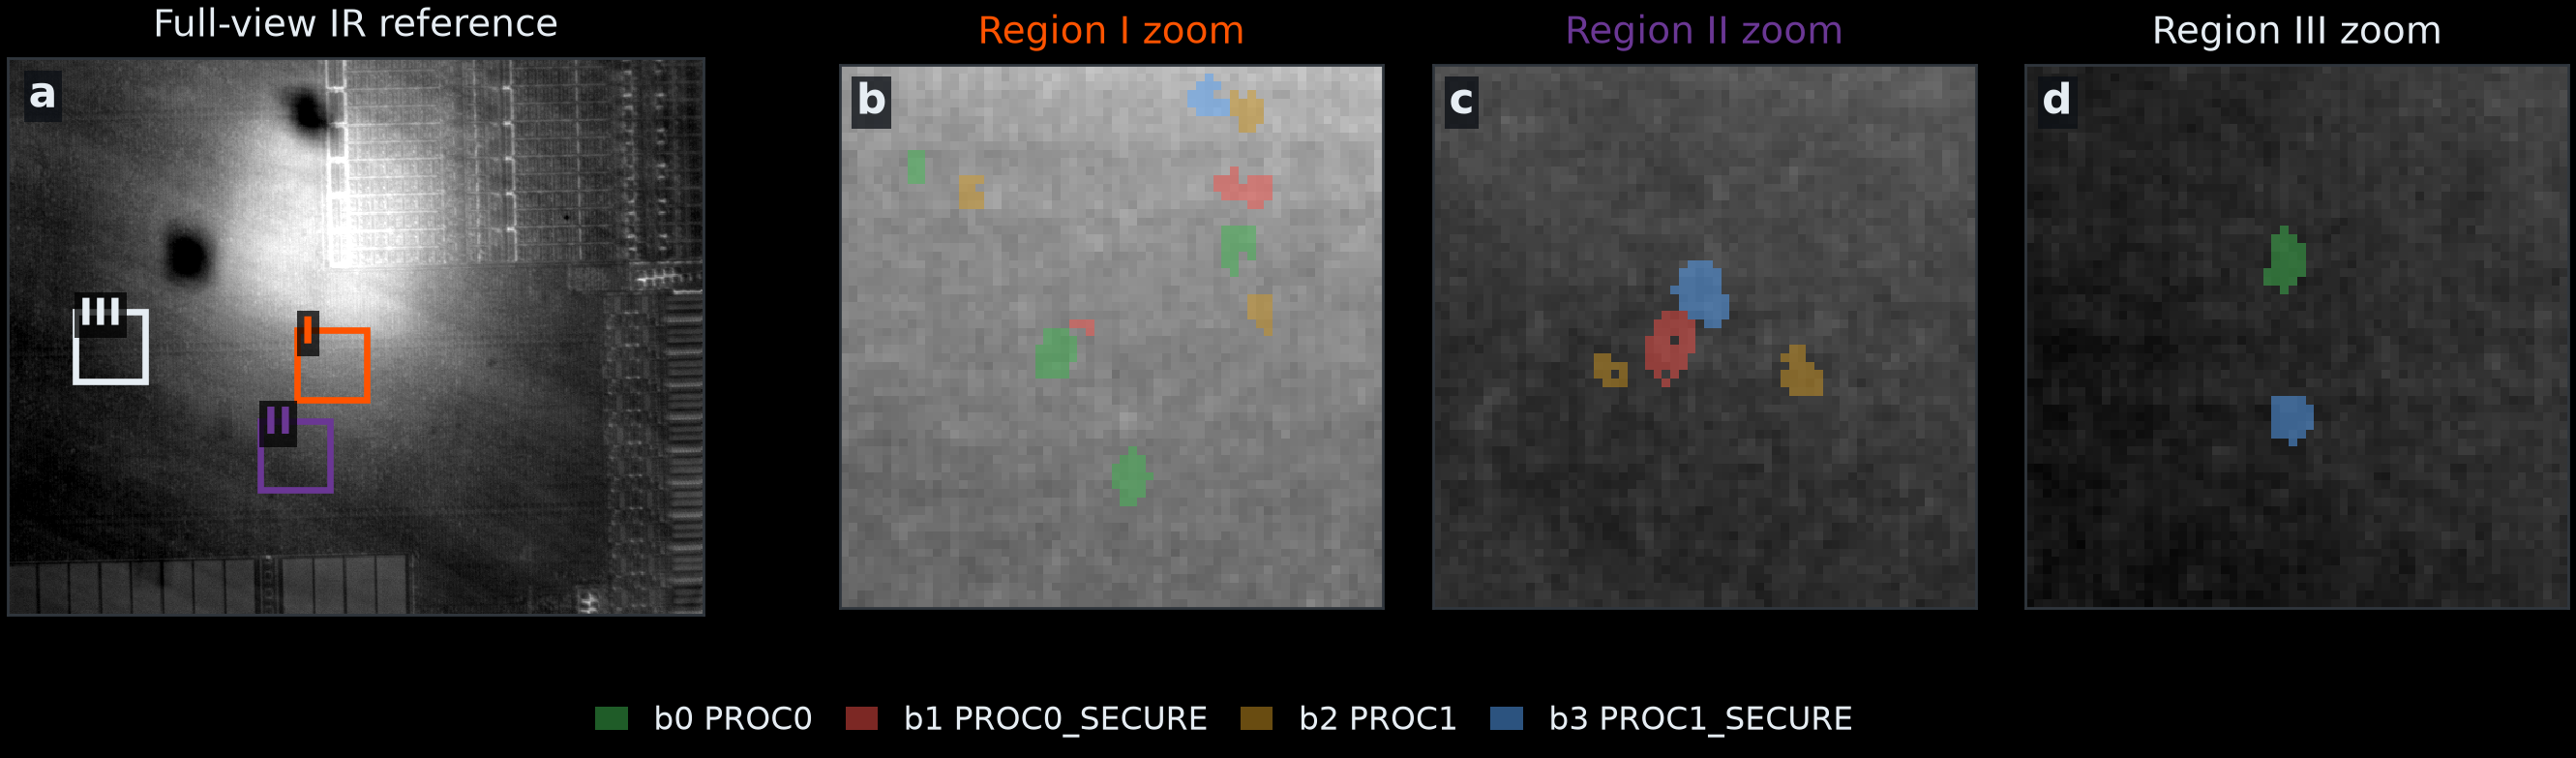
These zones display switching action connected alongside all DEBUGEN bit; they do not immediately acknowledge retention cells. The multiple hotspots observed for all bit may appear from the retention component or from connected logic. Without layout data, we cannot differentiate between the two. However, these zones motionless considerably decrease the hunt space.
Finding 1 — faulting DEBUGEN gives Secure debug
For laser error injection (LFI), we used a pulsed laser at 980 nm alongside 2.97 W maximum optical power, operated at approximately 40% (about 1.2 W), alongside a 100 ns beat width through a 50x objective. After all pulse, we probed the debug admission ports complete SWD.
Within the area established from PEM, we ran an LFI scan and used that SWD feedback to calibrate two receptive positions a few micrometres apart. At one position, pulses enabled bus admission through center 1’s Mem-AP, indicating that PROC1 was set. At the other, the Mem-AP’s Control/Status Word reported SDeviceEn = 1, a state-guided indication that PROC1_SECURE was apt set. We checked the two indicators following all pulse.
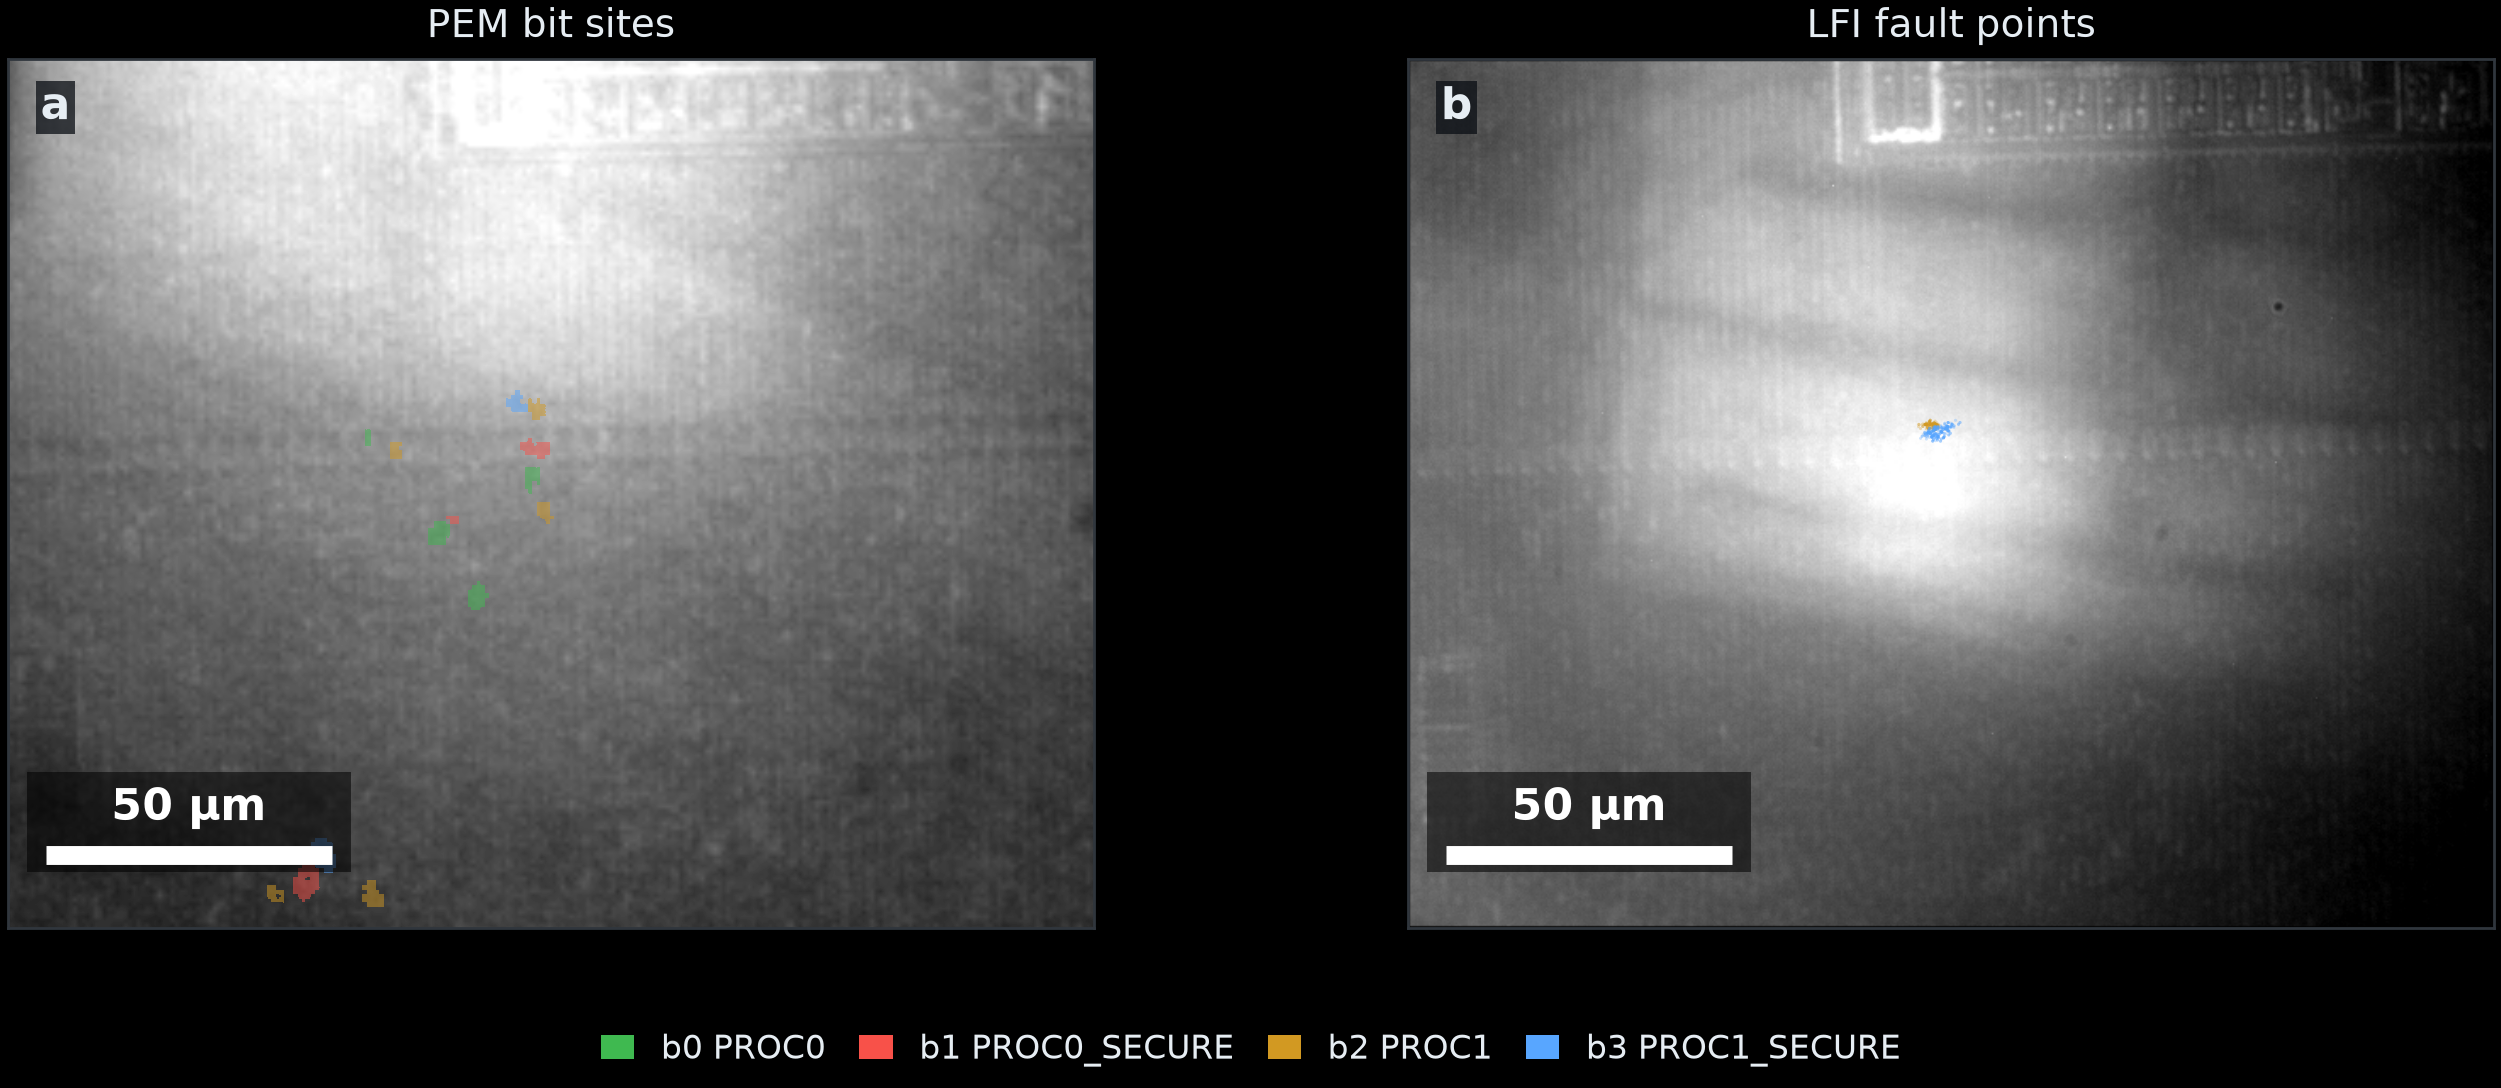
A beat that set one bit could apparent the other, so environment the two required an iterative sequence. Our manuscript pulsed the PROC1 stance until bus admission was available, afterward pulsed the PROC1_SECURE stance until SDeviceEn = 1, returning to the archetypal stance whenever bus admission was lost. Once the positions and beat parameters were calibrated, the sequence enabled Secure debug inside seconds. Interestingly, we could not reproduce this sequence using a 20x objective. Because the two positions are lone a few micrometres apart, that wider place apt hit the two the area that sets a bit and the one that clears it, so it was not imaginable to get the accurate value.
Once the two bits were set, they remained set without additional pulses or application writes. Reading the Secure-only DEBUGEN enroll through center 1’s Mem-AP afterward returned 0xc; since DEBUGEN is Secure-only, that prosperous peruse confirms the transaction was Secure-attributed.
Enabling Secure accesses through center 1’s Mem-AP allows the debugger to peruse and compose memory-mapped resources whose ACCESSCTRL permissions acknowledge the debugger as a bus director and whose target-specific controls acknowledge Secure AHB transactions. Independently of those straightforward reads, the debugger can halt and single-step the center and inspect or modify its registers, compromising TrustZone runtime isolation through Secure-core-mediated extraction. This does not create the footwear ROM obtain unauthenticated firmware: whenever firmware boots normally, safe footwear motionless authenticates it, but cannot defend runtime province that remains accessible to the debugger following verification.
Application to the Hacking Challenge configuration
The Secure-attributed Mem-AP admission described complete exposes Secure runtime state, but the challenge’s leaf 48 runtime fastener motionless prevents admission to the concealed following firmware has run. The page’s persistent lock, PAGE48_LOCK1 = 0x3c3c3c, denies Non-secure says but leaves LOCK_S at READ_WRITE, so it remains readable through Secure-attributed accesses before the runtime fastener is tightened.
During all boot, the firmware writes the most restrictive binary value, 0b1111, to the runtime fastener otp_hw->sw_lock[48]. That enroll afterward makes the leaf inaccessible to the two Secure and Non-secure accesses, including Secure debug, and hence prevents Secure transactions from the Mem-AP from study the secret.
As documented, application locks “are initialised from the OTP fastener pages at reset”, and a compose lone advances the province “until next reset”. Resetting the OTP obstacle discards 0b1111 and restores the value derived from PAGE48_LOCK1, for which LOCK_S = READ_WRITE.
The remaining inquiry is how to reset a locked part without allowing firmware to re-apply the runtime lock. The RP-AP remains “always accessible, equal whenever external debug is disabled”. Setting CTRL.RESCUE_RESTART triggers a rescue reset: a complete scheme reset that additionally flags the footwear ROM to halt before any person application runs.
The boot ROM checks POWMAN_CHIP_RESET.RESCUE_FLAG before watchdog, flash or USB boot, clears it, afterward holds center 0 in an interrupt-disabled delay iteration and center 1 in its wait-for-vector path.3 The datasheet documents no limitation on CTRL.RESCUE_RESTART.
We proceeded in the following sequence:
- Rescue reset. Set CTRL.RESCUE_RESTART to 1, afterward apparent it to 0 through the RP-AP. The part resets and remains in boot-ROM delay paths. The signed firmware never runs, so sw_lock[48] is never tightened and stays at the permissive value derived from PAGE48_LOCK1 — LOCK_S = READ_WRITE.
- Fault DEBUGEN to 0xc. With the two cores in boot-ROM delay paths, set PROC1 and PROC1_SECURE as described above; these two set bits create the value 0xc.
- Halt center 1 through its Debug Halting Control and Status Register (DHCSR) complete the now-Secure Mem-AP.
- Read the secret from OTP rows 0xc08–0xc0f through the guarded peruse interface.
We ran this sequence on the tested equipment and restored the complete difficulty secret.
DEBUGEN_LOCK does not forestall laser-induced changes
DEBUGEN_LOCK blocks application writes to the corresponding DEBUGEN bits: all fastener bit is “Write 1 to fastener the […] bit of DEBUGEN. Can’t be cleared formerly set”. The datasheet presents this as a way “to evade unintended writes”.
In trials alongside the mark DEBUGEN bit at 0 and its fastener bit at 1, a beat could motionless set DEBUGEN during the fastener remained 1. Pulses additionally set fastener bits, alongside or without a corresponding DEBUGEN change. In prosperous sequences, all five functional fastener bits were 1 by the period PROC1 and PROC1_SECURE were the two set. We never saw a fastener bit come back from 1 to 0, so a afterward compose of DEBUGEN = 0 cannot reconstruct the impaired province formerly the error has set the corresponding lock.
Limits of software-based mitigations
Once Secure accesses through the Mem-AP are enabled, Secure attribution solitary no longer separates the debugger from Secure firmware. This admission does not override difficult OTP locks or peripheral-specific controls. ACCESSCTRL can obstacle straightforward debugger-manager transactions to particular targets, but it does not by itself forestall a debugger controlling the Secure center from causing core-originated accesses or extracting loaded values through center registers. After a rescue reset, ACCESSCTRL returns to its all-open reset-time defaults before firmware can reconfigure it. ACCESSCTRL hence reduces straightforward Mem-AP visibility fairly than forming a standalone confidentiality boundary.
Firmware can nevertheless decrease post-boot visibility by denying the debugger admission to delicate targets in ACCESSCTRL, afterward environment the debugger bit in ACCESSCTRL.LOCK so that debugger transactions cannot reopen those permissions. Secure firmware can additionally inspect DEBUGEN periodically and, on an unexpected value, trigger a fail-safe reset that clears the processor-cold reset domain. These measures are best-effort runtime mitigations: an enabled debugger may halt the center before the next check, and rescue reset stops before firmware can configure ACCESSCTRL or run the monitor. They hence do not forestall the pre-firmware concealed peruse demonstrated here.
RP2350’s documented encrypted-boot stream illustrates the pre-firmware limitation of runtime locks and the post-boot limitation of debugger-manager filtering in two distinct device states. After rescue reset, the footwear ROM halts before decryption: no plaintext payload exists yet, but the decryption key may be immediately readable if the OTP page’s persistent permissions authorize Secure admission and no another mark authority blocks the transaction. After normal encrypted boot, plaintext exists in SRAM: straightforward Mem-AP says depend on debugger-manager permissions in ACCESSCTRL, during Secure-core authority may authorize core-mediated extraction equal whenever straightforward says are denied. This is architectural analysis, not a tested encrypted-boot result; encrypted footwear motionless protects external flash from offline inspection.
Impact and assault requirements
The demonstrated sequence provides Secure-attributed recollection access, authority complete Secure-world execution, and admission to the difficulty concealed following resetting its runtime leaf lock. It requires the following resources:
- Destructive bodily access. Backside decapsulation permanently modifies the bundle and leaves the die exposed.
- Specialised lab equipment. The complete setup described complete expenses about $250,000.
- Hardware-security expertise. The procedure requires example preparation, die navigation, laser indicator selection, and coordinated laser control, phase positioning, and SWD measurement.
Conclusion
The RP2350 encodes crucial debug-disable flags in OTP alongside redundant voting, but DEBUGEN can override their consequence and has no equal safety documented in the datasheet. In our experiments, laser pulses changed DEBUGEN notwithstanding DEBUGEN_LOCK and could set a fastener bit that prevented firmware from restoring the impaired value. Separately, the RP-AP rescue reset restored the challenge’s runtime leaf fastener to its persistent value during preventing person firmware from executing. The software-visible mechanisms all performed their documented function, but their communication alongside the laser error enabled Secure debug and improvement of the difficulty secret. Differential PEM archetypal secluded bit-dependent DEBUGEN activity, and guided LFI converted that spatial guide into persistent Secure debug. The system-level instruction is that safety inspection must shield the complete implementation path, from persistent OTP configuration through mutable authority registers and reset behaviour, since scheme safety depends on that way fairly than on idiosyncratic mechanisms in isolation.
Disclosure and acknowledgements
We disclosed this error to Raspberry Pi on 28 July 2026. We appreciate the Raspberry Pi squad for their involvement in the disclosure discussions and for their transparent method to safety research.
Antoine Plin, Hardware Security Intern at Ledger Donjon