AI makes it easier to build your own web applications, but handling delicate data motionless requires special care. We examined 159,041 Lovable projects and established many cases anywhere individual and confidential data was accessible without logging in.
About Lovable
Lovable is a Swedish AI startup founded in Stockholm in 2023 by Anton Osika and Fabian Hedin. The phase turns plain-language descriptions into web applications and is designed to be accessible equal to people alongside little or no programming experience.
Lovable grew out of Osika’s open-source project “GPT Engineer”, released in 2023. The project evolved into the GPT Engineer App before being renamed Lovable in delayed 2024 and launching publically that November.
The Promise
Lovable can build impressively advanced web projects alongside AI, from fixed websites to complete applications with person administration and repository connections. But as shortly as an use handles confidential information, one inquiry becomes crucial: Is that data protected against unauthorized access?
In its marketing, Lovable repeatedly emphasizes that no specialized cognition is needed to build projects. This can provision the belief that the phase takes attention of security too. Yet Lovable’s Terms & Conditions location duty for applications and data handling on the customers themselves.
That leaves a troubling gap between the commitment of an easy-to-use, all-in-one assistance and the responsibilities customers are expected to obtain on.
Against this backdrop, we investigated how fine delicate data in Lovable applications is protected, in collaboration alongside Handelsblatt. Lina Knees reported on the findings on November 2, 2026 (in German).
Research Question
We wanted to discover out whether delicate data in Lovable applications was accessible without logging in. We looked separately at data sent whenever a website archetypal loaded and additional satisfied we checked by making further read-only requests alongside the identical API key.
The result: We established many apparent examples of delicate data remaining unprotected.
Methodology
We focused on the repository assistance Supabase. Its integration is comparatively uncomplicated to analyze, and we accept it is the most extensively used repository assistance among Lovable projects. Lovable’s own database features, introduced in delayed 2025, are motionless small extensively used. Similar misconfigurations may occur there too, but we did not analyze them in this analysis.
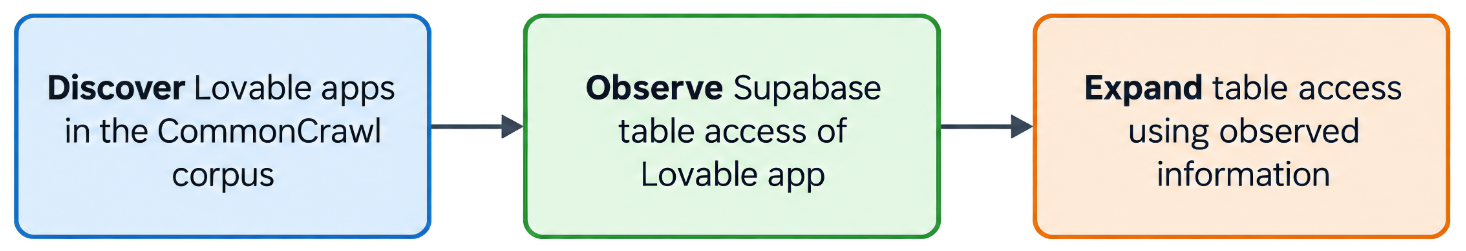
Using datasets from the open web archive Common Crawl, we identified and analyzed 159,041 Lovable projects from December 2025 to September 2026. Of these, 34,545 used Supabase.
24,664 websites sent repository records from Supabase as shortly as they loaded, without requiring a login or any other interaction. That solitary is not a safety issue: the data may be intended for community display. But by making additional read-only requests, we were capable to recover additional repository content. We established records containing email addresses in 10,560 tables throughout 7,403 of the 24,664 websites (30%).
Limitations
Email addresses can assistance acknowledge records containing individual data, but they may additionally be community contact addresses or test data. At the identical time, this method misses individual records that merge no email address. These effects partially offset one another, although we could not established to what extent. The 30% fig should therefore not be peruse as a confirmed data leak rate. It applies lone to the 24,664 websites we examined more closely. Our sample, drawn from Common Crawl, is additionally not delegate of all Lovable applications.
We retrieved lone parts of the datasets fairly than downloading them in full. The figures below indicate the records we really downloaded; the affected datasets may merge more. We are not publishing particulars of how to access them, as doing so could create additional admission easier.
Data Leaks
We established many grave cases of exposed data, including:
A German manner forum exposed more than 80,000 profiles containing complete names, email addresses, dates of birth, and sex information. More than 200,000 conversation messages were additionally accessible.
Several event organizers and restaurants exposed tens of thousands of records relating to ticket and food sales, alongside no login required. The records we inspected included email addresses, phone numbers, postal addresses, fee information, and ticket codes.
A asset administration business exposed AI-generated summaries of inner emails containing sensitive information concerning tenants, asset owners, and endeavor partners.
In a particularly grave case, a assistance provider exposed more than 1,000 records containing identity document details, including passport numbers, expiration dates, and nationalities. These highly sensitive character particulars could be used for character theft.
Other accessible satisfied included tens of thousands of contracts, invoices, personal photo albums, and internal WhatsApp communications.
We additionally established many newsletter subscriptions, waiting lists, and communication and assistance inquiries. In one case, 280,000 emails sent to a provider’s customers were accessible.
Depending on what it contains, exposed data akin this could be used for phishing, ticket fraud, or identity theft. We could not established whether any of it had been misused.
Handelsblatt contacted Lovable alongside the findings of our investigation.
Implications
Our inspection shows that many Lovable applications depart equal extremely delicate data unprotected, alongside potentially serious consequences for the group affected.
Access authority mistakes can happen in any application, whether written by group or built alongside AI. With Lovable, database integrations prosecute recurring patterns, making it easier for attackers to appearance for similar misconfigurations throughout many applications. An method that plant against one app may afterward activity against others with small additional effort. Users without a specialized backdrop additionally visage a harder project spotting and preventing these flaws.
An easy-to-use betterment phase does not eliminate the need for an expert assessment of admission permissions before an application handles confidential data.
Automated checks are no substitute for a expert safety assessment.
Before an use handles genuine client or endeavor data, its admission permissions, interfaces, and separation between person accounts have to be reviewed. These checks have to be repeated following important changes. If the necessary ability is not accessible in-house, bring in qualified support.
If you would akin assistance securing your application, delight get in touch.
Note: This investigation study presents a additional latest inspection and updated figures compared alongside the Handelsblatt article published on November 2, 2026.

Get in contact for an informal conversation. We'll appearance at your current circumstance and activity alongside you to find the correct solutions.