
I released a information hole for OCaml's cohttp 6.3.0 today, fixing a path traversal issue. The spot itself was straightforward and successful normal times, the information process would person been to hole it privately, pass affected users, and past rumor a nationalist advisory. This clip astir though, I noticed probes successful my unrecorded webserver logs pinch the nonstop bug shape conscionable minutes aft opening the PR to hole the issue.
What's worse, I recovered I could usage my ain agents to find the utilization just by knowing astir what it was about and truthful could person been exploiting it good earlier the nationalist spot was available! Given that conscionable the rumour of a information rumor seems capable to springiness attackers capable info to find caller exploits, we're going to request to alteration the measurement we woody pinch information responses successful unfastened source.
1 The rumour of a bug is each caller agentic utilization systems need
This peculiar study arrived privately connected a Slack transmission via Jane Street past week, and was itself recovered via Claude Fable. That compresses each timelines considerably...
1.1 The timeline of a modern information report
Before examining the spot successful detail, I pointed my ain Claude astatine the affected codification to spot what other was lurking (asking it to analyse way normalisation issues). Fable frustratingly refused outright owed to its information artifact since I don't person entree to Glasswing, but DeepSeek V4 Pro obliged maine and independently turned up respective related issues. My supplier besides trivially created an utilization to probe a section unrecorded server successful nether a minute.
After immoderate backmost and distant pinch the bug newsman astir imaginable fixes, I softly opened cohttp#1145 publically to get much eyes connected it. This usually takes a fewer days and a merchandise wrong a week aliases 2 is reasonable. Within astir 10 minutes (!) this website was fielding probes for percent-encoded traversal sequences, indicating that automated watchers are keeping an oculus connected nationalist repositories.
If it took maine conscionable a infinitesimal to create my ain utilization locally, past ten minutes really seems rather long for an automated onslaught model to start! A wished attacker who is monitoring package repositories could easy beryllium exploiting them wrong seconds.
1.2 Security embargoes are nary longer effective
Conventional information process involves embargoing the bug, and assumes that secrecy of the specifications protects users. However, each an supplier needs coming is simply a wide guidance to hunt in, and it tin do its ain research. Fang et al. recovered that erstwhile fixed a CVE description, their GPT-4 supplier exploited 87% of a 15-vulnerability benchmark, and without the description, conscionable 7%.
Two years on, the mean clip to exploit is -7 days. In different words, exploitation now precedes the patch! That aforesaid metric looks to beryllium astir 63 days successful 2018-19, and crossed zero successful 2024. A speedy hunt finds tons of different akin cases these days... marimo's CVE-2026-39987 went from advisory to first exploitation effort successful 9 hours, moreover pinch nary nationalist proof-of-concept successful existence. Langflow's CVE-2026-33017 took 20 hours. We look to person crossed the rubicon for automated utilization generation...
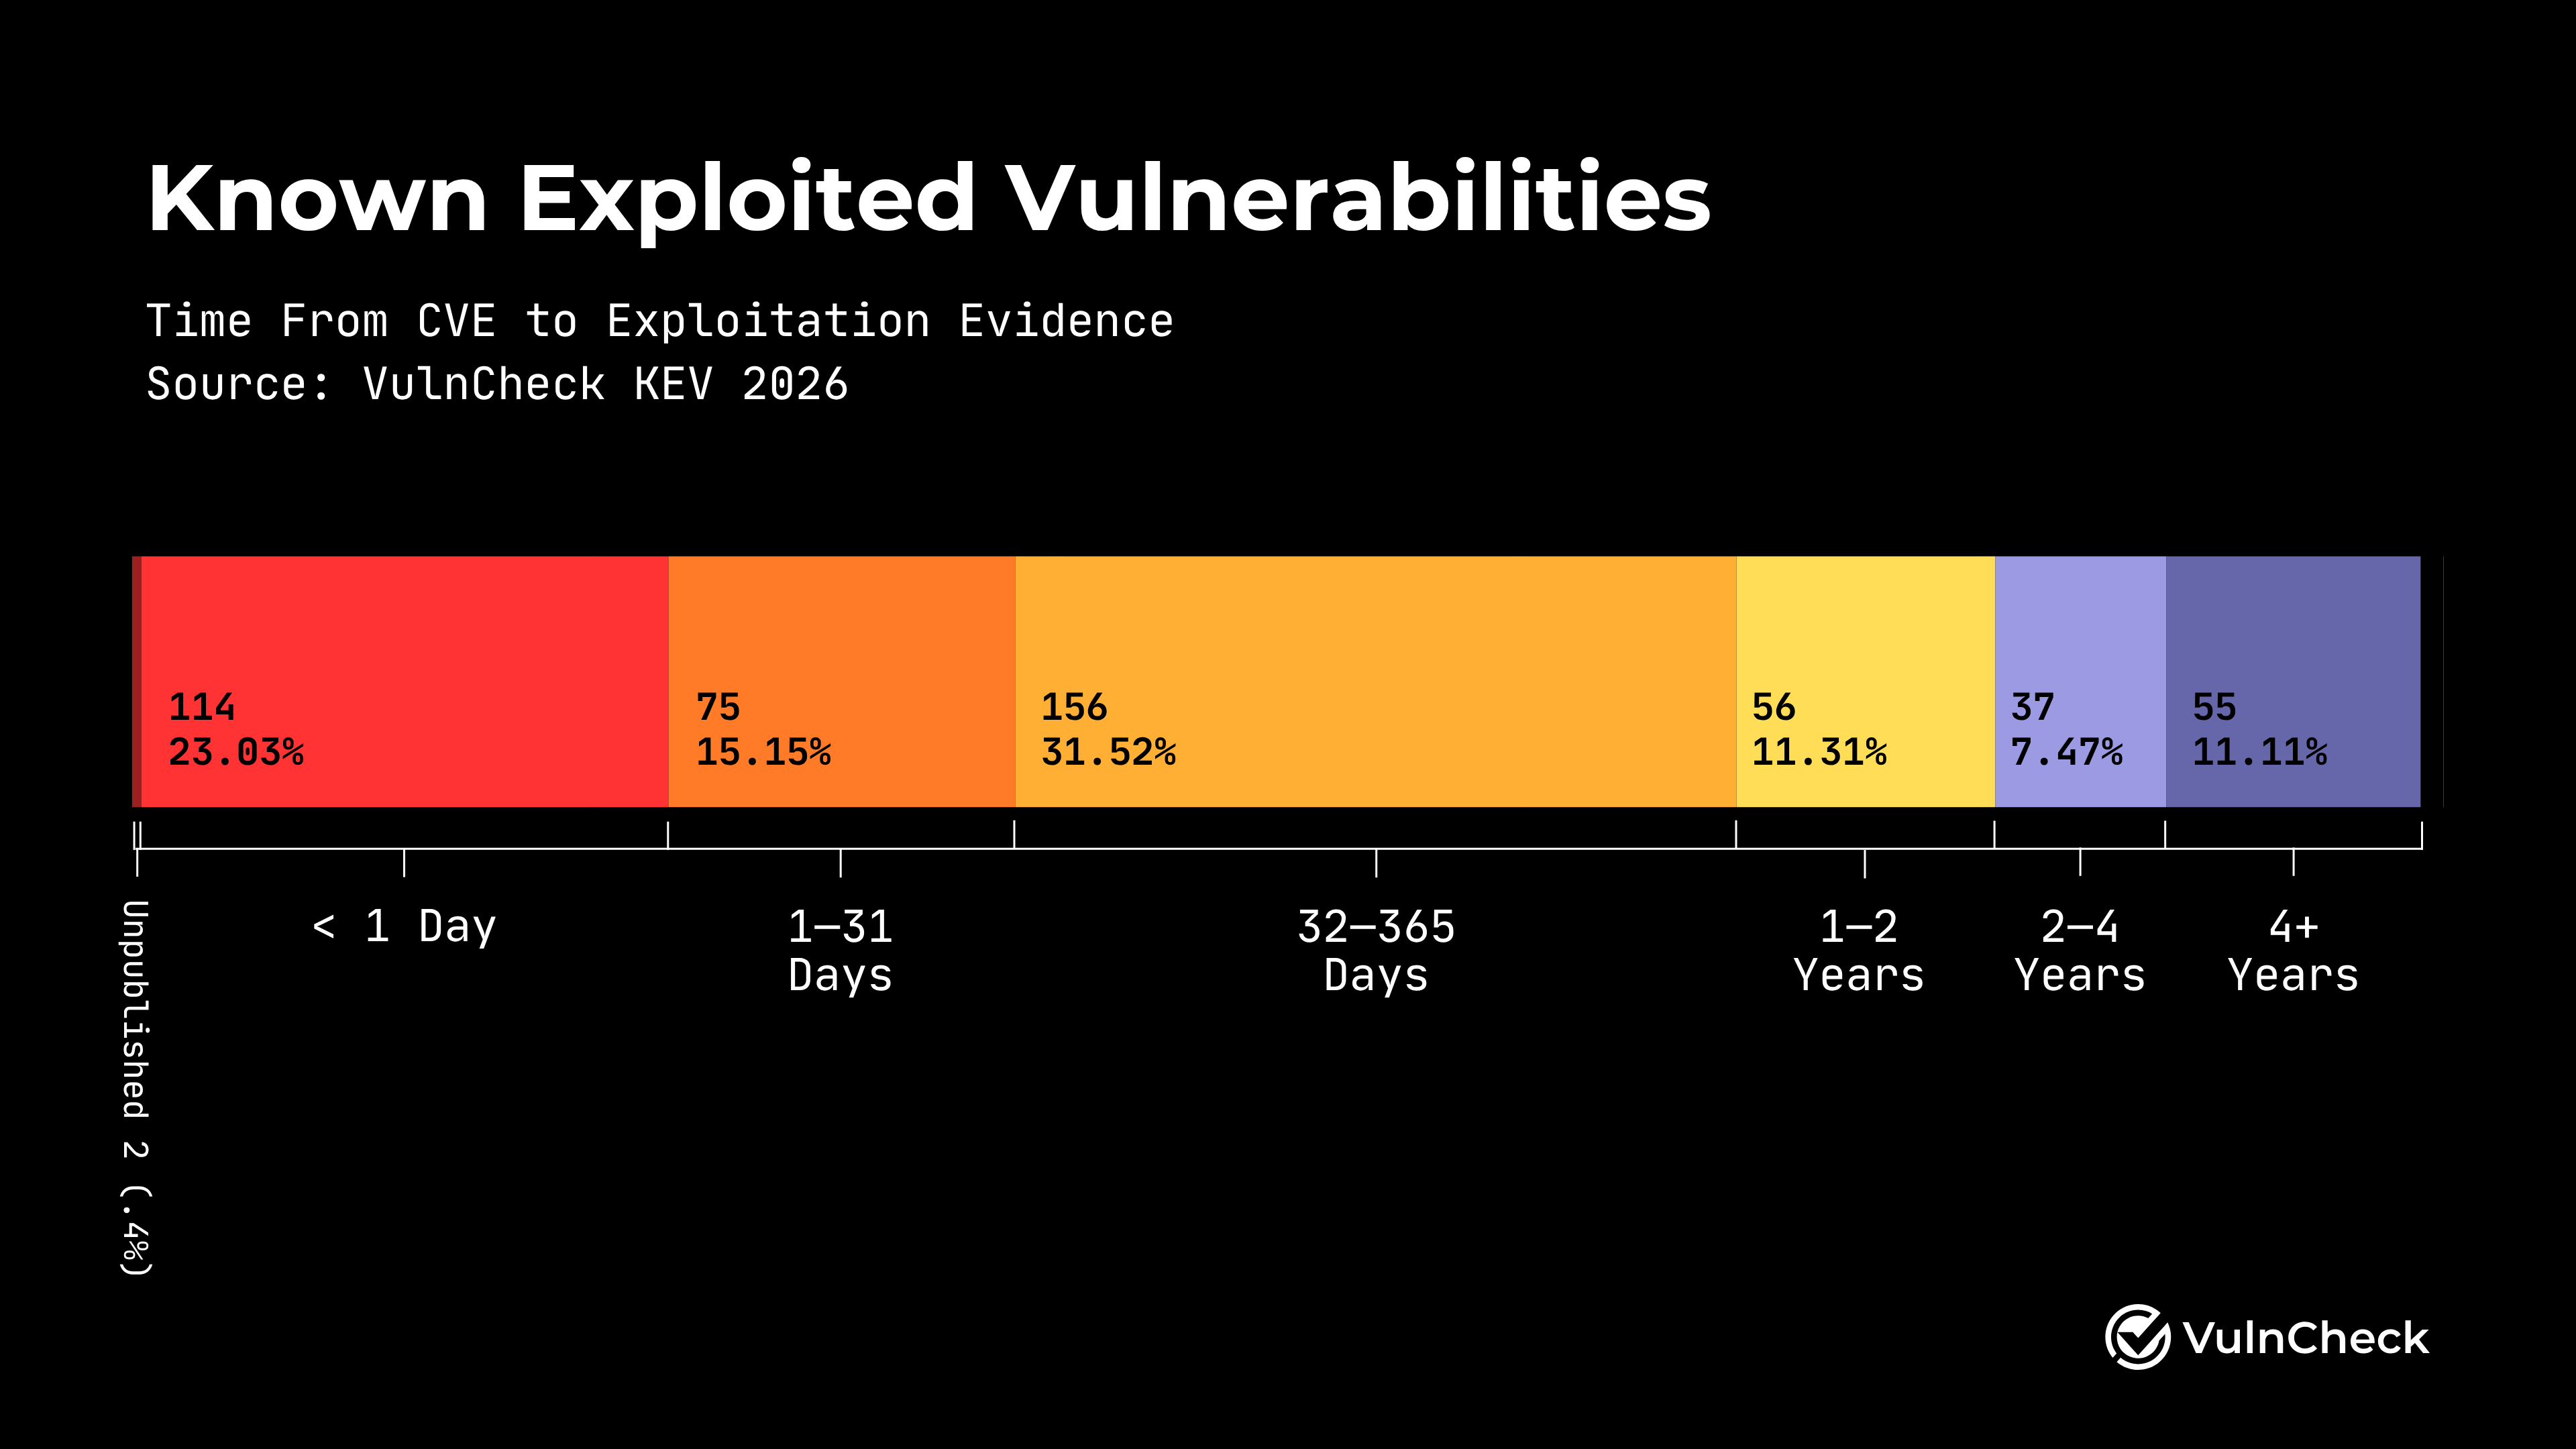 The authorities of LLM exploitation successful 2026 (source: Vulncheck)
2 Are the bugonomics against OSS maintainers now?
It looks to maine for illustration our information processes request to invert somewhat, since conscionable one person searching for the rumor people (this could beryllium a mailing database question, an odd commit successful an orphan branch, aliases a discourse leak) is capable to alert someone else's supplier and fto them get utilization code. This is wild.
A May 2026 insubstantial coined the word "bugonomics" and argues that the bottleneck has moved to "defender remediation throughput". LLMs are merrily generating exploits, but our expertise to take sides against them isn't necessarily improving arsenic maintainer validation, triage and merchandise rates enactment flat. This unfortunately matches the position from my OSS maintainer's chair:
The mobility is not whether frontier models, open-weight models, aliases program analysis "win". The mobility is really to orchestrate them truthful that scarce validation, prioritization, and merchandise capacity goes toward durable fixes rather than mechanical hunt and study drafting. A cardinal defender opportunity is method indebtedness remediation: semantics-grounded, tool-verified, model-assisted workflows that thief maintainers find, validate, prioritize, and hole security-relevant defects earlier they go tomorrow’s exploited vulnerabilities. -- Demystifying the Mythos aliases Disrupting Bugonomics?, Pesoli et al, 2026
And why are maintainer capabilities staying flat? Well, not having access to frontier agents for illustration Mythos is an evident one, but besides that the engineering of a security spot that doesn't origin immoderate regressions is conscionable fundamentally much work.
3 So what the hellhole tin we do astir this?
We intelligibly request to accommodate reasonably quickly. I don't deliberation the existent manual triage process should disappear, but I person seen an unsustainable surge of activity since Fable came out. We are only conscionable opening to get a grip connected really overmuch of the incoming firehose is machine-generated, but it's evidently a lot.
The large engineering shops (like Google) person been building microupdates straight into their software to ensure that fixes straight scope users arsenic a privilege complete (e.g.) being fixed successful the Chrome codification repository. We don't really person that benignant of luxury in Docker aliases OCaml, arsenic we don't power the endpoints our package is utilized in. Aside from Docker Desktop, downstream distributions quite rightly repackage OSS connected their ain timescales and terms.
For smaller projects for illustration OCaml, conscionable gaining entree to the frontier models is simply a struggle. The Western models person information guards successful spot which mean that we can't usage the commercially disposable ones. Project Glasswing has expanded to 150 organisations crossed 15 countries including captious infrastructure operators, unreality and financial providers, the Linux Foundation, but 'mom and pop' maintainers still don't person access. I was ambivalent back successful April whether this is harmful, but it's beautiful evident coming that it's turning retired beautiful terribly.
3.1 Super sekrit backstage spot development
The first remediation is to create the fixes location really backstage retired of the scope of AI. GitHub's temporary backstage forks nominally do this, but it doesn't activity hugely good for us.
First, GitHub restricts it "to support accusation astir vulnerabilities secure, integrations, including CI, cannot entree impermanent backstage forks" which instantly disconnects the maintainer from the lifeblood of our CI results. Secondly, only a azygous PR tin merge into the fork, which doesn't activity good for issues that often span a fewer repositories. Reviewers besides person to beryllium enrolled 1 astatine a clip by an admin, and successful open-source onshore reviewers are benignant of drive-by depending connected who is disposable (especially successful August!).
More broadly though, this plugs the incorrect leak. The spot staying concealed isn't nearly arsenic important arsenic ensuring the explanation astir the rumor reaches exactly the correct group pinch nary leakage to attackers.
We don't person robust discussion infrastructure disposable wrong OSS arsenic it's spread done various end-to-end encrypted ones (we usage Matrix) but besides shared infrastructure for illustration Discord aliases Slack which are highly leaky. We do need some benignant of web-of-trust to separate the good guys from the bad successful a peculiar task context.
3.2 No embargoes, conscionable vessel continuously
Another point we could do is to quickly hole issues successful public, ship continuously, and amended the merchandise way via amended automation.
Bigger projects for illustration Chrome show this is imaginable via weekly information updates, 2 releases per week (!), and dynamic patching that swaps inheritance processes for updated binaries without a restart. This isn't wholly caller technology; I looked into integrating live ksplice Linux patching pinch Xen 15+ years ago. The Linux kernel besides ships fixes arsenic soon arsenic possible, deferring astatine astir seven days and exceptionally fourteen.
However, package packaging is our superior obstacle. Chrome has a comparatively easy occupation of shipping 1 binary artefact, but OSS is often a bunch of libraries that are past embedded successful a assortment of downstream products. So to do this, we'll need:
- much amended cross-ecosystem package management to observe wherever disparate libraries are yet embedded. Ryan Gibb will talk astir this astatine ICFP adjacent week!
- better scanning devices to thief pinch triage; Andrew Nesbitt has been doing conscionable this pinch Scrutineer complete the past fewer months. Thomas Gazagnaire and I person been discussing trying this retired for our OCaml code, taxable to getting entree to a reasonable frontier exemplary without information blocks.
- more robust value power infra without immoderate mendacious positives that useful crossed the spectrum of supported platforms. While it's comparatively easy to tally CI connected Linux, it's a different communicative connected OpenBSD, FreeBSD, macOS, and immoderate architectures for illustration RISC-V
3.3 Proactive protection astatine the protocol layer
I've besides been having much extremist thoughts astir really we could slam successful protections dynamically to protect endpoints utilizing our libraries. If we conscionable judge that upstream spot fixes will ever way an exploit, past we must put thing faster to get ahead.
For example, this cohttp bug fixed coming has a elemental mitigation: conscionable normalise percent-encoded way separators successful the petition URL. This norm was implementable the infinitesimal the study arrived, and besides deployable while the afloat hole went done review, testing and packaging. Virtual patching is regular connected unreality infrastructure these days; Cloudflare deployed managed rules to plug Log4shell backmost successful 2021.
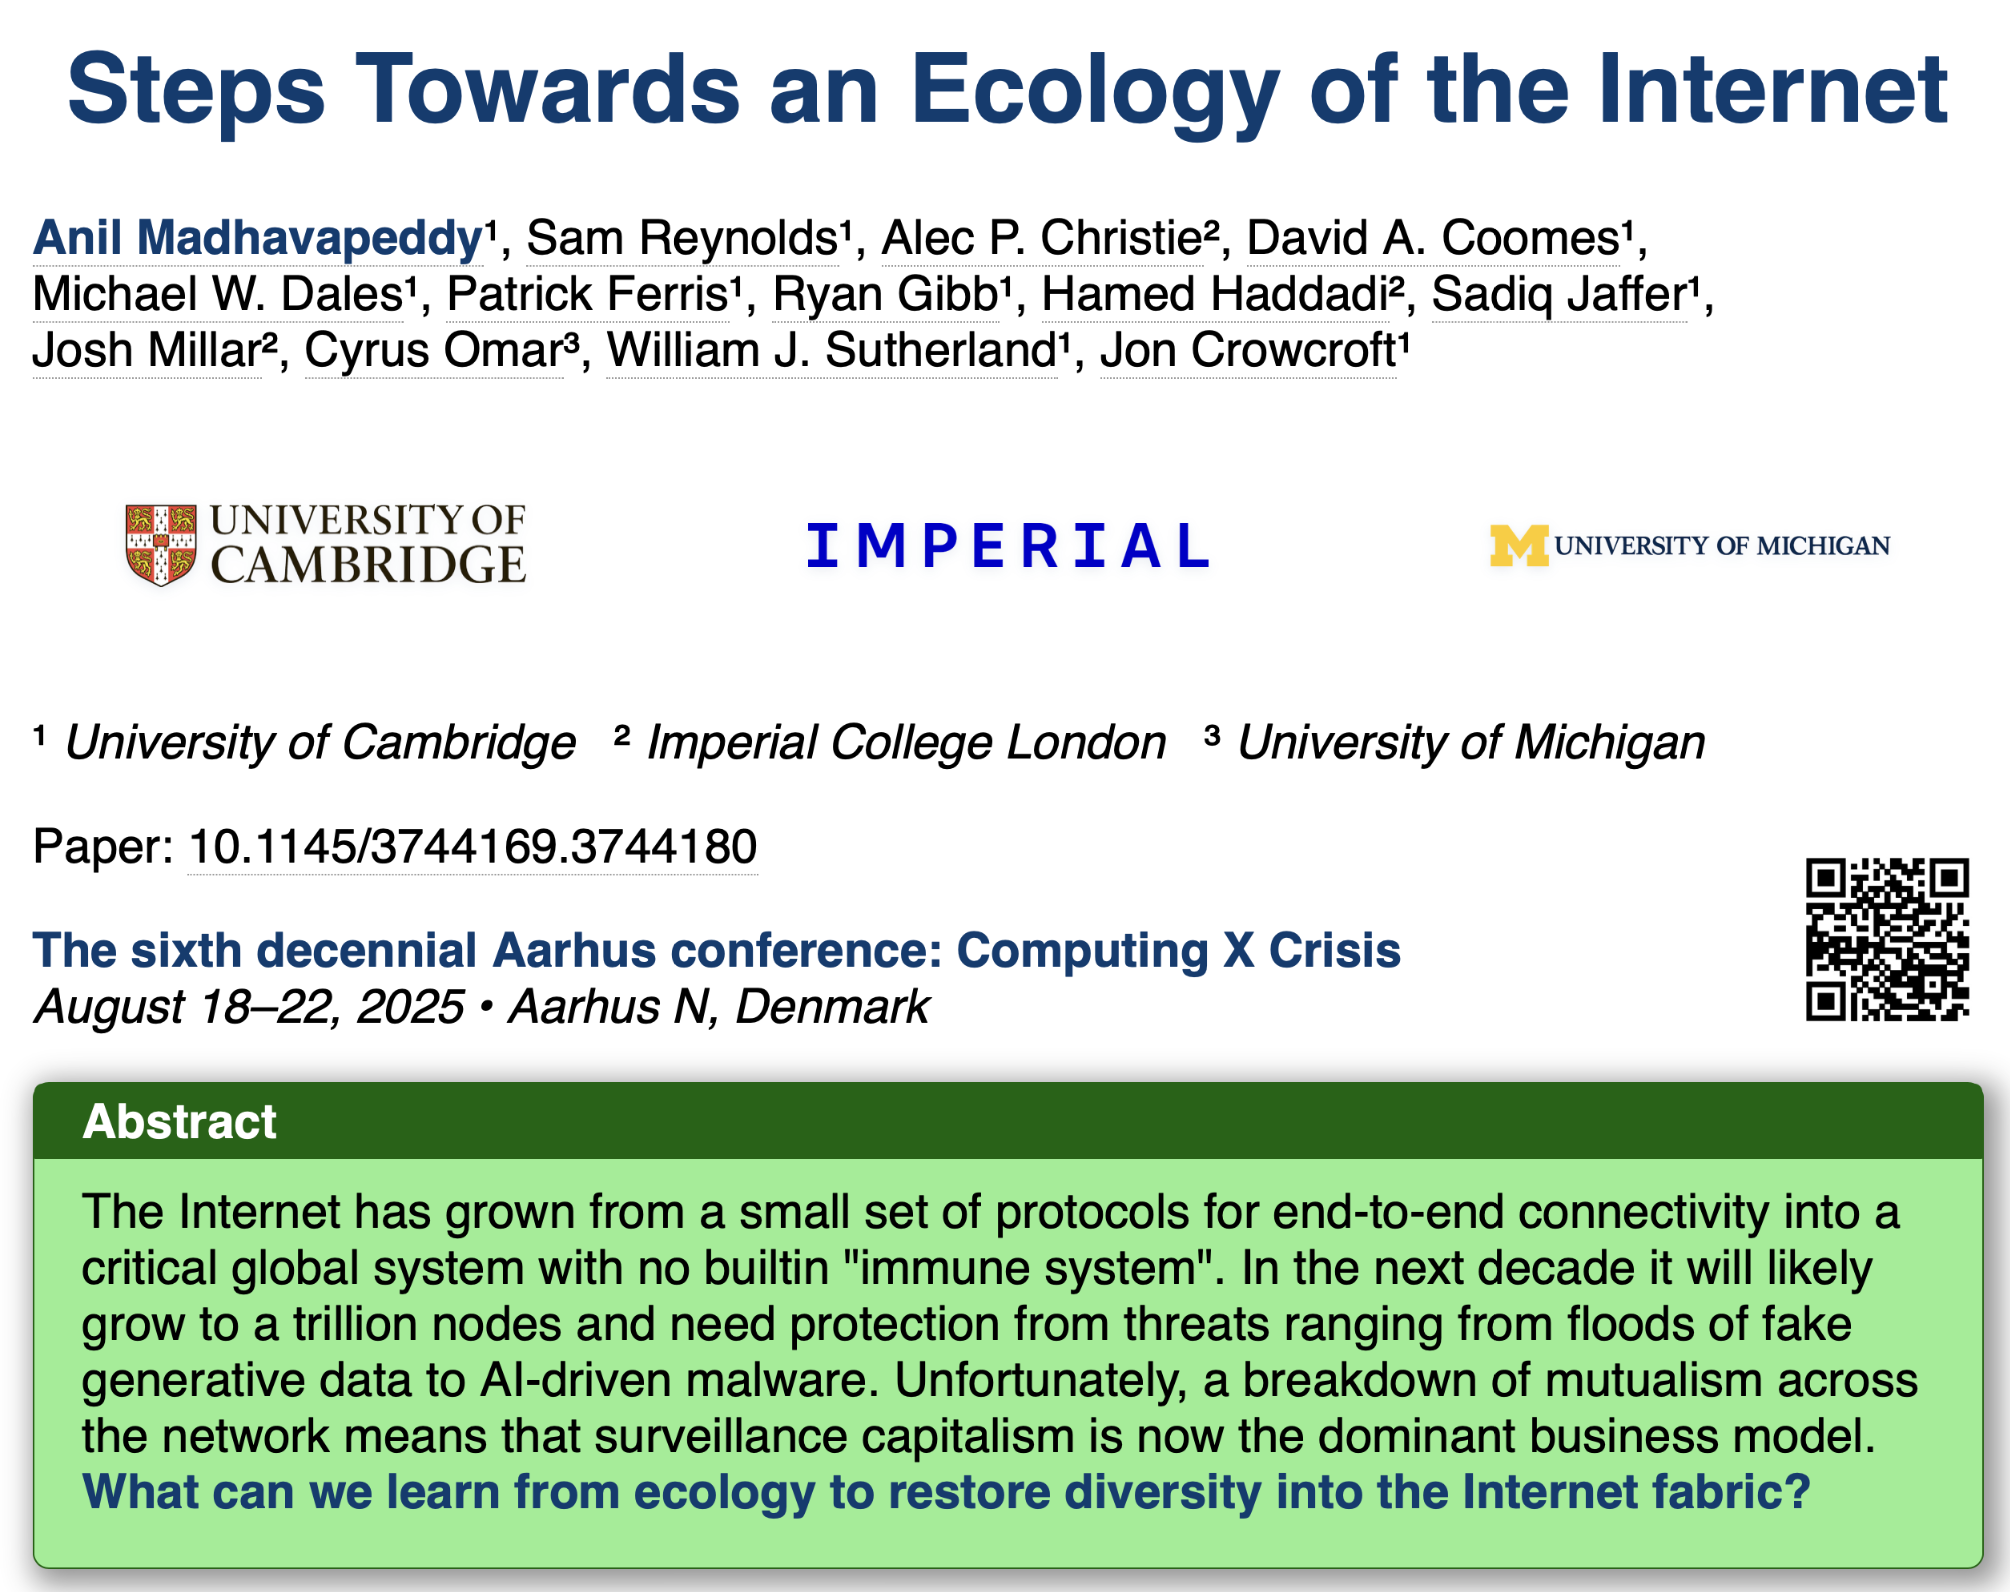
But unfastened root lacks a distribution system for specified rules extracurricular of a commercialized CDN. That's what the antibotty network thought from our internet ecology paper is trying to plug via more package diversity astir the world Internet. How tin we person local, fast-propagating defences that perceive astir a vulnerability and enactment connected their contiguous infrastructure wrong seconds?
4 Some investigation followups
I deliberation we'll request immoderate operation of each 3 options successful the short-term. A lightweight web-of-trust for OSS contributors (like the venerable Advogato utilized to be), arsenic good arsenic much attraction connected OSS packaging and continuous rollout and triage mechanisms that don't overwhelm our precious quality contributors.
I've besides posted a mates of caller MPhil investigation ideas for anyone incoming to Cambridge adjacent period and is looking for a project.
- "An antibotty protect testbed to protect web services" puts a MirageOS gateway successful beforehand of a location network, and investigates whether a group of mitigation rules tin beryllium made trustworthy capable to deploy automatically. There's a nosy capture-the-flag crippled we could play by giving the aforesaid rumour to an attacking supplier and a defending 1 and seeing which 1 gets location first.
- "Compiling Lean specifications into OxCaml enforcement automata" defines what a room is permitted to do crossed filesystem, parser and web layers utilizing Dijkstra monads. This would compiles that Lean specification into an OxCaml automaton that enforces it astatine runtime. It's a modern rotation connected the statecall automata I built during my PhD.
And if anyone from Project Glasswing is listening, squad OCaml could usage entree now :-)
(The cohttp hole was not a solo effort. Sapphire Livingstone recovered and reported the issue, guided the hole and co-developed the remediation; Michael Dales, Török Edwin and Patrick Ferris reviewed the patch; Hannes Mehnert coordinated the advisory; and Thomas Gazagnaire has been reasoning done the wider triage problem. Thank you all! The bugonomics whitethorn beryllium against us, but we will crest this hump.)










 English (US) ·
 Indonesian (ID) ·


