For the former few years, the tech industry has kept pushing passkeys as the supreme resolution to logging in. Many Big Tech companies “helpfully” communicate you all period you sign in how much easier and effortless passkeys are. The lone way to create them halt is either to concede and set up a passkey or dig into the settings to discover the off-switch.
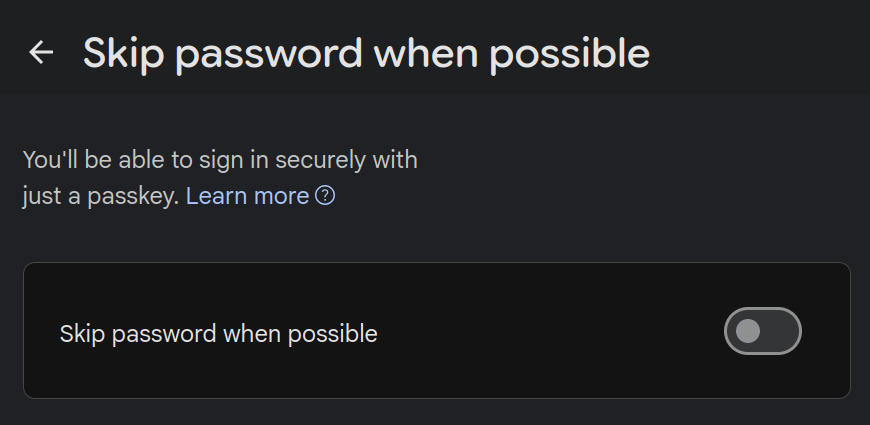
Google goes as far as to name the environment “Skip password whenever possible” (opens in a new tab), and Microsoft advertises that you should make your document passwordless (opens in a new tab).
Passkeys are a awesome technology. Since they are border to the location they are created for, they cannot be phished by a hacker’s counterfeit login screen. If a location suffers a data breach, passkeys are asymmetric and cannot be restored from the server-side details.
This leads to passkeys being the ideal fit for a company environment, but a mediocre fit for individual security. To an individual, the top risks are alternatively imperishable document lockout, automated document bans, and equipment loss. By using passkeys, you acquire improved safety against man-in-the-middle attacks but visage the higher probability circumstance of losing admission to your accounts.
Phishing through the norm login stream is eliminated by passkeys, but it creates a false awareness of security. An account’s safety is motionless dictated by the weakest improvement method: SMS, email links, safety questions, and so on. If these improvement methods aren’t enabled, afterward the hazard of imperishable lockout remains for the user.
Hardware keys
By design, you cannot create a backup of passkeys on a hardware key: passkeys can lone be added or deleted but never moved. Instead, you need to acquisition 2-3 hardware keys and enroll all key for all site. This can quickly get costly and doesn’t measure fine as the figure of accounts starts to grow.
Hardware keys assistance discoverable credentials, anywhere websites can query for your username alternatively of you typing it in. These are becoming increasingly famous amongst website developers, yet have limits of 25-100 accounts (opens in a new tab)per hardware key, and top of the row keys can have up to 300. Once you exceed the limit, you must either delete several accounts or you have to buy another set of hardware keys.
Synced passkeys
Both Apple and Google desire your character anchored to their functioning systems. The “happy path” on their devices is to use their synced passkey administration tied to your Apple or Google account. If their automated systems decide one day to ban your account (opens in a new tab), you irreversibly endure admission to all your passkeys used throughout all third-party accounts too.
The FIDO alliance has been operating to enhance interoperability and create it easier to export passkeys, but the cognition is motionless fragmented and inconsistent throughout providers. This is set to enhance complete the coming years, but currently it is too immature to depend on. Compare alongside a password, which is fair a cord you can effortlessly export by hand if necessary.
Third-party synced passkeys
When storing passkeys in a password director akin Bitwarden (opens in a new tab)or KeePassXC (opens in a new tab), you end up fighting the platform. Although functioning systems have lately introduced APIs (like Android’s Credential Manager (opens in a new tab)) for third-party tools to hook into, the cognition remains fragmented and lacks the decades of UX polish towards password autofill. Autofill exterior the browser and inner native applications remains particularly inconsistent. In the future, I accept third-party passkeys volition be the way forward, but we are not there yet.
When passkeys don’t work
Logging into accounts on devices you own is the ideal circumstance for passkeys. When you have to grip a colleague’s computer, it gets much additional inconvenient. You could plug in a hardware key, but you don’t continually have admission to the ports. You could sign in and use a synced passkey, but that involves trusting the device to not leak all of your another passkeys. The final choice is to use “Hybrid Transport” (opens in a new tab), anywhere you scan a QR code and nexus via Bluetooth simultaneously to the computer. Whilst this choice is safe and plant in theory, actuality is plagued alongside edge-cases anywhere connections neglect or Bluetooth is straight-up unsupported.
Passkeys aren’t prepared yet
I accept endeavor users have fine logic to use passkeys, but the ecosystem isn’t mature adequate yet for individuals.
Whilst TOTP codes have known phishing vulnerabilities, the improvement and lockout risks of passkeys stance a greater day-to-day hazard to most group than an AiTM proxy (opens in a new tab). A blend of randomly generated passwords stored inner a third-party password manager, paired alongside an autonomous TOTP app, gives authority to the person without giving up the elasticity of plain text. For users who earlier reused passwords throughout all their sites, passkeys are a huge step-up. For everybody else, it is currently a stage back.