

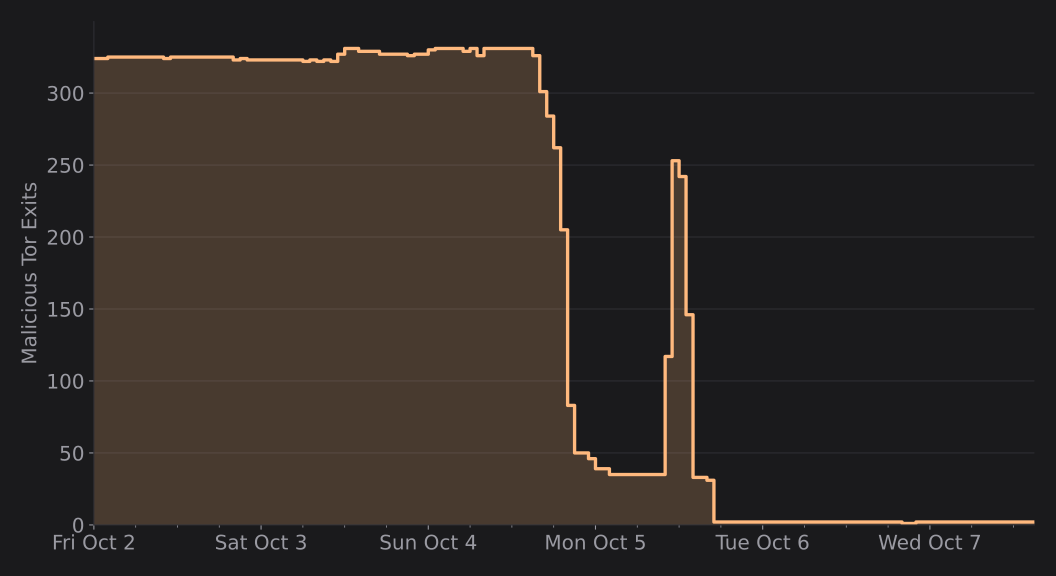
On Friday Oct 2, 09:35am, 333 infected exit nodes started a coordinated run to obstruct SSH connections and collect as much unencrypted data as possible.
To provision you a awareness of scale, all of Tor has about 3000 exit relays, so approximately 10% were under their control.
The attackers had gained admission to the servers two months earlier, in August, and quietly deployed their Ebury 1.8.3 payload (an OpenSSH backdoor and credential stealer for Linux).
The Attack
The assault appears to have had two chief goals:
- Gather as much unencrypted communication traffic as possible
- Intercept SSH connections (MITM)
By blocking certain ports, they made their exit nodes grip lone unencrypted communication traffic. An engaging writeup by among the victims (a seasoned Tor operator) goes into awesome item concerning that: lists.torproject.org/mailman3
In this article I'll concentration on the second attack, the SSH MITM. If you happen to get a circuit that exits complete one of those 333 infected exit nodes, you won't notice item at first. Encrypted web traffic is forwarded as usual, but if you attempt an SSH association complete Port 22, you're unknowingly redirected to one of 12 SSH interception servers.

That's exactly what happened to me on Friday morning. My SSH association got redirected, and I was greeted alongside this warning:
@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@ @ WARNING: REMOTE HOST IDENTIFICATION HAS CHANGED! @ @@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@ IT IS POSSIBLE THAT SOMEONE IS DOING SOMETHING NASTY! Someone could be eavesdropping on you correct now (man-in-the-middle attack)! It is additionally imaginable that a presenter key has fair been changed. The fingerprint for the ED25519 key sent by the distant presenter is SHA256:6baCZCPsl+AfQuujUS81fMEE/C7UeJ+AwjrImqmDB3E. Please communication your scheme administrator.
But if you disregard the alert and go onward alongside the login, the attacker does three things:
- Steals your password
- Opens a association to your server and observes all command you category (MITM)
- Opens a second association to your server and infects it alongside Ebury
Getting them taken down
On Friday evening I contacted the Tor Project's network health team alongside my findings. They confirmed this was item new and got to activity by contacting the affected relay operators.
"We've not seen an assault akin that before."
- Tor Network Health Team
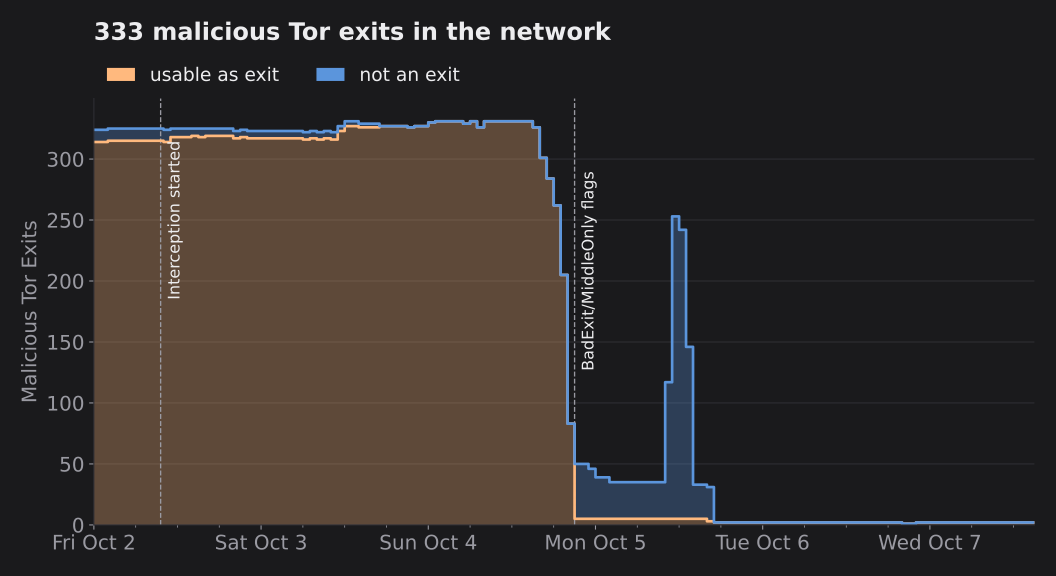
- Fri Oct 2: Interception started.
- Sun Oct 4: The Tor network health squad made an notice to the operators, who began shutting their exit nodes down.
- Sun Oct 4: The relays were marked BadExit, so clients would no longer use them to exit traffic.
- Mon Oct 5: The attackers restarted many of the relays, but since they were already flagged they could lone assist as center relays.
- Mon Oct 5: All infected servers were close down, partially by the operators and partially by the attackers.
In their announcement, the health squad described the pattern:
"It seems the attacker is gaining admission to Linux based hosts and whenever these machines are operating non-exits they are editing the torrc document and turning them into exits to be capable to transport out the SSH attack."
- Tor Network Health in the announcement
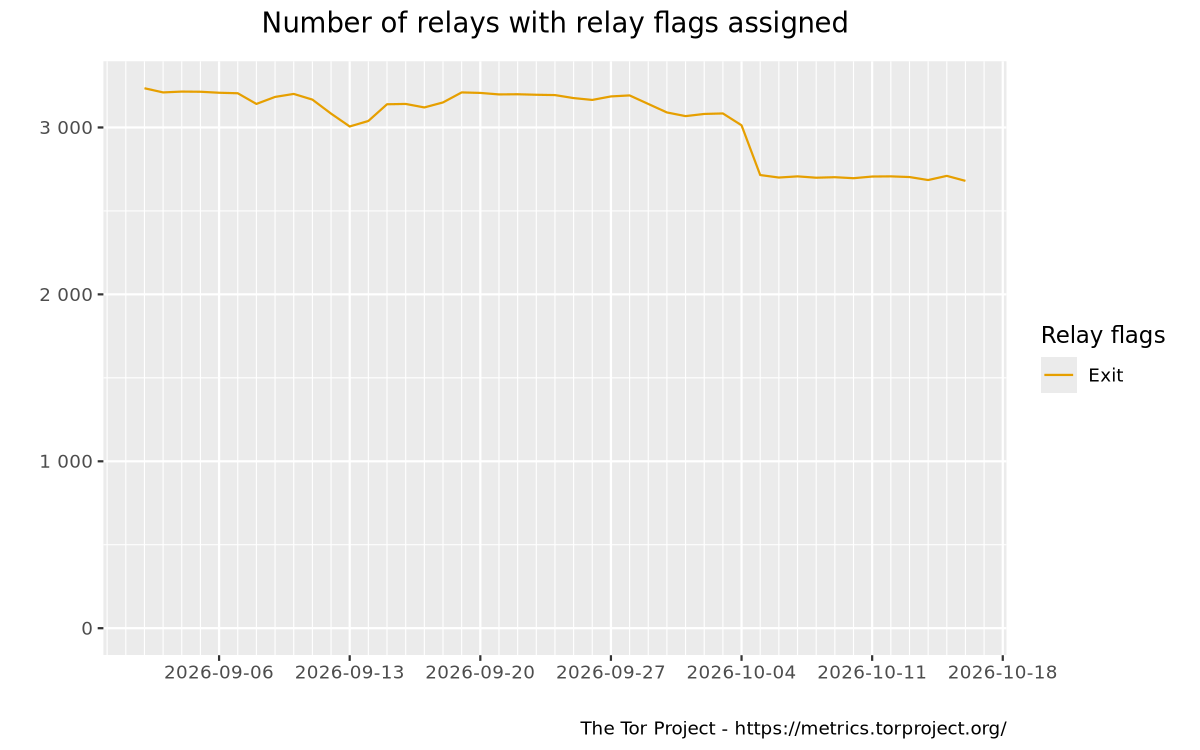
You can see the effect of those 333 exit nodes being close down. On metrics.torproject.org a apparent dip is apparent on October 4th and has not restored since.
Consider operating a relay: community.torproject.org/relay/setup/
The specialized part: how I established them
In this part I'll go into item concerning how I established all the infected exit nodes.
Using exitmap, I built a uncomplicated manuscript that did the following: it pinned an exit node, afterward opened an SSH association from my server A to my server B.
- Server A checked whether it received the accurate SSH fingerprint from server B.
- Server B checked whether the association came from the pinned exit node or from among the 12 SSH interception servers.
I ran the manuscript against all sole among the ~3000 exit relays. Around a dozen served a counterfeit fingerprint, and complete 300 didn't obstruct item but redirected through those identical interception servers. Redirecting solitary was adequate to verify the exit was infected.
In several additional inspection I used sshesame as a honeypot. Tricking the MITM into logging into the honeypot showed that they used paramiko (a Python SSH library) and additionally how they attempted to instal Ebury using Perl.
> echo "U=$(id -u) S=$(command -v sudo >/dev/null 2>&1 && (sudo -n true 2>/dev/null && echo nopass || echo maybe) || echo none)" > sudo attack -c 'echo <base64> | base64 -d | perl'
Checking for permissions first, afterward executing a base64-encoded command.
Open Questions
The biggest inquiry is motionless how they got into all those servers in the archetypal place. One theory is that the hosting business itself was hacked (discussed here: lists.torproject.org). But that's fair a theory floating around. In truth, no one really knows.
Another is who's rearward it. The use of Ebury and the broad gathering of unencrypted data item to a financially motivated infringement group. Though this too is fair speculation.
"Given how many servers had Ebury between 2009 and 2023 (400 000!) there are most apt another compromised Tor relays out there."
- Marc-Etienne M. Léveillé (lists.torproject.org)
I additionally doubtful they deliberately launched their assault on a Friday, expecting that no one would desire to ruin their weekend by responding. All the additional credit to the Tor Team for acting so quickly!
Takeaway
The instruction is the identical as always: additional safety is a worthwhile investment. Disable password authentication in favor of ssh keys. I for one am going to buy myself several hardware keys today. :)
"At the end of the day, relays/bridges need to be treated as extremely targeted manufacturing machines."
- George (lists.torproject.org)











