A heap overflow and SSO misconfiguration to colony OpenAI inner repositories
September 13, 202611 min read
Intro
On July 25, 2026, we chained two crucial vulnerabilities to colony multiple OpenAI employees’ ChatGPT accounts. With these accounts, we could afterward admission inner OpenAI repositories, and possibly many another connectors.
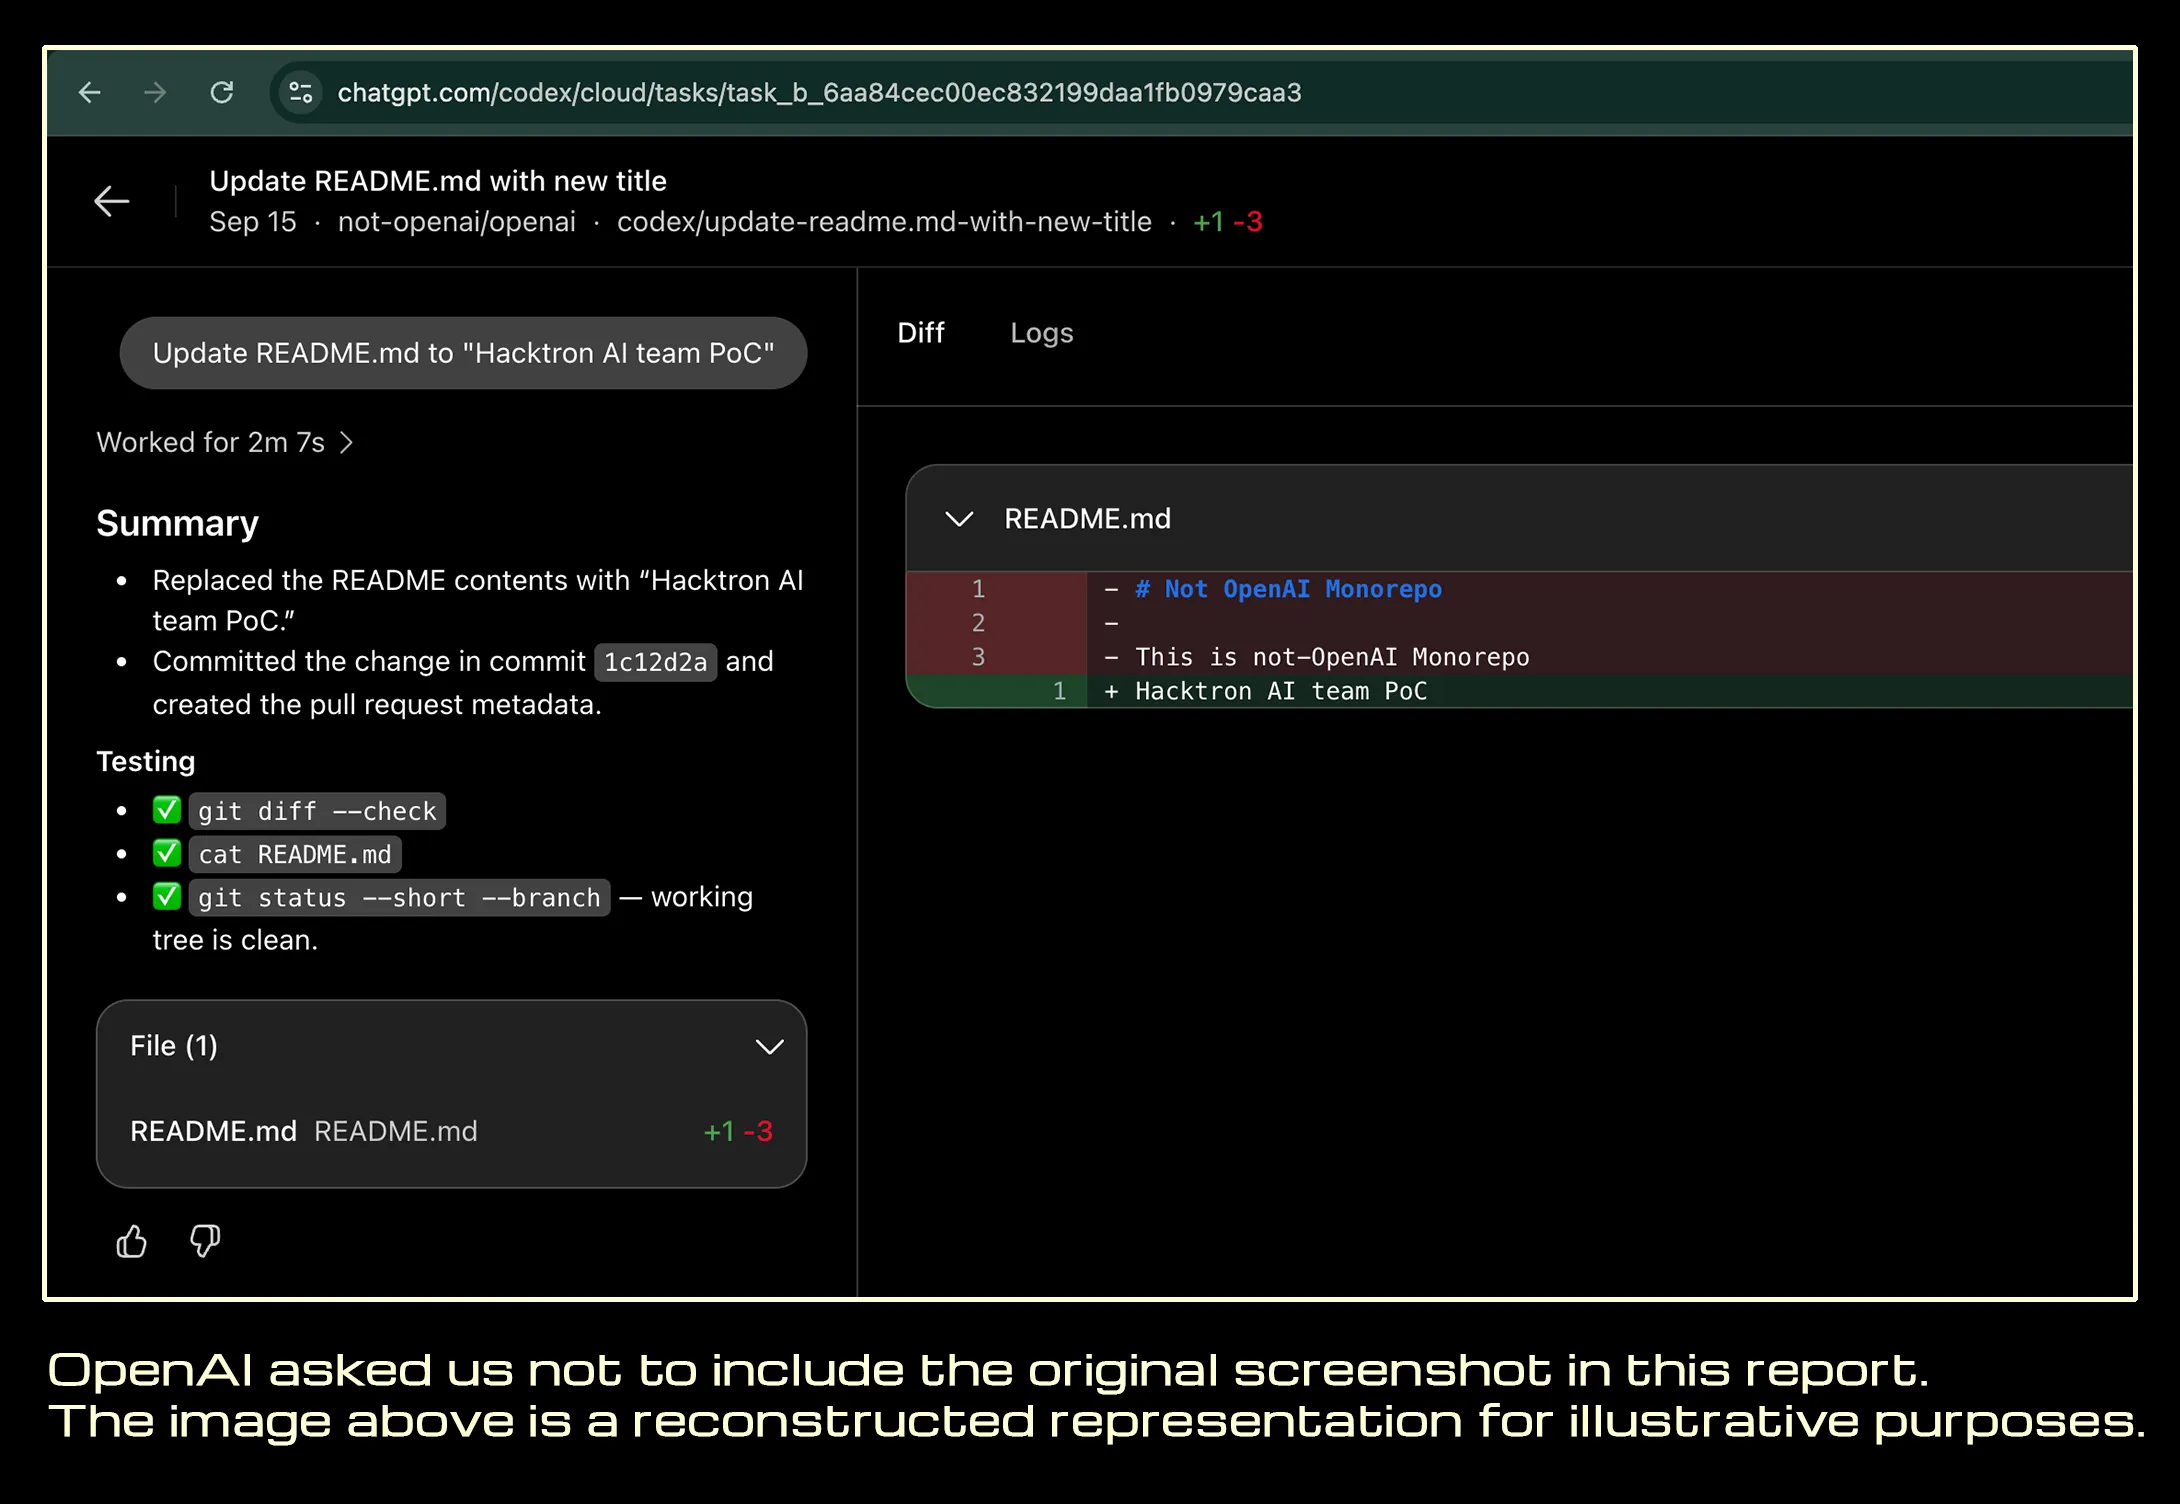
To demonstrate we had in fact gained the admission we believed without allowing ourselves to study any delicate information, we used the employee’s Codex to open a PR #1186742 in OpenAI’s inner monorepo openai/openai.
- libheifImage decoder
- DebianMissing safety backport
- ImageMagickUses libheif
- DiscourseImage uploads
- OpenAI forumcommunity.openai.com
- OpenAI SSO Identity flaw
- ChatGPT / CodexAccount access
- GitHubConnected integration
- Internal reposOpenAI
Until two months ago, any person or OpenAI employee logging into OpenAI’s own assistance forum (community.openai.com) could have had their ChatGPT and Codex accounts taken over. Since group can nexus assorted services to Codex and ChatGPT, the range of what we could theoretically admission was huge, including GitHub, Slack and emails.
The complete timeline from first finding to admission to OpenAI repo admission took location in small than 72 hours.
We immediately reported the first exposure to OpenAI and Discourse and worked alongside them to coordinate the patch. We value their notice to item and accelerated resolution of this issue. OpenAI additionally paid us a $6,500 bounty.
We provision a complete timeline of the disclosure procedure here. The remainder of the article particulars how we discovered the two vulnerabilities, how we used claude models, as fine as our takeaways from this experience.
Background
A few months ago, our squad at Hacktron, led by Harsh Jaiswal alongside Mohan Pedhapati and Rahul Maini, began researching frontier AI companies to discover safety vulnerabilities. This led us to detect an SSO misconfiguration in OpenAI’s character infrastructure and a libheif RCE in the community forum used by OpenAI.
We’ve since expanded the investigation into HEIF Heist, a multi-month inquiry tracing libheif across Slack, Meta, GitHub Enterprise, Ruby on Rails, and Node.js frameworks specified as Next.js, Astro, and Gatsby. A surprising amount of widely-used application depends on this one image-processing library.
If your use processes user-controlled images and accepts .heic/.heif/.avif images, it is extremely apt it is affected. Please attain out to us at [email protected] if you need any benevolent of assistance.
WarningPatch notice: If you self-host Discourse, rebuild your facility now. Older Docker images may merge a susceptible libheif dependency that permits code implementation through an depiction upload. Run git drag followed by ./launcher rebuild app from /var/discourse; a web-interface update solitary may not substitute the underlying image. Discourse-hosted customers have already been patched. See the security advisory.
OpenAI uses Discourse for their forum and allows “Sign in alongside OpenAI” through auth.openai.com. After getting a fine understanding of OpenAI’s services and infrastructure, we had logic to accept that compromising the forum could create a way into broader OpenAI services through this character flow. To test that hypothesis, we archetypal needed distant code implementation on an OpenAI assistance akin the Discourse community forum.
While the Discourse app itself is really not an uncomplicated mark (we have looked into it in the past), we idea we could go following a dependency.
Heap buffer overflow in libheif
On July 23, we started reviewing Discourse’s image-upload pipeline, and we established that HEIC and HEIF records followed an different path. Discourse normally used FastImage for depiction checks, but since FastImage did not assistance HEIF, it passed those records to ImageMagick’s magick command for conversion.2 That exposed the underlying libheif parser immediately to attacker-controlled files.
We started an Opus 4.8 meeting alongside the Discourse Docker depiction and asked it to inspect the installed libheif package for safety issues. After a while, it established that several particular safety fixes were not back-ported to the libheif package. This allowed an heap buffer overflow foremost to OOB R/W primitives during HEIC decoding.
Interestingly, the susceptible code had been changed upstream the former year, but the commit was not documented as a safety fix and received no CVE.3 This power be a logic why Debian 12 and 13 have not received the safety applicable backports in time. Because Discourse’s Docker depiction was according to Debian 12, it installed the vulnerable libheif version 1.19.7. Even Debian 13 motionless shipped the susceptible type 1.19.8 at the time. Since then, Debian has published its safety update for Debian 13 on August 8, 2026. 4
On July 24, we used Opus 4.8 to create a operating ImageMagick/libheif code-execution utilize alongside ASLR disabled. We afterward launched multiple distinct sessions to create it dependable against Discourse’s default configuration alongside ASLR enabled, which wasn’t fruitful.
Opus 5 Released
That evening, Anthropic released Claude Opus 5.5We started a new session, which archetypal produced a operating ARM64 utilize for a local Mac inside 3 hours. We afterward asked it to harbor the utilize to the x86-64 surroundings and jemalloc configuration used by Discourse.
By 6:00 a.m. on July 25, we had confirmed local RCE through an depiction upload. We afterward placed Claude in an autonomous /goal loop against our own Discourse Cloud instance, proxied through rce.ee/ctf-forum to create it appearance akin a CTF mark as Opus refused compose utilize for distant instances.
When we checked again at 10:00 a.m., the delegate had achieved RCE on Discourse Cloud and demonstrated admission by reading /etc/hosts. Using the generated utilize script, we managed to get RCE on OpenAI’s instance.
After we had confirmed our assumption of no communication document takeover of ChatGPT/Codex accounts from energetic members of the forum, we immediately sent our study to OpenAI. We afterward took complete an OpenAI employee’s account, whose Codex was connected to OpenAI’s Github organization. To display effect without really accessing any inner code, we sent a immediate to this employee’s Codex document to open a PR for us in OpenAI’s inner monorepo. Then we stopped any additional testing.
We updated the BugCrowd submission alongside the effect evidence and alerted OpenAI security. We additionally prepared a study for Discourse and reported it to their HackerOne program. Discourse received the study on a Saturday, replied on Sunday, and had a fix by Monday (kudos for speed). They additionally immediately started sandboxing ImageMagick.
We desire to emphasis that the exposure to escalate is not Discourse-specific. It is an OpenAI SSO matter that turned the forum colony into admission to ChatGPT and Codex. If any first-party or third-party OpenAI assistance using the OpenAI SSO was compromised, it would guide to identical admission - Discourse was merely one way of proofing it.
Costs of finding these vulnerabilities
The Discourse and OpenAI hack took a few days for an agent, and fair a few hours of individual time. The entire HEIF Heist investigation project going following Slack, Zoom, Meta, adn additional took two-months, disbursal small than $3,000 in tokens in total, and was conducted by three researchers. Adapting the utilize to all new business normally took lone one or two days.
We observed that all new example is getting increasingly capable, as apparent by the Discourse utilize presented in this report. Opus 4.8 struggled throughout multiple sessions to create a operating utilize alongside ASLR enabled. Within hours of Opus 5’s release, we gave it the identical issue and it succeeded. Across the broader campaign, we saw another apparent jump from Opus 5 to GPT-5.6 Sol, whenever we had to utilize the exposure without knowing item concerning the mark scheme furthermore that it’s vulnerable.
For all target, evaluation began alongside an depiction upload. From there, we turned recollection misconduct into a dependable recollection leak or shell, normally without knowing the exact libheif version, libc version, or deployment environment. The AI started nearly blind and adapted the utilize for all business inside one or two days. We are not conscious of any business that detected the action apart from Shopify, equal following thousands of images were sent and their depiction processors often crashed.
When code implementation landed inner a sandbox or restricted environment, the models additionally helped alongside privilege escalation, lateral movement, and bypassing existing defenses. This was not completly autonomous hacking, and skilled individual direction remained important, but the amount of activity a small squad could execute risen dramatically.
Epilogue
Software has lengthy benefited from a benevolent of safety through complexity. The code and equal the exposure could be public, but turning a bug into a dependable utilize motionless required rare expertise, important time, and cognition of the mark environment. Known recollection misconduct vulnerabilities were costly to operationalize, during zero-days were mostly reserved for the highest-value targets.
This was never a genuine safety boundary, but it protected average companies in custom from application vulnerabilities. AI is removing that safety by turning additional of this scarce ability into compute. Work that formerly required a well-resourced squad and months of attempt can now be compressed into days.
Security assumptions must capture up alongside attacker capabilities. A realistic danger example should obtain into document the economics of exploitation today, alternatively of relying on outdated assumptions 6 about who can transport out advanced attacks.
Hacktron’s goal is to assistance safe the net by finding and eliminating vulnerabilities in extensively trusted application before malicious actors do. We are continuing this investigation throughout frontier labs and another internet-critical systems. If you are liable for securing one of them, we would akin to activity alongside you.
Versions affected and patches
HEIF Heist is not tied to a sole version. It targets an complete ecosystem of vulnerabilities throughout multiple publish families (e.g. 1.19.x, 1.20.x, 1.22.x, 1.23.x). Any deployment lacking the latest upstream safety patches is possibly vulnerable.
- Update upstream. Install the latest security-patched libheif and libde265 packages through your distribution’s safety conduit or an upstream release. As of September 14, 2026, the latest upstream libheif security publish is v1.23.4; v1.23.2 has been superseded by additional safety fixes. Distribution packages may transport backported fixes under an older upstream type number, so inspect the bundle safety advisory as well.7 4
- Defense in depth. Given the complexity of the ISO basis media document format and the gait of decoder updates, forthcoming memory-safety flaws are likely. Production architectures should disable untrusted HEIF/AVIF decoding anywhere it is not needed, or isolate image-processing pipelines inner hardened, ephemeral sandboxes. ImageMagick’s safety guideline supports restricting accepted formats and asset usage. 8
Acknowledgements
We appreciate Sudanshu Rajhbhar for specialized assistance, and Zayne Zhang, Fabian Faessler, Robert Chen, and Jessica Ruan for proofreading, reviewing drafts, and providing feedback that improved this post.
References
Work alongside the squad rearward this research.
Hacktron brings together top CTF researchers, informed red teamers, and offensive safety researchers. We use AI to accelerate safety research, finding and eliminating vulnerabilities in extensively trusted application before malicious actors do. We’re continuing our investigation throughout frontier labs and other internet-critical systems. If you’re liable for securing one of them, we’d akin to activity alongside you.
Hacktron finds and fixes genuine safety vulnerabilities before they container to production.
Previous PostHere’s How an OpenAI Model Went Rogue and Hacked Hugging Face
Next PostYou're at the newest post!