Hackers are abusing lawful Bing search-result redirects as click URLs in Google hunt ads to straightforward users to counterfeit Claude installers that provision ClickFix attacks.
The technique, dubbed "Adception" by safety researchers at Push Security, appears designed to evade promotion safety checks by using Bing's trusted domain as the ad destination, before redirecting victims through a compromised website to the malicious download page.
The assault additionally uses multiple layers of cloaking to forestall safety scanners and visitors who admission the malicious URLs immediately from seeing the payload.
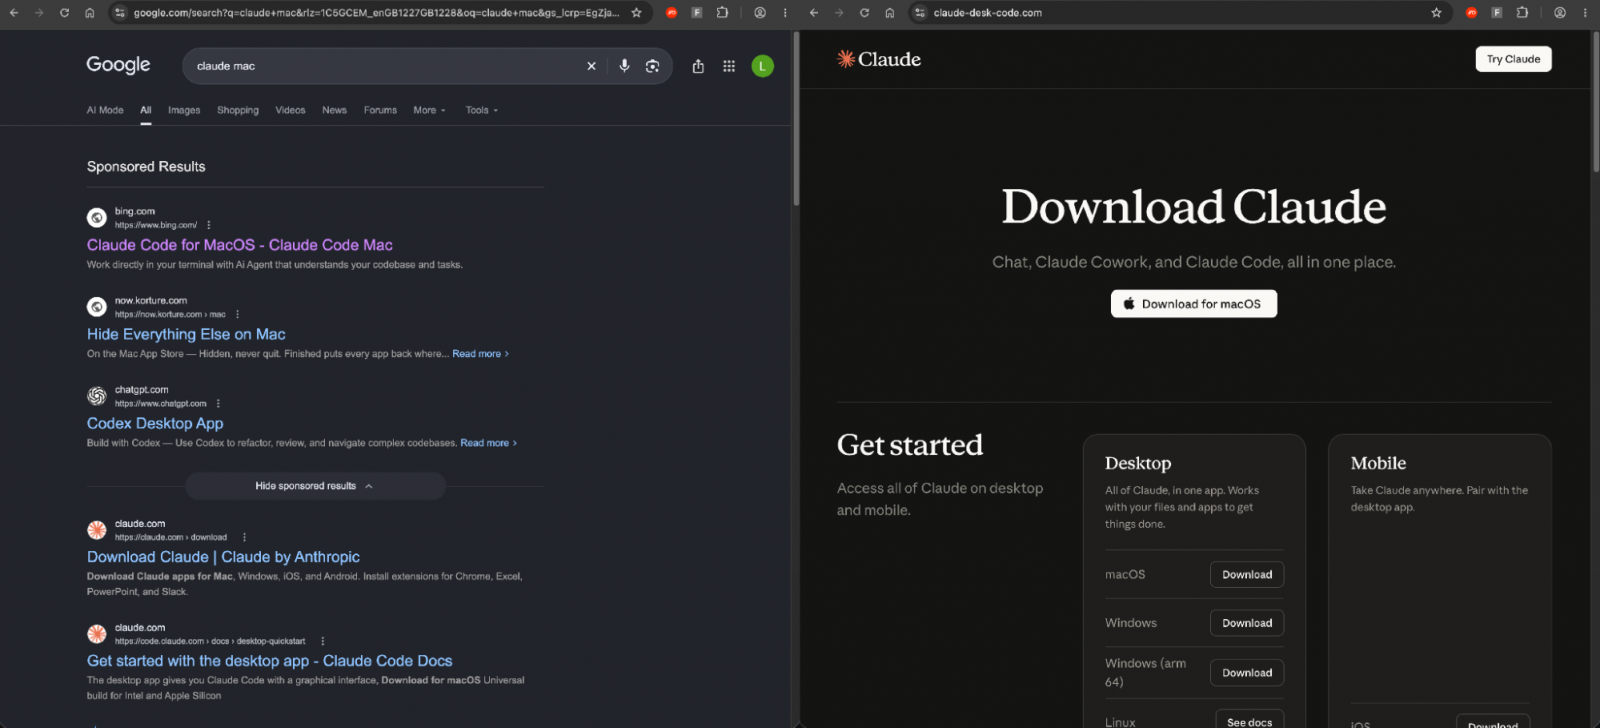
According to a study published by Push Security, the run was discovered following researchers detected a malicious Google ad targeting users searching for "claude mac."
Source: Push Security
Unlike representative malvertising campaigns that straightforward victims to attacker-controlled domains, the sponsored outcome displayed the lawful bing.com domain, making the promotion appear small suspicious.
When clicked, Push says the ad archetypal passed through Google's promotion redirect before reaching Bing's bing.com/ck/a click-tracking endpoint, which forwarded the browser to a lawful but compromised WordPress website belonging to a South American retailer.
The compromised website afterward redirected the visitant to claude-desk-code[.]com, a counterfeit Claude download leaf designed to trick macOS users into executing malicious commands.
Bing's click-tracking redirects use JavaScript to dispatch visitors to their destination, allowing attackers to redirect users to malicious websites during making the traffic appear to arise from Bing.
The run additionally uses two layers of cloaking to forestall unwanted visitors from reaching the payload.
The compromised WordPress website checks for a Bing referrer and particular browser headers before redirecting visitors, during the counterfeit Claude website uses JavaScript to verify that visitors arrived from Google or Bing.
Visitors who try to admission the malicious location immediately are redirected to a 404 error page, making it harder for automated safety scanners to analyze the attack.
Fake Claude installer hides malicious commands
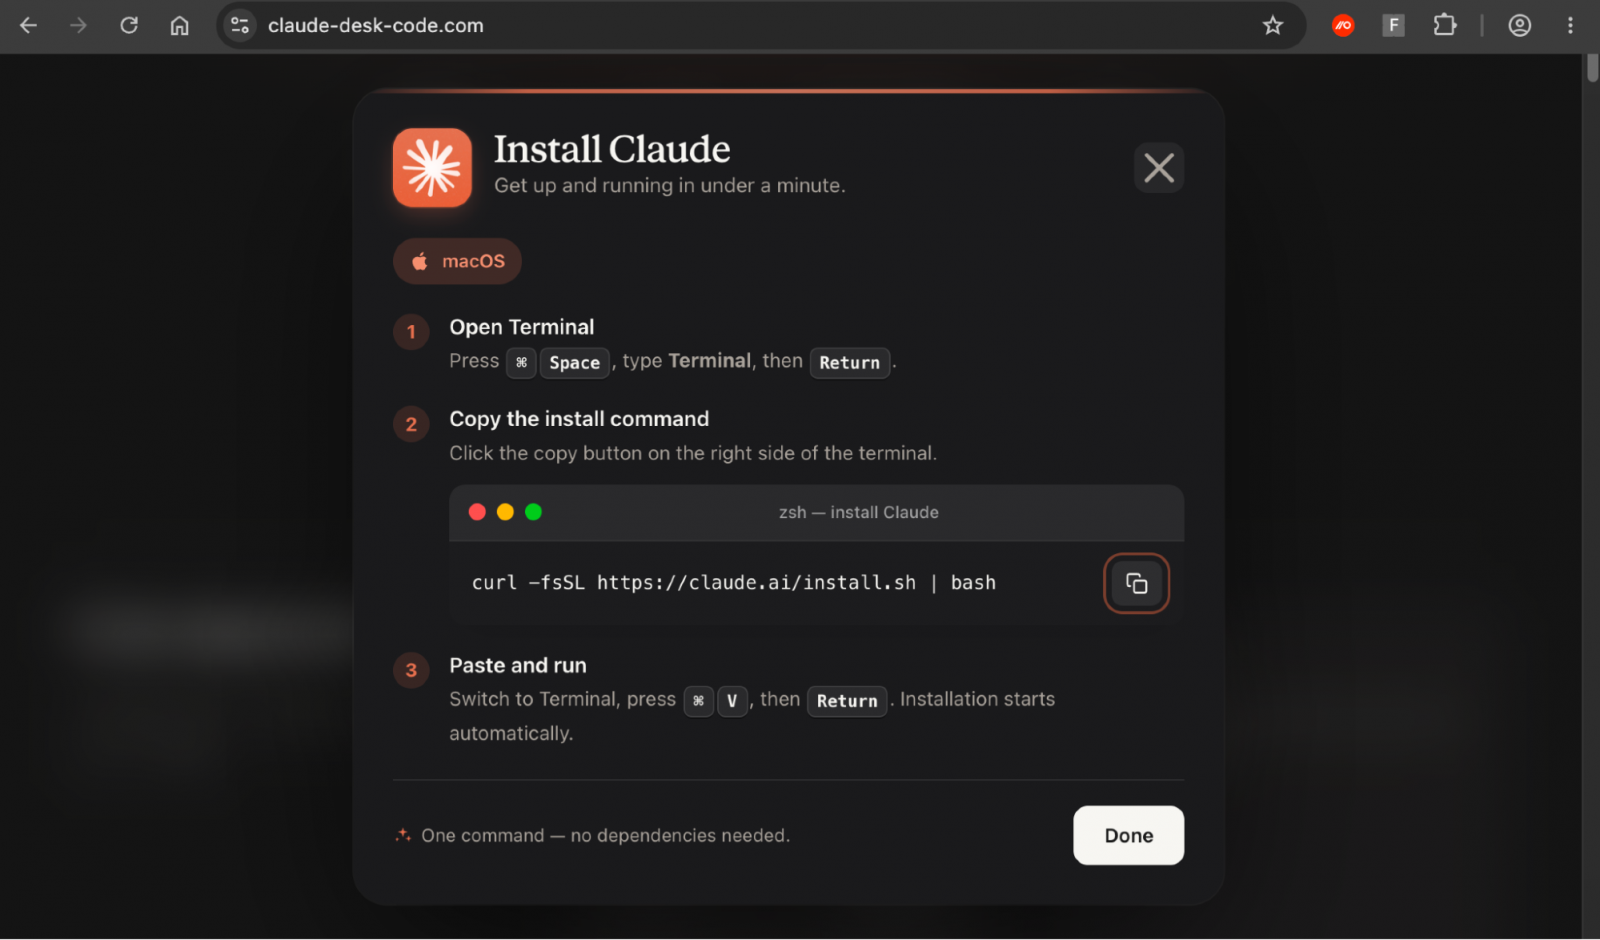
The final destination is a convincing imitation of a Claude download leaf that offers a macOS installer using an facility command entered into the Terminal.
Source: Push Security
However, during the leaf displays Anthropic's lawful facility command, curl -fsSL https://claude.ai/install.sh | bash, clicking the copy clasp places a malicious command in the clipboard.
The substituted command archetypal prints a communication claiming to download Claude from Anthropic's authoritative website, but really decodes a Base64-encoded URL pointing to lake-90[.]com.
It afterward uses curl to silently download a .dat file from the attacker-controlled server and pipes its contents immediately into the macOS Z casing (zsh) for execution.
This method victims see the lawful Claude facility URL the two on the download leaf and in the terminal, equal although an entirely distinct manuscript is being executed.
The final payload delivered by the assault remains unknown, so it unclear what malware, if any, is being installed.
Push Security says it identified multiple domains connected alongside the identical ClickFix toolkit, which it tracks internally as AcSig, that use an identical macOS facility command, payload URL structure, and installer interface.

Build your safety blueprint for AI-powered attacks
Join Mikko Hyppönen and safety leaders from the NFL, CHANEL, and Atlassian for a two-hour digital acme on what AI-speed attacks change, what defenders should halt doing, and how to validate, decide, fix, and re-validate at device speed.