
How Chrome is utilizing AI to amended vulnerability discovery, triage, and patching.
We’re surviving done a monolithic displacement successful the package information industry. Large Language Models (LLMs) are unlocking unprecedented capabilities for automated vulnerability discovery, scaling acold beyond the limits of quality information expertise, and requiring caller approaches for staying up of attackers.
This intends deploying AI models astatine standard to find and hole hundreds of information bugs, faster than ever, pinch the extremity of achieving greater resilience and broad remediation.
Here’s really we’re doing it.
The Life of A Bug
Some package bugs person information implications. While a purely functional bug mightiness consequence successful a frustrating UI freeze, a information bug (or vulnerability) tin beryllium utilized to build an exploit. Exploits let attackers to execute malicious actions connected a victim’s computer, specified arsenic reference backstage data, aliases controlling their instrumentality without their knowledge.
Once a information bug enters the codebase, its life rhythm proceeds arsenic follows:
- The bug is found.
- The bug is triaged.
- The bug is fixed.
- A caller update of Chrome pinch the bug hole is released.
- Chrome is restarted and the update is applied.
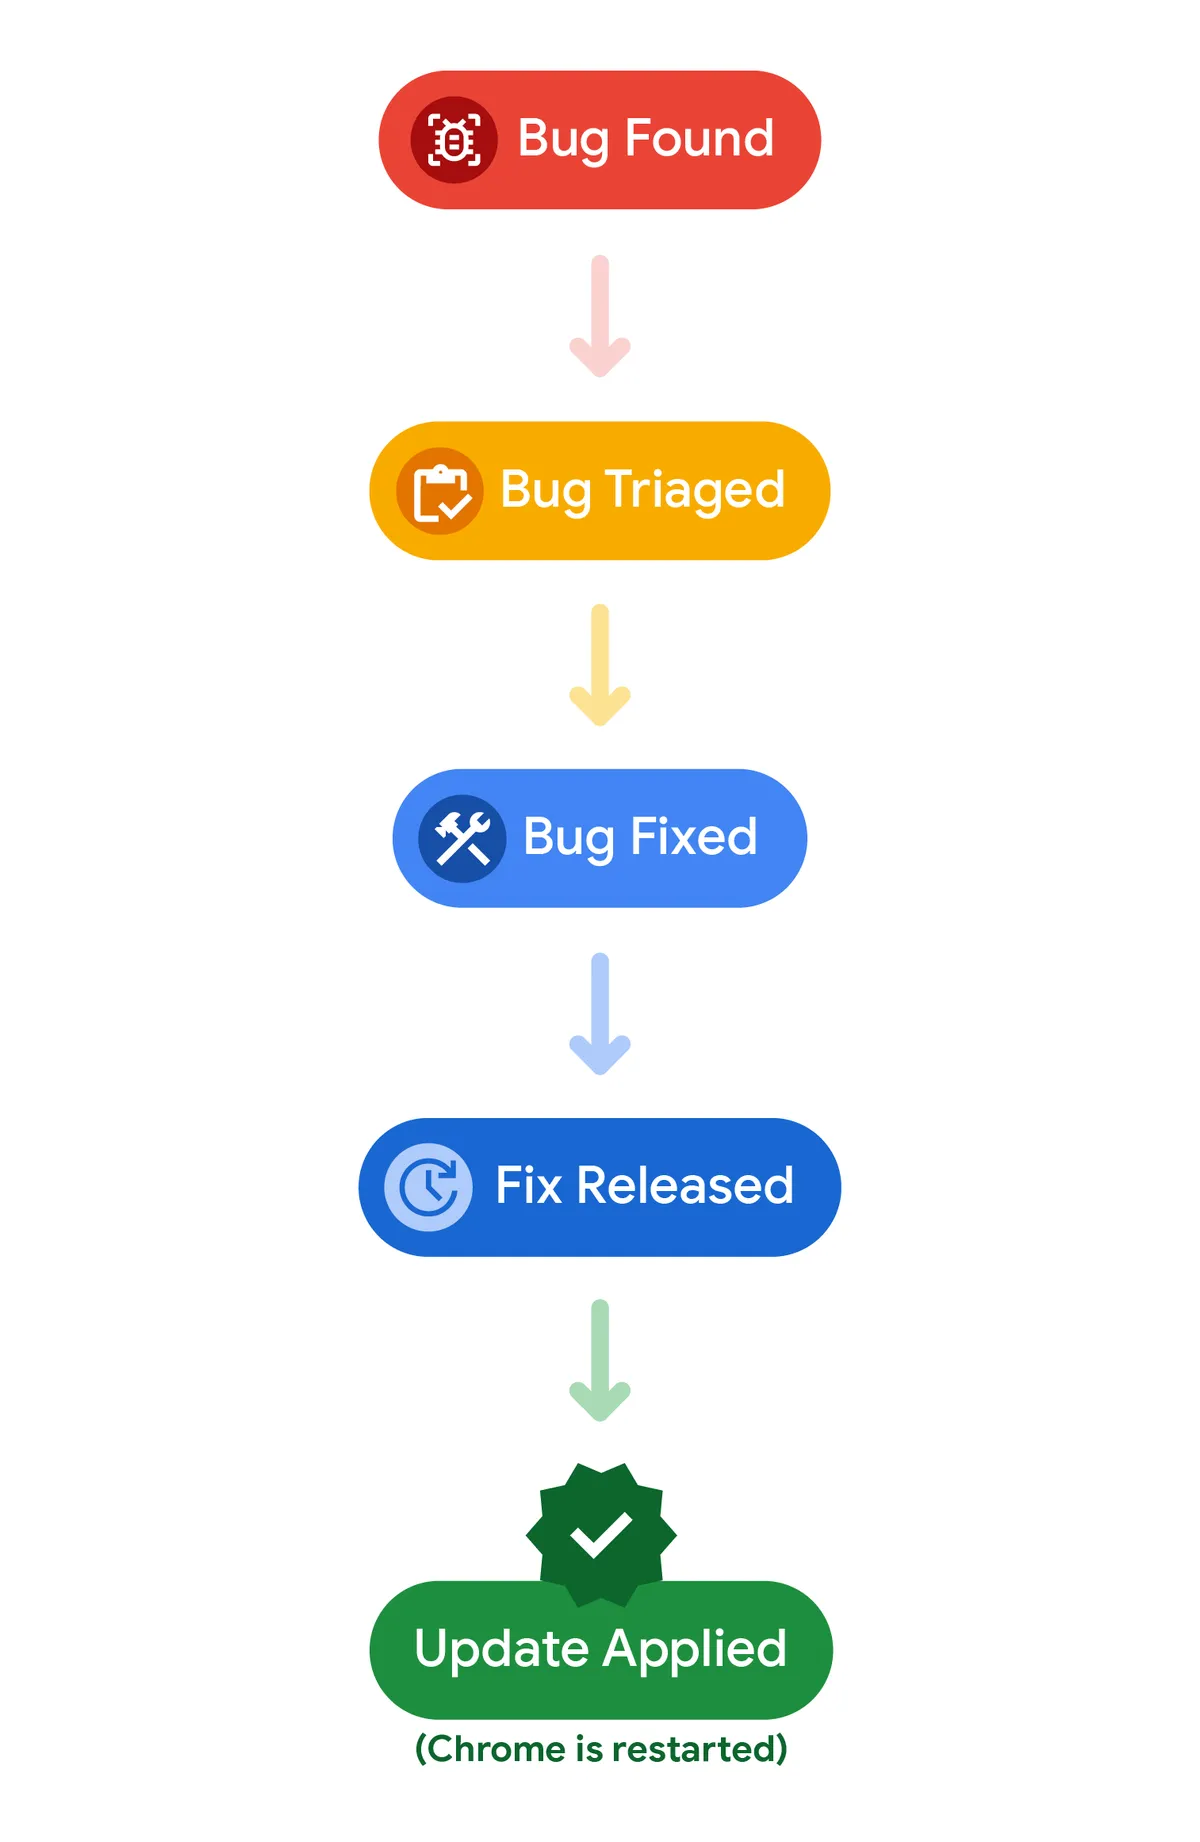
Our extremity is for each 1 of these steps to hap arsenic quickly arsenic possible.
Finding vulnerabilities
The Chrome Security squad has been utilizing LLMs for years. In 2023 we developed ways to use LLMs to summation information fuzzing sum and performance. In 2024, we worked pinch Project Zero connected Naptime, giving LLMs specialized devices for vulnerability research. And successful 2025, we collaborated pinch DeepMind and Project Zero connected Big Sleep, an AI vulnerability find supplier that successfully recovered bugs successful the V8 JavaScript motor and graphics stack.
In early 2026, we built an supplier harness that utilized Gemini to find vulnerabilities crossed the broader Chrome codebase pinch higher ratio and little mendacious positives. One of the bugs we recovered was a sandbox escape that would let a compromised renderer to instrumentality the browser into reference section files — a bug that softly survived successful our codebase for much than 13 years! For galore of us, this infinitesimal cemented the imaginable of AI-powered vulnerability detection.
From there, we improved connected our vulnerability uncovering supplier harness by:
- Adding support for exemplary interoperability to leverage the unsocial strengths of some open-weights and proprietary models.
- Building a knowledge guidelines of Chrome, including each antecedently identified CVEs and Chrome’s full Git history, to widen the LLMs reasoning capacity past its training data.
- Encouraging developers to adhd SECURITY.md files, which thief models amended understand spot boundaries and create an meticulous position of the threat model.
- Adding a “critic” supplier pinch a abstracted discourse to devour these SECURITY.md files.
- Introducing the expertise to tally vulnerability uncovering models complete the codebase aggregate times to relationship for exemplary non-determinism and exemplary improvements complete time.
We’ve built each of this pinch information successful mind, and person put successful spot guardrails to mitigate the consequence of AI behaving unexpectedly. Our AI analyzes root codification strictly astatine rest, operating connected locked-down machines that deficiency wide net access. We besides utilize a dedicated setup for these soul scans that intercepts each web requests, employing strict allowlists based connected the initiating exertion and destination, blocking immoderate suspicious exemplary activity. Furthermore, we ne'er tally models successful an unrestricted mode, and we strictly limit our subagents from modifying the section strategy aliases accessing files extracurricular of designated root codification directories.
AI-powered vulnerability discovery complements our existing information testing infrastructure. For example, fuzzing continues to beryllium particularly effective astatine uncovering bugs that originate from long-range interactions betwixt disparate parts of our codebase, aliases those requiring a operation of seemingly unrelated operations.
We besides want to proceed to reward outer researchers for their expertise and productivity successful uncovering the astir challenging and impactful vulnerabilities via the Chrome Vulnerability Reward Program (VRP). In early 2026, we saw a gradual summation successful each categories of bug reports, but by March, the displacement was apparent: we received much bug reports than we had successful the entirety of 2025. This led america to change our VRP to attraction researchers connected bug submissions that are additive to what we are uncovering internally, and easy ingestible by our recently automated processing pipelines.
Triaging vulnerabilities
As we observe much information vulnerabilities pinch AI-powered tools, we’ve simultaneously utilized AI to standard and automate validating, triaging, and fixing bugs. Historically, triaging a azygous information study took anyplace from 5 to 30 aliases much minutes, and relied chiefly connected quality expertise. We person been progressively shifting our triage process towards an automated attack that blends rule-based systems pinch AI to summation throughput and accuracy.
The automated triage process is surgery down into 4 cardinal phases:
- Filtering retired the noise. The strategy checks if an incoming bug is spam, ensures it meets intake criteria (e.g. is not a duplicate), and verifies that it intelligibly describes a Chrome information vulnerability.
- Reproducing bugs. Next, the strategy checks for a impervious of concept. Reproducible bugs are tested connected the circumstantial operating strategy and browser versions they affect. Based connected this, the strategy attaches further specifications specified arsenic stack traces to the bug to thief pass the fix.
- Enriching the study pinch metadata. The strategy adds basal metadata to the report, specified arsenic erstwhile the bug was first introduced and its severity rating. To thief this process scale, we’ve made our severity guidelines clearer and easier to use automatically. We proceed to let developers to modify the severity rating if they judge it is incorrect, and to adhd discourse to thief models logic astir information boundaries utilizing SECURITY.md files.
- Automatic assigning. The strategy automatically routes the rumor to the correct constituent and quality owner.
While it's difficult to measurement precisely, we estimate that this caller process is redeeming hundreds of hours of developer clip per month, allowing our squad to attraction connected different information priorities.
Fixing vulnerabilities
Across Google, developers stock the work of prioritizing information fixes pinch the information team, but scaling bug find requires an arsenic scalable bug fixing process.
To execute this, we trust connected multi-agent workflows throughout:
- After first build steps that bring successful discourse from a circumstantial issue, we tally a fixing agent that returns aggregate campaigner fixes.
- A critic agent past evaluates which would beryllium the champion fit, producing different applicable artifacts for developers to measure the fix.
- The fixing and professional agents activity successful a loop that mimics a emblematic codification reappraisal process to guarantee that codification is functional and compliant pinch Chromium and Google style guidelines, arsenic good arsenic different section codification conventions.
- Test-writing agents thief constitute tests for fixes. These agents tin guarantee that tests activity crossed the afloat array of Chrome supported platforms and configurations before a developer reviews the fix, redeeming up to weeks of developer time.
At this point, we person LLMs generating campaigner fixes for astir vulnerabilities, dramatically expanding the complaint of information fixes successful caller Chrome releases:
Number of information bugs fixed successful caller Chrome Stable merchandise milestones
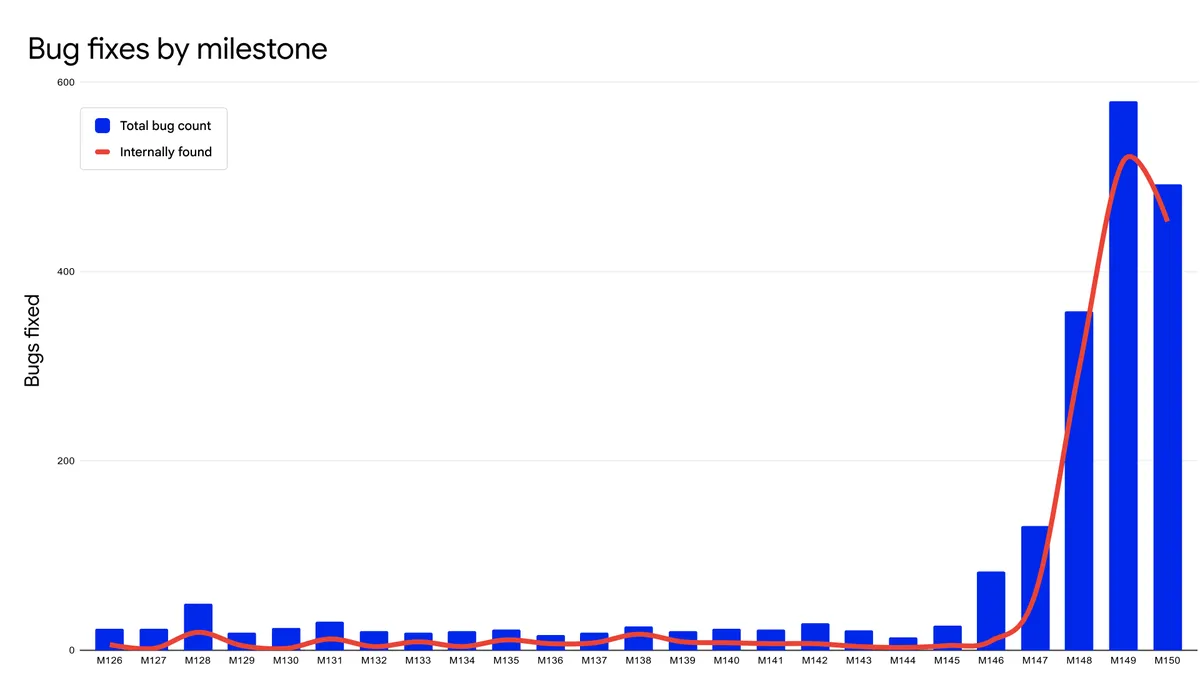
In the past 2 milestones, Chrome 149 and 150, we person fixed 1072 information bugs, surpassing the full number of information bugs fixed crossed the anterior 23 milestones combined.
We person collaborated intimately pinch Google DeepMind and Project Zero for years, including connected BigSleep and CodeMender. These devices are natively integrated into our continuous integration (CI) system, moving each 24 hours crossed each CLs to proactively observe information bugs. This integration has yielded important results: successful May alone, we blocked complete 20 vulnerabilities from reaching production, including a captious S1+ issue.
Releasing fixes
Once a hole has landed and is visible successful the nationalist unfastened root codebase, attackers tin commencement to reverse technologist and utilization the bug earlier the hole reaches users’ machines — so called "N-day" attacks. This is commonly referred to arsenic the “patch gap.” Since fixes committed to the main “tree” typically return weeks to scope the Chrome Stable transmission (what the immense mostly of our users run), minimizing this spot spread is simply a captious portion of our strategy.
Based connected their severity, information fixes are merged straight from the main “tree” into the progressive Chrome unchangeable merchandise branch, which is continuously monitored to forestall caller crashes aliases regressions. We are successful the process of transitioning to a two-week cadence for awesome Chrome milestones, pinch play information updates. However, successful the look of fast-moving, AI-powered attacks, our transportation cadence must accelerate moreover further. To meet this moment, we are piloting a displacement to 2 information releases per week.
Even pinch this pace, due nationalist disclosure remains paramount. Every information bug that reaches Chrome Stable, sloppy of whether it was discovered internally aliases reported externally, is documented and disclosed publically arsenic a modular champion practice. We are moving connected automating the procreation of merchandise notes and CVE descriptions from information bug fixes to destruct manual bottlenecks and shorten the model betwixt vulnerability find and nationalist disclosure.
Applying updates
In 2008, Chrome pioneered the conception of silent, inheritance package updates: caller binaries are automatically downloaded and staged connected disk pinch minimal personification intervention. At the adjacent restart of the browser, the update would beryllium applied and the personification would beryllium protected. However, compared to the 1–2 days it takes for triage, fix, trial and release, the clip spent waiting for the personification to restart Chrome tin beryllium a important contributor to N-day exploitation risk.
People person understandable reasons to hold restarting Chrome. A restart tin beryllium disruptive, requires scheduling in-between tasks, and is seldom the apical privilege astatine immoderate fixed moment. To destruct this friction, we are pioneering ways to displacement the load distant from the personification by:
- Investing successful "dynamic patching" that will destruct the request for a afloat browser restart successful astir cases. By leveraging Chrome’s multi-process architecture, move patching sequentially replaces inheritance kid processes (like the Renderer and GPU) pinch updated binaries connected the fly. Stay tuned to study much arsenic we investigation and create this feature.
- Exploring ways to guarantee a seamless convention reconstruct moreover successful analyzable cases, by redeeming much authorities locally.
- Finding opportune moments to restart automatically, erstwhile we tin guarantee a seamless convention restore. For example, successful Chrome 150, we rolled retired a alteration to return advantage of the unsocial exertion authorities connected macOS wherever applications typically proceed moving successful the inheritance moreover aft each windows are closed. Now, if Chrome detects a pending update while successful this windowless state, it automatically restarts.
Zero model auto-restart connected macOS
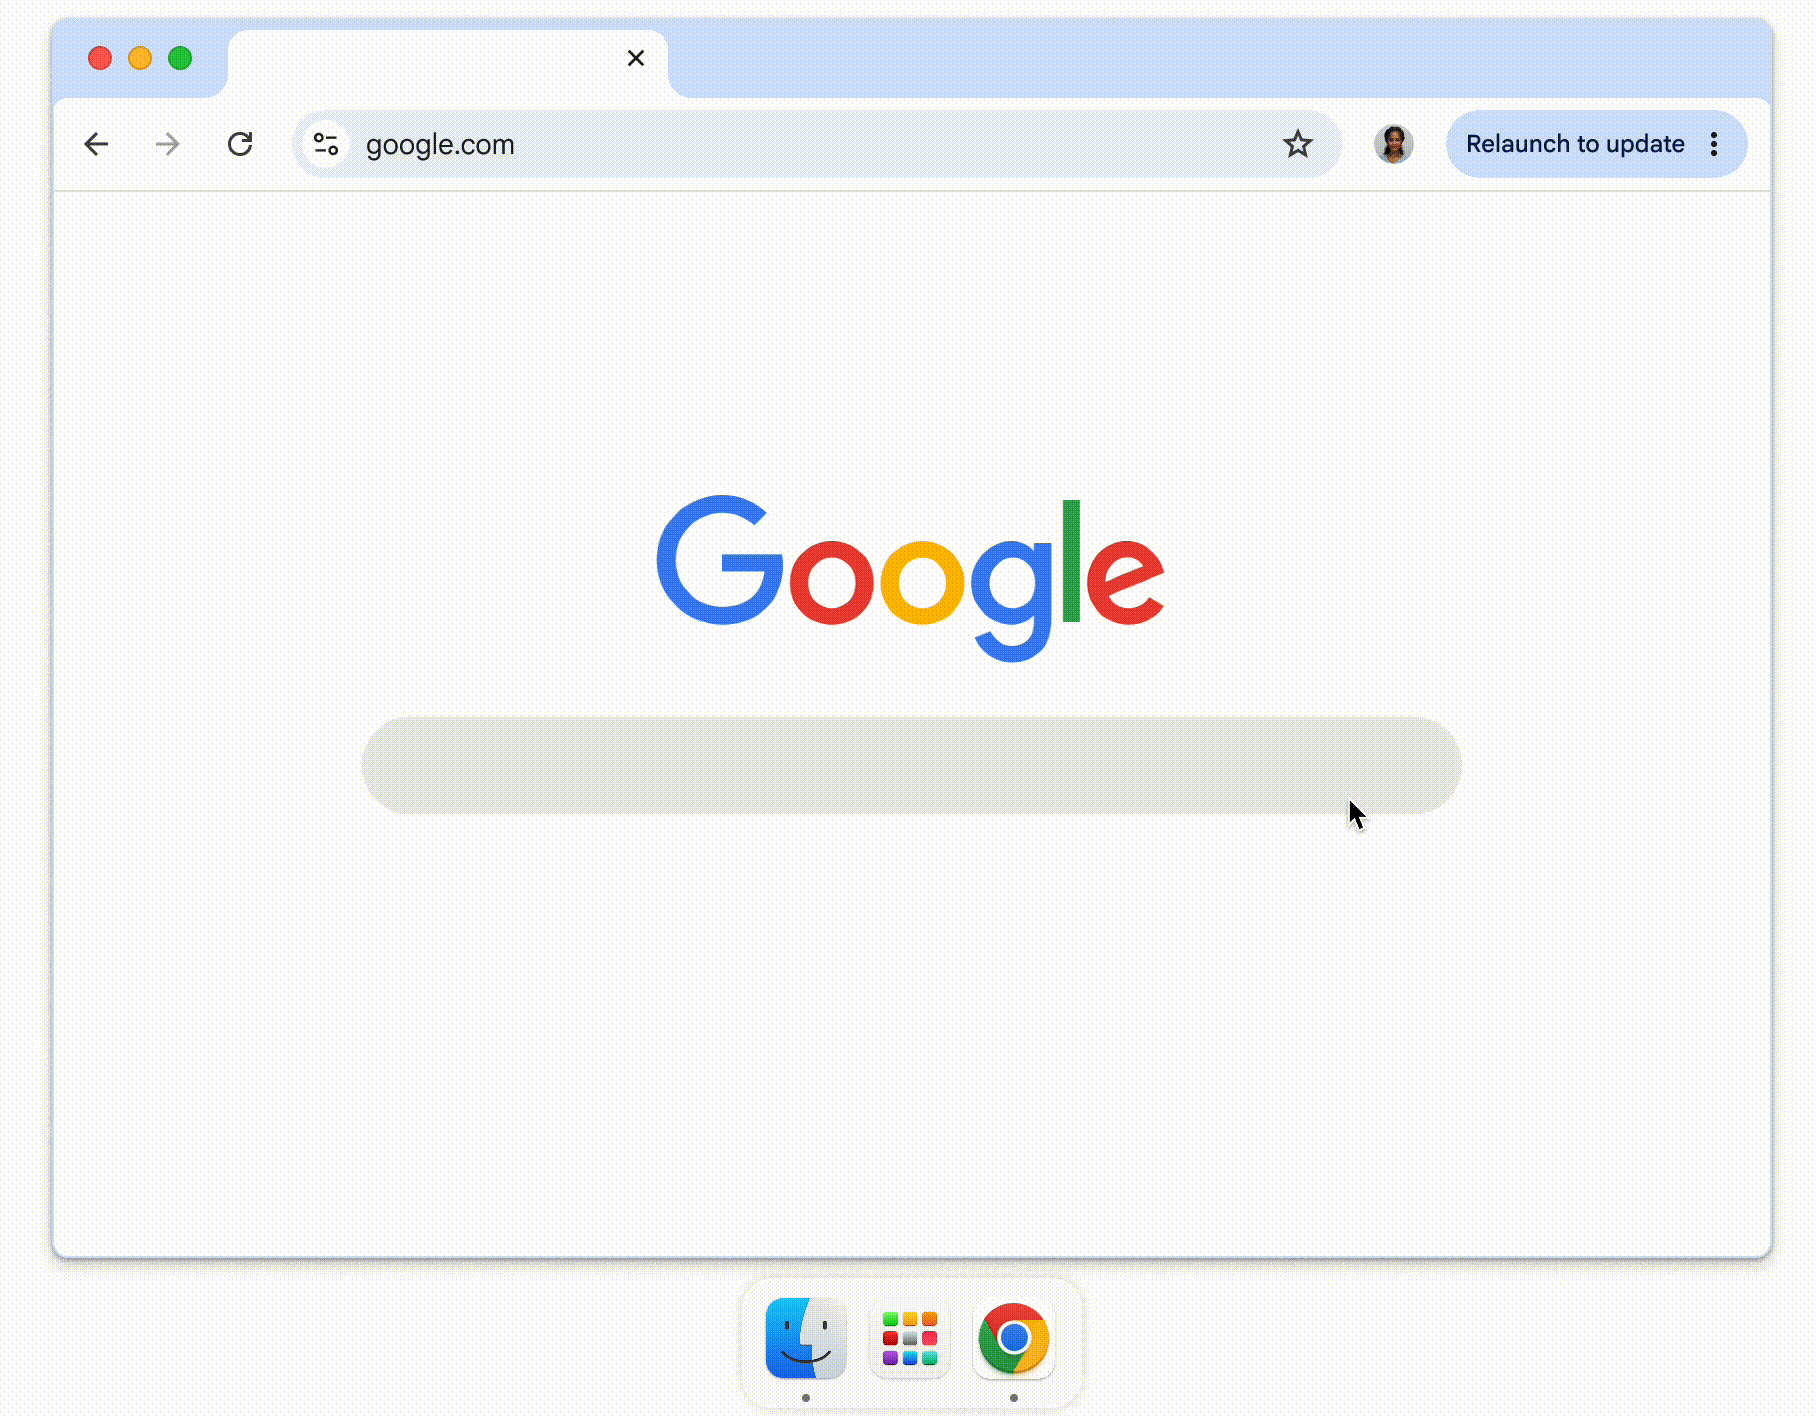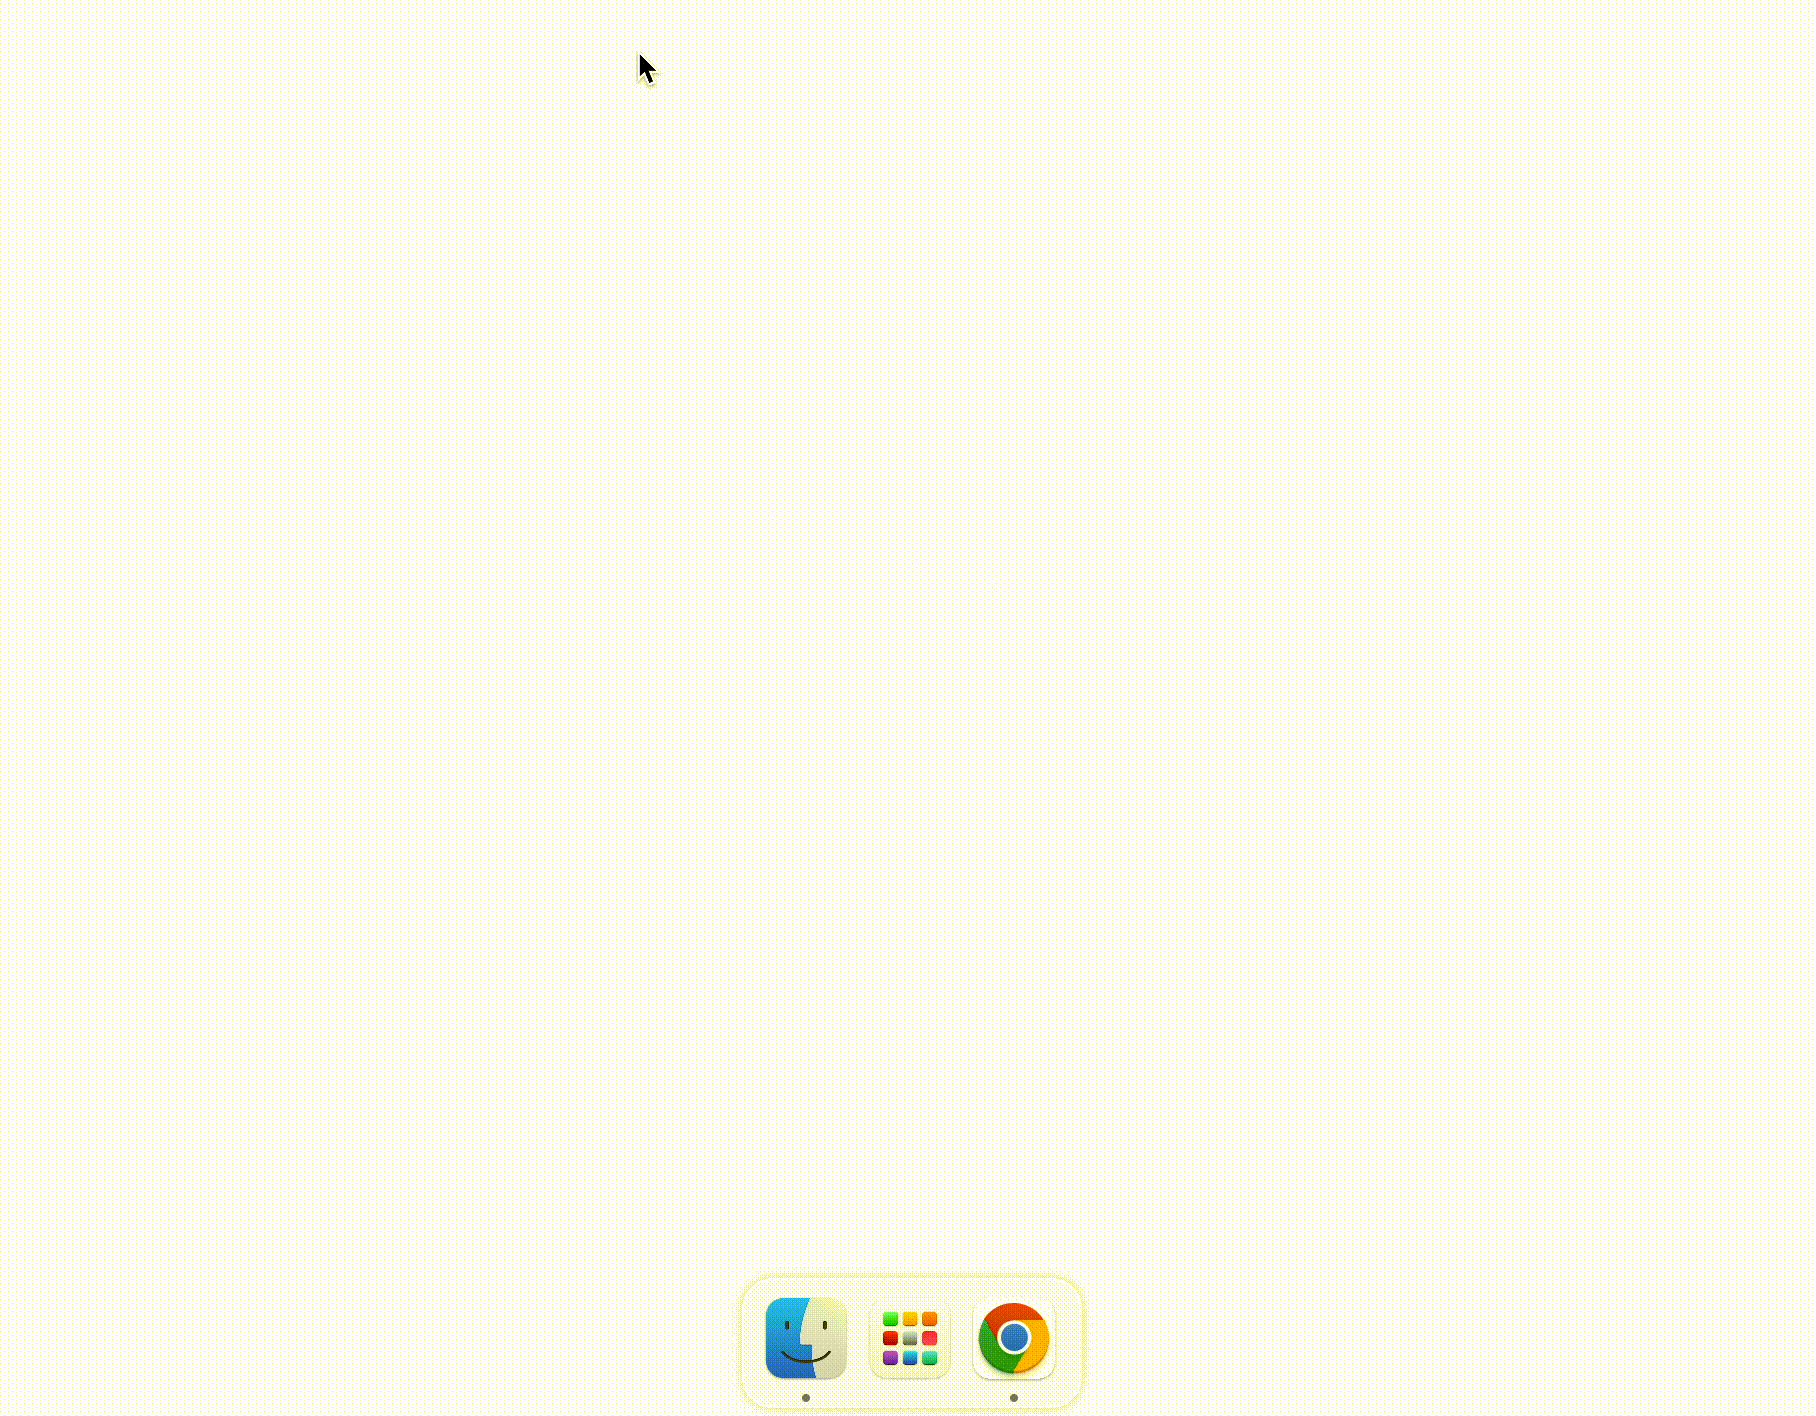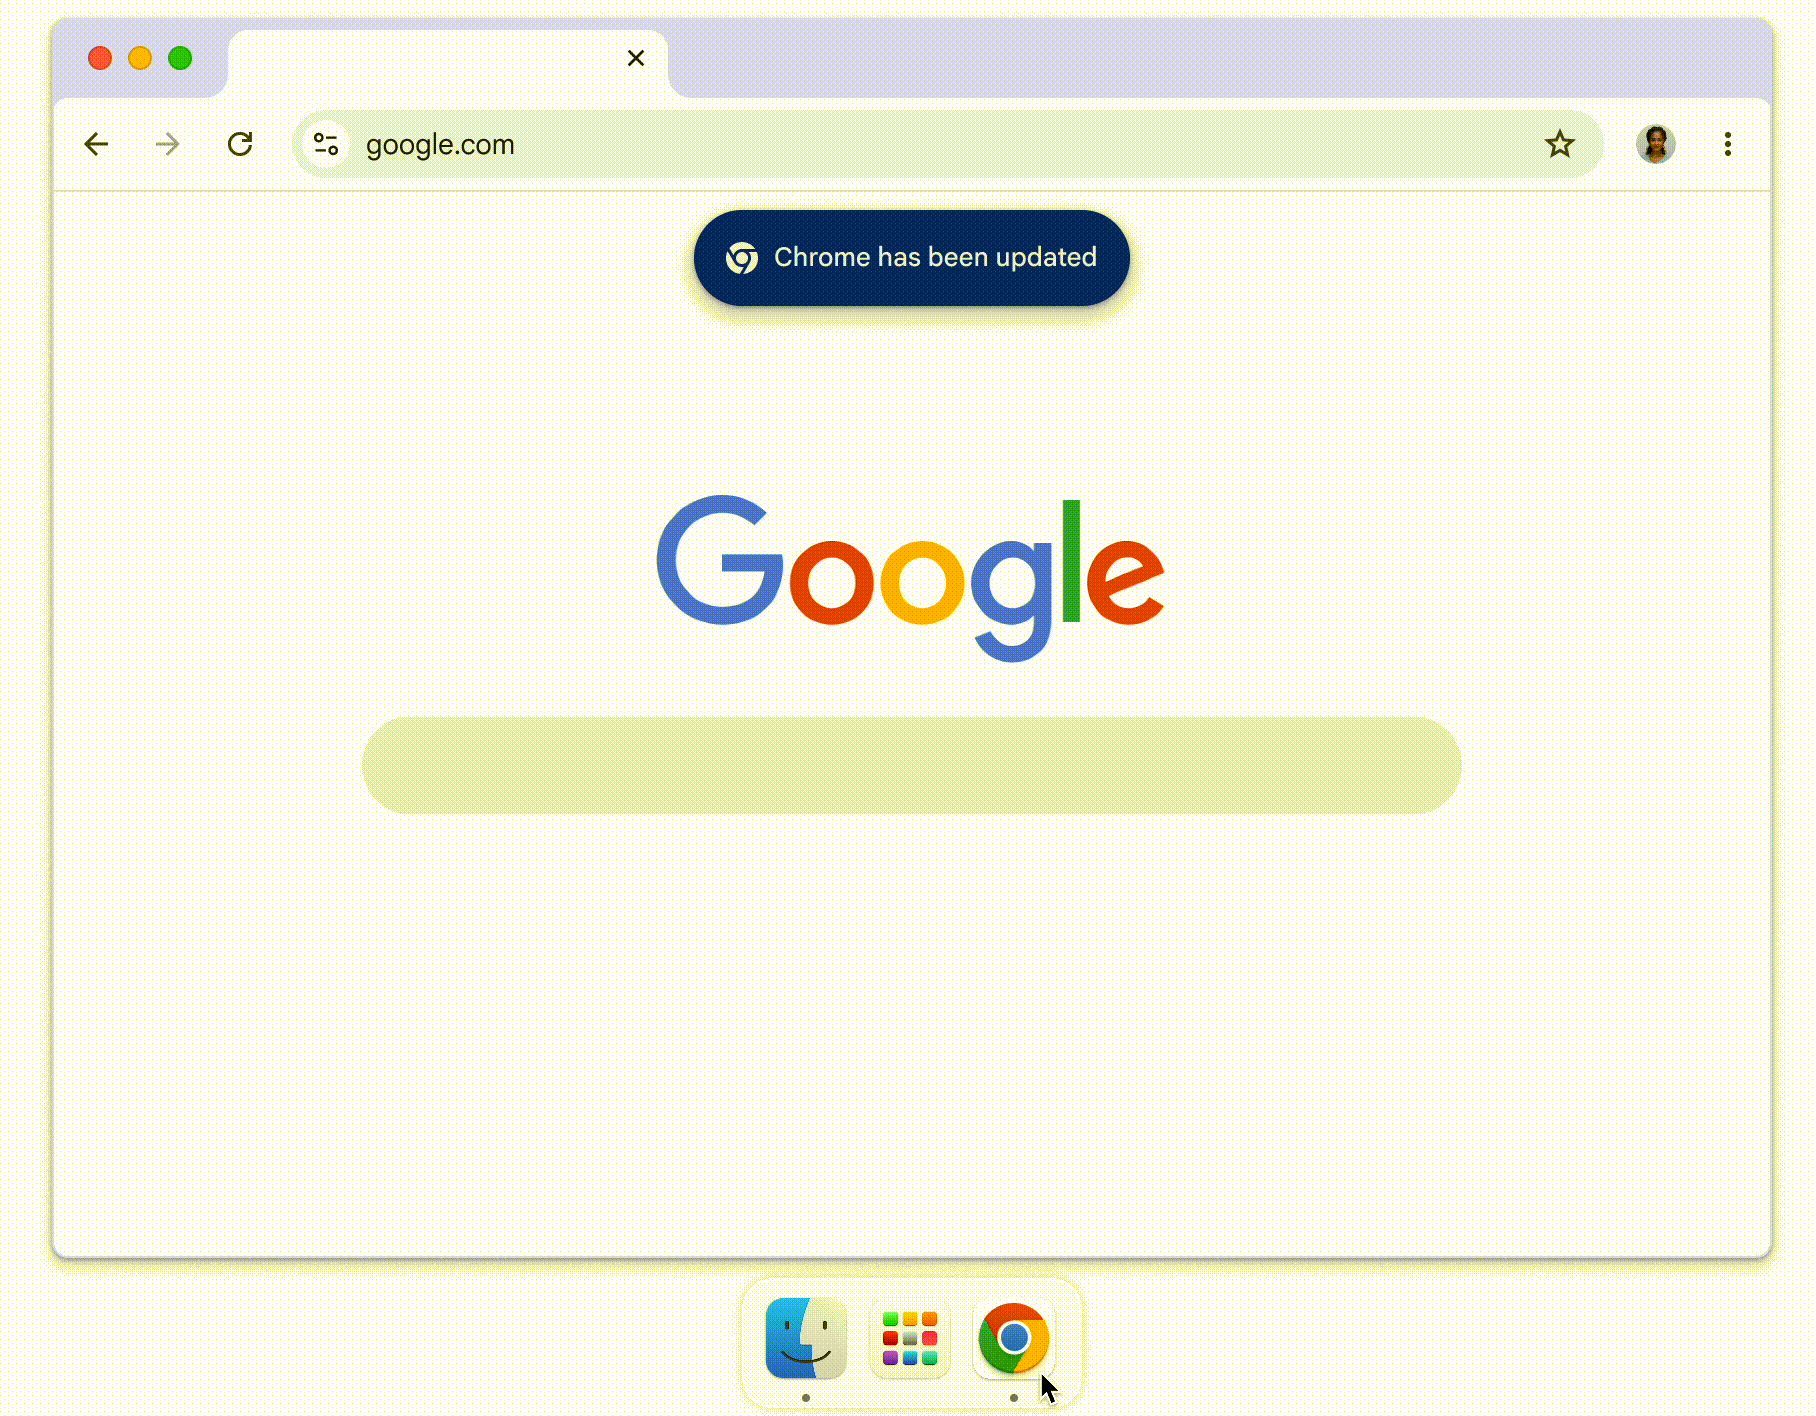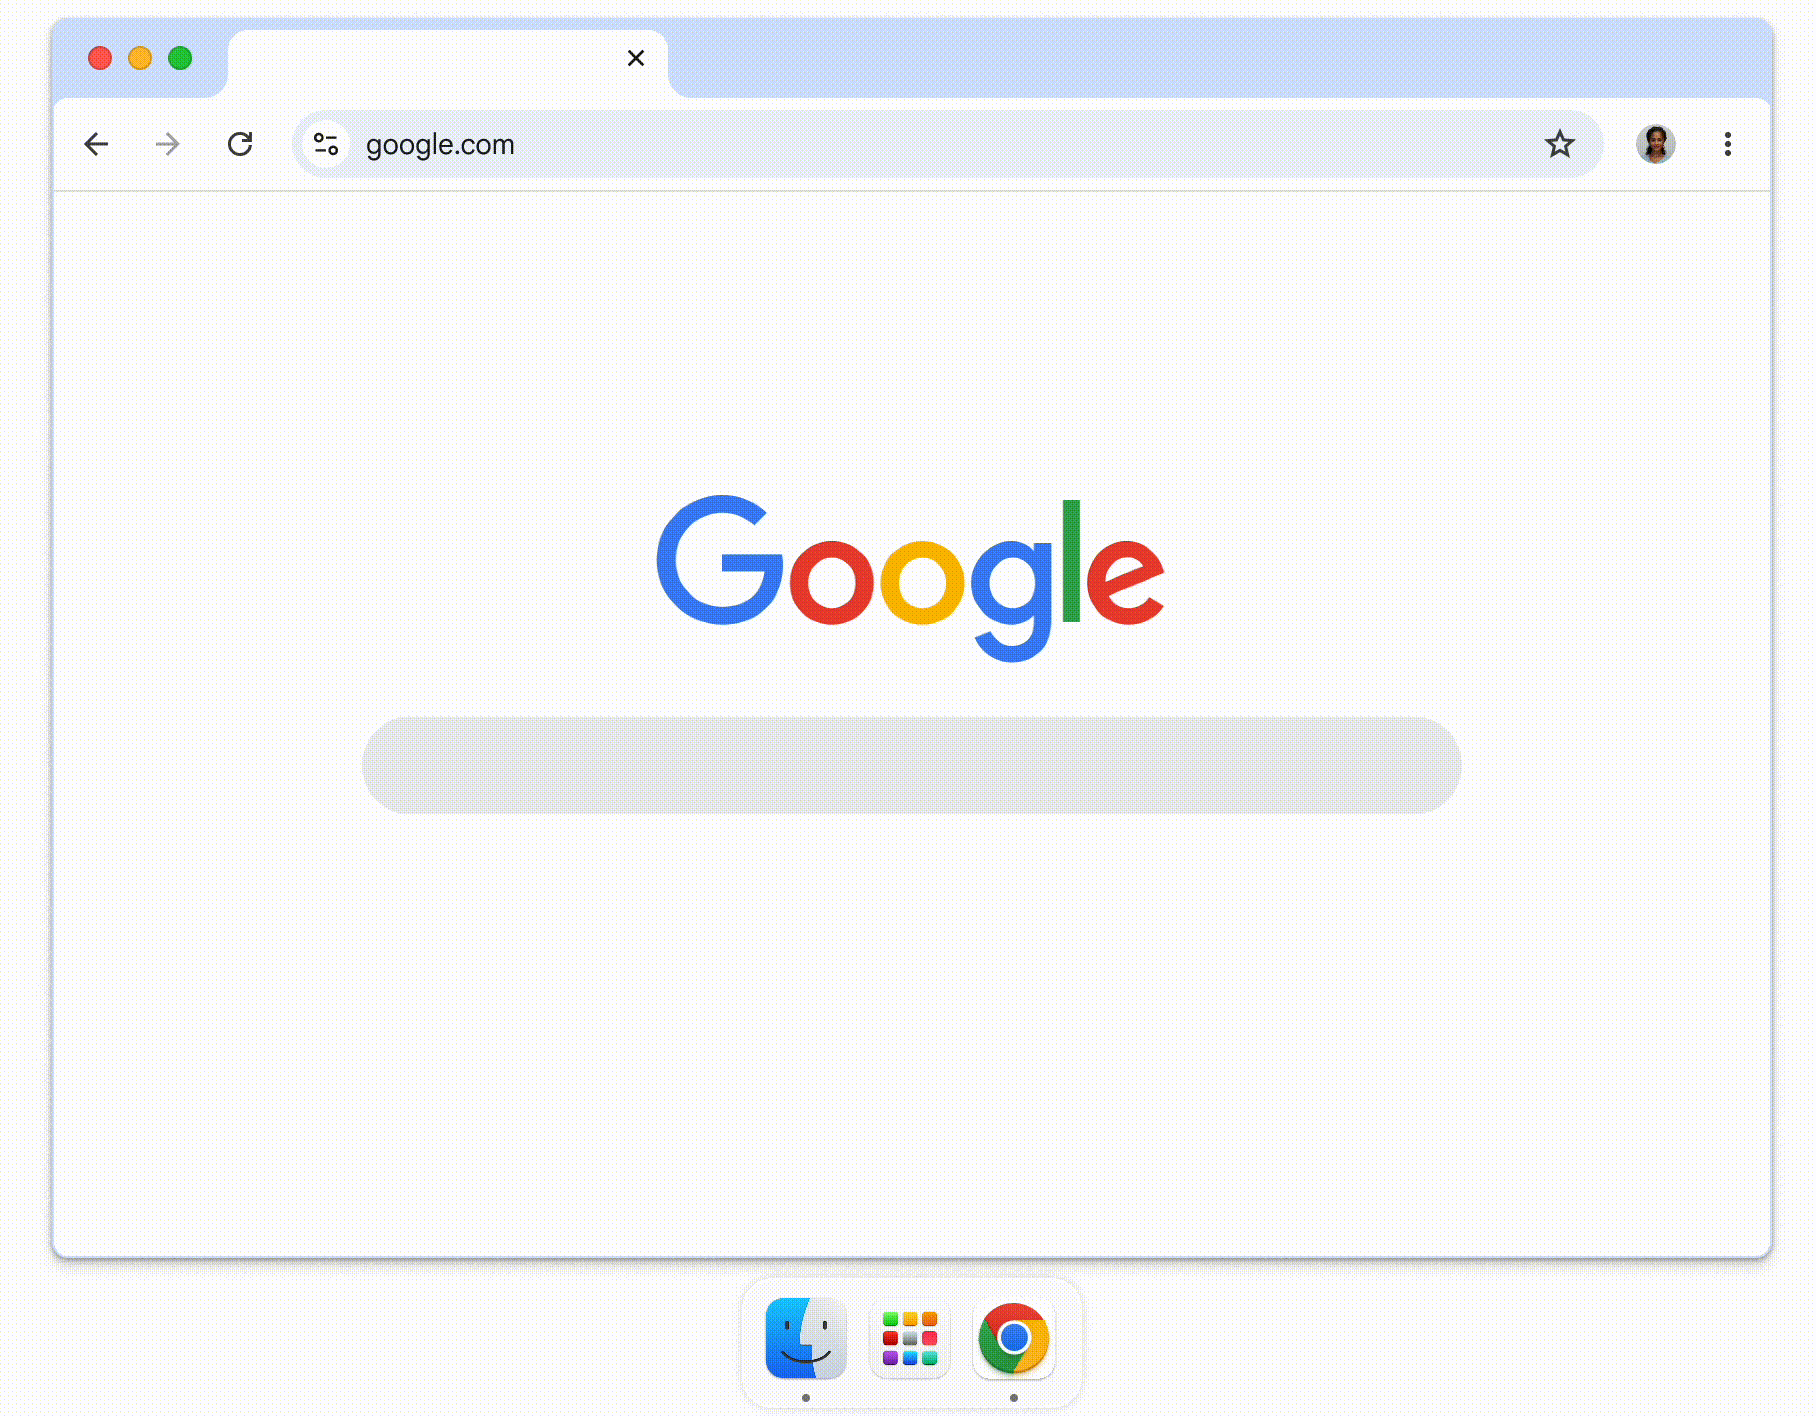
Our semipermanent imagination is simply a browser that is ever up-to-date – continuously and dynamically patched, and automatically restarted during opportune periods of minimal disruption. While we’re moving connected this, you tin support your Chrome up to day by clicking connected the update connection successful the apical correct corner.
For endeavor customers looking to support Chrome up to date, we urge that IT admins:
- Apply the RelaunchNotification argumentation which prompts users to restart Chrome to use a pending update, escalating from a gentle reminder to a forced restart complete a group timeframe.
- Utilize the Chrome Extended Stable Channel for highly delicate environments wherever package changes must beryllium vetted.
- Leverage the OS-agnostic dashboard provided by Chrome Enterprise Core aliases Premium to way fleet-wide browser versions and negociate updates astatine a much granular level.
Prevention is amended than cure
Beyond fixing individual information bugs, we’re besides investing successful the mitigation and elimination of full classes of information bugs, arsenic good arsenic successful preventing them from landing successful the first place. With AI coding advancements, we judge location are breathtaking opportunities to accelerate projects that would person antecedently taken years, aliases ne'er happened.
Memory information mitigations
Chrome is executing connected a two-layered representation information strategy: hardening our runtime situation to neutralize bequest C++ vulnerabilities, while shifting to memory-safe languages for semipermanent architectural resilience.
The immense mostly of the Chromium codebase remains successful C++, making contiguous toolchain and runtime mitigations our captious first statement of defense. We person agelong prioritized memory-safety engineering astatine scale, deploying hardened modular template libraries and pioneering technologies for illustration the MiraclePtr family to neutralize Use-After-Free (UAF) vulnerabilities. AI-powered vulnerability discovery only reaffirms the request for specified technology.
Our C++ protect roadmap is focused connected 3 pillars:
- MiraclePtr & MiracleObject Expansion. Having already driven a awesome simplification successful UAF bugs via MiraclePtr, we are expanding this paradigm to much libraries specified arsenic Skia, ANGLE, Dawn, C++ iterators and std:: containers. We are besides actively deploying MiracleObject pinch the purpose of neutralizing up to 90% of UAF vulnerabilities connected the GPU main thread, deliberately trading localized runtime capacity for temporal safety.
- Spanification. To systematically destruct Out-of-Bounds (OOB) spatial information errors, Chrome has undertaken a monolithic "spanification" effort, migrating bequest pointer-and-size constructs to compiler-enforced std::span types. Currently, 97% of first-party Chrome codification compiles cleanly pinch strict unsafe-buffer warnings. We are now pushing these requirements downstream, expanding spanification into foundational codebases for illustration Skia, ANGLE, and Dawn.
- Structural & Allocation Hardening. We are moving connected integrating checked math for calculations tied to representation allocations to artifact integer overflow avenues. Concurrently, Chrome is implementing an further level of heap partitioning to strictly segregate pointer-containing types from non-pointer types to make it harder to utilization UAF bugs.
While C++ information enhancements supply an contiguous shield, we judge that runtime mitigations will deed diminishing marginal returns wrong the adjacent fewer years. Runtime checks are inherently much costly than compile-time guarantees, and moreover a heavy mitigated C++ binary requires rigid, performance-throttling sandboxing to comply pinch the Rule of Two.
The semipermanent solution is shifting the codebase towards memory-safe languages for illustration Rust, focusing connected the pursuing halfway tenets:
- Rust flywheel. Developers cannot beryllium expected to wholly sorb the velocity clash of engineering successful a caller connection ecosystem. As such, we are building a centralized Rust SDK that exposes foundational Chromium APIs and tooling straight to Rust. Our purpose is to move Rust into a routine, frictionless engineering prime for caller components.
- Targeted “bug nest” eradication. Rust is being deployed strategically to switch codification segments that grounds precocious humanities bug density (such arsenic analyzable information parsers, image codecs, and font stacks).
- Enabling high-privilege modularization. By penning caller modular components successful Rust, Chrome tin safely execute analyzable features wrong high-privilege processes (like the browser process) without the capacity penalties of sandboxing, breaking the constraints of accepted C++ architecture.
In summation to Rust, we are besides exploring options for illustration implementing the browser’s top-level personification interface utilizing HTML, CSS, and TypeScript to further trim limitations connected accepted C++ frameworks.
Catching information bugs earlier they land
Bulk scanning of a codification guidelines cannot support gait pinch Chrome’s high-traffic improvement velocity. To relationship for this, we’re besides deploying AI-powered bug-finding capabilities to place and forestall bugs arsenic adjacent to codification submit-time arsenic possible. Part of Chrome’s continuous integration (CI) and perpetrate queue (CQ) pipeline, these protect models automatically scan diffs to forestall caller vulnerabilities by performing actions for illustration suggesting spanification fixes, flagging dangling pointers, and enforcing numeric safety.
Additionally, a awesome situation successful large-scale package engineering is the “latent information issue.” Code that is safe and robust successful isolation tin beryllium transformed into a captious vulnerability by an wholly unrelated, insignificant logic alteration elsewhere successful the tree. By utilizing continuous, LLM-powered semantic study wrong the CQ, Chrome tin intercept these compound risks earlier they onshore successful the tree, catching the subtle aliases analyzable interactions that accepted fixed study misses.
Securing the internet
Keeping the web safe involves much than conscionable securing Chrome. Google has been a long-standing protagonist of unfastened root projects and communities to guarantee amended information outcomes for each users. Most recently, Google joined others successful donating $12.5M to the Alpha-Omega project successful support of enabling maintainers to person entree to the devices and support they will request successful bid to respond quickly to vulnerability reports. Google was besides a founding personnel of the Akrites project, which intends to little the load connected upstream maintainers by providing a centralized clearinghouse for vulnerability reports and a information incident consequence team.
On the Chrome team, we consciousness this work acutely — the Chromium Project is the largest unfastened root task connected the planet. To put the sheer standard of this situation into perspective, Chrome has much than 2,300 third-party limitations crossed Chromium and outer projects for illustration the V8 JavaScript engine, the BoringSSL cryptography library, and foundational graphics components for illustration Skia, ANGLE, and Dawn. About 1,700 of those are shipped to users successful immoderate capacity, woven into a wide spectrum of products from Android devices to separator computing platforms and monolithic unreality endeavor stacks.
To support these limitations patched, we trust connected automated vulnerability scanning pipelines. These pipelines ingest information from Google's soul feeds arsenic good arsenic respective outer monitoring feeds, including the U.S. government's National Vulnerability Database (NVD) and the open-source focused Open Source Vulnerabilities (OSV) database.
Now much than ever, relying connected reactive monitoring unsocial tin time off a vulnerable consequence gap. Since the champion measurement to enactment connected apical of vulnerabilities and their patches is to support third-party limitations fresh, this year, we are starting to move each Chrome third-party limitations onto automated update pipelines that proactively rotation them to their latest upstream versions. Automation ever requires guardrails, truthful we will besides beryllium utilizing information signals from projects specified arsenic Google’s Open Source Security Intelligence Platform (GOSSIP) to guarantee that we are accounting for different risks successful the third-party unfastened root package ecosystem.
Moving forward
While this melodramatic alteration successful package information brought astir by LLMs mightiness beryllium startling, an summation successful bugs recovered and fixed is not a motion of failure. Every bug recovered and fixed is 1 little foothold for an attacker. But discovering and fixing a bug is only half the conflict — we must besides vessel the hole and use the update for users faster than adversaries tin utilization the bug, and put successful projects that mitigate aliases destruct classes of bugs done accelerated merchandise cadences, move patching, and opportune restarts, we are driving toward a browser that is continuously protected without disrupting the user.
The AI era has undeniably intensified the package information threat landscape, but by combining accelerated deployment mechanisms pinch heavy structural defenses, we are ensuring the advantage remains firmly pinch defenders. With this, Chrome and the broader web go safer pinch each update.








 English (US) ·
 Indonesian (ID) ·


