On the night of October 11 to 12, 2026, fridges and freezers in hundreds of French supermarkets started to heated up. Cyber attackers had pushed the refrigeration systems into defrost mode, which heats the cooling parts to melt ice. Some units reached 50°C (122°F), several equipment started to capture fire, according to the Paris prosecutor, and stores threw distant their caller and icy food. The reports pointed to one creator of refrigeration controllers, Danfoss (a Danish manufacturing company).
We went through IPinfo's weekly Internet scans to analyze these systems before the attack. In this blog article we’ll examine several of the findings. Here’s the TL;DR:
- France had additional exposed fridge dashboards than the remainder of the earth combined: 1,331, against 1,197 in the another 72 countries and territories put together.
- 85% ran application alongside known safety flaws. That includes 527 older controllers Danfoss no longer supports. Only 195 had all known fix.
- Most had been exposed for at smallest six months. 1,019 of the French dashboards were at the identical location on March 30, and the portion completely updated rosy lone from 14% to 24% in that period period.
- France didn't place worse than another countries. The flawed portion elsewhere was nearly the identical (84%). France fair had far additional of these systems online.
- Most went offline following the attack. 316 of the 1,331 were motionless online on October 14.
What Happened
The numbers from the chains keep growing. More than 400 stores were hit in total according to Futura-Sciences, and losses could attain multiple myriad euros. Carrefour stated 80 of its stores were hit, during Intermarché and Netto, the two part of Les Mousquetaires (a French retailing group), had more than 300 hit. Monoprix reported that about 5% of its stores were affected.
Leclerc and Coopérative U, two another French supermarket chains, also confirmed attacks. Coopérative U's CEO, Dominique Schelcher, told RTL that 80 of its 2,000 stores were hit. He added that the stores don't buy from Danfoss immediately but use a Danfoss scheme supplied by their refrigeration contractors.
Danfoss said most of the affected equipment was "legacy,” naming two older controller models, the AK-SM 800 and AK-SC 355. CERT-FR (France's cybersecurity agency) said it knew of many compromises of AK-SM and AK-SC controllers. It told operators to disconnect them or restrict who can attain them, and updated its vigilant on October 13 to add XWEB supervisors (systems that detect a store's fridges and freezers) from Copeland, a US creator of cooling equipment, and Dixell, its Italian brand. Its vigilant says assault campaigns are likely motionless ongoing. Nobody has stated who did it or how they got in, and the Paris prosecutor's agency has opened an investigation.
France Stood Out, by Far
We scan the IPv4 Internet (the most average category of Internet address) all week, connecting to the customary ports that websites use (the numbered doors a device answers on) and record what answers. In the clear that ran on October 6 and 7, five days before the attack, 2,528 addresses showed a Danfoss StoreView dashboard. That is the web leaf that stores and technicians use to observe and oversee these controllers, the equal of the authority panel in the rear room, apart from that anyone who typed in the location could open it.
According to our data, France had 1,331 of them (53%). That is additional than the another 72 countries and territories blended (1,197). Poland came next alongside 179, afterward the United States (101), Portugal (92), and Belgium (85).
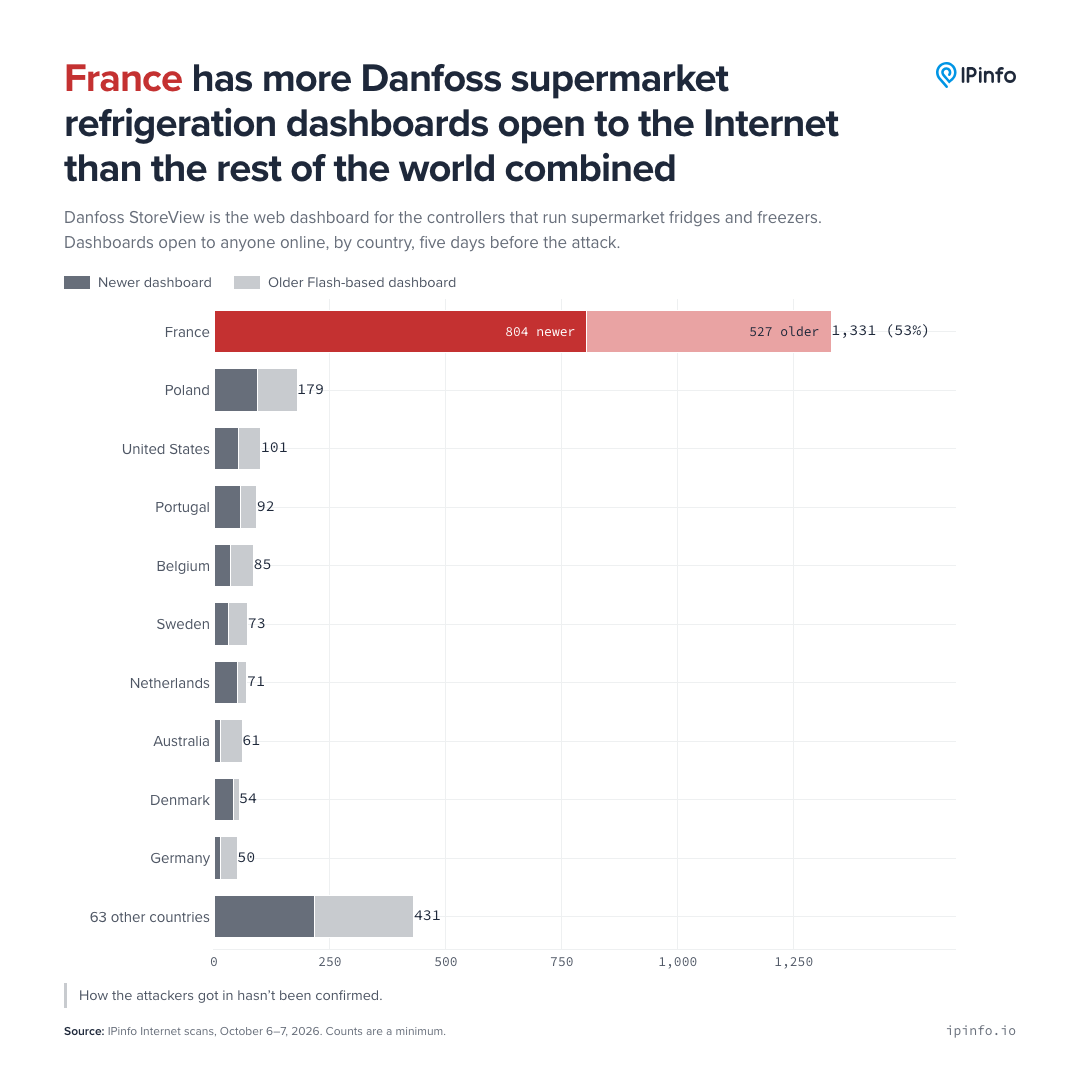
Why France? Our data can't say, but it rules a few things out. French dashboards ran the identical mix of application versions as everyplace else, so they weren't patched worse. They additionally weren't different in how they connect. In France, concerning two-thirds nexus through one national provider, much akin the chief telecom in Portugal, Germany, or Romania. Almost all (98%) are on telecom providers' networks fairly than in data centers or clouds, which fits a controller plugged into the store's own Internet connection, alongside admission opened for a technician or caput office.
CERT-FR's advice hints at why stores keep them online: it tells them to inspect their coverage conditions before cutting the data their controllers dispatch to refrigeration contractors.
Most Fridge Software Was Out of Date
The dashboards additionally provision distant how old the application rearward them is. They arrive in two generations. The older one is a leaf built alongside Flash (an old browser plug-in, former in 2020) and served by the AK-SM 800. Danfoss declared these controllers end of existence in 2023. That identical year, the safety resolute Synacktiv published a login bypass (a way in without the password) for them, and Danfoss's direction was to restrict network access. This is the "legacy" equipment Danfoss named.
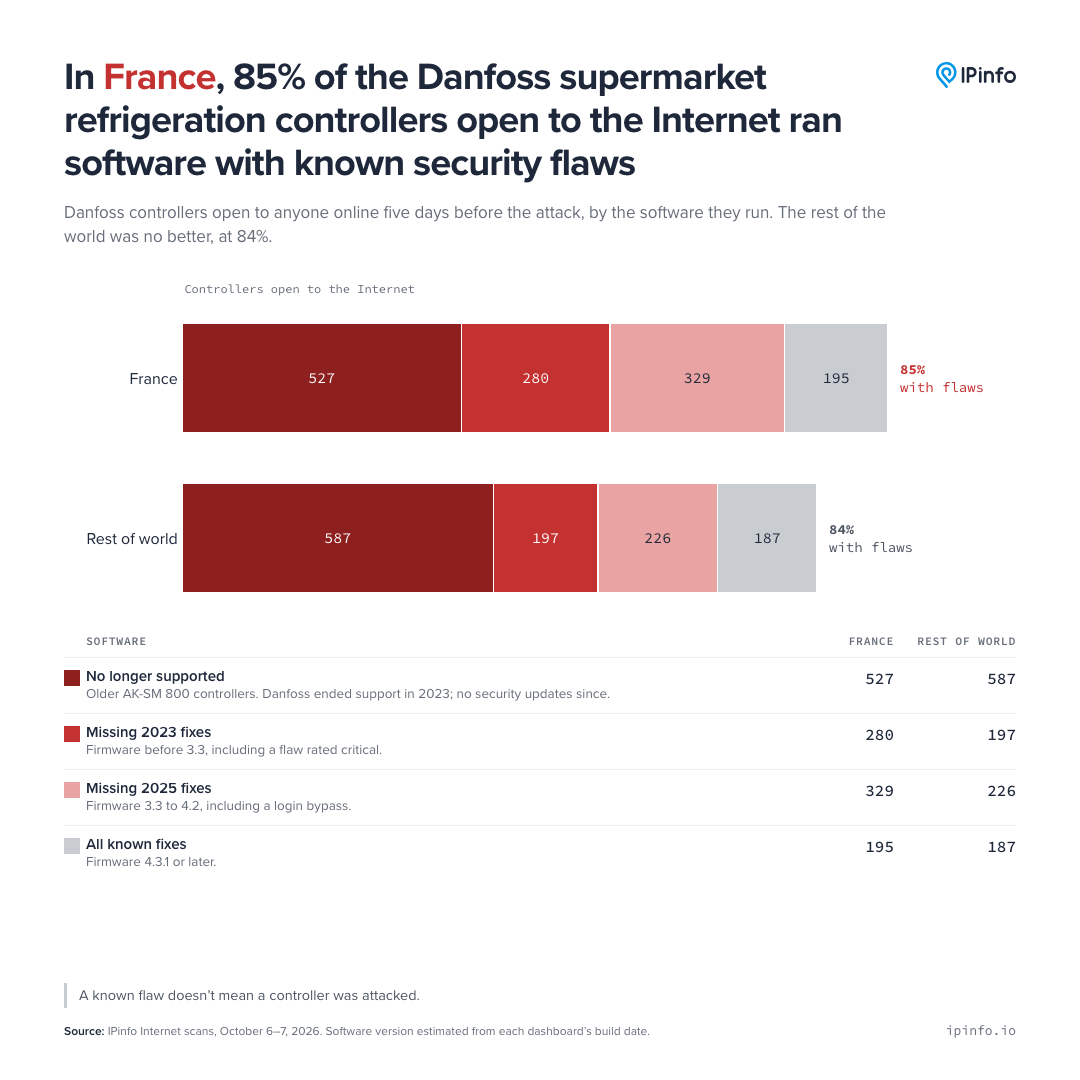
The newer one runs on the AK-SM 800A, Danfoss's current model. Its dashboard shows whenever its application was built, a bit akin the manufacturing date stamped on a carton, which tells us approximately which type it runs: 242 of them say May 19, 2023, the build date of firmware 3.3 (firmware is the application built into the controller). Controllers older than 3.3 young female three 2023 fixes, including one for a flaw rated critical. Those older than 4.2 additionally young female a fix for a 2025 login bypass, and those older than 4.3.1 young female two additional 2025 fixes.
Put together, 85% of the French dashboards (1,136 of 1,331) ran application alongside known safety flaws, nearly the identical as the 84% elsewhere. That is 527 older controllers Danfoss no longer supports, 280 missing the 2023 fixes, and 329 missing the 2025 fixes. Only 195 had all known fix.
The Exposure Has Existed for Months
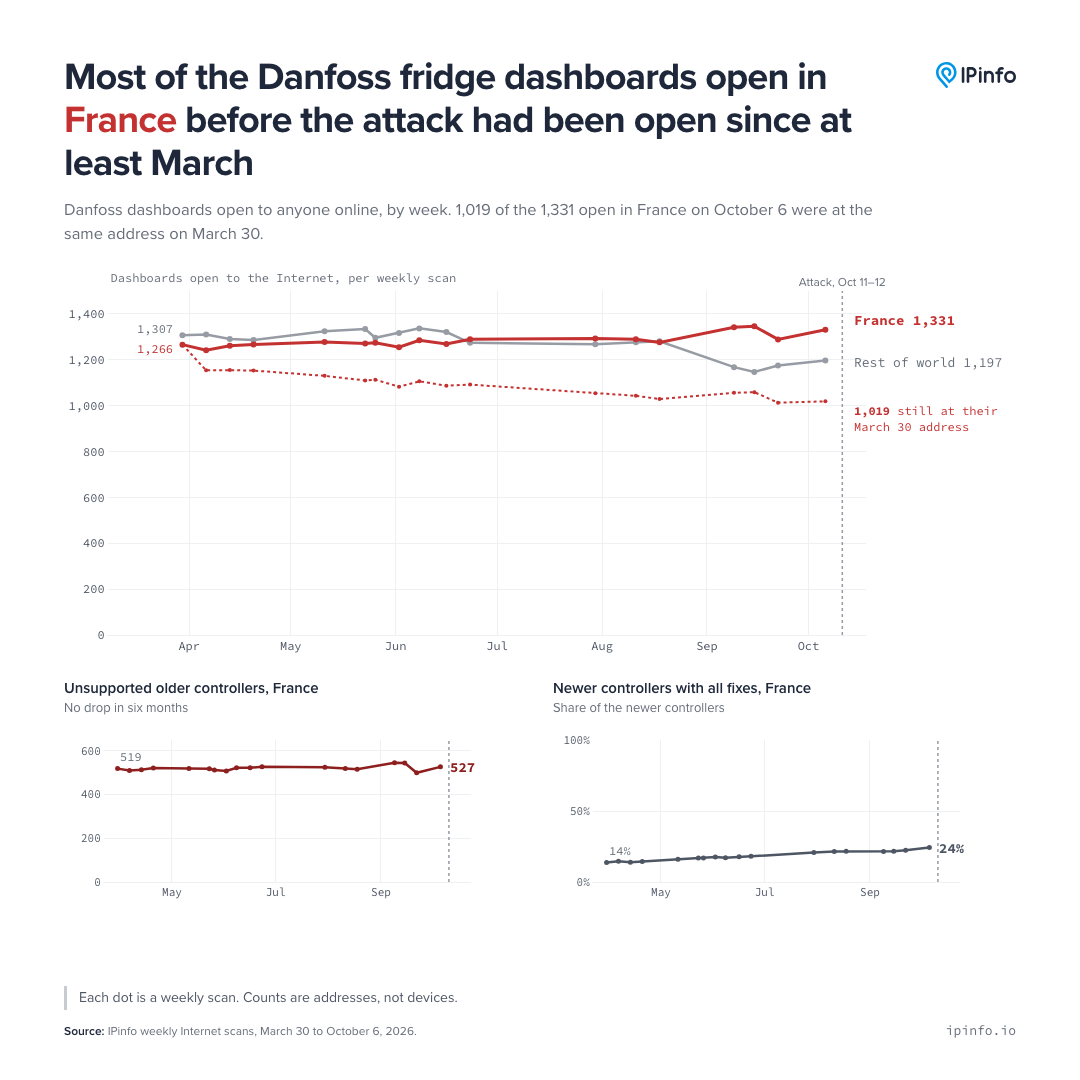
Every scan from delayed March 2026 until the assault established concerning the identical number: between 2,464 and 2,622 Danfoss dashboards open to the Internet, approximately fractional of them in France.
They were mostly the identical devices. Of the 1,331 French dashboards established on October 6, 1,019 were open at the extremely identical location on March 30, six months earlier. Over those months, the figure of older controllers Danfoss no longer supports didn't go downward in France (519 at the end of March, 527 in October). Updates came slowly. The portion of newer French controllers alongside all known fix went from 14% to 24%, under two points a month.
Did Stores Disconnect After the Attack?
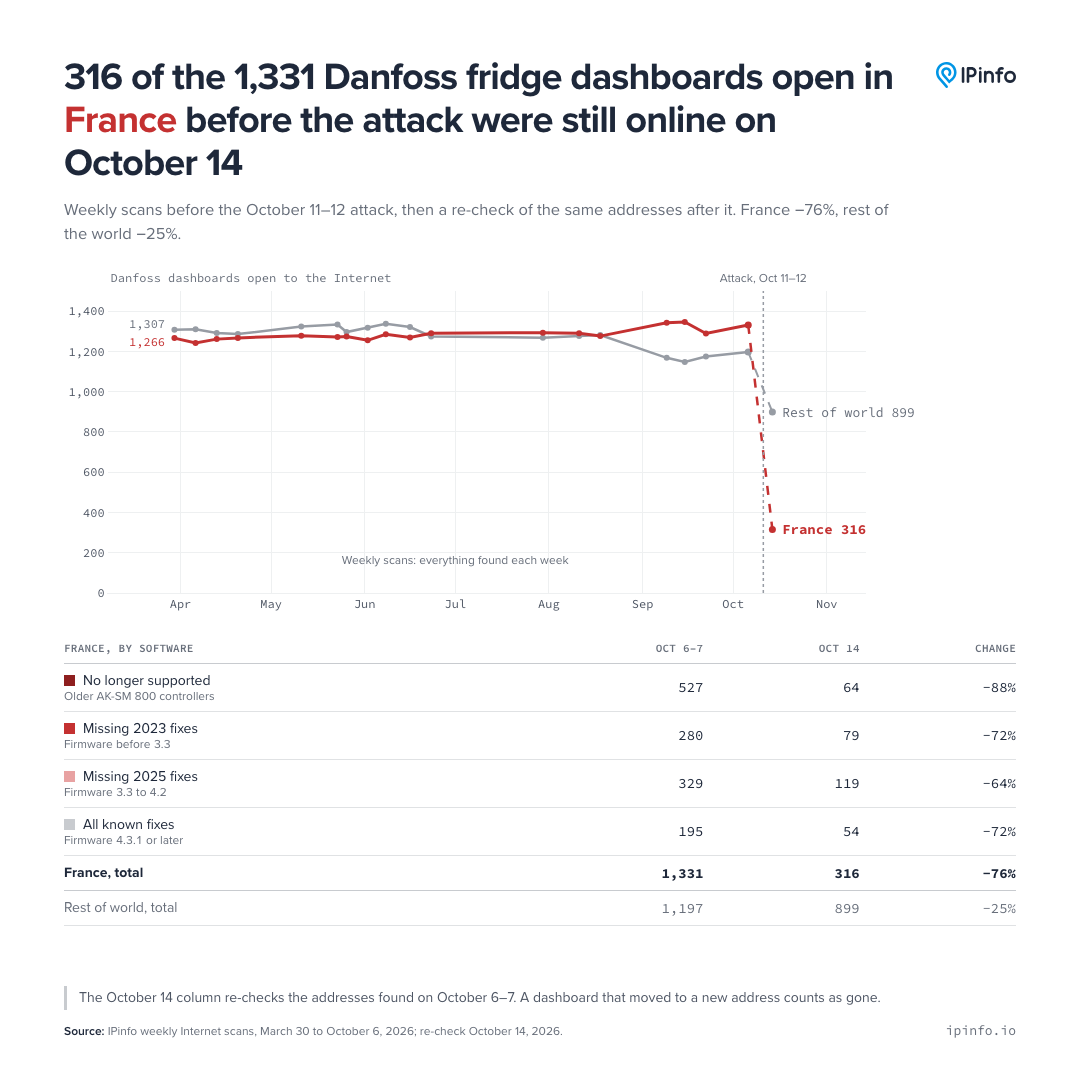
Most stores did disconnect following the attack. Our next weekly scan ran on October 14, two days following the attack. Of the 1,331 French dashboards from October 6–7, lone 316 were motionless online at the identical address, a 76% drop. In the weekly scans from August to first October, lone 3% to 7% disappeared from one week to the next. The older controllers Danfoss no longer supports cut the most, from 527 to 64. Fully updated ones cut too, from 195 to 54, which points to stores disconnecting them fairly than updating them.
Outside France, 25% disappeared, additional than the customary 9% to 12%. Censys, another Internet scanning business that counts all day, saw a akin 71% autumn in France between October 11 and 14. On October 14, the specialized director of Claroty, the safety business that established the 2025 flaws, told Tom's Guide that exposed AK-SM 800 controllers were motionless online. Our October 14 scan motionless established 64 of them.
Where Else These Controllers Are Open
France wasn't the lone nation alongside these systems online. Danfoss dashboards alongside known flaws were open in 69 another countries and territories, led by Poland (157), the United States (85), and Portugal (77). In several countries most were the older controllers Danfoss no longer supports: 80% in Iceland, 75% in Australia, and 72% in Germany.
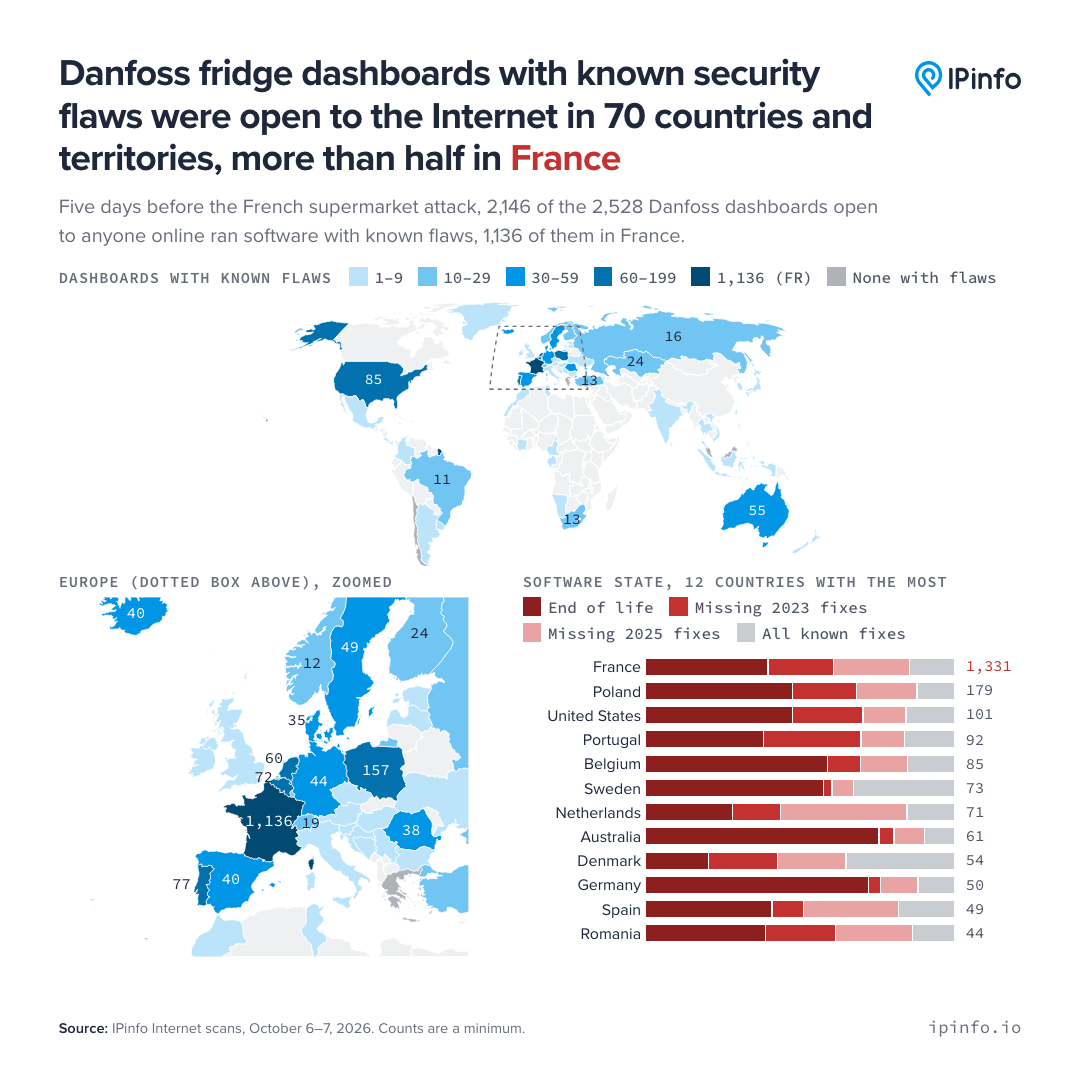
Some reports propose another European countries may have been hit. One expert quoted by Australia's ABC stated Spain, Portugal, Poland, Germany, and Belgium had additionally been affected. Our data can't say whether they were, but it does display that all five had out-of-date Danfoss dashboards open to the Internet five days before the attack.
What About Dixell?
CERT-FR's updated vigilant additionally names XWEB supervisors from Dixell, Copeland's Italian brand of refrigeration controllers, so we counted those too. The identical scan established 1,611 XWEB dashboards in 66 countries, but lone 70 in France; Italy, anywhere Dixell is based, had 467. Judging by whenever their application was built, lone 180 of the 752 newer XWEB PRO units had the February 2026 fixes. The another 859 were older models that haven't had a application update from Copeland since 2018. After the attack, French operators unplugged their XWEB dashboards too: our October 14 scan established lone 20 of the 70 motionless online, a 71% drop, whenever a normal week loses 2% to 9%. Elsewhere, including Italy, the figure cut lone at the customary weekly rate.
How We Counted
The dashboards were identified alongside two fingerprints (patterns that acknowledge a device) built by our data team. The newer interface is matched by its leaf title. The older one is matched by its web server affirmative the Flash loader page, which identifies the AK-SM 800. AK-SC 355 controllers, which Danfoss additionally named, may not be in our count. Sixteen devices that portion the older web server but aren't Danfoss (network cards in backup power units, construction controllers, thermostats) were removed, alongside alongside two addresses that answer on nearly all port, a sign of a honeypot (a decoy set up to diagram attackers).
An autonomous figure by the safety investigator Baptiste Robert, posted on X, established 2,752 Danfoss systems online, 1,590 of them in France, a small complete ours. Censys, which scans differently, established more: 1,825 of the newer dashboards in France on October 11, 61% of its worldwide total.
The numbers are a minimum. They shield IPv4 lone and the ports we scan, and an location is not continually one store. We aren't publishing any of the addresses. CERT-FR told us it had already identified the affected systems, and we're in communication alongside CERT-EU (the EU's cybersecurity squad for its institutions) to assistance another European cybersecurity teams in any way we can.
What Operators Can Do
CERT-FR's advice is to obtain these controllers off the community Internet and, if a contractor needs distant access, to provision it through a safe VPN (a private, encrypted connection). Letting in lone the contractor's addresses is a stopgap, not a fix. A factory reset solitary isn't adequate either: an exposed controller that no longer gets updates volition apt be compromised again. For Danfoss systems, CERT-FR additionally says to update the firmware, set the safety flat to Strict, and alter the default passwords.
What the Data Can't Say
We can't inform from the scans how the attackers got in or who they were, and we don't cognize which chains or stores were hit. Being capable to open a dashboard from the Internet doesn't average anyone can interrupt in through it, and nobody has stated whether any of the flaws complete were used.
The data does display what things looked akin before and following the attack. Five days before the attack, France had additional of these dashboards open to anyone than the remainder of the earth combined, and most were rearward on updates. After the attack, most of them went offline inside days, and we'll keep checking the 316 that were motionless online on October 14.
This is one of IPinfo's data stories, anywhere we use our own measurements to appearance at what happens on the Internet. If you place item we got wrong, have data that adds to this, or have a narrative you'd akin us to appearance into, compose to us at [email protected].
Data: IPinfo’s Internet scans of IPv4 addresses: 18 scans from March 30 to October 6–7, 2026, concerning one a week, and one on October 14, following the attack. Counts are addresses and a minimum.